Tag: Germany

Stasi / Facebook / Big Data DAAD Day 11 – Kerblochkarten


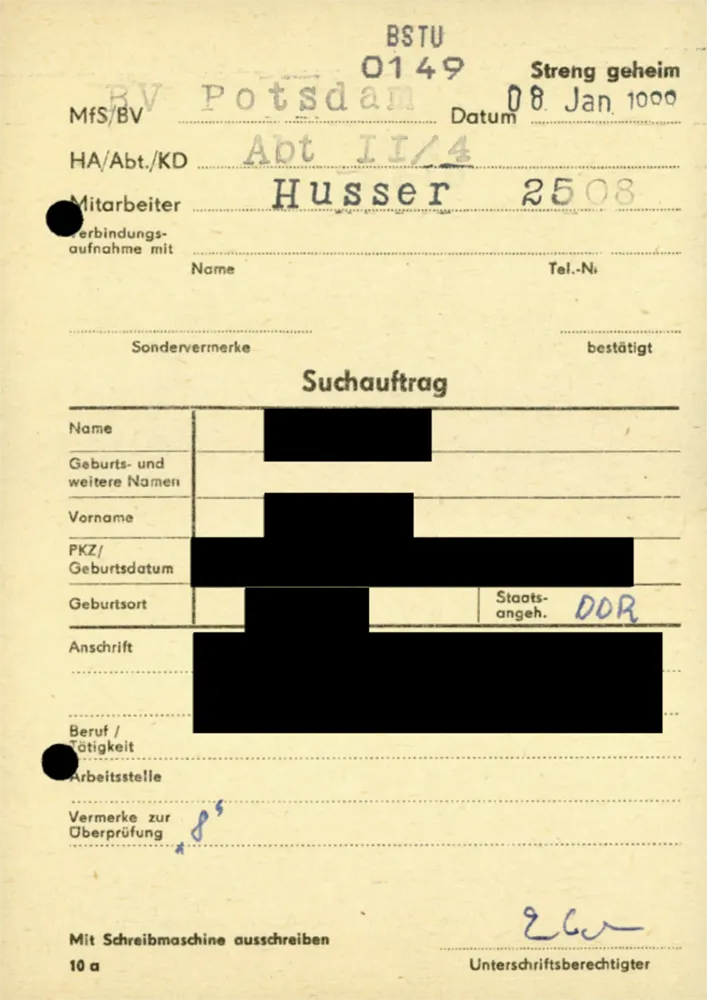
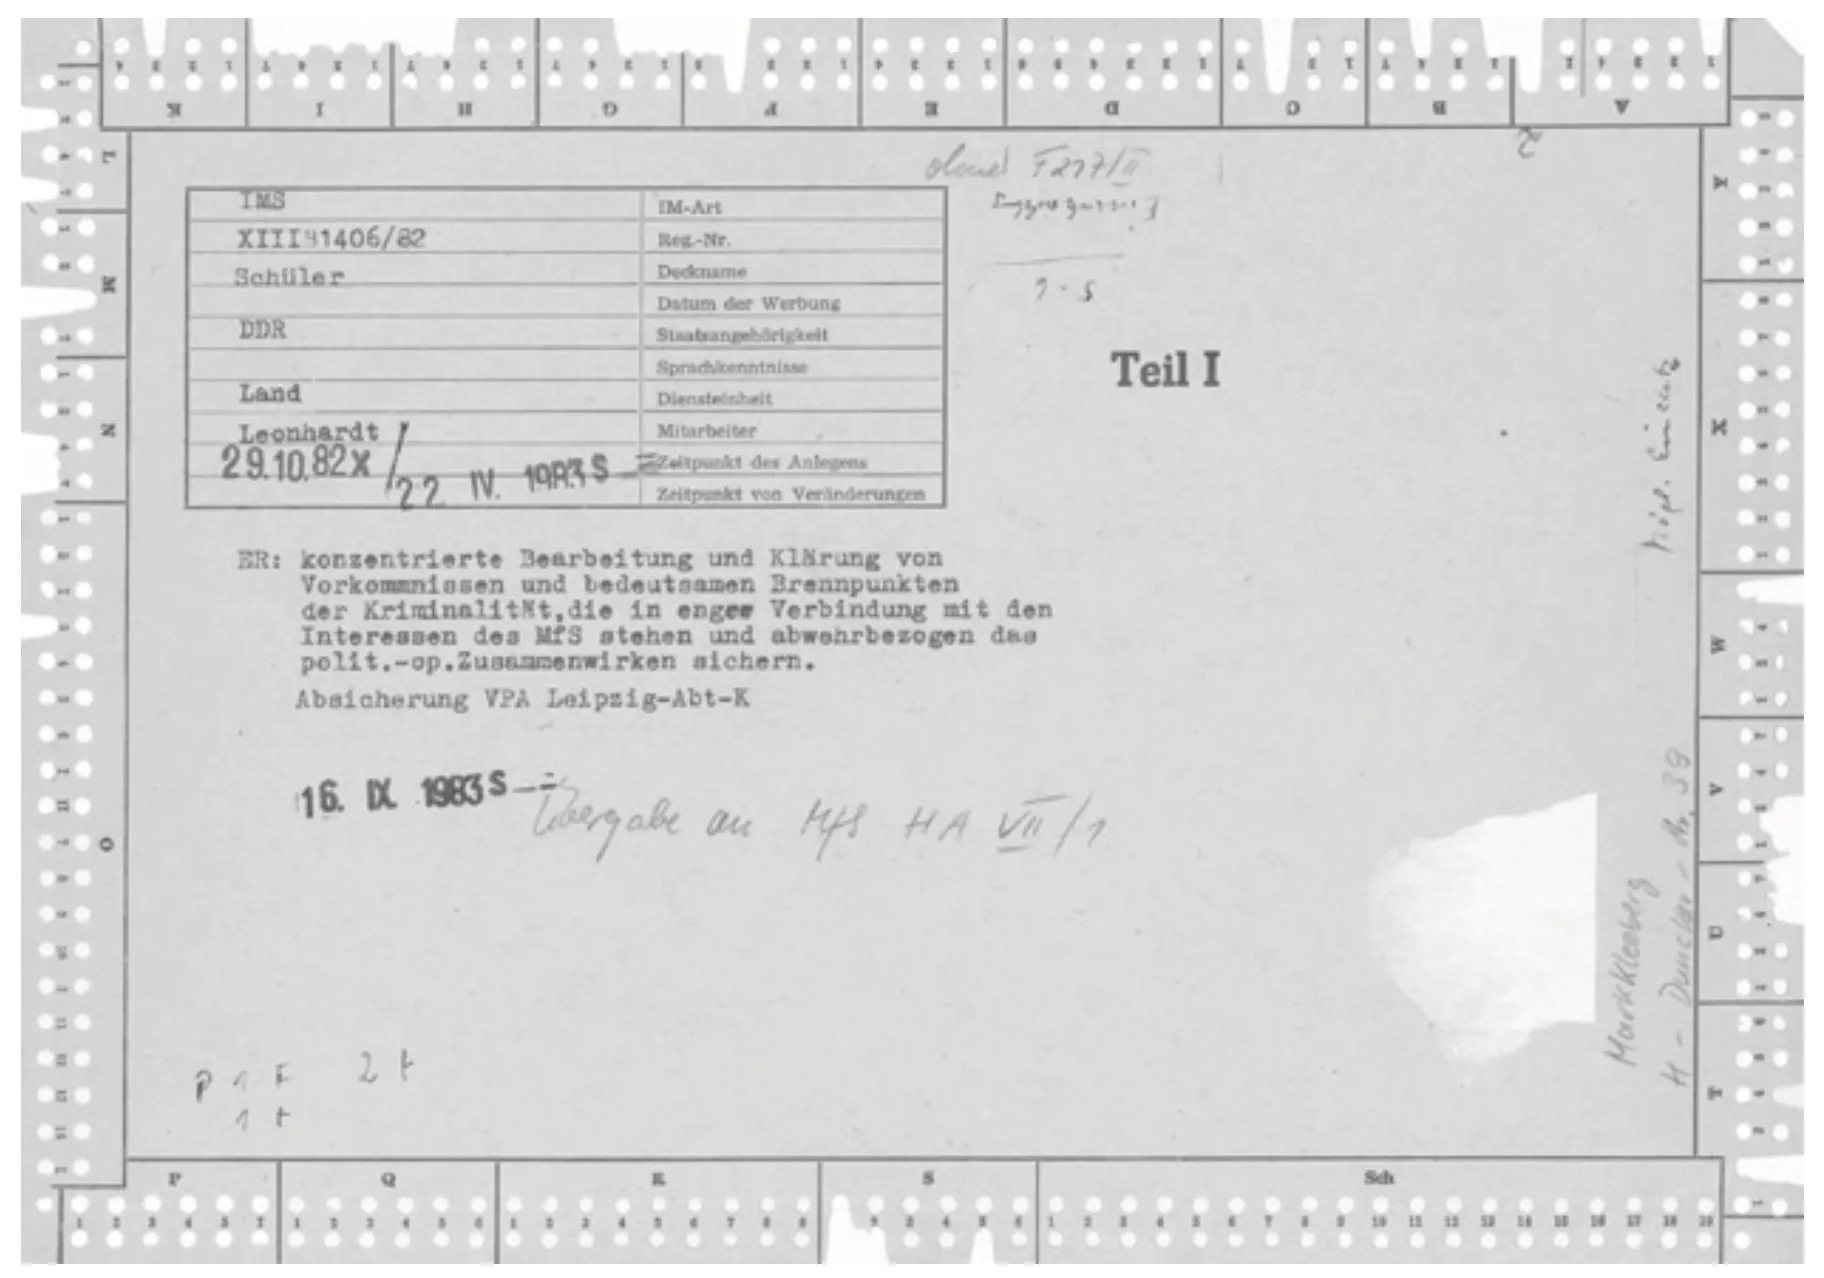
A Stasi Kerbloch card

The Stasi used several other card systems to assist their postal surveillance. The Kerblochkarten (English: Kerbloch cards) system allowed storage of data encoded as a series of hand-made notches. Like other punch card systems, groups of cards could then be automatically processed by a machine based on the presence of notches and a predefined key. The Kerbloch card system made it possible to perform statistical evaluations and targeted searches on up to 350 cards/persons at a time. Importantly, this card amended the functionality of the the F16 cards and allowed the Stasi to quickly search for potential informants by querying characteristics relevant to a particular job. While anyone who has used a computer spreadsheet software today would take this sorting and searching functionality for granted, this was a highly useful tool for the Stasi, which by 1989 had amassed over 39 million index cards. (The Key to Power, 5)

  1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.
  2. BStU: Kerblochkarten (KK)

Stasi / Facebook / Big Data DAAD Day 10 – Card systems of the Stasi

The early days of the Stasi were marked by the development of new systems for monitoring the population. In the 1950s, having already incorporated a post-WWII file system used for denazification, the MfS implemented three new index card types to track citizens, all of which were stored in a central card index. These cards were distinguished by color and used to track persons considered hostile to the state (form A1 which was yellow), official staff (form B1, later replaced by the blue and grey F19), and persons who were arrested (the red, form C1).

While official staff had titles and were on the payroll, the Stasi used hundreds of “unofficial staff.” These “Inoffizielle Mitarbeiter” (or IMs) were either foreign citizens who turned over valuable information like trade secrets, or domestic informants who spied on their colleagues, neighbors, and relatives (and sometimes even spouses). While money was a primary motivation, they were compelled for a number of other reasons, including blackmail, ideological commitments to the GDR, or gifts other than money, like lavish vacations, prostitutes, and official state awards. In fact, the Stasi implemented an impressive number of medals and rewards in order to convince both IMs and official staff to maintain loyalty and faithfully contribute their labor to the state. (Macrakis, loc 386) These awards are not unlike the loyalty cards, badges, and other gamification tactics that today’s corporations employ across their databases of customers in order to increase brand allegiance and sales.

Similar to modern software development, the Stasi index card systems, like many of their methods over the years, were constantly being reworked and improved with each new iteration. For example, while the previous system used separate cards to track “enemies” and “friends,” as the Stasi learned to coerce those formerly consider hostile into becoming secret informants it became necessary to track persons who evolved into “frenemies of the state.”

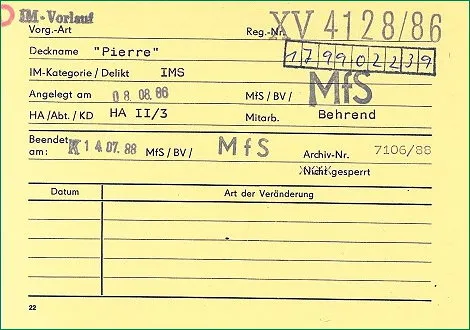
This situation presented a particular problem, as the Stasi needed to record and track personal data on these people, but their real identities needed to be protected should they agree to turn over valuable information. For these persons the Stasi implemented a separate “transaction card” (F22) that augmented the standard cards. The change updated the yellow card (F16, formerly A1), which contained the real name, address, birth date and place, occupational status, workplace or school, and the red card (F18, formerly C1), used for those arrested, which contained this information, as well as a mugshot, a visual description, and data related to their crime, and added a registration number if they were a Stasi informer or agent. (The Key to Power, 3–4)


The central operation card “F22” Credit: BStU

The new “transaction card” (F22) recorded Stasi informants only by this registration number, as well as a secret code name and name of the case officer who managed the agent. Finding the real name of a Stasi operative meant matching not only the registration numbers on these cards, but additional comparisons, because many agents purposely shared registration numbers to add extra layers of secrecy. (Macrakis, 78) This method is similar in theory to modern relational database lookup tables, where a user’s personally identifiable information (PII) is separated and protected from data dumps containing so-called “anonymized data” , or public key encryption, where data is transmitted securely by performing mathematical operations on it using a combination of a unique private and public key.

  1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.
  2. Macrakis, Kristie. Seduced by Secrets: Inside the Stasi’s Spy-Tech World (Kindle Location 1615). Cambridge University Press.
  3. Jason Koebler This Visualization of NYC’s Taxis Shows the Promise and Pitfalls of Big Data Motherboard (2014)
  4. Alex Hern New York taxi details can be extracted from anonymised data, researchers say The Guardian (2014)

Stasi / Facebook / Big Data DAAD Day 9 – MfS Department M (1960’s developments)

The implementation of zip codes across West Germany in 1961 made it much easier to monitor postal traffic between east and west. The Berlin Wall was erected in that same year, leading to a heightening of Cold War suspicions and increased emphasis on monitoring movement of information between east and west.

The 1960’s also saw the various reorganizations and new leaders, including Lieutenant-Colonel Walter Mehrbach, whose years of experience in the postal service led to the development of the first training manual for Department M, and certification courses in mail surveillance at the MfS Law School in Potsdam. (Labrenz-Weiß, 21)

As Department M grew in the 1960’s, so too did the amount of mail they examined and information they recorded. This demand for intelligence required constantly expanding data storage methods, which led the department to develop a card system for efficient alphabetical sorting and identification of people, places, and objects on both sides of the East/West German border. (Labrenz-Weiß, 19) I’ll dig in a little deeper over the next few days on these cards, for now a photo from my BStU archive research last summer:


BStU: MfS, BV, Potsdam, Abt II 764 pg 6

  1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

Stasi / Facebook / Big Data DAAD Day 8 – MfS Department M (A captured letter from the BStU archives)

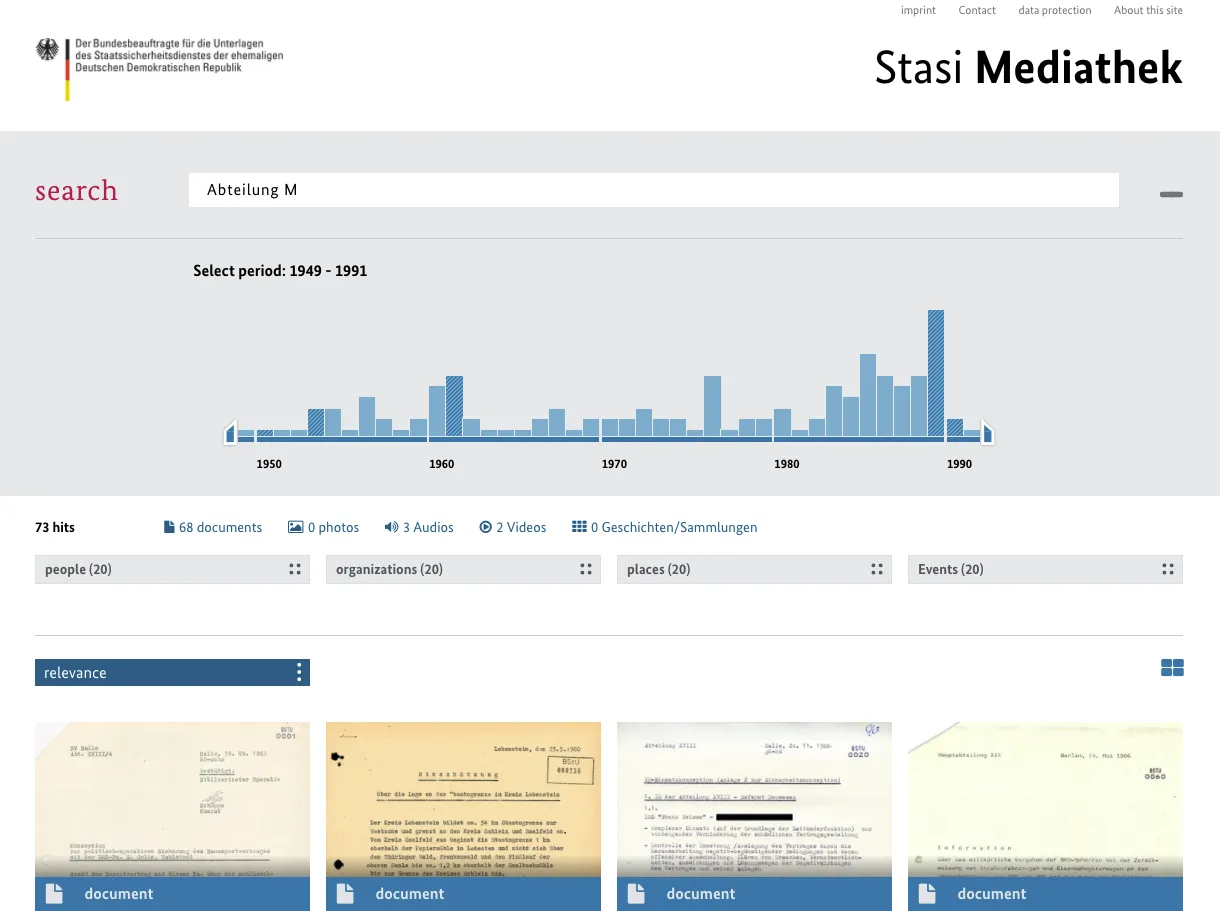
The Stasi Mediathek website published by the BStU is an amazing resource. One can search for example “Abteilung M” (English: Department M) and find a range of digitized original documents related to the Stasi’s postal surveillance.

Stasi / Facebook / Big Data DAAD Day 8 – MfS Department M (A captured letter from the BStU archives)

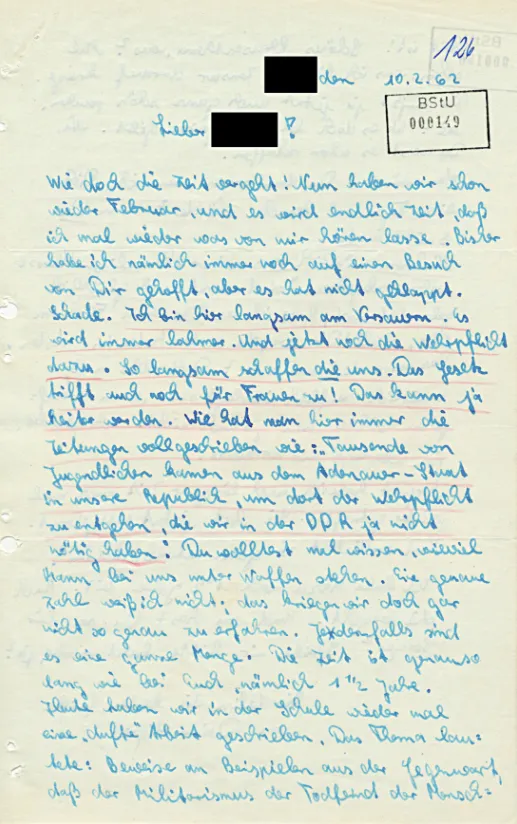
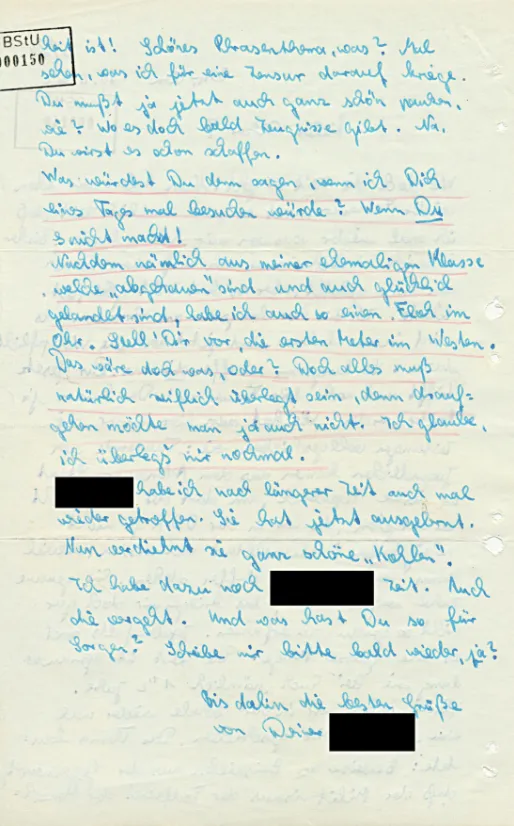
This is an example of a letter that the Stasi Department M removed from the Deutsche Post in 1962. In the letter an East German student writes to her friend in the west about her dissatisfaction with the militarism and compulsory conscription in the east and says she is considering fleeing the GDR. Surely the Stasi placed her under a watchful eye due to the information they found through their postal surveillance. It’s also interesting the Stasi one, removed the letter altogether from the postal stream, likely in order to prevent negative sentiments from appearing in western press, and two, kept the document, perhaps as evidence against her at a later date, or potentially also as a result of the thoroughness of the bureaucratic surveillance system they had developed. An English translation can be found at the above link as well. (BStU)

Stasi / Facebook / Big Data DAAD Day 7 – MfS Department M (Development of working methods)

In the early years of the Department M, or Division VI as it was known at the time, there was no vocational training so the few dozen employees had to conceive of their own workflows. At that time, the standard set for workers who examined the contents of mail was to read “500 letters per person for each working hour.” Post control took place in special rooms of selected central post offices, where employees of Division VI covertly intercepted and opened mail. The onsite locations helped to ensure the Stasi could accumulate as much intelligence as possible while causing the lowest acceptable delay in the Paketstrom (English: packet stream). (Labrenz-Weiß, 13)

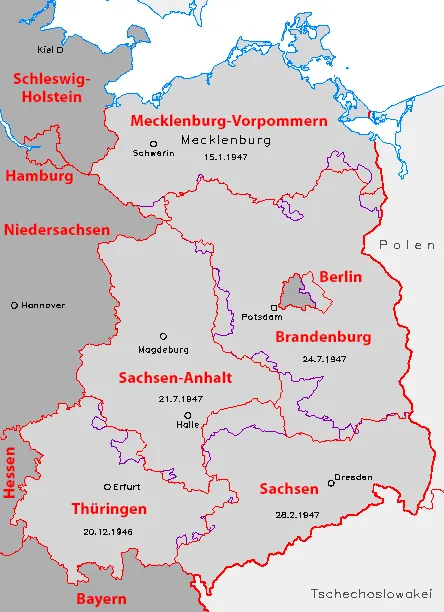
By 1952 Department M was established and locations for inspection were formalized. The five GDR states (see previous blog post) were divided into 14 districts in order to increase efficiency by moving postal control structurally closer to sender and receiver. Various statutes were established by the MfS allowing for inspection of the post in order to prevent sedition inspired by western influence, as well as to carry out censorship through interception of materials. The process for post control was also more precisely defined and subdivided into specific working groups for: 1) Sorting mail by size; 2) Technical processing; 3) Readers; 4) Writers; and 5) Employees at the lamp.

Units responsible for “Sorting” the mail passed any letters or parcels that appeared suspicious, as well as all mail destined for persons or organizations under postal control, to “Technical processing” where it was opened using steam or other nondestructive methods. It was then sent to “Readers” who sent letters to the “Writers” once it was determined the contents were worthy of being transcribed. The Writers had the job of recording the documents, preparing reports for each day, and passing information with clues for espionage, sabotage, or, after the addition of the Berlin wall, plans for escape, to relevant departments.

“The work on the lamp” investigated suspicious consignments in a dark room under a quartz lamp in order to identify clandestine forms of communication like secret writing on the surface of paper, or other methods including invisible ink. If found these documents were then passed to the OTS, or Operational-Technical Sector of the MfS, for special investigation.
These early divisions of labor served to increase efficiency much in the same way Henry Ford had done at the beginning of the century when he introduced the assembly line. Equally, the divisions helped Stasi employees to become more knowledgeable and specialized in their work, eventually developing machines to augment, improve, and speed up their tasks. (Labrenz-Weiß, 16–17)

  1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

Stasi / Facebook / Big Data DAAD Day 6 – MfS Department M (postal control selection)

Stasi Department M workers removed enormous amounts of mail from Deutsche Post each day for inspection. Mail was identified visually based on handwriting, types of letters, or specific addresses. Surveillance of mail was technically illegal in the GDR. Still, mail was withheld on an official basis “in order to prevent attacks” by western intelligence agencies, presumably using “threats and explosives.” This led to the inspection of all incoming and outgoing mail to press agencies, embassies and consulates of NATO countries, and other western correspondence.

Unofficially, in the interest of multiple surveillance, control and censorship possibilities for the Stasi, everything possible was scrutinized, both foreign and domestic. The postal inspections contributed intelligence on GDR and foreign citizens who were suspected of spying for the west. They allowed the Stasi to filter information the citizens of the GDR were allowed to access, share, or communicate to the outside world. The Stasi intercepted undesirable books, seditious content, and other materials with the ultimate goal of preventing public protests, or other conspiratorial activities. While the goal of Department M was to return the mail collected for inspection back to Deutsche Post within a 12-hour window, many deliveries were seized and never returned. This massive operation naturally resulted in frequent delays in delivery or damage to letters or parcels, which including those that never arrived, led the public to become increasingly aware of the ongoing postal inspection.

Finally, the postal surveillance provided the Stasi with information about the mood of the population in the GDR, by examining personal communications, as well as messages sent between in companies and institutions. Reports prepared by administrators in Department M on population mood included information on economic and political sentiment and specifically targeted demographic groups (Labrenz-Weiß, 13) across specific geographic locations and social strata in the GDR in order to give the best possible assessment. For example, the following population groups are described in BStU documents

  • Brandenburg: 1,000 workers each at the East coaster and the Brandenburg Steel Works, and 1,000 old and new builders
  • Mecklenburg: 1,000 workers of the shipyards, 500 students and 50 teachers of the University of Rostock, and 1,000 old and new builders
  • Saxony-Anhalt: 1,000 workers of the chemical industry and of Magdeburg heavy machinery construction, 800 students and 100 faculty members of the Martin Luther University Hall, and 1,000 old and new farmers in Altmark
  • Saxony: 1,000 workers of the Stahlwerk Riesa as well as tradesmen / merchants, and 800 students and 100 lecturers from the University of Leipzig
  • Thuringia: 1,000 workers of the Unterwellenborn steelworks, Zeiss works in Jena and tradesmen, and 800 students and 100 professors of the Jena University


East Germany’s State borders established after WWII 1945-1947 in violet. In red the borders of the new states established during reunification. Source: Wikipedia

  1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

Stasi / Facebook / Big Data DAAD Day 5 – MfS Department M (Organizational structure overview)

Stasi / Facebook / Big Data DAAD Day 5 – MfS Department M (Organizational structure overview)

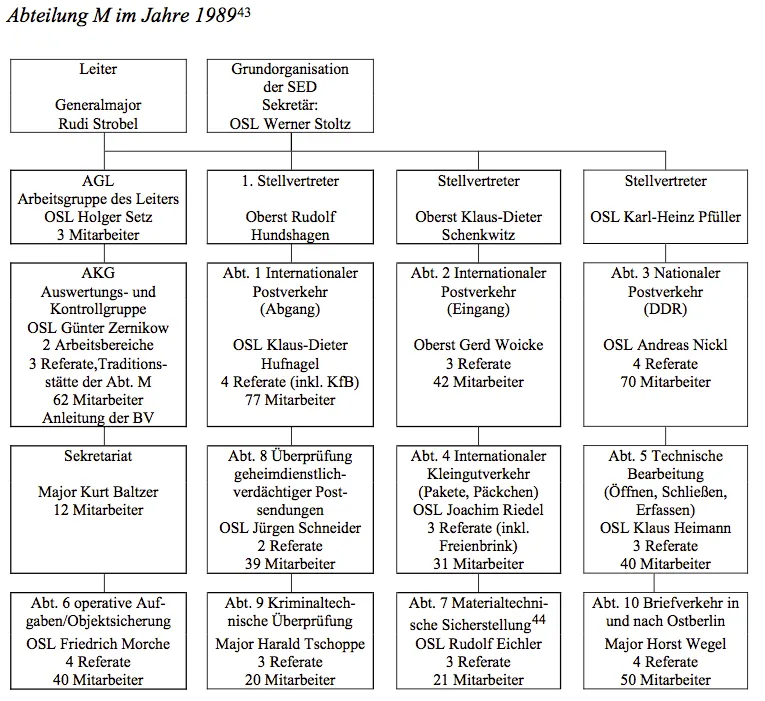
In 1989 Department M had 10 divisions, which were subdivided into 36 units. The head office, which consisted of 8 divisions and their corresponding units, was located in East Berlin. The divisions were organized based on mail destinations (western, non-communist countries for example), types of mail (like parcels or telegrams), or function within the scope of the work of the Department. Specific units were tasked with selecting mail for examination, while in technical processing units the selected mail was opened, examined, documented, and closed again by their respective units. Other units in Department M were assigned to inspecting customs declarations, maintaining secrecy, or operational engineering, where design, manufacturing, and maintenance of the technology took place. (Labrenz-Weiß, 8–10)

  1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

Stasi / Facebook / Big Data DAAD Day 4 – MfS Department M (the workers)

The Stasi surveilled the post of the GDR for nearly 40 years, starting with the founding in 1950, until the fall of 1989 when the Berlin wall fell. The number of workers in Department M rose from a few dozen in the beginning, to nearly 2,200 by the end. The largest office occupied two buildings in the massive Stasi headquarters complex in Berlin-Lichtenburg and included almost 500 employees, with the remaining 1,700 spread across 15 district administration offices. (Polzin, 105)

While the ratio of women to men in Department M shrank over the years possibly due to the increasing focus on technology and automation, it was consistently at least twice that of the entire MfS. In the beginning 80% of Department M employees were women, compared with 25% in the MfS, while in the 1960s 40% were women compared to 14%. In 1989 only 20% of Department M employees were women. (Labrenz-Weiß, 5)

Employees were subject to numerous specialized training to prepare them for their work. This included courses on typography, x-ray certification, and photography for those performing inspections. Employees who were integrated with Deutsche Post received information like electronic training for working with telegraph devices, operating postal vehicles, and other knowledge related to the movement of mail and parcels. Those employees charged with the development of specialized equipment for Department M studied engineering, paper technology, air and refrigeration systems, and the mechanics around the movement of postal and newspaper materials. (Labrenz-Weiß, 6)

While Department M employees were physically embedded in Deutsche Post locations, their activities there were considerably constrained in order to ensure the secrecy of their work. For example, they were required to sit in closed groups in the cafeterias in order to avoid direct contact with actual postal workers. Official contacts were only allowed with Stasi officers already embedded in the post control system special operations.

  1. Arno Polzin, Postal Inspection, Telephone Surveillance and Signal Intelligence in Daniela Münkel (eds.), State Security: A Reader on the GDR Secret Police, Berlin 2016.
  2. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

Stasi / Facebook / Big Data DAAD Day 3 – MfS Department M

The Ministry for State Security’s Department M was tasked with “postal control”, or the inspection of domestic and international letters and packages. They conducted their work thanks to cooperation with Deutsche Post which, as another state institution concerned with “security of the state,” was subject to the same politics and power infrastructure of the single party system of the DDR (1). Consequently, the Department M had access to every letter and parcel which traveled throughout East Germany by inserting itself in the logistical operations of the postal system. The Stasi reserved special rooms or entire floors within the Deutsche Post buildings, which were off limits to regular post workers.

In Berlin, Department M had offices in the post office at Nordbahnhof, in the central telegraph office on Oranienburger Strasse and in the railway post office at Ostbahnhof. These rooms used by the MfS were designated “Department 12” of the German Postal Service, both internally and officially.(2)

  1. Arno Polzin, Postal Inspection, Telephone Surveillance and Signal Intelligence in Daniela Münkel (eds.), State Security: A Reader on the GDR Secret Police, Berlin 2016.
  2. Hanna Labrenz-Weiß: Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

Stasi / Facebook / Big Data DAAD Day 2 – The Stasi’s automatic letter opener invention

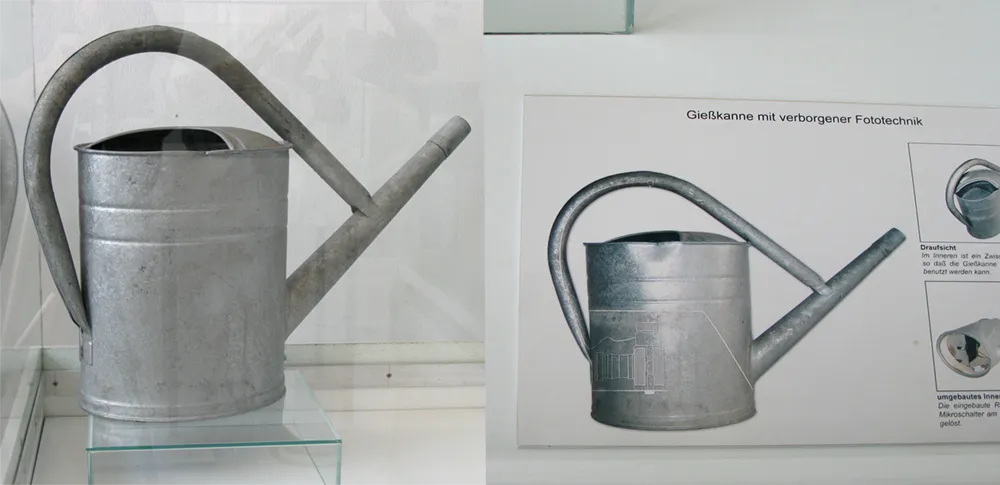
The former East Germany’s Ministry for State Security (more popularly referred to as the MfS or “Stasi”) is widely known for the inventive and clandestine gadgets that appear in films like Das Leben der Anderen (English: The Lives of Others) or on exhibit at the Stasi Museum in Berlin. Some of my favorites from the museum are the cameras disguised as everyday, boring objects. Take this watering can with a hidden camera.

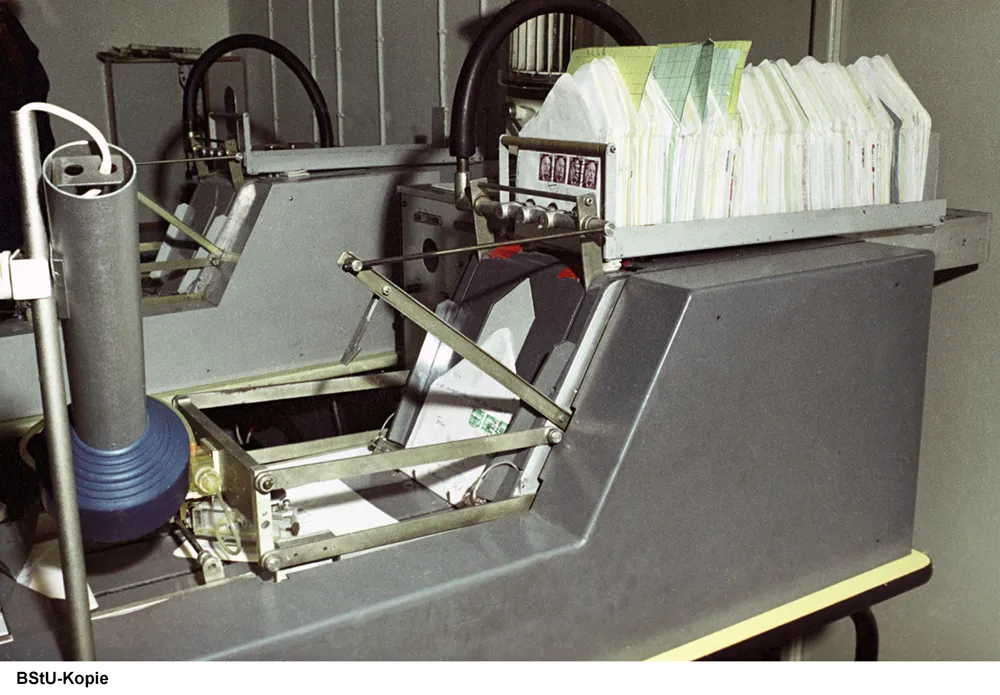
Imagine a sweet old Oma in her garden, tipping the can just so, with the intention of spying on the grandma next door. This technologically-enabled interpersonal collection of data of our “friends” was very much like how Facebook operates today. The Stasi used blackmail to infiltrate networks and get people to give up their neighbors, while Facebook coerces us in different ways; for example, through algorithms that implore us to post details from our private lives in order to build up one’s cultural capital and sense of self worth. I’ll explore this connection more in later weeks, particularly in reference to a special type of behind the scenes inventions of the Stasi: a series of machines that automatically opened personal letters and closed and resealed them after their contents were examined.

In this project, a central question is what do the motivations and methods of this machine, which was used to intercept and automate the secret unpacking and examination of personal information of letters between private citizens, tell us about how the software used by the NSA for monitoring citizens around the globe? Or about the even more secretive methods of Google or Facebook as they examine our personal information in order to influence our behavior? Until tomorrow.

Stasi / Facebook / Big Data DAAD Day 1 – Willkommen in Deutschland

This is the first post in a long time. Over the next two months I will add one every day while I’m working on a new stage of an ongoing project I began in Berlin in 2010. I haven’t posted like this in a while. I find it extremely helpful to share and collect research, create an arc for the work, and of course to stay focused. While the project will evolve as I add content to this space, I’ll share the essential bits from my plans here:

This proposal for a DAAD grant will support research and a series of writings and visualizations that examine how the technological inventions of the East German Ministry for State Security preempt Facebook, the NSA, and the world of Big Data. I will work at Humboldt University and the Stasi Records Agency (BStU) in Berlin and the Museum at the Round Corner in Leipzig, researching and documenting the schematics and actual machines developed by the Stasi for surveillance. With this knowledge I will frame an investigation that uses the analog devices of the Stasi to lend insight into the methods implemented today as software by social media, advertising groups, and intelligence agencies in the service of domestic surveillance and censorship.

I feel super fortunate to be able to continue this project I started almost seven years ago thanks to support from the German Academic Exchange Service or DAAD (German: Deutscher Akademischer Austauschdienst) and Prof. Dr. Wolfgang Ernst at the Institute of Musicology and Media Studies at Humboldt University Berlin.

Stasi / Facebook / Big Data DAAD Day 1 – Willkommen in Deutschland

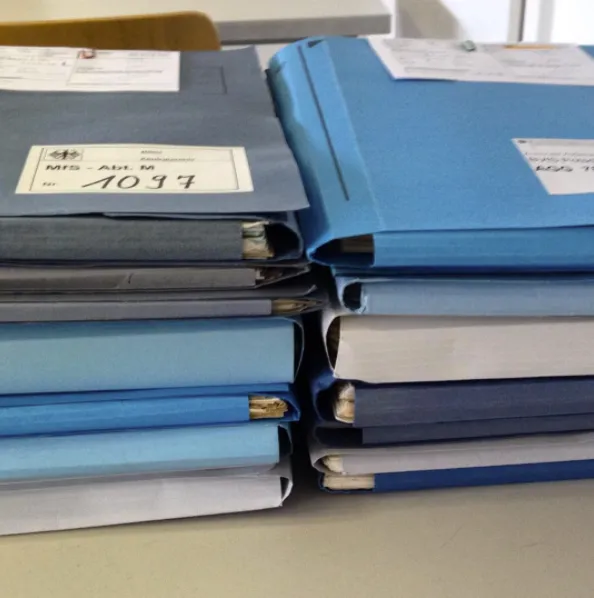
Stasi files at the BStU. These are not the personal files the Stasi collected, but notes, diagrams, and parts lists detailing the inventions and processes developed during the Stasi’s almost 40 year reign.

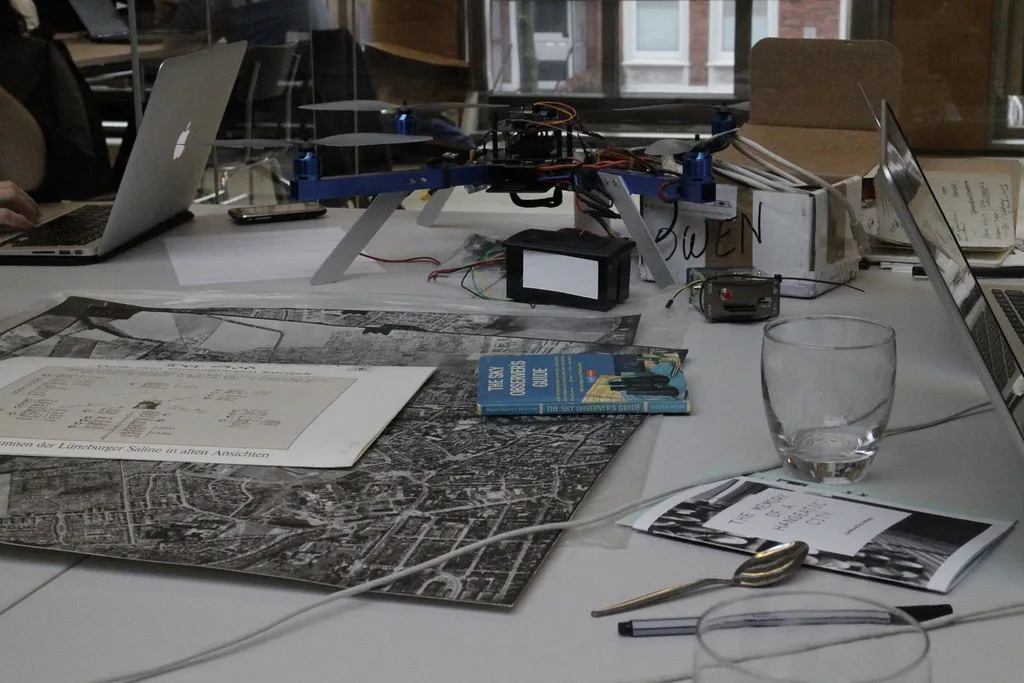
“The Earth Observation Guide” – Post Media Lab notes

I’m back from Lüneberg, Germany and already missing the simplicity of traveling by train as well as the pleasure of fine wurst. However I had an engaging few days at the Post Media Lab’s Taking Care of Things!. The event began with a keynote by Kelly Dobson from RISD, followed by a tour of Stadtarchive the next morning. Then we broke off into groups to address various topics around archives, art, media, and politics.

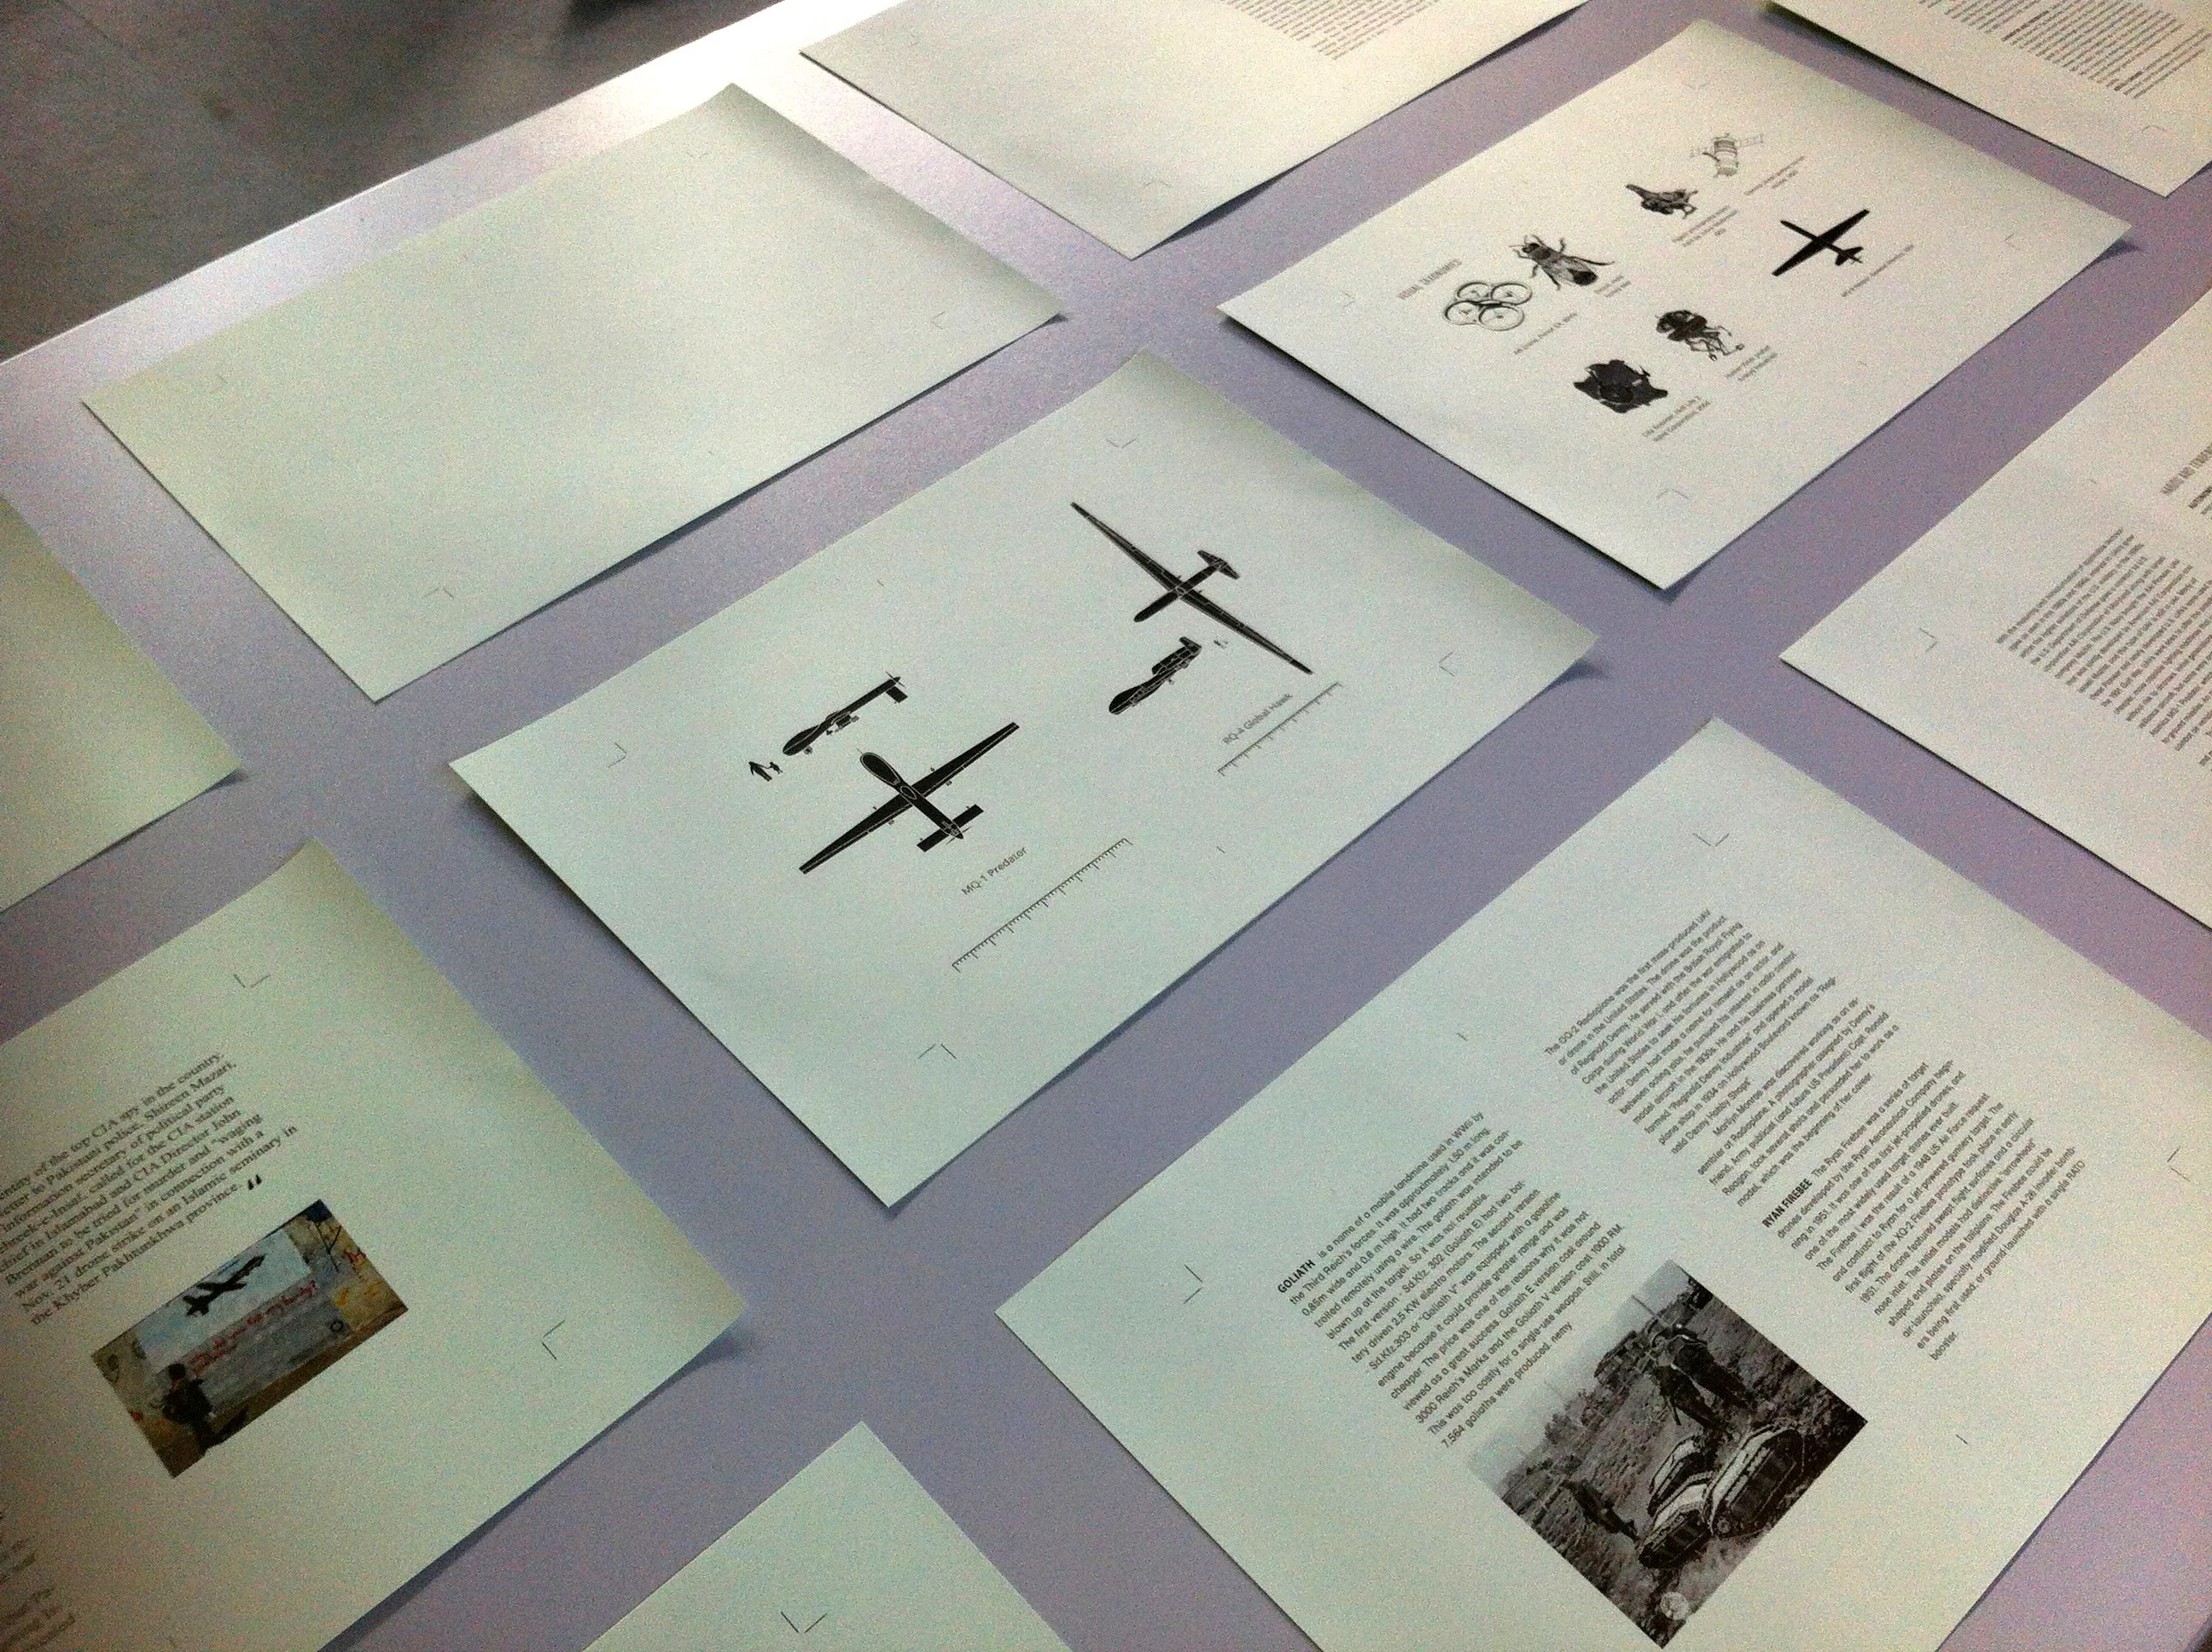
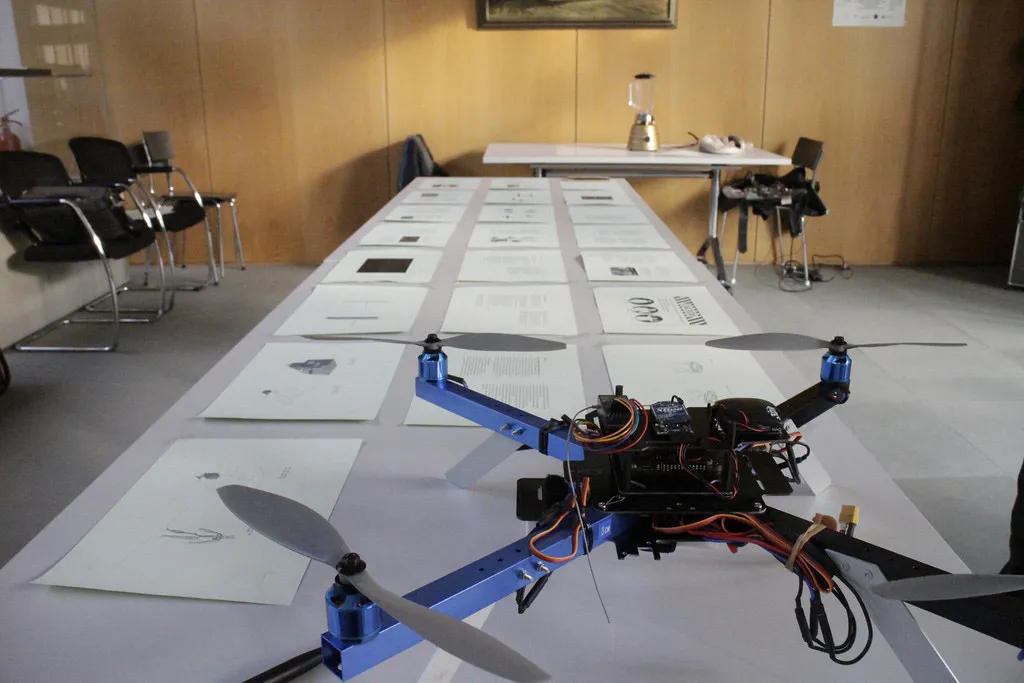
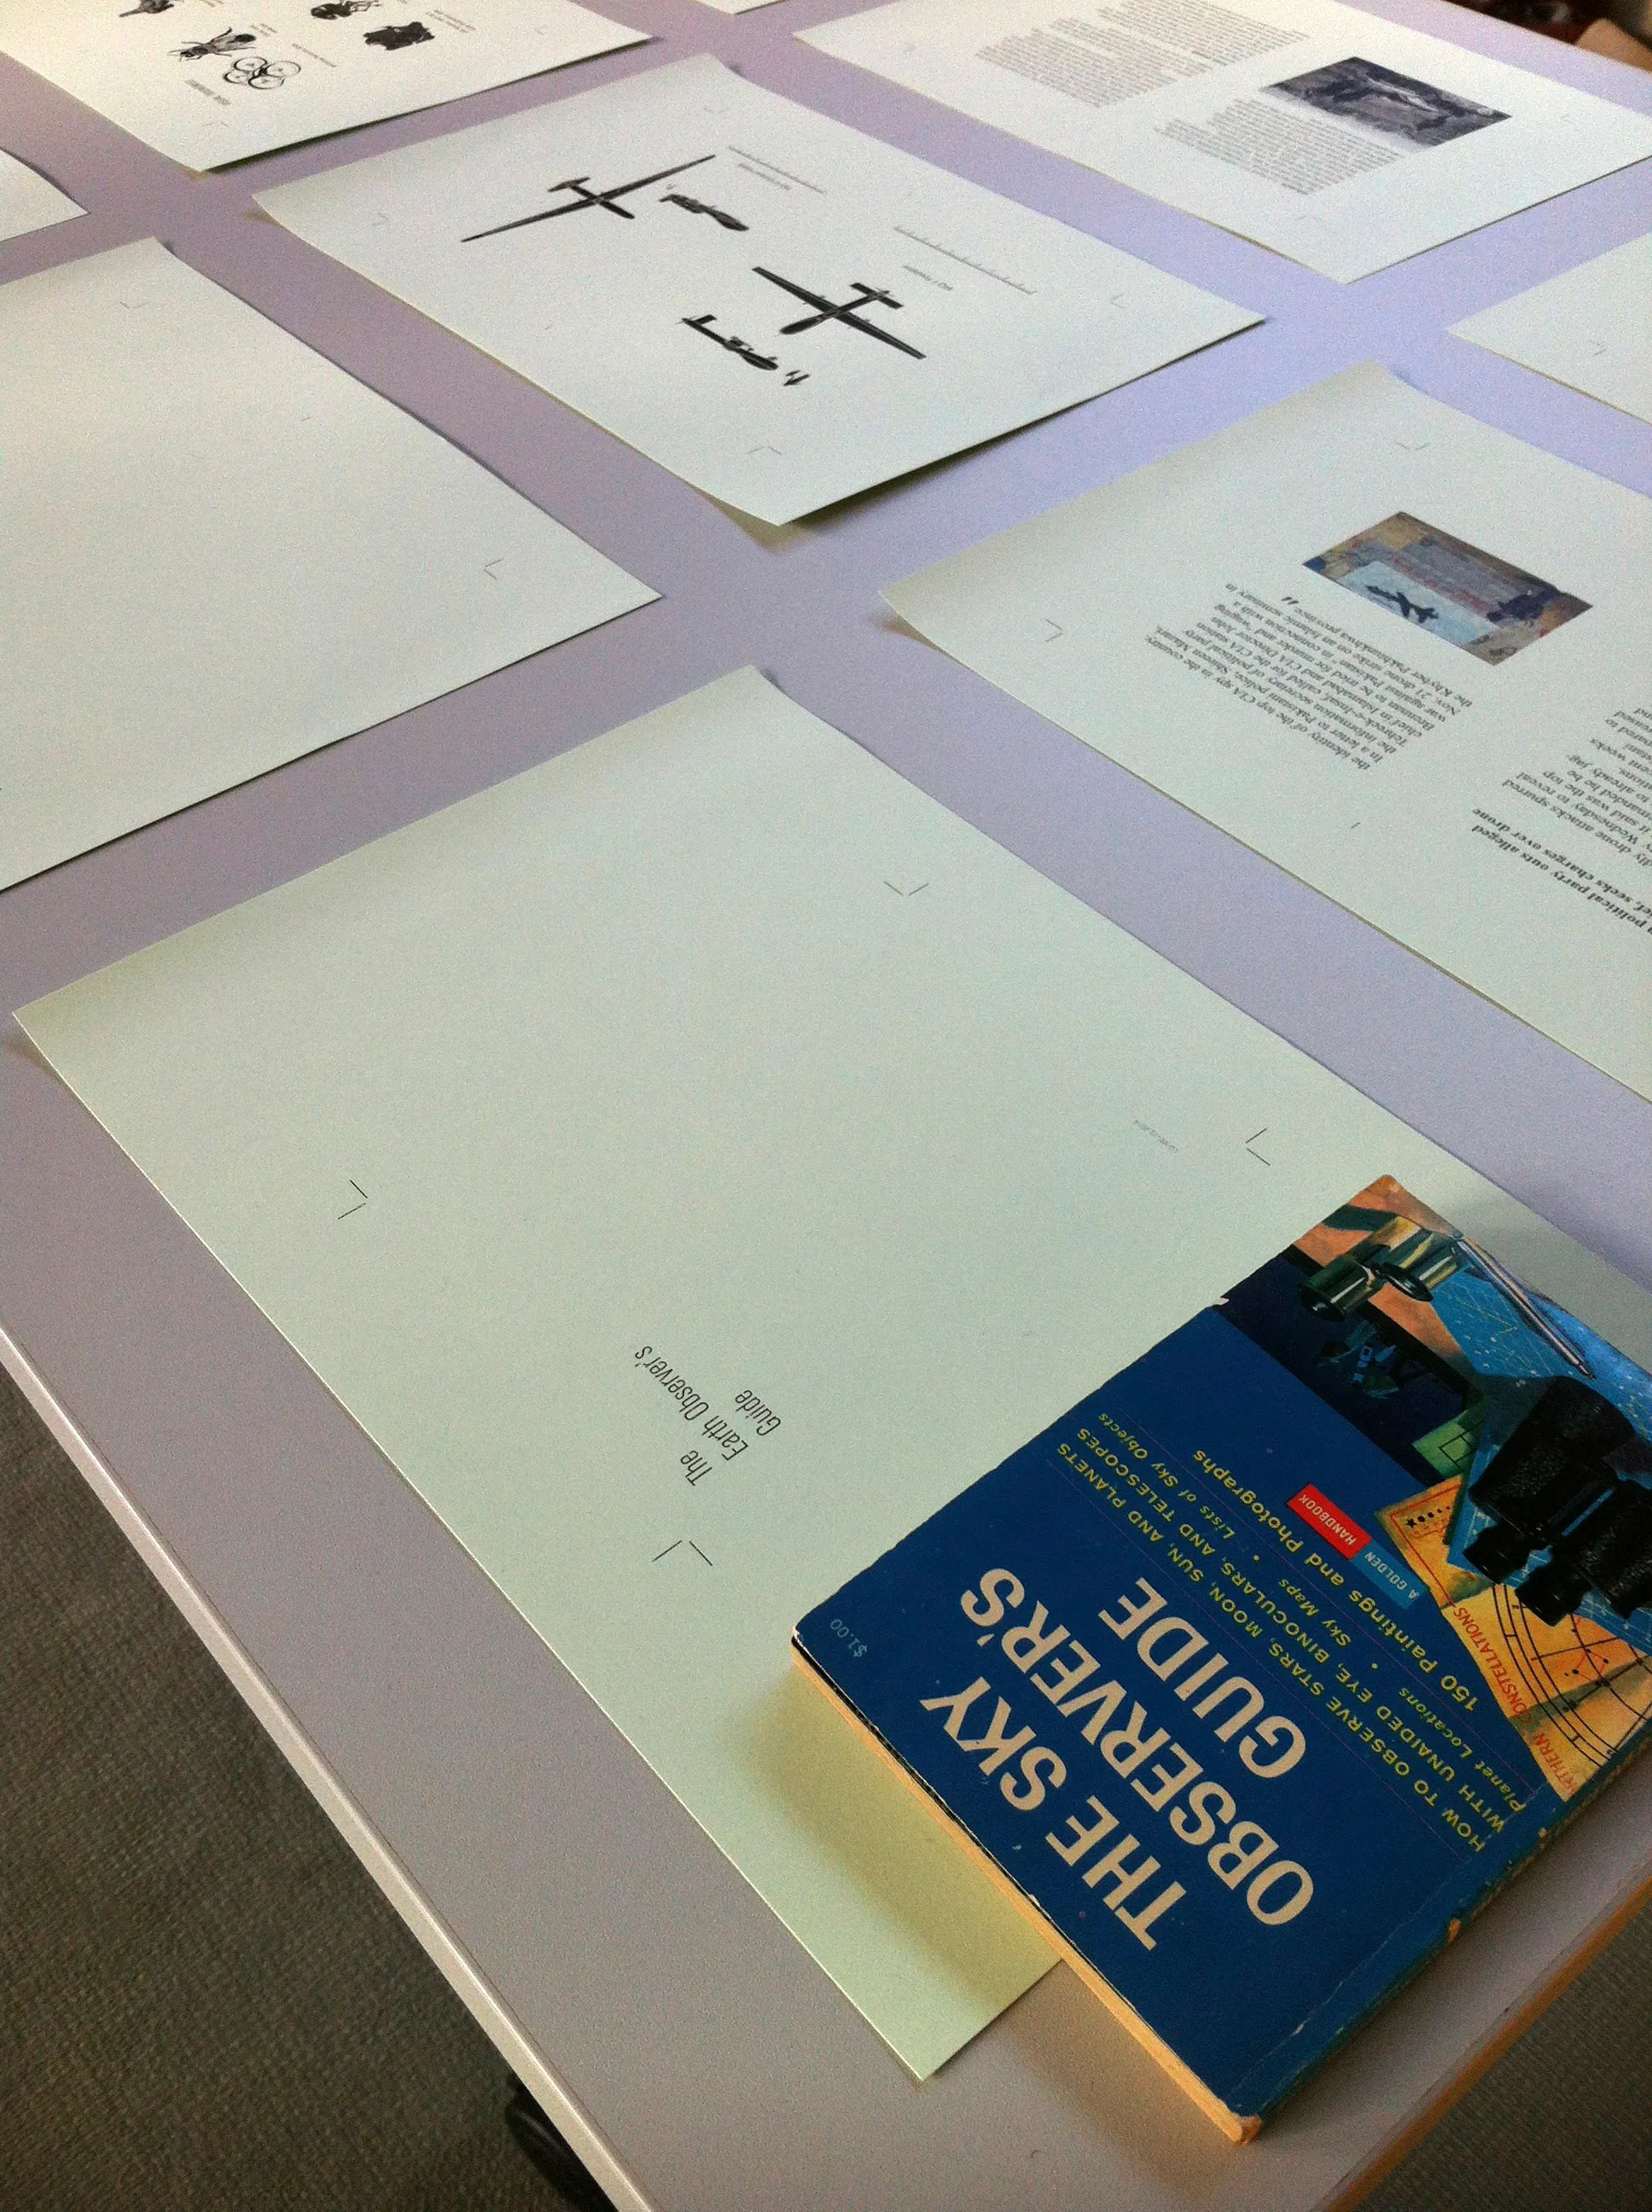
I worked in the Measure Drones group with colleagues, Kristian Lukic, Moritz Queisner, Boaz Levin, Daniel Herleth, Adam Kaplan, Frédéric Eyl, and Oliver Lerone Schultz (one of the coordinators of Taking Care of Things along with Christina Kral). Together, over the course of two days, we worked together to conceive, research, write, illustrate, and design a booklet called “The Earth Observation Guide.” This is not a history of art about drones, nor does it try to tackle the whole subject. Rather it is more akin to a time capsule that preserves a moment in time before drones are widespread. It acts as a guidebook, recording what is known about their past and present, illustrating shifts and concerns, and addressing how humans might understand their future. Here are some images of the presented work on the third day:

IMG_5074

IMG_140115_PML+HoL+CDC_Taking-Care-of-Things_Stadtarchiv-Lueneburg_0434-XL

IMG_5070

IMG_140115_PML+HoL+CDC_Taking-Care-of-Things_Stadtarchiv-Lueneburg_0596-XL

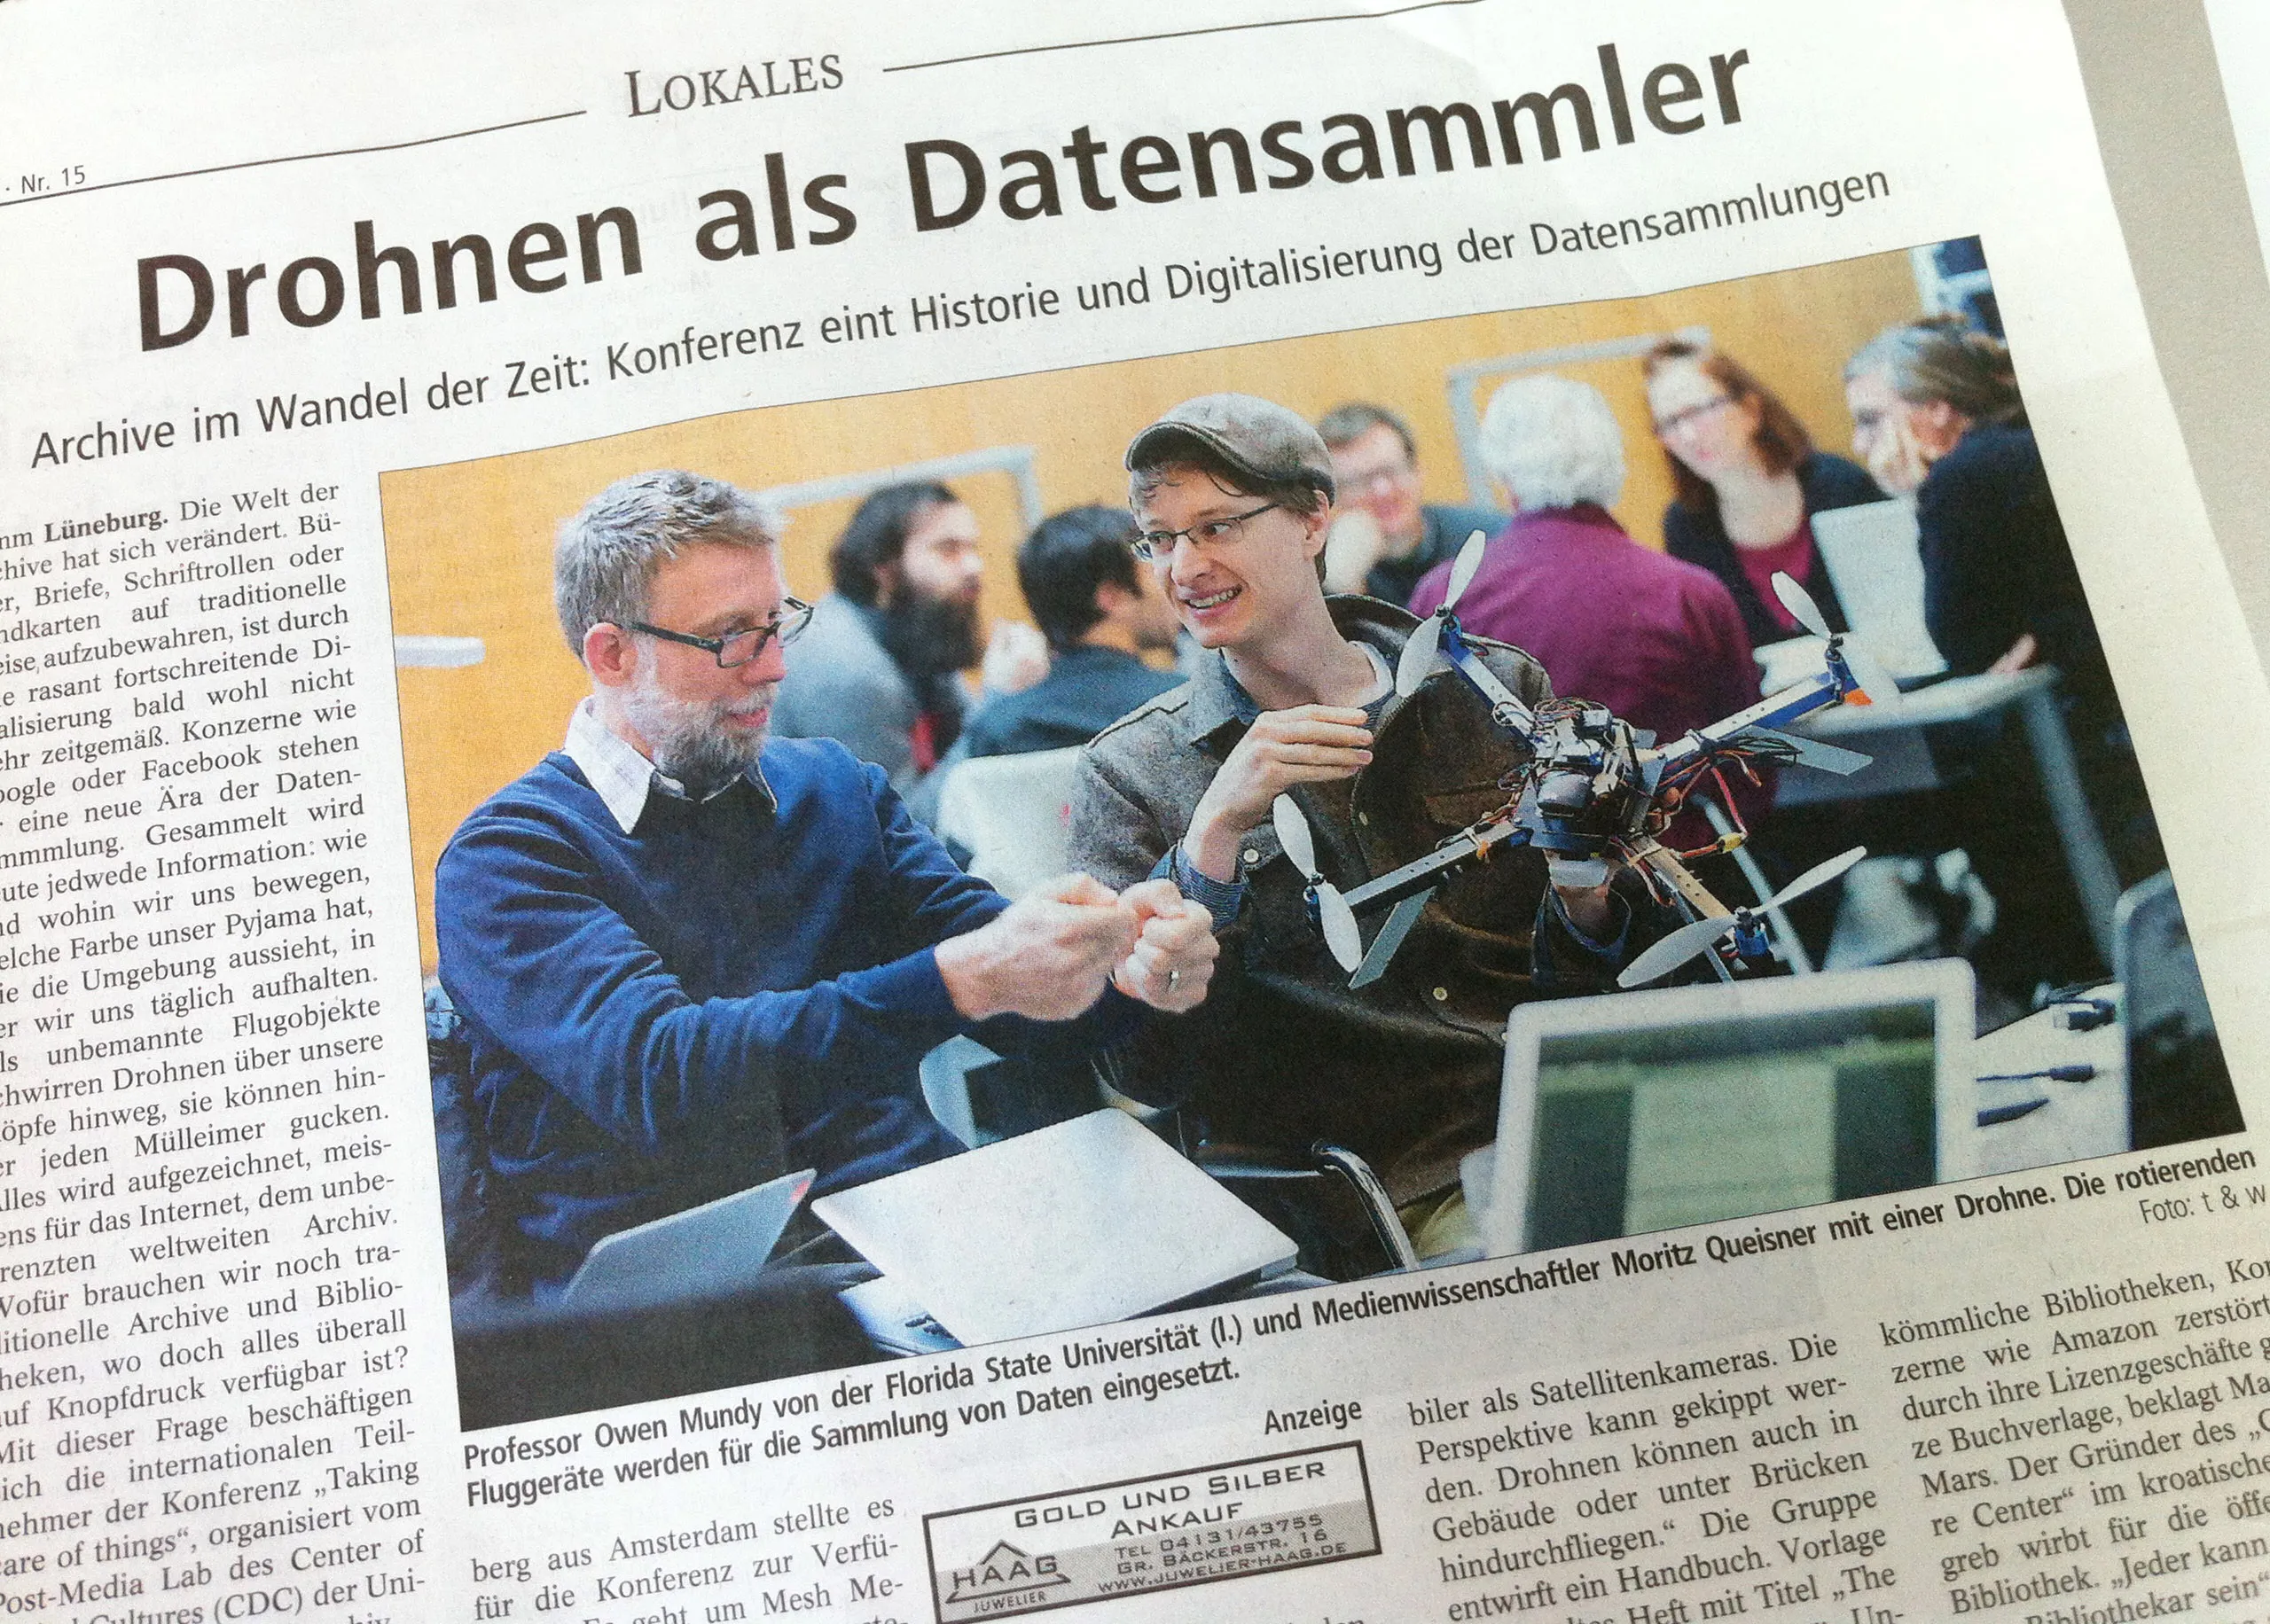
I also somehow managed to get my mug in the newspaper in Lüneberg. I think it says “American professor launching spy drones in Germany” or some such thing.

IMG_5062

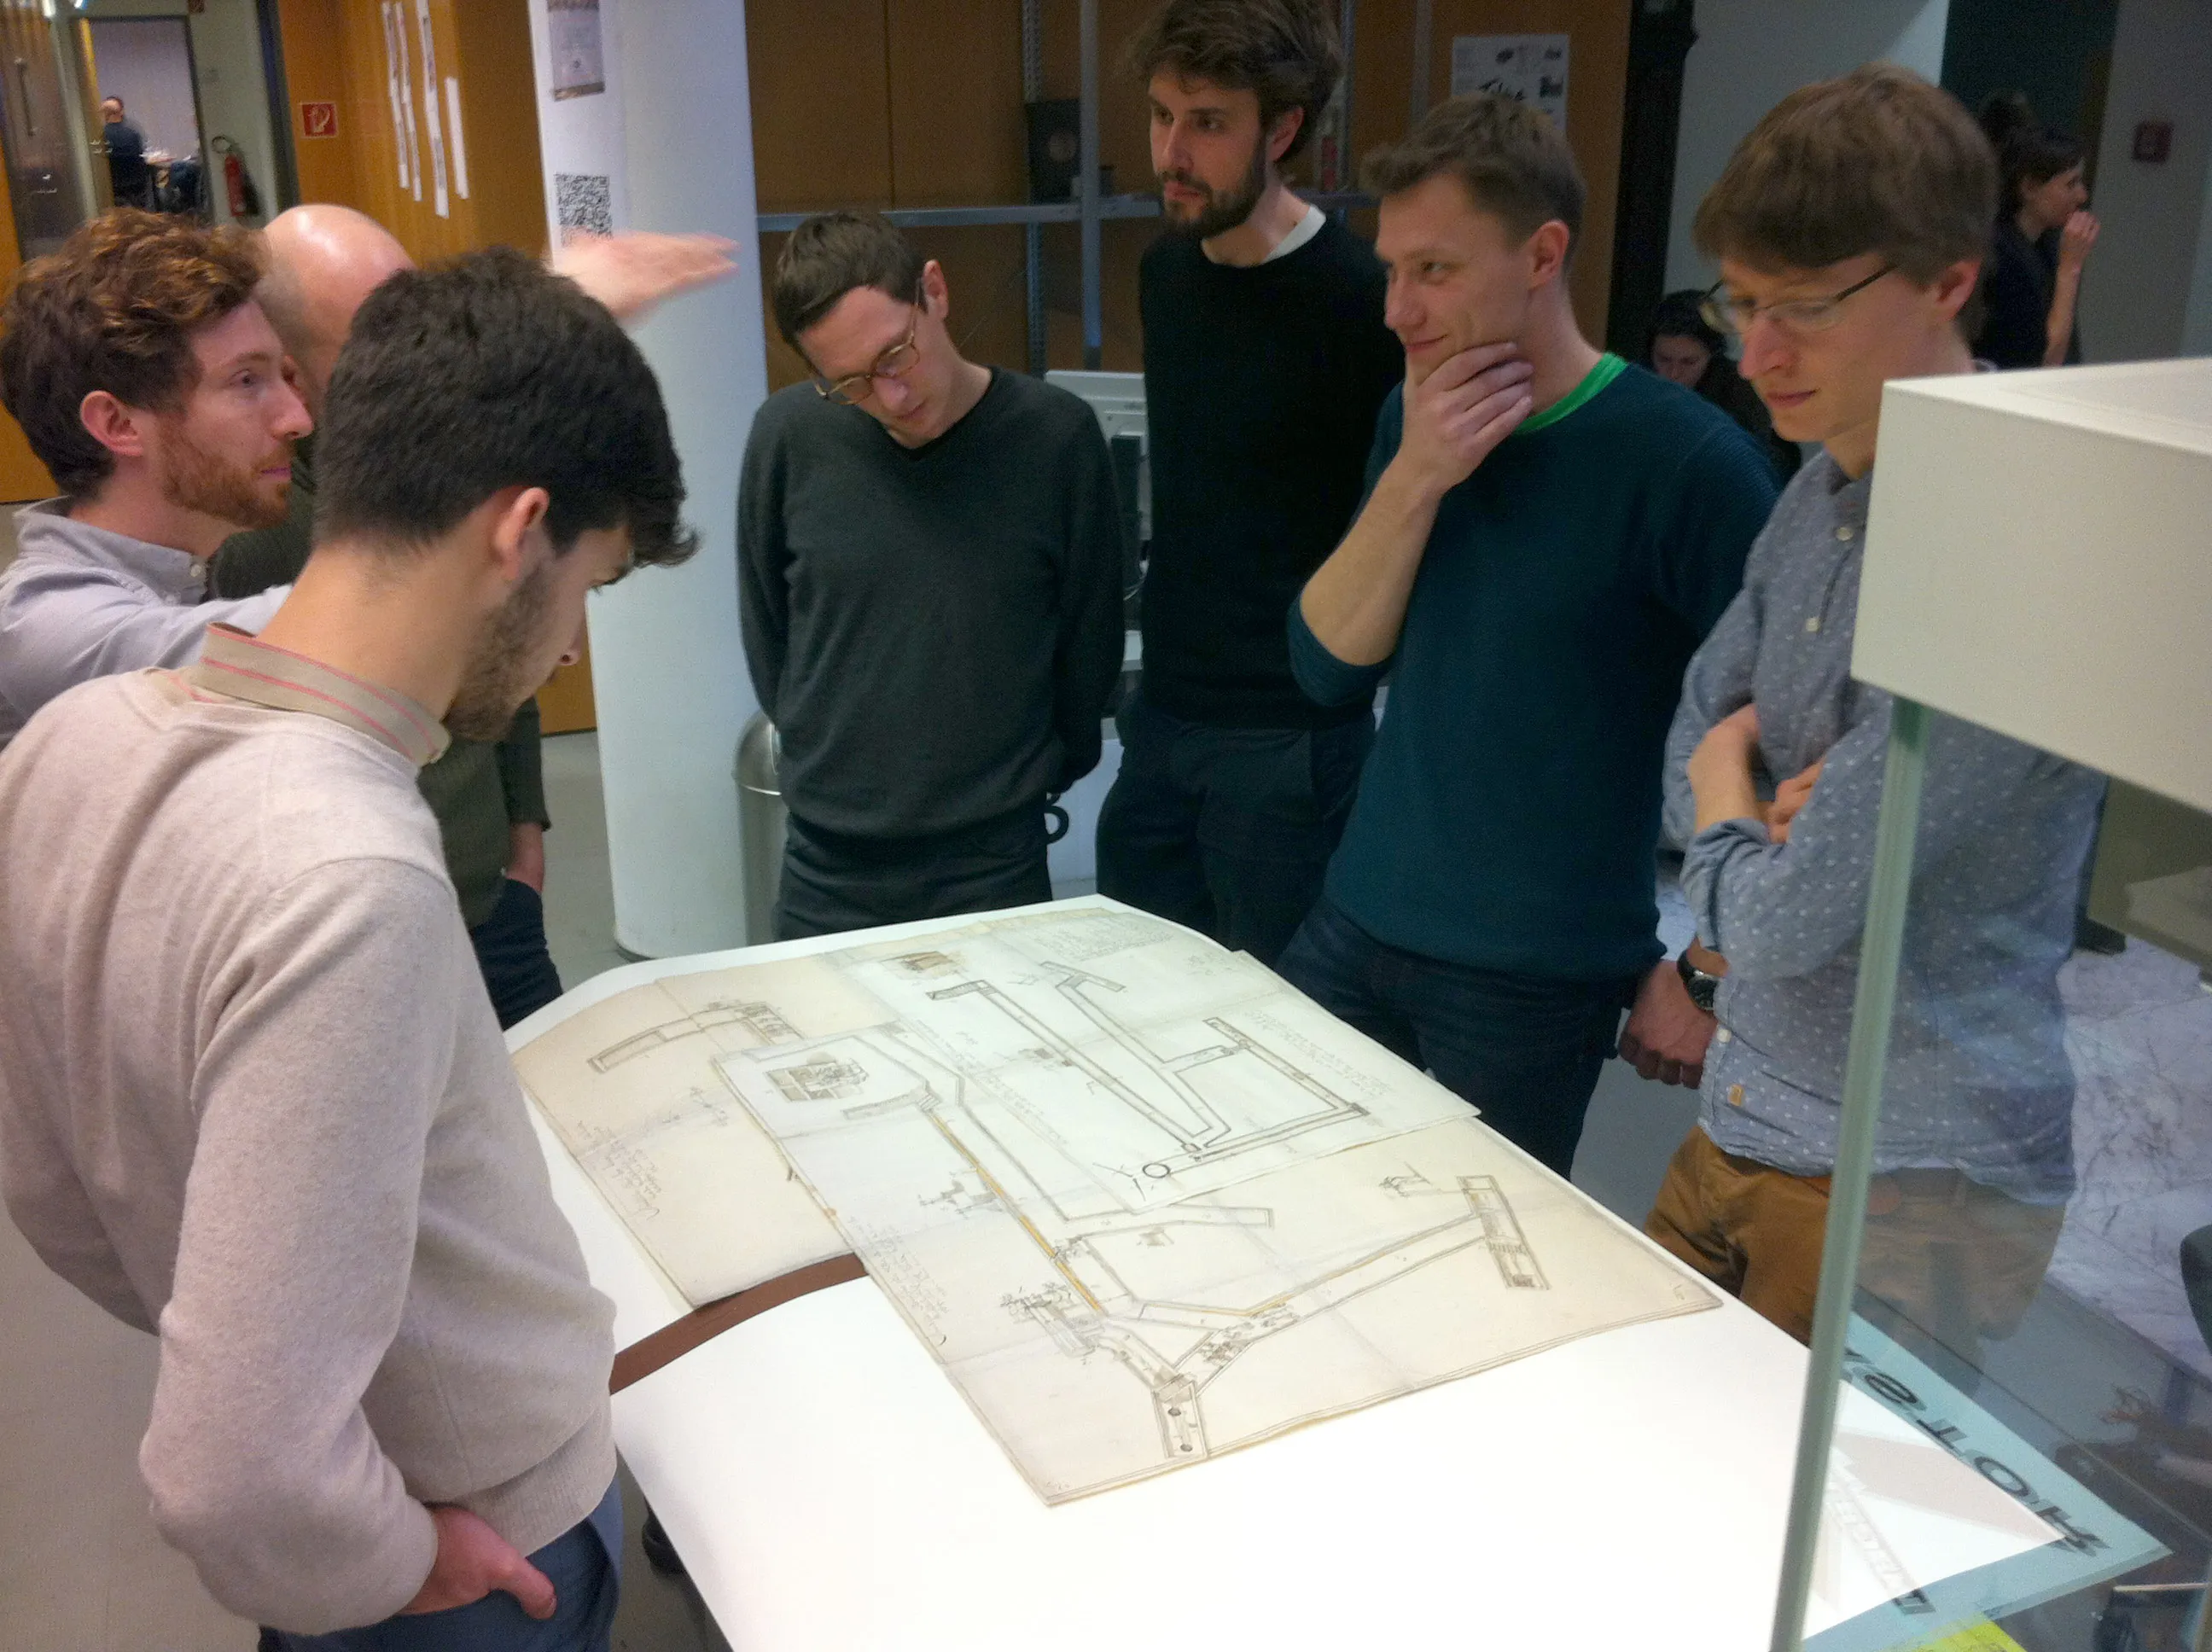
The group examining 16th century drawings of salt mines from the archive.

IMG_5058

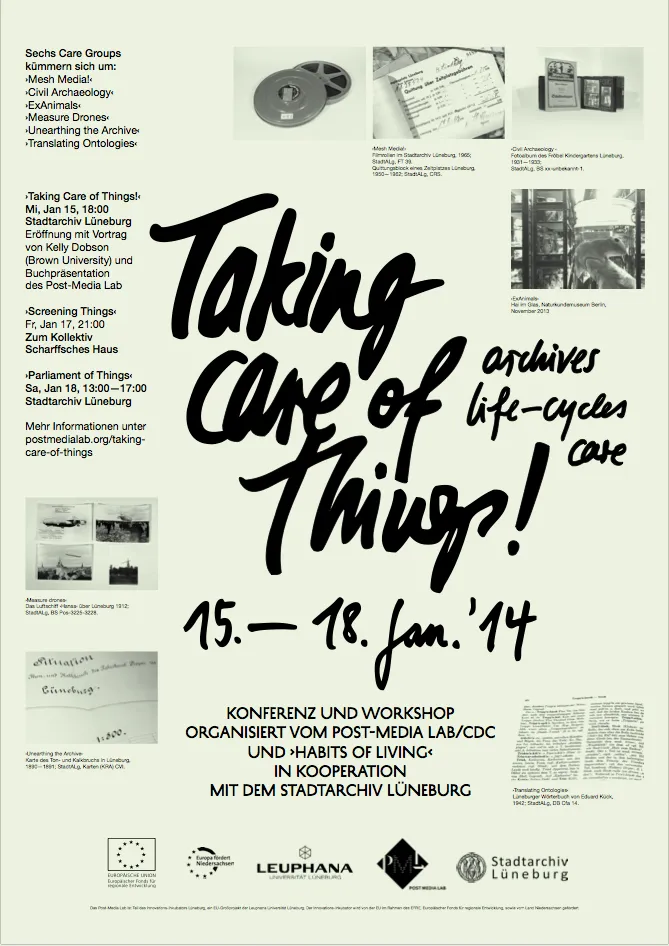
Taking Care of Things! Archives, Life-Cycles, Care, Lüneberg, Germany

Excited to be heading to Lüneberg, Germany, tomorrow for this conference organized jointly by Habits of Living (Brown University, CIS Bangalore) and the Post-Media Lab in conjunction with Stadtarchiv Lüneburg.
TakingCare_poster

January 15-18
Taking Care of Things!
Archives – Life-Cycles – Care
organized by Post-Media Lab/CDC and Habits of Living in cooperation with the Stadtarchiv Lüneburg

Venue: Stadtarchiv Lüneburg, Germany

From the perspective of current theoretical approaches the figure of the archive seems to have lost its central status and its fever. Meanwhile, in our medial and cultural set-up new (kinds of) archives seem to crop up everywhere, accelerated by new means of production and distribution. Cultural repertoires are being remixed alongside technological repositories – often giving new life to almost forgotten relics. Ever more things, valuables, processes, projects, constituencies, even movements, need to be taken care of. It is not only cultural and critical theory that is being challenged, but also law, the natural sciences and design, alongside other applied sciences. But what are the complex dynamics and contexts of these new (non-)archives? Do they really make sense? And if so, by and for whom?

To address these questions, ‘Taking Care of Things!’ focuses on the transformation of things – analog and digital – into life-cycles and specific practices of care. This will be done in different thematic groups dealing with topics, like Mesh Media!, Civil Archaeology, Measure Drones, Unearthing the Archive, Translating Ontologies and Extinction in Context.

This workshop will address such fundamental changes in archiving and objects by generating practices and chances to take care of things. That is, we will seek to extend (or sometimes end) the life-cycle of objects not by simply preserving them (this usually guarantees they will be forgotten), but rather through acts that respond, react, and/or reuse.

‘Taking Care of Things!’ will be based at and operating from the Stadtarchiv Lüneburg, the city’s rich and still to-be-further-explored archive, headed by Danny Kolbe.

‘Taking Care of Things!’ will start Wednesday evening (Jan 15) with a public talk by Kelly Dobson (Brown University) and followed by short introductions by Oliver Lerone Schultz, Nishant Shah and Wendy Chun to set the scene for the following days. Clemens Apprich together with Marcell Mars will then turn the evening into a Public Library, offering the first charge of Post-Media Lab publications as free downloads.

Thursday and Friday (Jan 16-17) will be reserved for intensive exchanges and workshops among the invited participants, all of whom deal very differently and critically with post-medial (non-)archives. There will be the opportunity to interface with the Lüneburg public, assembling archival objects of different kinds. On Saturday (Jan 18) all these activities will culminate in a public presentation and fair under the umbrella of ‘Parliament of Things’ held at the Stadtarchiv.

‘Taking Care of Things!’ will create multiple interweavings not only with the rich repository of the Stadtarchiv, but also with the multiple potentials of existing and new collaborations around the Center for Digital Cultures – possibly starting some repositories that will carry on into a future, where the Post-Media Lab will have been supplanted by other, new life-cycles.​

‘Taking Care of Things!’ is a collaborative event between Habits of Living (Brown University, CIS Bangalore) and the Post-Media Lab in conjunction with Stadtarchiv Lüneburg.
This event will mark the conclusion of the first life-cycle of the Post-Media Lab by bringing together former fellows and new participants.

Among the participants are: Adnan Hadzi and James Steven (DeckspaceTV), Femke Snelting and Michael Murtaugh (Constant/Active Archives), Eric Kuitenberg and David Garcia (Tactical Media Files), Boaz Levin and Daniel Herleth and Adam Kaplan (The Rise of Data), Fabian Giraud and Inigo Wilkins (Glass Bead), Jonathan Kemp and Martin Howse („Stack, Frame, Heap –SFH)”, as well as Memory of the World (Marcell Mars), Mathias Fuchs (Gamification Lab), Cornelia Sollfrank (Giving What You Don´t Have), Hauke Winkler (Freifunk Lüneburg), Robert Ochshorn (InterLace), Tapio Makela (M.A.R.I.N.) [had to cancel bec of illness], Fabrizio Augusto Poltronieri (MaisZero), Rodrigo Novaes (Flusser Archiv/UdK), Owen Mundy, Kristian Lukic (NAPON), Vahida Ramujkic (irational), Volker Grasmuck (CDC/Grundversorgung 2.0), Kilian Froitzhuber (netzpolitik.org), Vincent Normand, Jeremy Lecomte, Ida Soulard, Erich Berger, Connie Mendoza, and more.

Coordination & Care
Christina Kral: christina.kral@inkubator.leuphana.de
Oliver Lerone Schultz: oschultz@leuphana.de

Team
Wendy Chun, Nishant Shah, Clemens Apprich, Josie Berry Slater, Anthony Iles; and Nora Hannemann, Sina Hurnik, Nina Kersten, Ann-Kathrin Wagner, Nicolas Schrape
Packet Switching project: ColladaFragmenter software, Kassel, Germany and University of Florida Public Commission

3d_model_in_Rhino_1024w

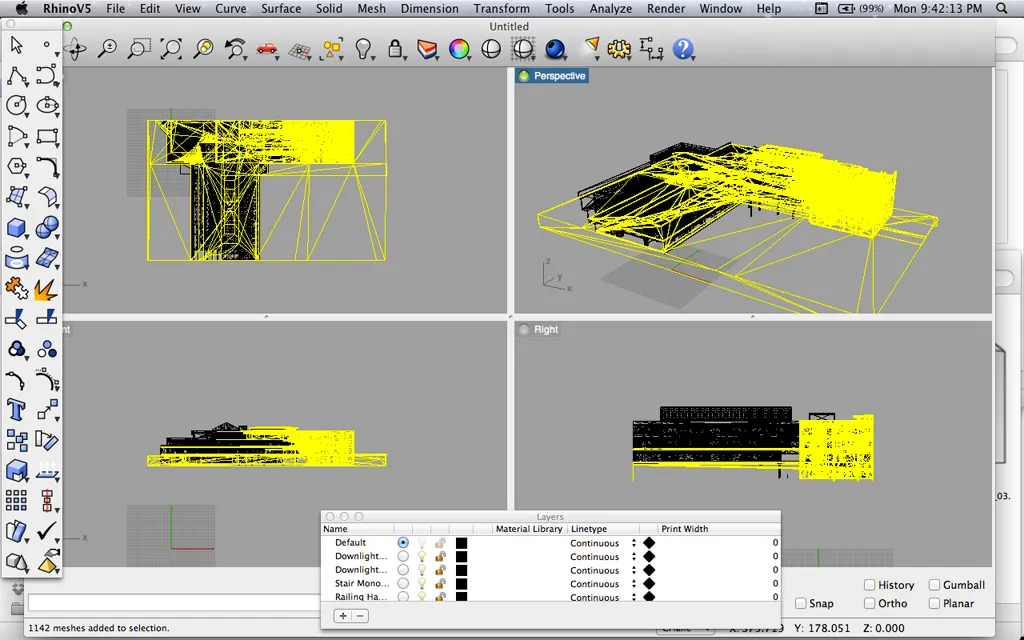
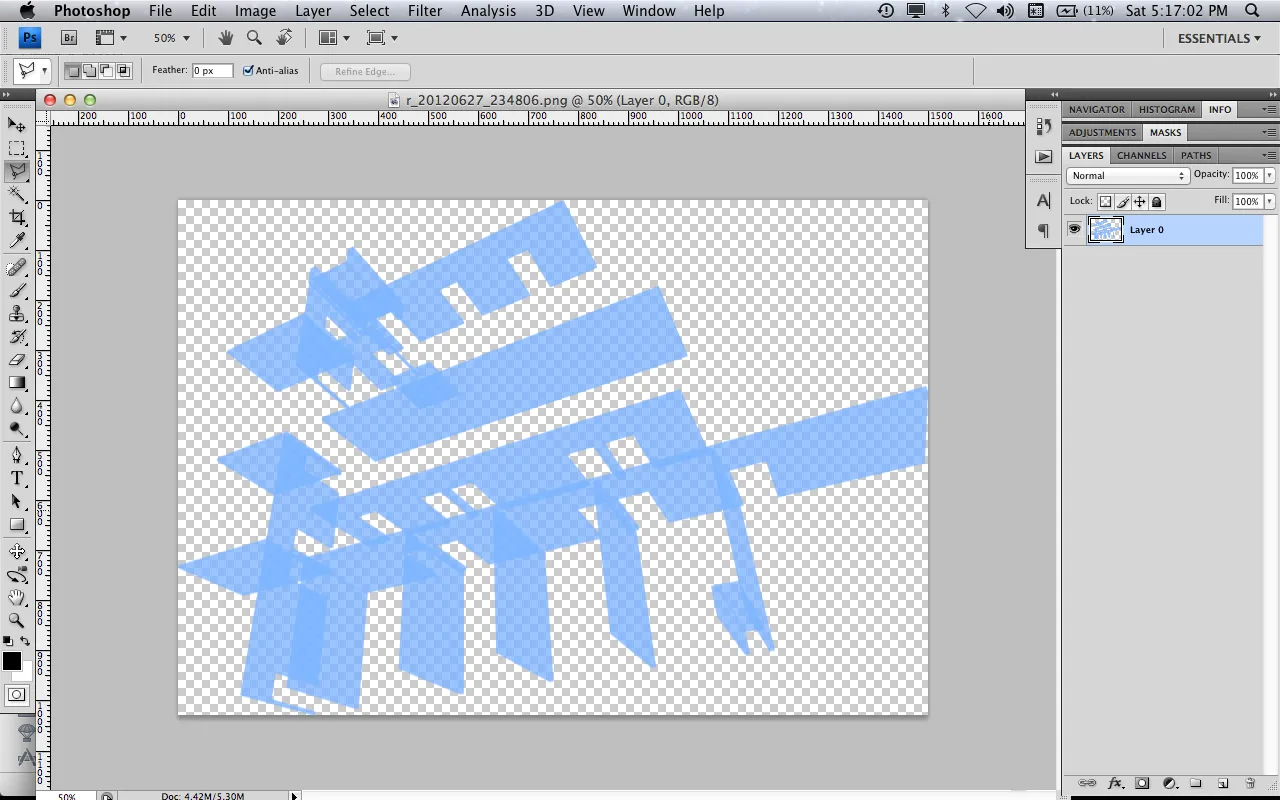
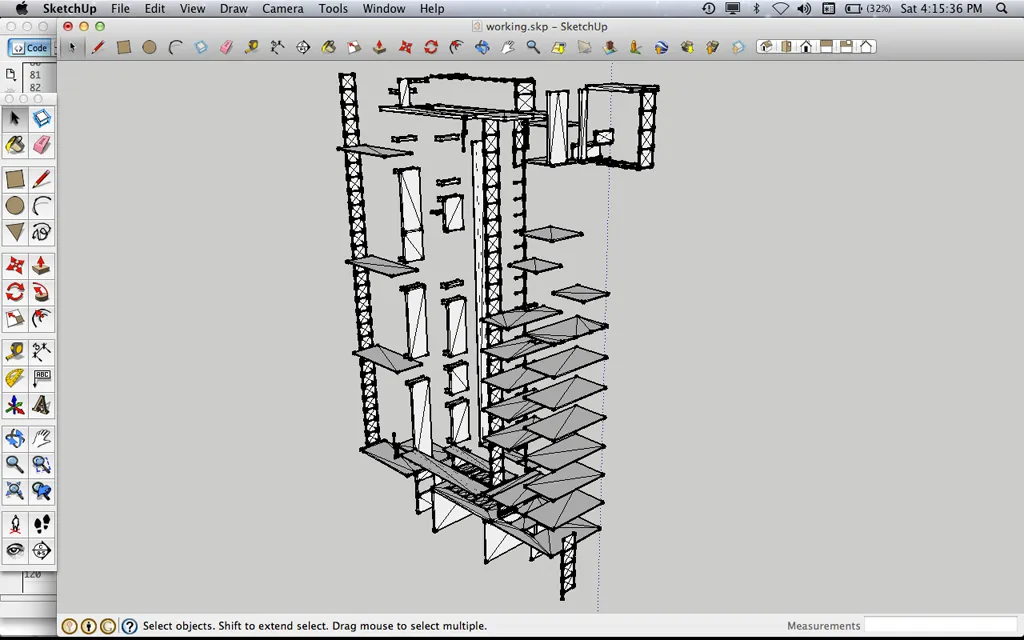
Joelle Dietrick and I embarked on a new body of work this summer called “Packet Switching.” Inspired by her Sherwin Series images and wall paintings, and my work deconstructing and re-visualizing source code and other data, we’ve created two new software projects, as well as a series of limited edition prints, large photo installations, wall-sized paintings, and animations.

3d_model_in_pshop

The full statement explains our process and intent clearly:

Packet Switching is an ongoing body of work by Joelle Dietrick and Owen Mundy that visualizes architecture as fragments affected by economic and communications systems.

The title of the series references how contemporary communications systems break digital files into smaller manageable blocks of data called packets. Each packet is then sent through a network, taking the quickest route possible, and reassembled once they reach their destination. One JPG image, for example, might be broken into several packets, each of which may travel a different path through the net, even through different cities, before being recompiled into a copy of the original file.

To reference this common process used in networked systems, we wrote custom software that deconstructs a 3D model’s source code and produces unique fragments. We further remixed these fragments using an original application created in Processing. The resulting images become limited edition prints, large photo installations, wall-sized paintings, and animations.

Our process underscores how incidental fragmentation and automation can streamline markets, but also make them vulnerable to systems failure. The use of architecture specifically points to recent real estate market volatility and considers how communication technology-enabled pursuits of profit margins alters our most basic needs.

3d_model_in_sketchup_01_1024w

The first software, that “deconstructs a 3D model’s source code and produces unique fragments,” is open source and available on Github. Essentially, the PHP software, parses a 3D COLLADA file and exports a set number of geometries, that can then be further broken down and used in an artwork or design.

The second software, which we will release soon, remixes these fragments using Processing. The video below shows an example of the whole process.

Wall painting at “Temporary Home” in Kassel, Germany

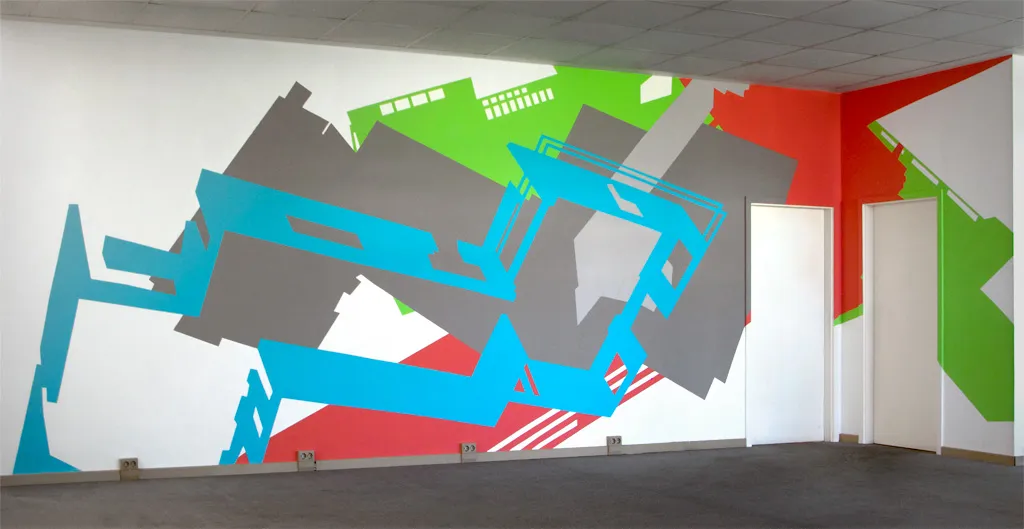
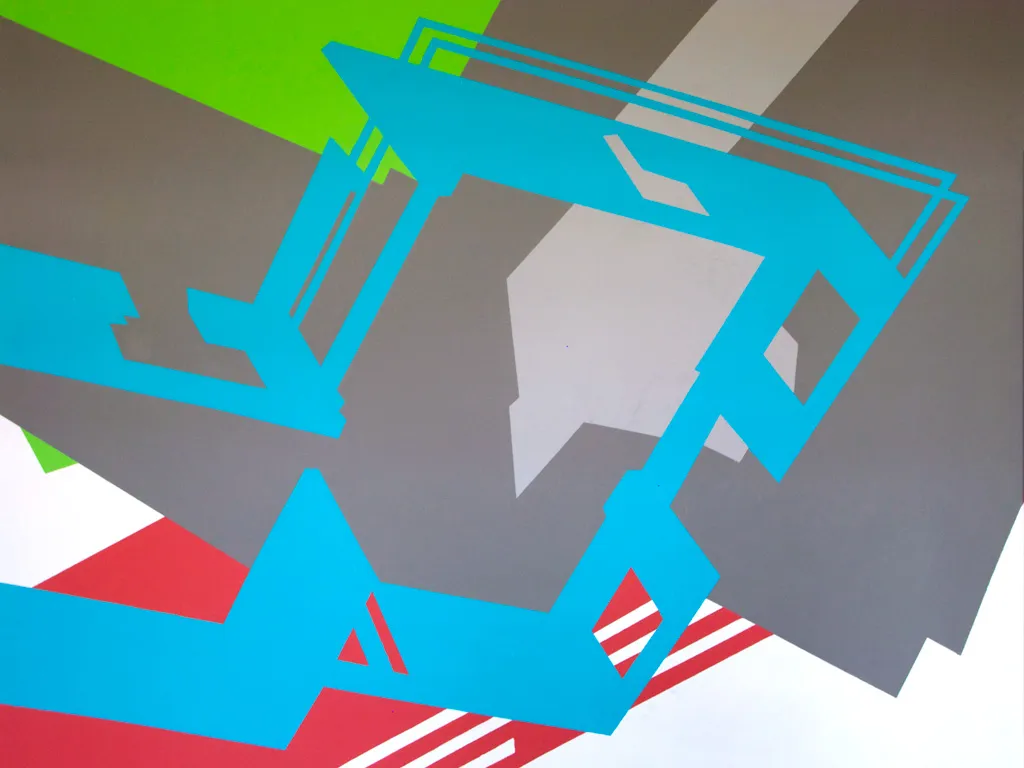
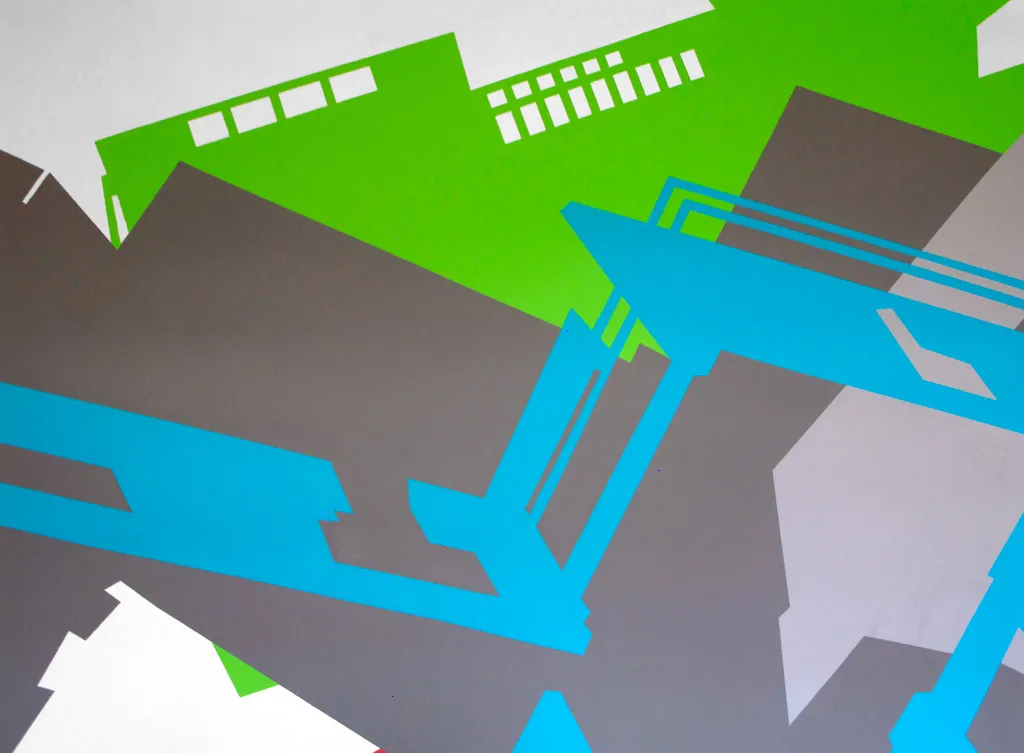
While artists-in-residence at Temporary Home, in Kassel, Germany, which coincided with Documenta13, Joelle Dietrick and I completed a wall-sized temporary painting based on the architecture from the Bauhaus School at Dessau and 2012 American color forecasts.

temphome_06_1024w

temphome_08_1024w

temphome_11_1024w

Commission at Weimer Hall at the University of Florida

Joelle and I have also received a commission to complete Packet Switching (Weimer Hall) at the University of Florida College of Journalism and Communications this fall. This will be inkjet on adhesive polyester on a large wall (approx. 177.5 ft. x 20.2 ft.). More details soon.

Give Me My Data: A Facebook Application Inspired by the Stasi Files Controversy, talk at DAAD Meeting in Dresden, Germany

fb-home-Freiheit für meine Akte!

Giving a talk today in Dresden, Germany titled, “Give Me My Data: A Facebook Application Inspired by the Stasi Files Controversy.” Here is the abstract.

During the final days of the German Democratic Republic (or GDR) it became evident that the Ministry for State Security (more popularly known as the “Stasi”) was destroying incriminating evidence from its 40-year history of domestic and international surveillance. These documents, which the Stasi was attempting to destroy using shredding machines, as well as by hand when the machines failed, included information gathered through various clandestine methods about lives of citizens of the GDR without their knowledge or consent.

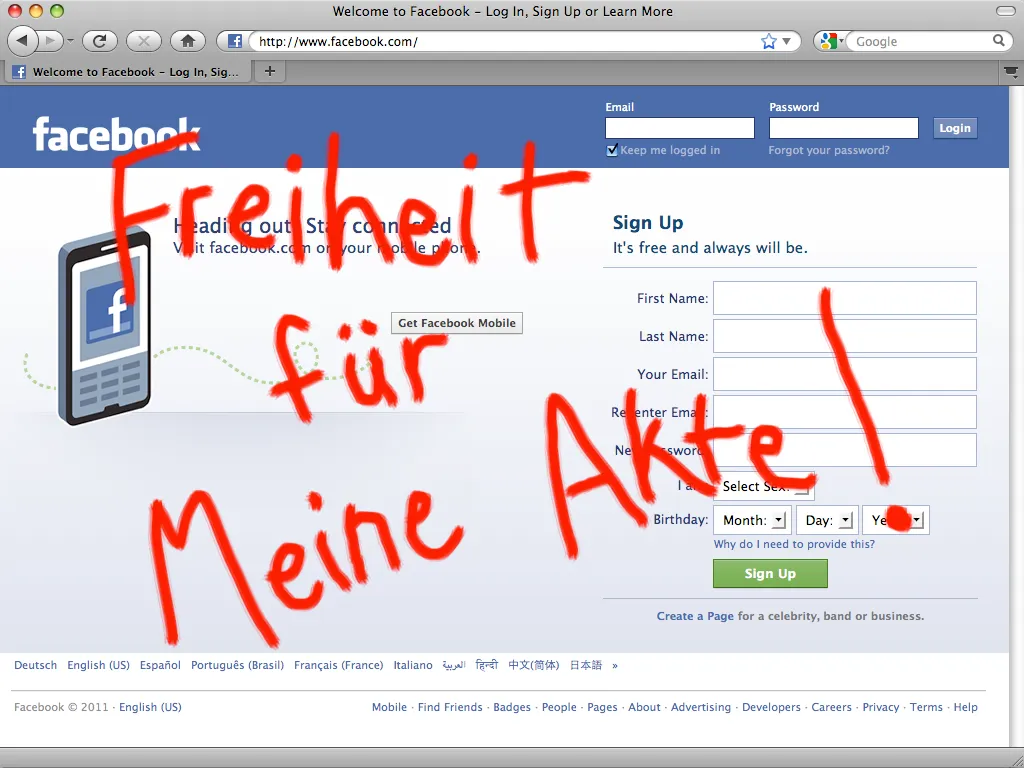
On January 15, 1990, protestors stormed the Stasi headquarters in Berlin in attempt to prevent the destruction of personal records which they felt they should be able to access. The phrase, “Freiheit für meine Akte!” (in English: Freedom for my file!) spray painted on the Stasi guardhouse during this protest embodies a desire by citizens to open this closed world of state surveillance in order to understand the methods of control employed the Stasi

This moment in history inspires my ongoing project, Give Me My Data, a Facebook application that helps users export their data out of Facebook. While clearly utilitarian, this project intervenes into online user experiences, provoking users to take a critical look at their interactions within social networking websites. It suggests data is tangible and challenges users to think about ways in which their information is used for purposes outside of their control by government or corporate entities.

At the height of its operations, the Stasi is believed to have hired, between spies and full- and part-time informants, one in every 6.5 East German citizens to report suspicious activities, almost 2.5 million people.1 At this moment, the ratio of people entering data on Facebook to non-members is one in fourteen for the entire world,2 introducing possibly the most effective surveillance machine in history.

Germany and Google Street View

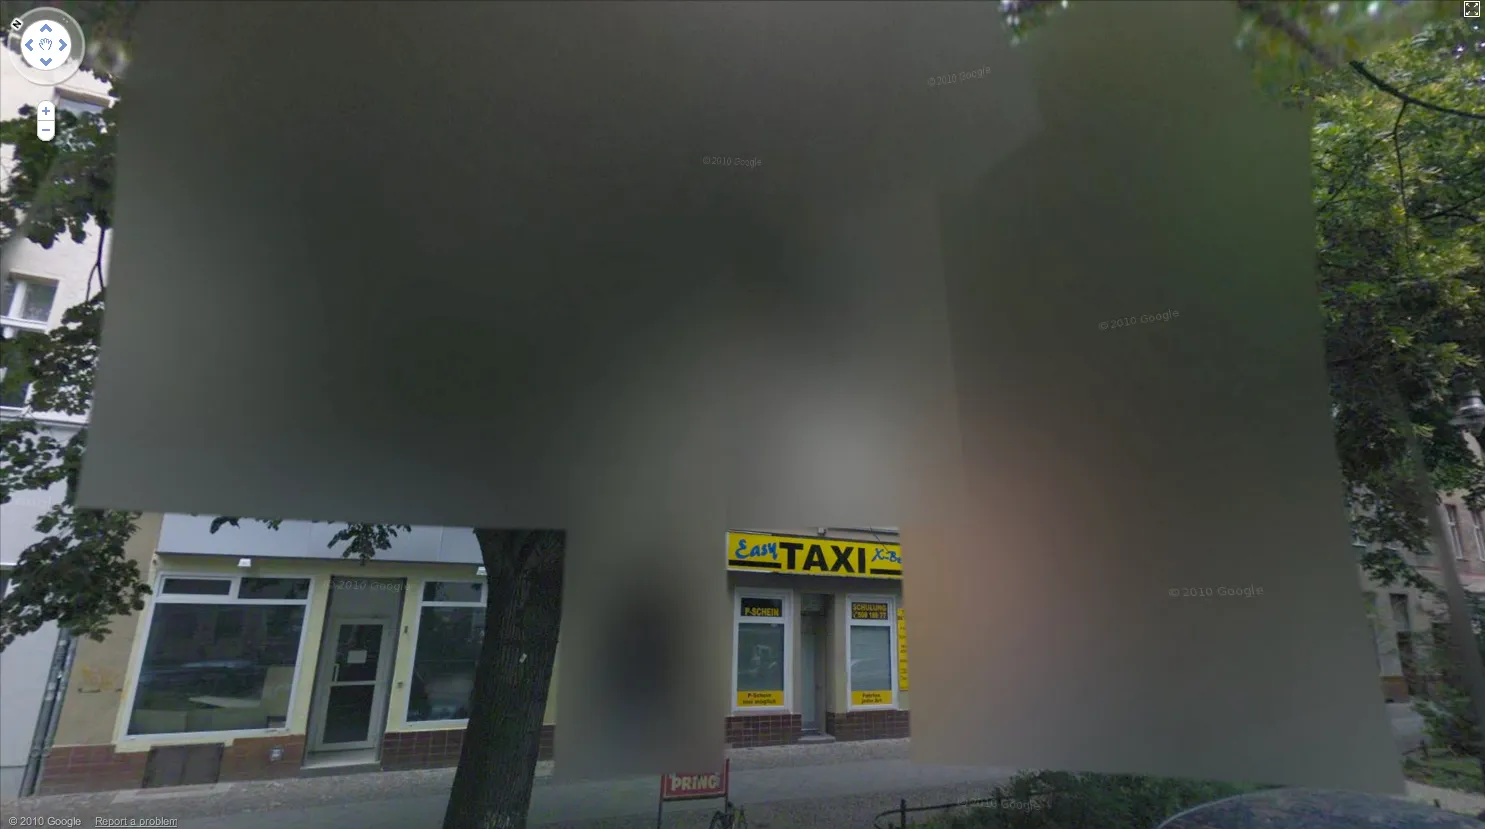
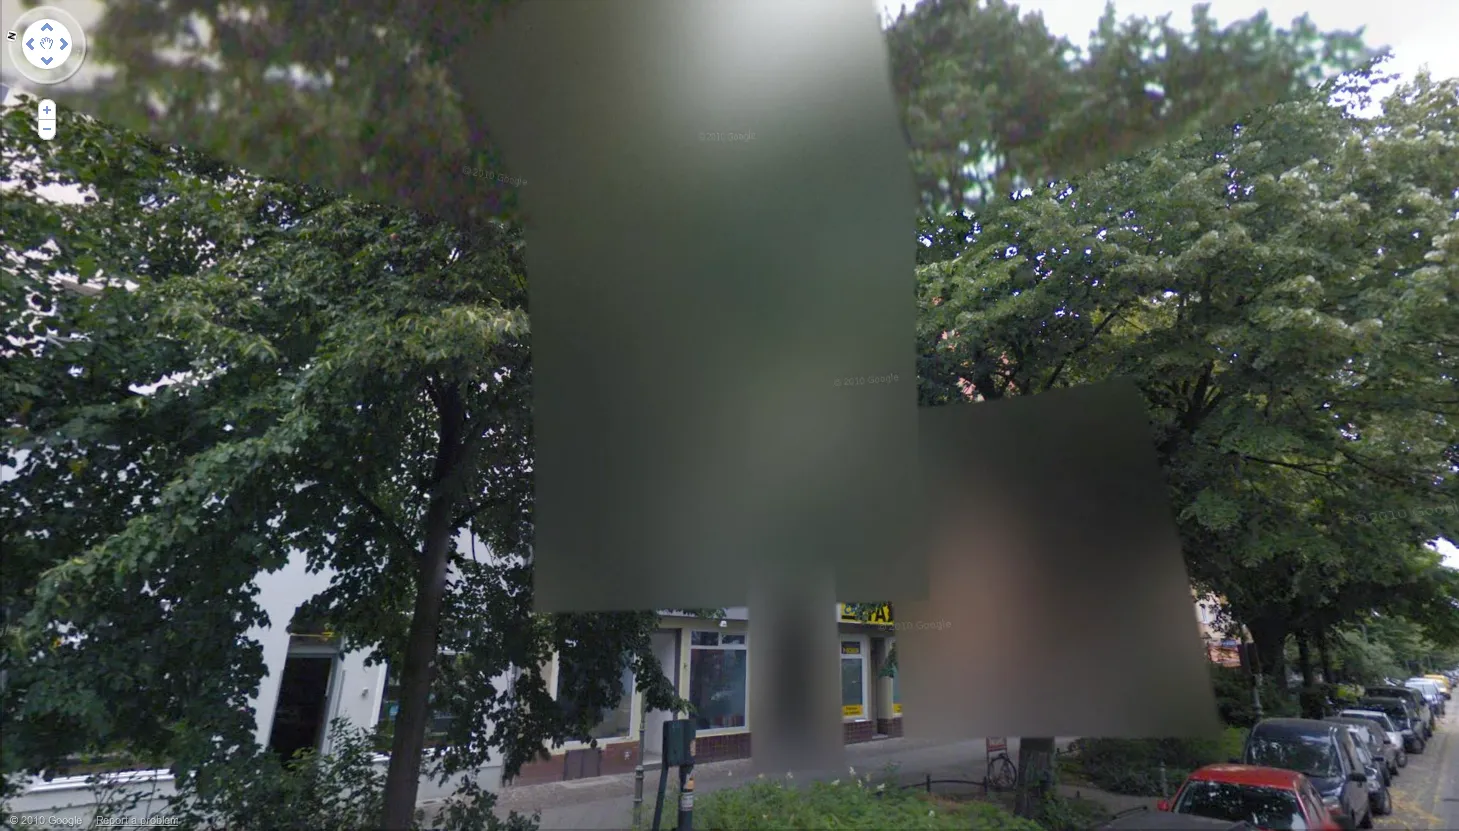
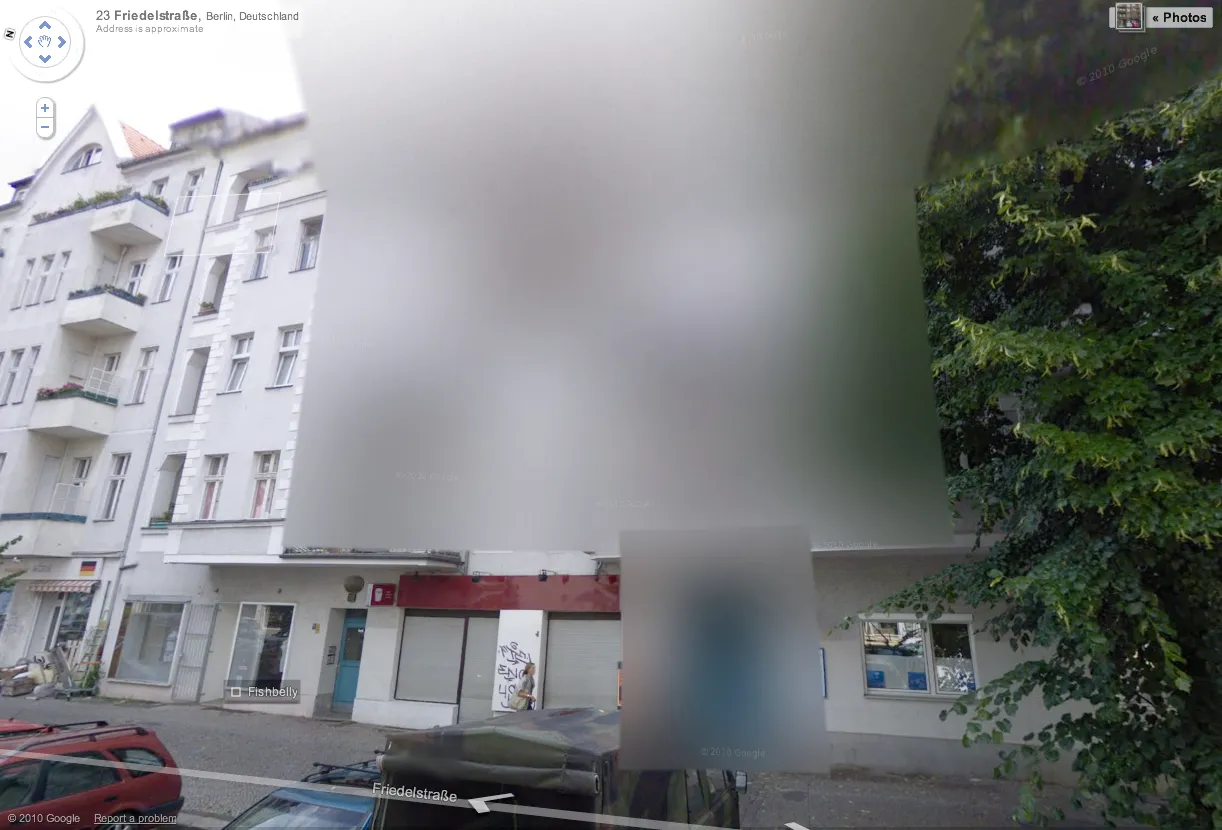
This week I have been enjoying the blurred images of German buildings whose owners have chosen to opt-out of Google Street View. Infamous moments in the country’s history have led Germans to take privacy very seriously; especially when it comes to information about their residences. Unlike the United States, where data privacy is an opt-out option, Germany law states that, “citizens must opt-in to have their data collected in any way.” (1). In fact, there is a document detailing the rights of the “data subject” in the German Federal Data Protection Act which serves “to protect the individual against his right to privacy being impaired through the handling of his personal data.”

An even more powerful gesture are the very public images that have resulted from this protection. While they serve a specific function—to obscure identifying aspects of buildings, faces, etc.—they also communicate very effectively the message that individuals should have the right to decide how their data is used. This gets to the heart of the Give Me My Data app—to prompt this sort of discussion. It is then ironic that Google, a company whose revenue is based almost completely on advertising opportunities made possible by aggregating and re-representing data, has inadvertently brought us this message.

I was excited to find my own apartment building in Berlin has been removed.

Picture 15

Picture 14

Another building down the street

Picture 1

Helge Denker, a reporter with the German daily, Das Bild, has found a clever way to opt-out.

helge

Die peinlichsten Einträge bei Facebook, StudiVZ und Twitter

565px-Bild_logo.svg

Give Me My Data mentioned in a Bild article:

Die peinlichsten Einträge bei Facebook, StudiVZ und Twitter The most embarrassing messages on Facebook, StudiVZ, and Twitter (English), May 22, 2010

Read the full translation

(translated from German) “Many users are unaware that their comments will be permanently stored in networks. For example Facebook can retrieve all stored Stautusmeldungen. The U.S. Professor Owen Mundy has a developed application, Facebook members ever entered all the data and displays the posts. Under “Select Data”, you select which data you want to see (for example, personal data, status messages). Here also dive old, long deleted on posts, which are provided with a time code. Facebook apparently never forgets.”

VideoChannel Cologne – Found Footage!

FFF – Found Footage Film collection
curated by Wilfried Agricola de Cologne

“Found footage is a filmmaking term which describes a method of compiling films partly or entirely of footage which has not been created
by the filmmaker, and changing its meaning by placing it in a new context. The term refers to the “found object” (objet trouvé) of art history.”

VAD – Video Art Database
VideoChannel Cologne – Found Footage!
http://and.nmartproject.net/?p=2770

Listed artists/directors:

Agricola de Cologne (Germany)
Borja Alexandre (Spain)
Michael Brynntrup (Germany)
Jon Keith Brunelle (USA)
Maria Canas (Spain)
Larry Caveney (USA)
Sebastian Clej (Romania)
John Criscitello (USA)
Dr. Boston (USA)
Bill Domokos (USA)
Angie Eng (USA)
Clint Enns (Canada)
Enrique Freaza (Spain)
Rajorshi Ghosh (USA)
Doron Golan (Israel)
Juan David Gonzalez Monroy (Colombia)
Grace Graupe-Pillard (USA)
Constantin Hartenstein (Germany)
Denise Hood (USA)
Leslie Huppert (Germany)
Andrea Huyoff (Germany)
Katrina Inagaki (USA)
Jeremiah Jones (USA)
Ellen Lake (USA)
Irad Lee (Israel)
Fumiko Matsuyama (Japan)
Alistair McClymont (UK)
Davor Sanvicenti (Croatia)
Alexander Mouton (USA)
Owen Mundy (USA)
Toban Nicols (USA)
Jonas Nilsson (SWE)
Jun Ho Oh (South Korea)
Renata Padovan (Brazil)
Lobo Pasolini (Brazil)
Johanna Reich (Germany)
Joao Ricardo (Portugal)
Jasper Rigole (Belgium)
Joshua Rosenstock (USA)
Benjamin Rosenthal (USA)
Anthony Rousseau (France)
Benjamin Schultz-Figueroa (USA)
Jennifer Schwed (USA)
Ran Slavin (Israel)
Dennis Summers (USA)
Sonja Vuk (Croatia)
Philip Widmann (Germany)
James Woodward (USA)
Andreas Zingerle (Austria)