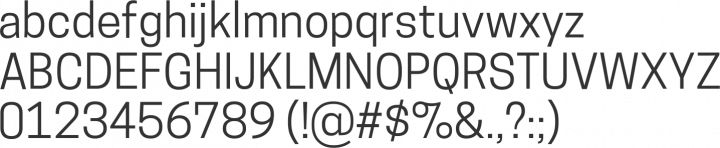Category: research

Convert a PHP/MySQL site to Jamstack and host on Github Pages

One of the first items on my sabbatical to do list last year was to convert the Camp La Jolla Military Park website to a static Jamstack site hosted at Github Pages. This post documents that process.

I originally created the site as a research tool using PHP and a MySQL database for data entry, to record, organize, and ultimately publish research about the military history of UCSD. Moving the project to Github Pages would simplify maintenance and hosting costs, but was no small task. Technically it didn’t cost me extra to host, but the domain was $20/year, which adds up. Further, maintaining a PHP/MySQL website with a custom admin tool requires a bit of overhead for security and updates. Additionally, I wanted to continue having the benefit of using template engines or some way to include files (like PHP’s require()) to save time coding the site.

There are a plethora of tools available to publish a database-driven site on a static host. They mostly can be categorized as follows (ordered by most to least dynamic data sources):

  • Move the database to a remote service like Firebase, Atlas, et al. — ⚠️ Ultimately creates vendor lock-in, potential hidden costs, and probably more maintenance issues in the future.
  • Create a static version of the database by converting MySQL to flat files (JSON, CSV, etc.), which still allows for querying using one of various tools — 🤔 This method is interesting, because it still decouples the data from the presentation and allows for potentially more options later, including a remote database. I am already using this in various forms but worry again about maintenance, or issues with the client’s ability to manipulate the data as needed.
  • Generate a static version of the site, including all its pages which contain the data formerly dynamically inserted from MySQL. — 🤔 I like this concept, and have been using it to auto-publish my class lectures and tutorials using Markdown and Grunt with Marp. Plus, there are many site generators to choose from, which I explore below.
  • Scrape the site and save pages as static files. After all, everything is static once the HTML is rendered on the frontend. — ⚠️ While fast, this requires the site be built first and would make updates difficult.

Essential Concepts

Here I outline some concepts on rendering. See SSR vs CSR vs ISR vs SSG for a more in-depth look:

  • Client-Side Rendering (CSR) (e.g. Single-Page Application (SPA)) – JS renders pages in client’s browser with empty HTML files + raw data from the server. (e.g. React, Vue, Angular)
  • Server-Side Rendering (SSR) (e.g. Fullstack) – Generates pages on server with dynamic data before delivering to client. Improves SEO and loading, decreases server performance. (e.g. EJS, PHP, or Next.js)
  • Static Site Generation (SSG) (e.g. JAMStack) – Pre-renders all pages as static HTML during build process. Fast loading times, enhanced security, and dynamic content can still be achieved via “islands”.
  • Incremental Static Regeneration (ISR) – Combines SSR and SSG to pre-render static pages during build time while periodically regenerating specific pages with updated data.
  • Edge-Side Rendering (ESR) – Rendering process is pushed to the CDN’s edge servers which handles requests and generates HTML. Requires Nitro engine.

Requirements

Requirements for most of the projects I mention above.

  1. Javascript-based
  2. The data will be static, but editable using Git
  3. The data should be searchable using a tool like chosen
  4. The site design will be simple, but I should have creative control
  5. The site will be public, and be presented mostly using the same design as the original site
  6. HTML/CSS validation + Accessibility checks
  7. Convert from Google Maps to Leaflet
  8. Host the site on Github Pages

While planning the project I also wanted to select a method I could use for other potential static (or nearly static) sites like:

  1. A new site documenting the hundreds of examples and overlapping categories of Critical Web Design and internet art I’ve been collecting for an upcoming book. Update: I built it with SvelteKit
  2. Converting tallysavestheinternet.com to a static site (currently SSR) and unlinking the extension from the server to use local data only
  3. Moving away from WordPress more generally (and its security problems) and blogging with Markdown instead, starting with this blog (NO MORE TYPING IN A WEB FORM!!)

It’s nice to learn new tools. I already have some experiences with React, Next.js, and Vue.js, but wouldn’t say I’m confident in any. I found that publishing apps using React Native is very frustrating and unreliable, and my general distrust of Facebook makes me lean towards Vue. Still, I went in with with an open attitude.

Tool Comparison

A breakdown of some tools I considered. Some of the icons are clickable…

FrameworkSPASSRSSGMDThemesSearchCons
Jekyll❌❌✅✅✅?❌ Ruby
Hugo❌❌✅✅✅?❌ Go
Astro✅✅✅✅✅✅React, Vue, Svelte in dynamic islands, simple routing
Vue.js✅✅✅✅✅?✅ vuepress
Nuxt.js✅✅✅✅✅?Built on Vue
SvelteKit✅✅✅✅✅✅MD rendering not native but supported via MDX
Next.js✅✅✅✅✅✅MD rendering not native but supported via MDX

Next

My experience with Next.js SSG was painful.

  • Constantly running into subtle changes in syntax across versions
  • Adding an image is ridiculously difficult.
  • Exporting the SSG ultimately created dead links, packaged up in Next code that was hard to understand.
  • So much automation to make a static site in the end you can’t do anything unless you have the exact right code, in the right version, in the right paths.
  • Error messages are rarely helpful or pinpoint the line number causing the issue in the stack.
  • I followed so many tutorials that ultimately ended in dead-ends, incorrect versions, or that completely didn’t work.

Astro

I ended up choosing Astro for the final project, which can be seen here https://omundy.github.io/camplajolla/. While they appear to have many similarities, I found Astro soooooo much easier than Next.js. It’s fairly simple to install, even using a starter theme, and it didn’t take long torip out tailwind to add bootstrap.
Stasi / Facebook / Big Data DAAD Day 28 – The Stasi Archive and BStU

After some traveling and conferences and development sprints on other projects I have time this week to come back to the Stasi work. The first post is about the Stasi Records Agency (BStU), whose full name (in English) is the impressive, “Federal Commissioner for the Records of the State Security Service of the former German Democratic Republic”.


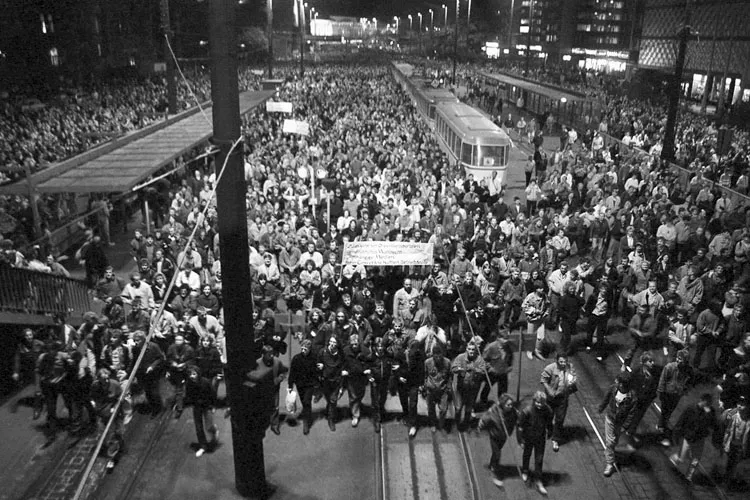
Monday Demonstration in Leipzig on 16 October 1989

At the end of 1989 the Peaceful Revolution spread across the former East Germany. These protests led to the opening of the border via the emotional breaking apart of the Berlin Wall, as well as the end of the reign of the SED government, and with it, the Stasi.

During the transition protesters realized the Stasi agencies were destroying the files that could incriminate them. Groups of citizens occupied Stasi offices across East Germany and sealed the buildings to prevent further destruction of information. On January 15, 1990, citizens gained access and occupied the Berlin headquarters of the Stasi.

After German reunification the BStU was established to preserve the archives and investigate the past of the Stasi. Since January 1992 they have provided a service to allow citizens to view the Stasi files that concern them.

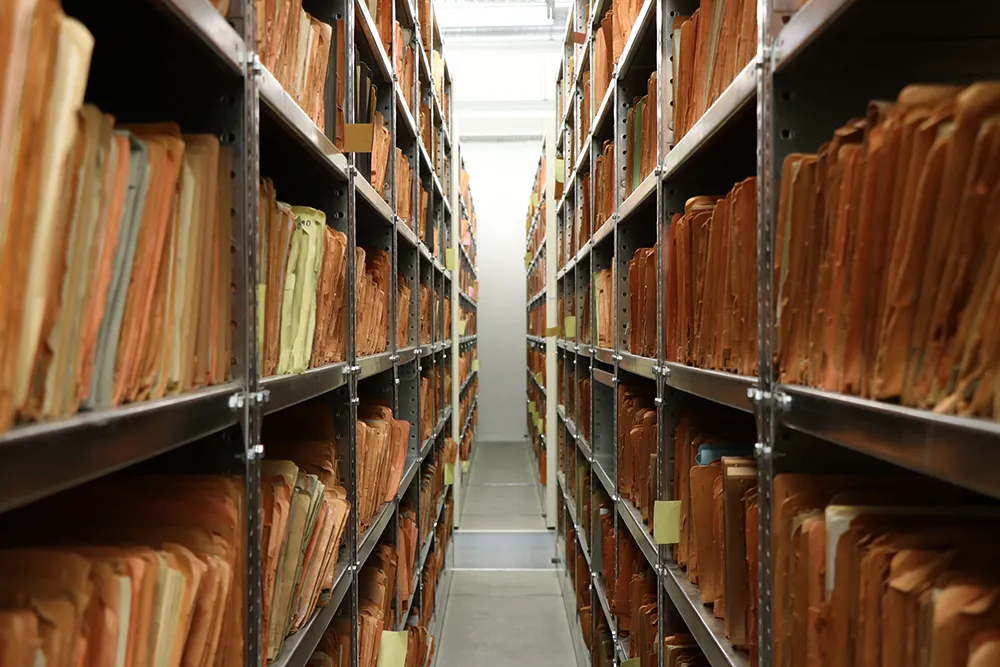
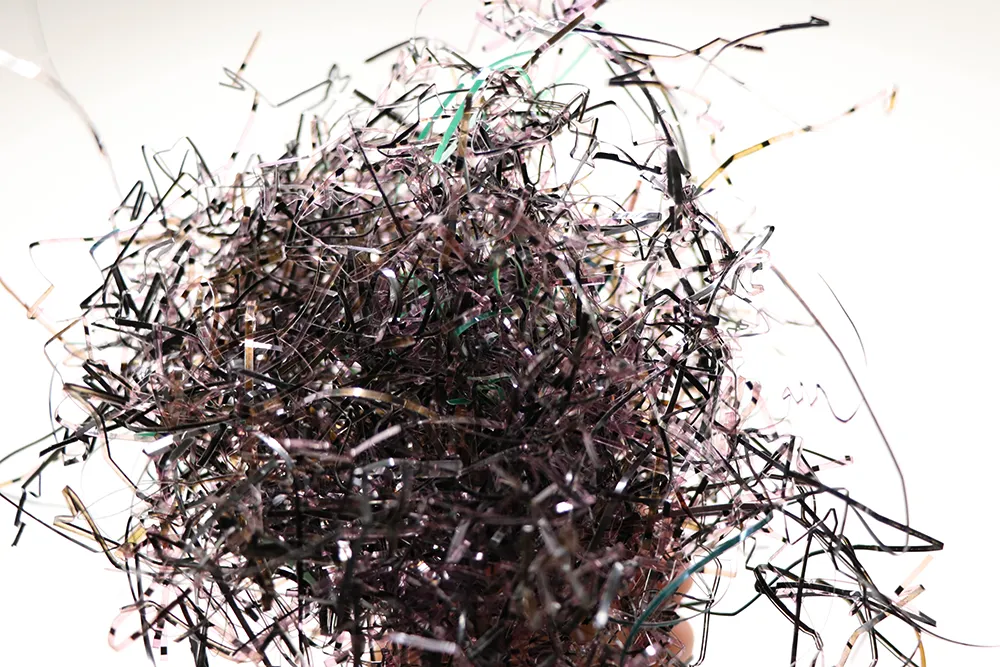
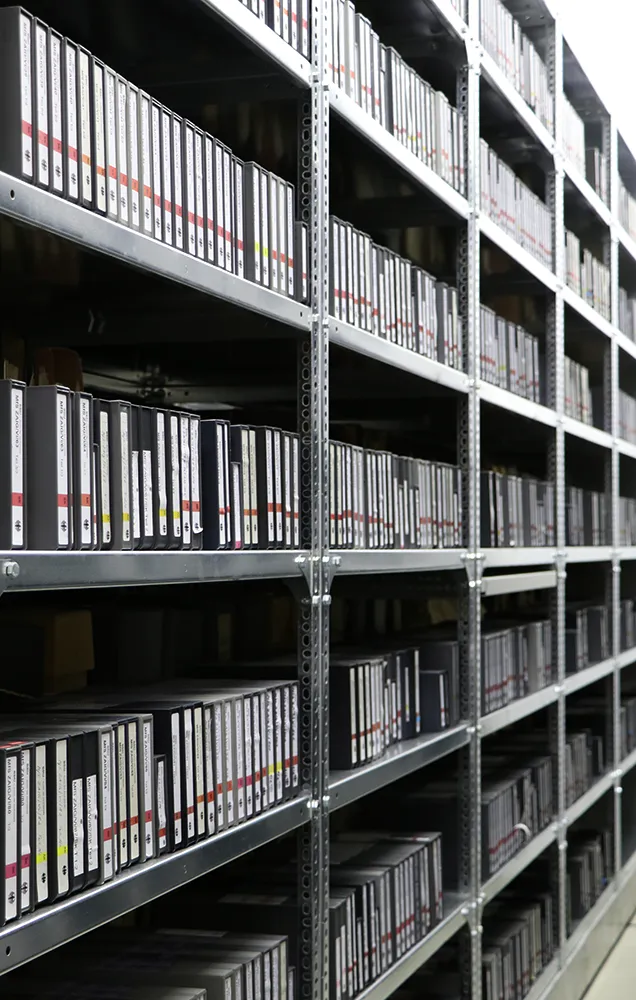
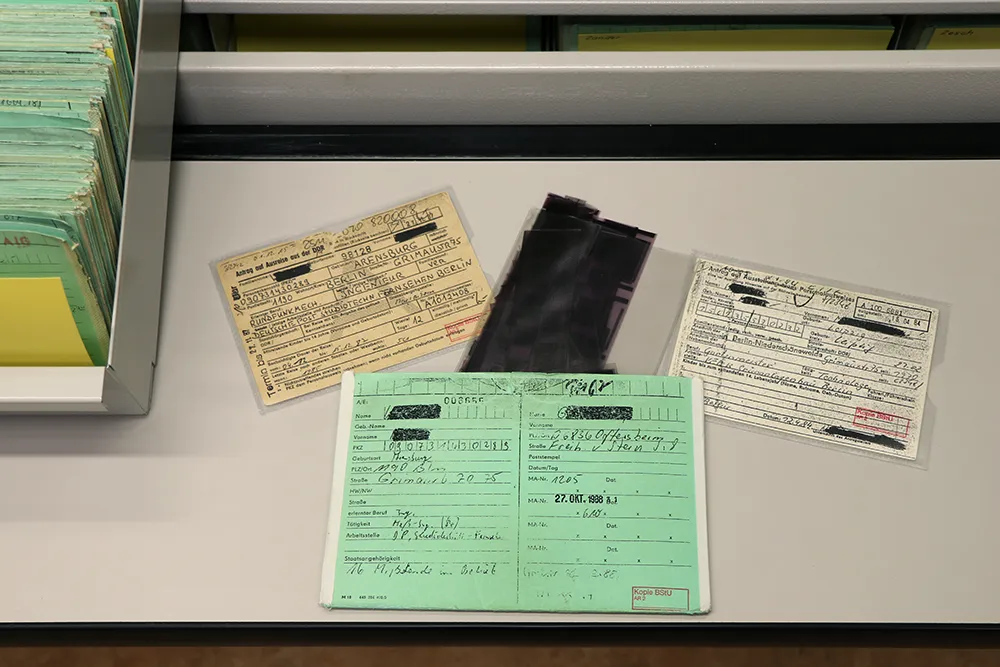
In Berlin the BStU is located at 31 Karl-Liebknecht-Straße, with the files appropriately continuing to be located in the former Stasi headquarters on Frankfurter Allee in Lichtenberg. Here are some photos I took inside the archives in the former Stasi headquarters.


An example card from the Stasi card index now used to locate information for citizens wanting to know what data the Stasi collected, Stasi Records Agency, 2017


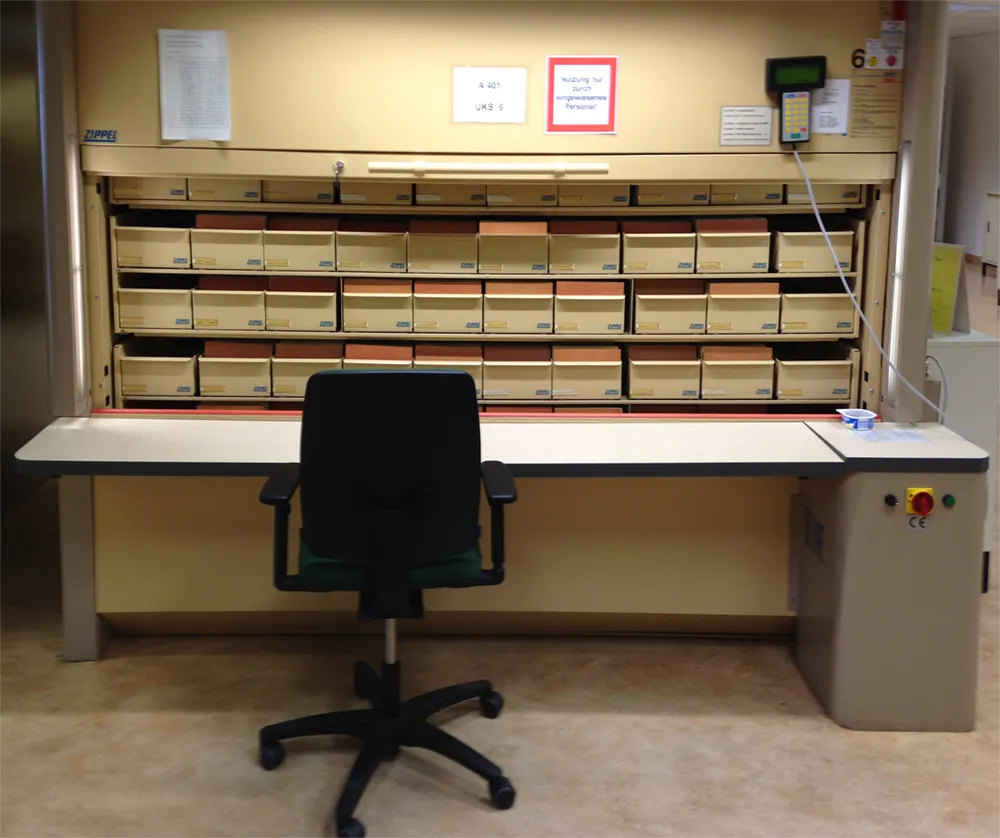
Shelves of citizen files now open to view by the citizens the Stasi surveilled, Stasi Records Agency, 2017


Microfiche shredded by Stasi agents, Stasi Records Agency, 2017


Shelves of surveillance video, Stasi Records Agency, 2017

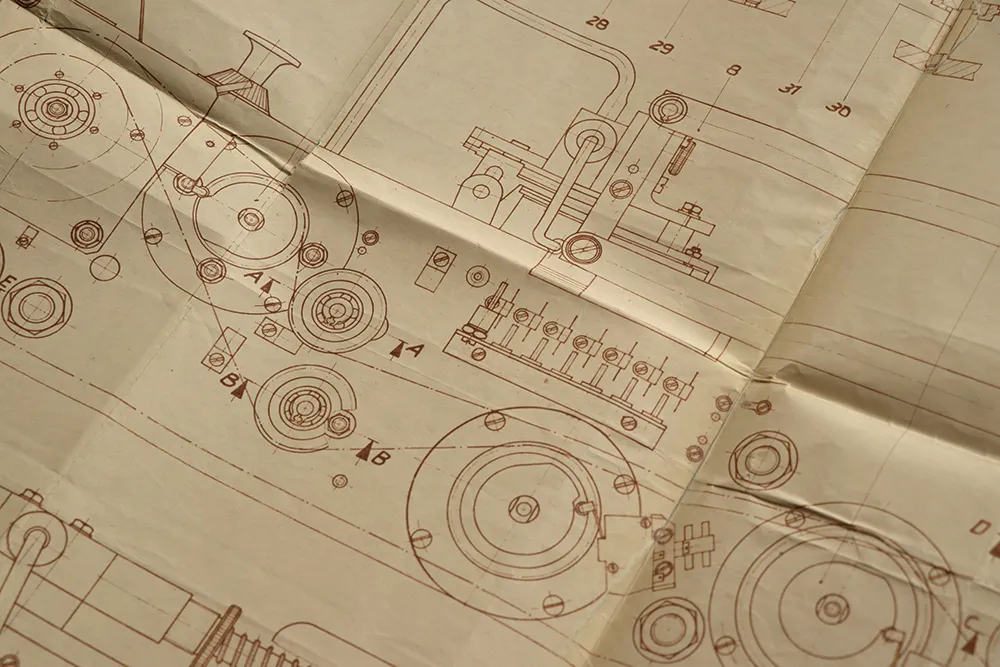
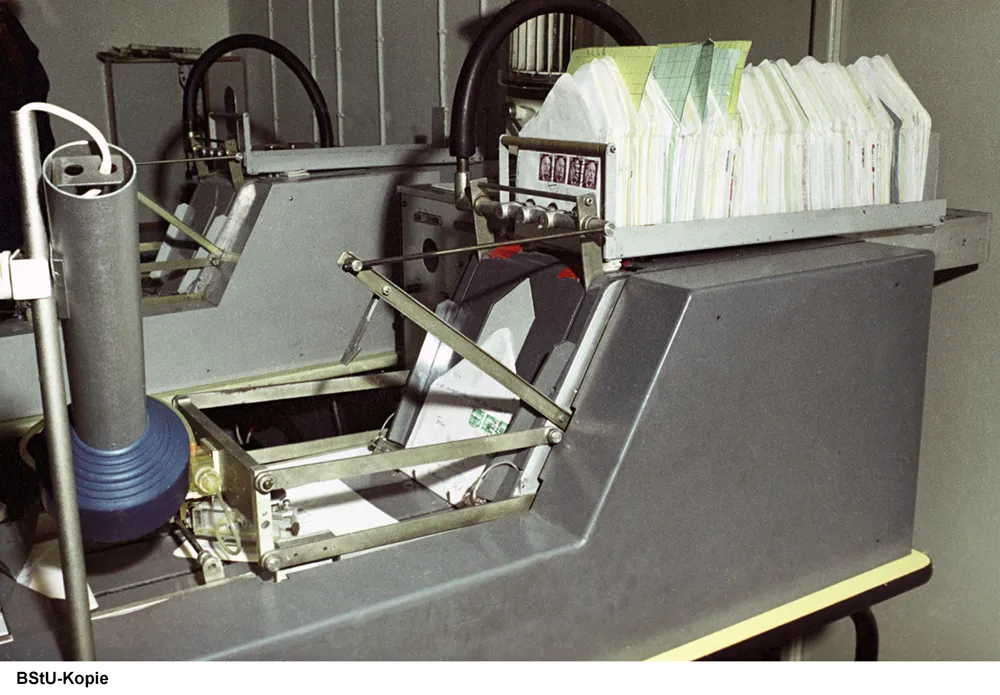
In addition to providing access to citizen’s files, the BStU assists scholars by allowing viewing of other Stasi documents. In my case, their staff helped me to find and view schematics of postal surveillance machines prepared by the Stasi OTS.


Detail of the Stasi Automatic Letter Closing Machine schematic, Stasi Records Agency, 2017

The BStU also has a thorough library at the Karl-Liebknecht-Straße location. Unlike the Stasi documents, which require one to make an application as a scholar, the library is open to the public.


The BStU library, 2017

A Deutsche Welle report on the Stasi archives, 2010

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie

Yesterday I headed to the Museum für Fotografie to see two exhibitions on surveillance.

The Field Has Eyes. Images of the Surveillant Gaze includes 75 prints, books, photographs and examples of optical apparatus to present a visual and cultural history of the controlling gaze from the 16th to the 20th century. I don’t have many images because ironically the museum of photography does not allow photographs.


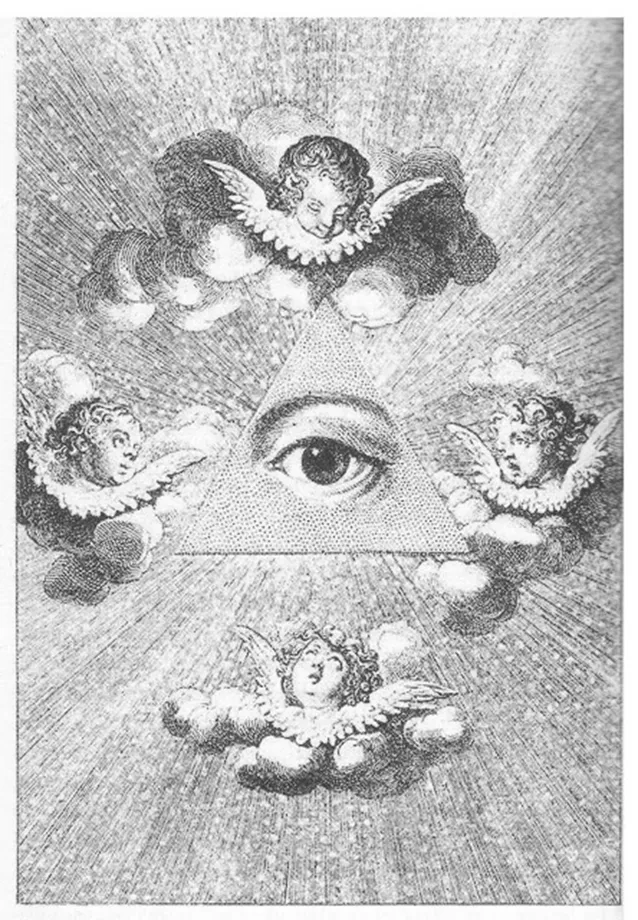
Daniel Chodowiecki. The Eye of Providence. 1787. Etching, 4 x 5′”

Still, I was able to track down many works online. An example is this one, which focuses on the “all seeing eye” of God as a heavenly entity that watches over everyone like Daniel Chodowiecki’s The Eye of Providence (1787).


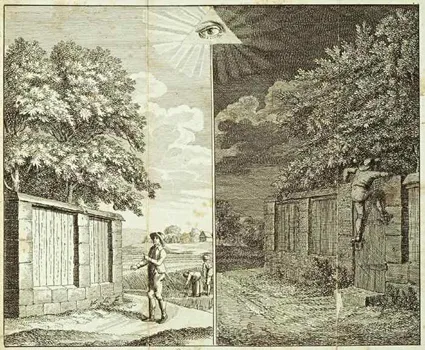
Johann Paul Pöhlmann. Gottes Augen schauen auch in die heimlichen Winkel (English: “God’s eyes also look into the secret angles”), Kupferstich: 135 x 165 mm, 1809

This view of God as a watcher later evolved into a sort of big brother figure like in Gottes Augen schauen auch in die heimlichen Winkel (English: “God’s eyes also look into the secret angles”), a copperplate by Johann Paul Pöhlmann from 1809. Here the all seeing eye is essentially a surveillance camera, encouraging potential law breakers to heed the warning that their bad deeds won’t go unpunished. This sort of indoctrination was easily transferred to messages from political bodies wishing to keep the behavior of their citizens inline as nation states emerged.

Watching You, Watching Me. A Photographic Response to Surveillance shows works by 10 contemporary artists using photography to address surveillance. This exhibition was sponsored by the Open Society Foundation.

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie


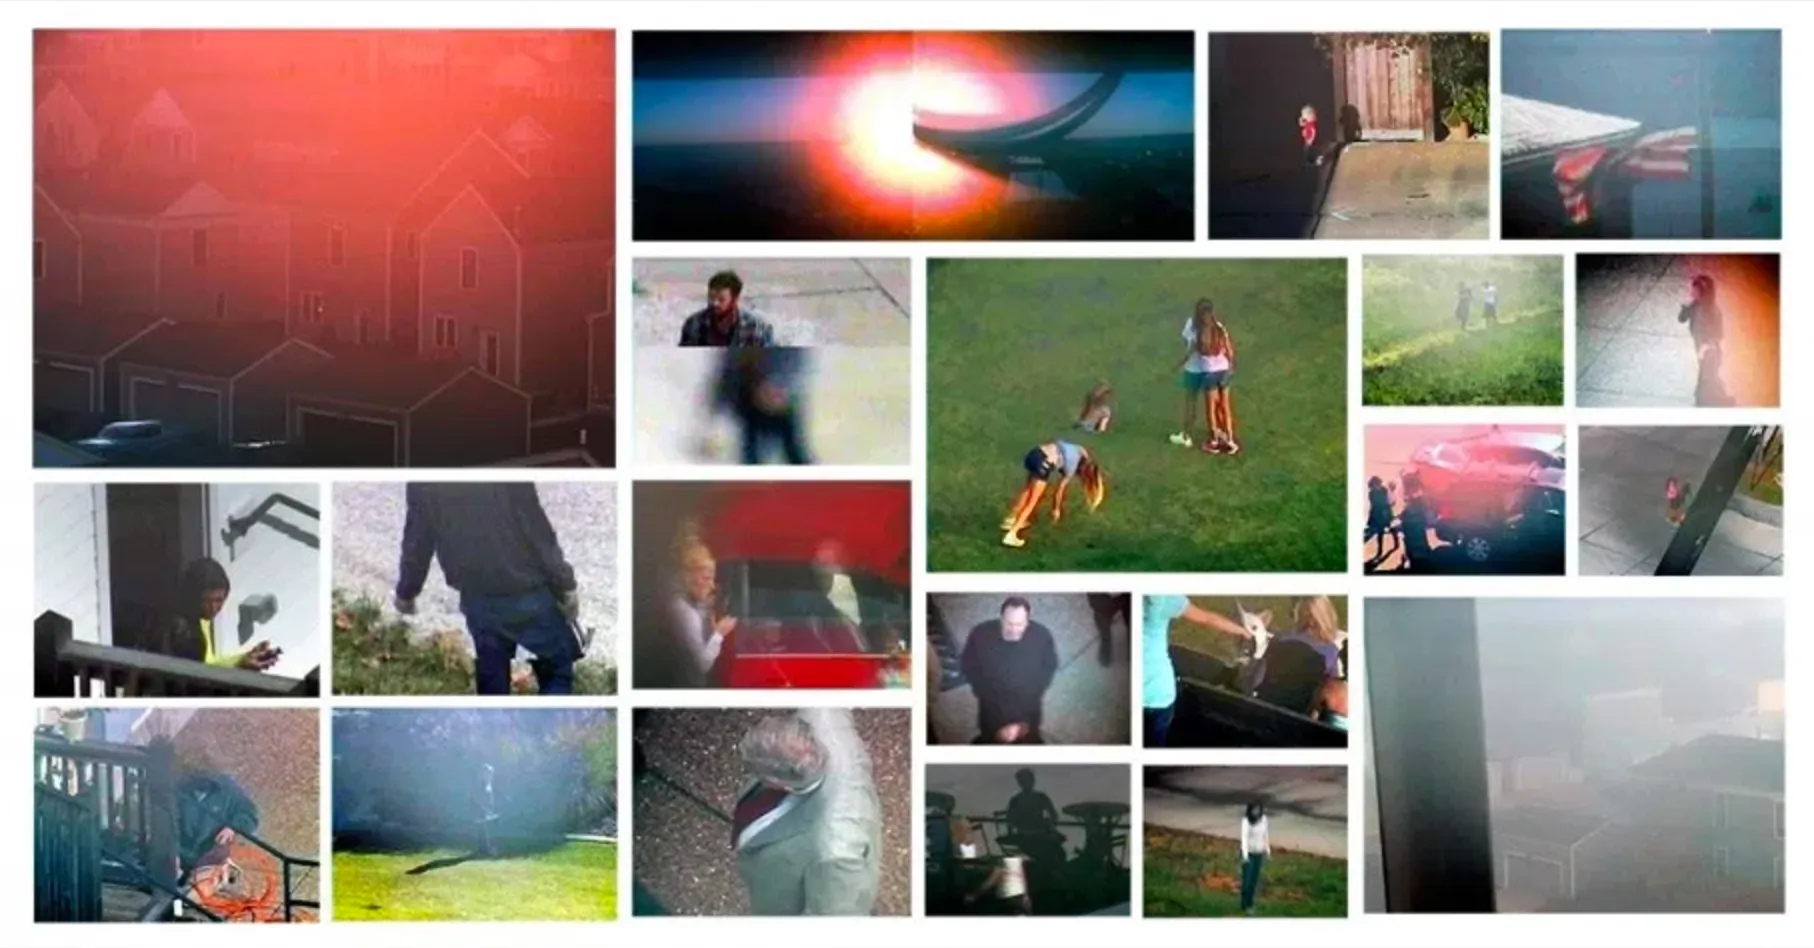
Andrew Hammerand. The New Town. 2013.

In Andrew Hammerand’s The new town (2013), the artist captured surveillance images from a camera placed in the center of an idealized planned community in the American Midwest. These are haunting and beautiful reminders of the gaze of the all seeing eye, and the inability to escape from it in even the most ideal locations.


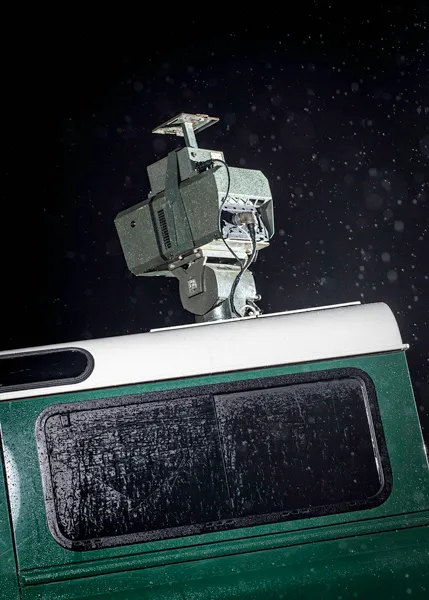
Julian Roeder. Thermal Imaging Camera, Northern Greece, 2012, Archival Pigment Print, 152 x 109 cm


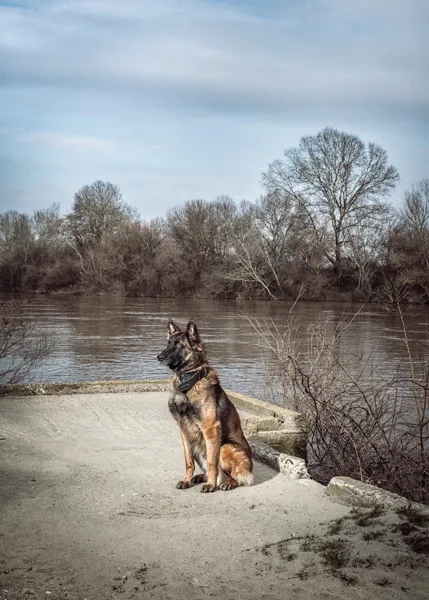
Julian Roeder. Tracking Dog, Northern Greece, 2012, Archival Pigment Print, 152 x 109 cm

Julian Roeder’s Mission and Task (2012) consists of images of the technology and people working in contemporary surveillance at the border of the Schengen zone.

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie


Mari Bastashevski & Privacy International. Private Interests. 2014

Mari Bastashevski & Privacy International presented photographs and evidence of Central Asian governments use of electronic surveillance technologies to spy on activists and journalists, domestically and abroad, in order to clamp down on dissent and to reinforce their political
control. This installation included the stories of several Uzbekistan journalists and lawyers who were surveilled, intimidated, and threatened with prison for their work. This project is covered in detail in this PDF.


Hasan Elahi. Thousand Little Brothers.

In response to questioning by the FBI in suspicious post-9/11 USA, Hasan Elahi created Thousand Little Brothers which includes 32,000 photographs he made during his ongoing project to give the FBI every detail of his life, especially the mundane.

Both exhibitions are up until 2 July, 2017.

Stasi / Facebook / Big Data DAAD Day 26 – Gedenkstätte Berlin-Hohenschönhausen

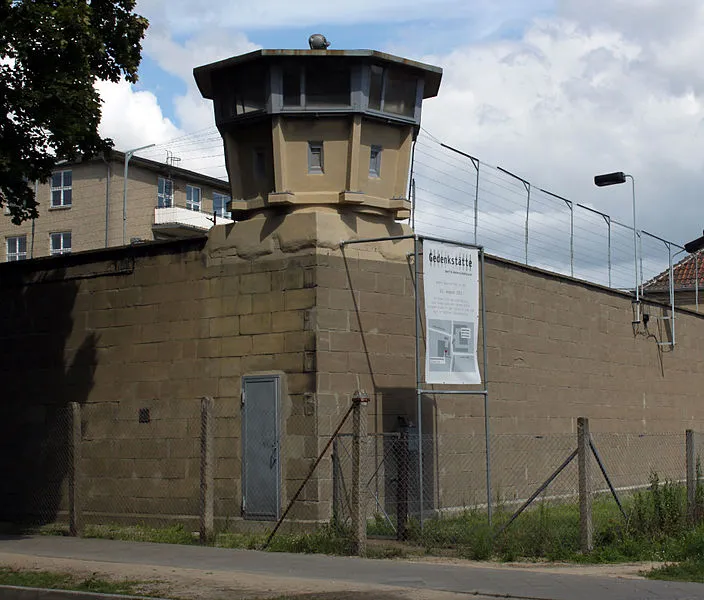
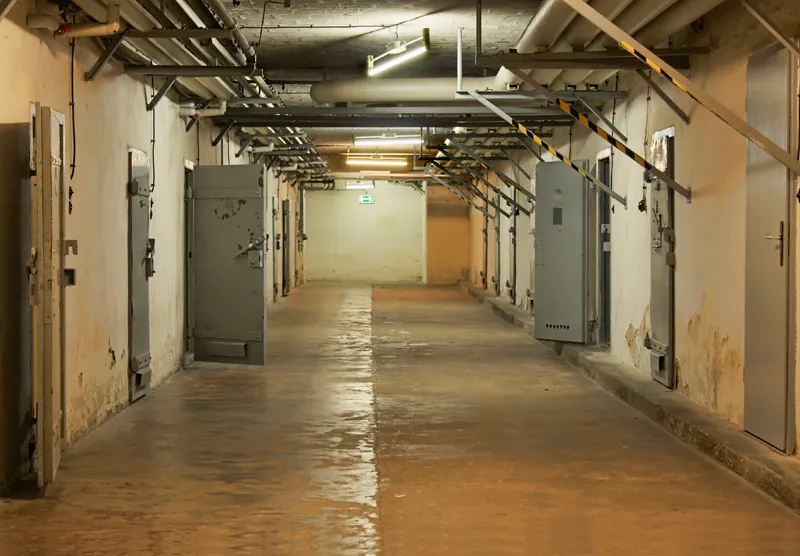
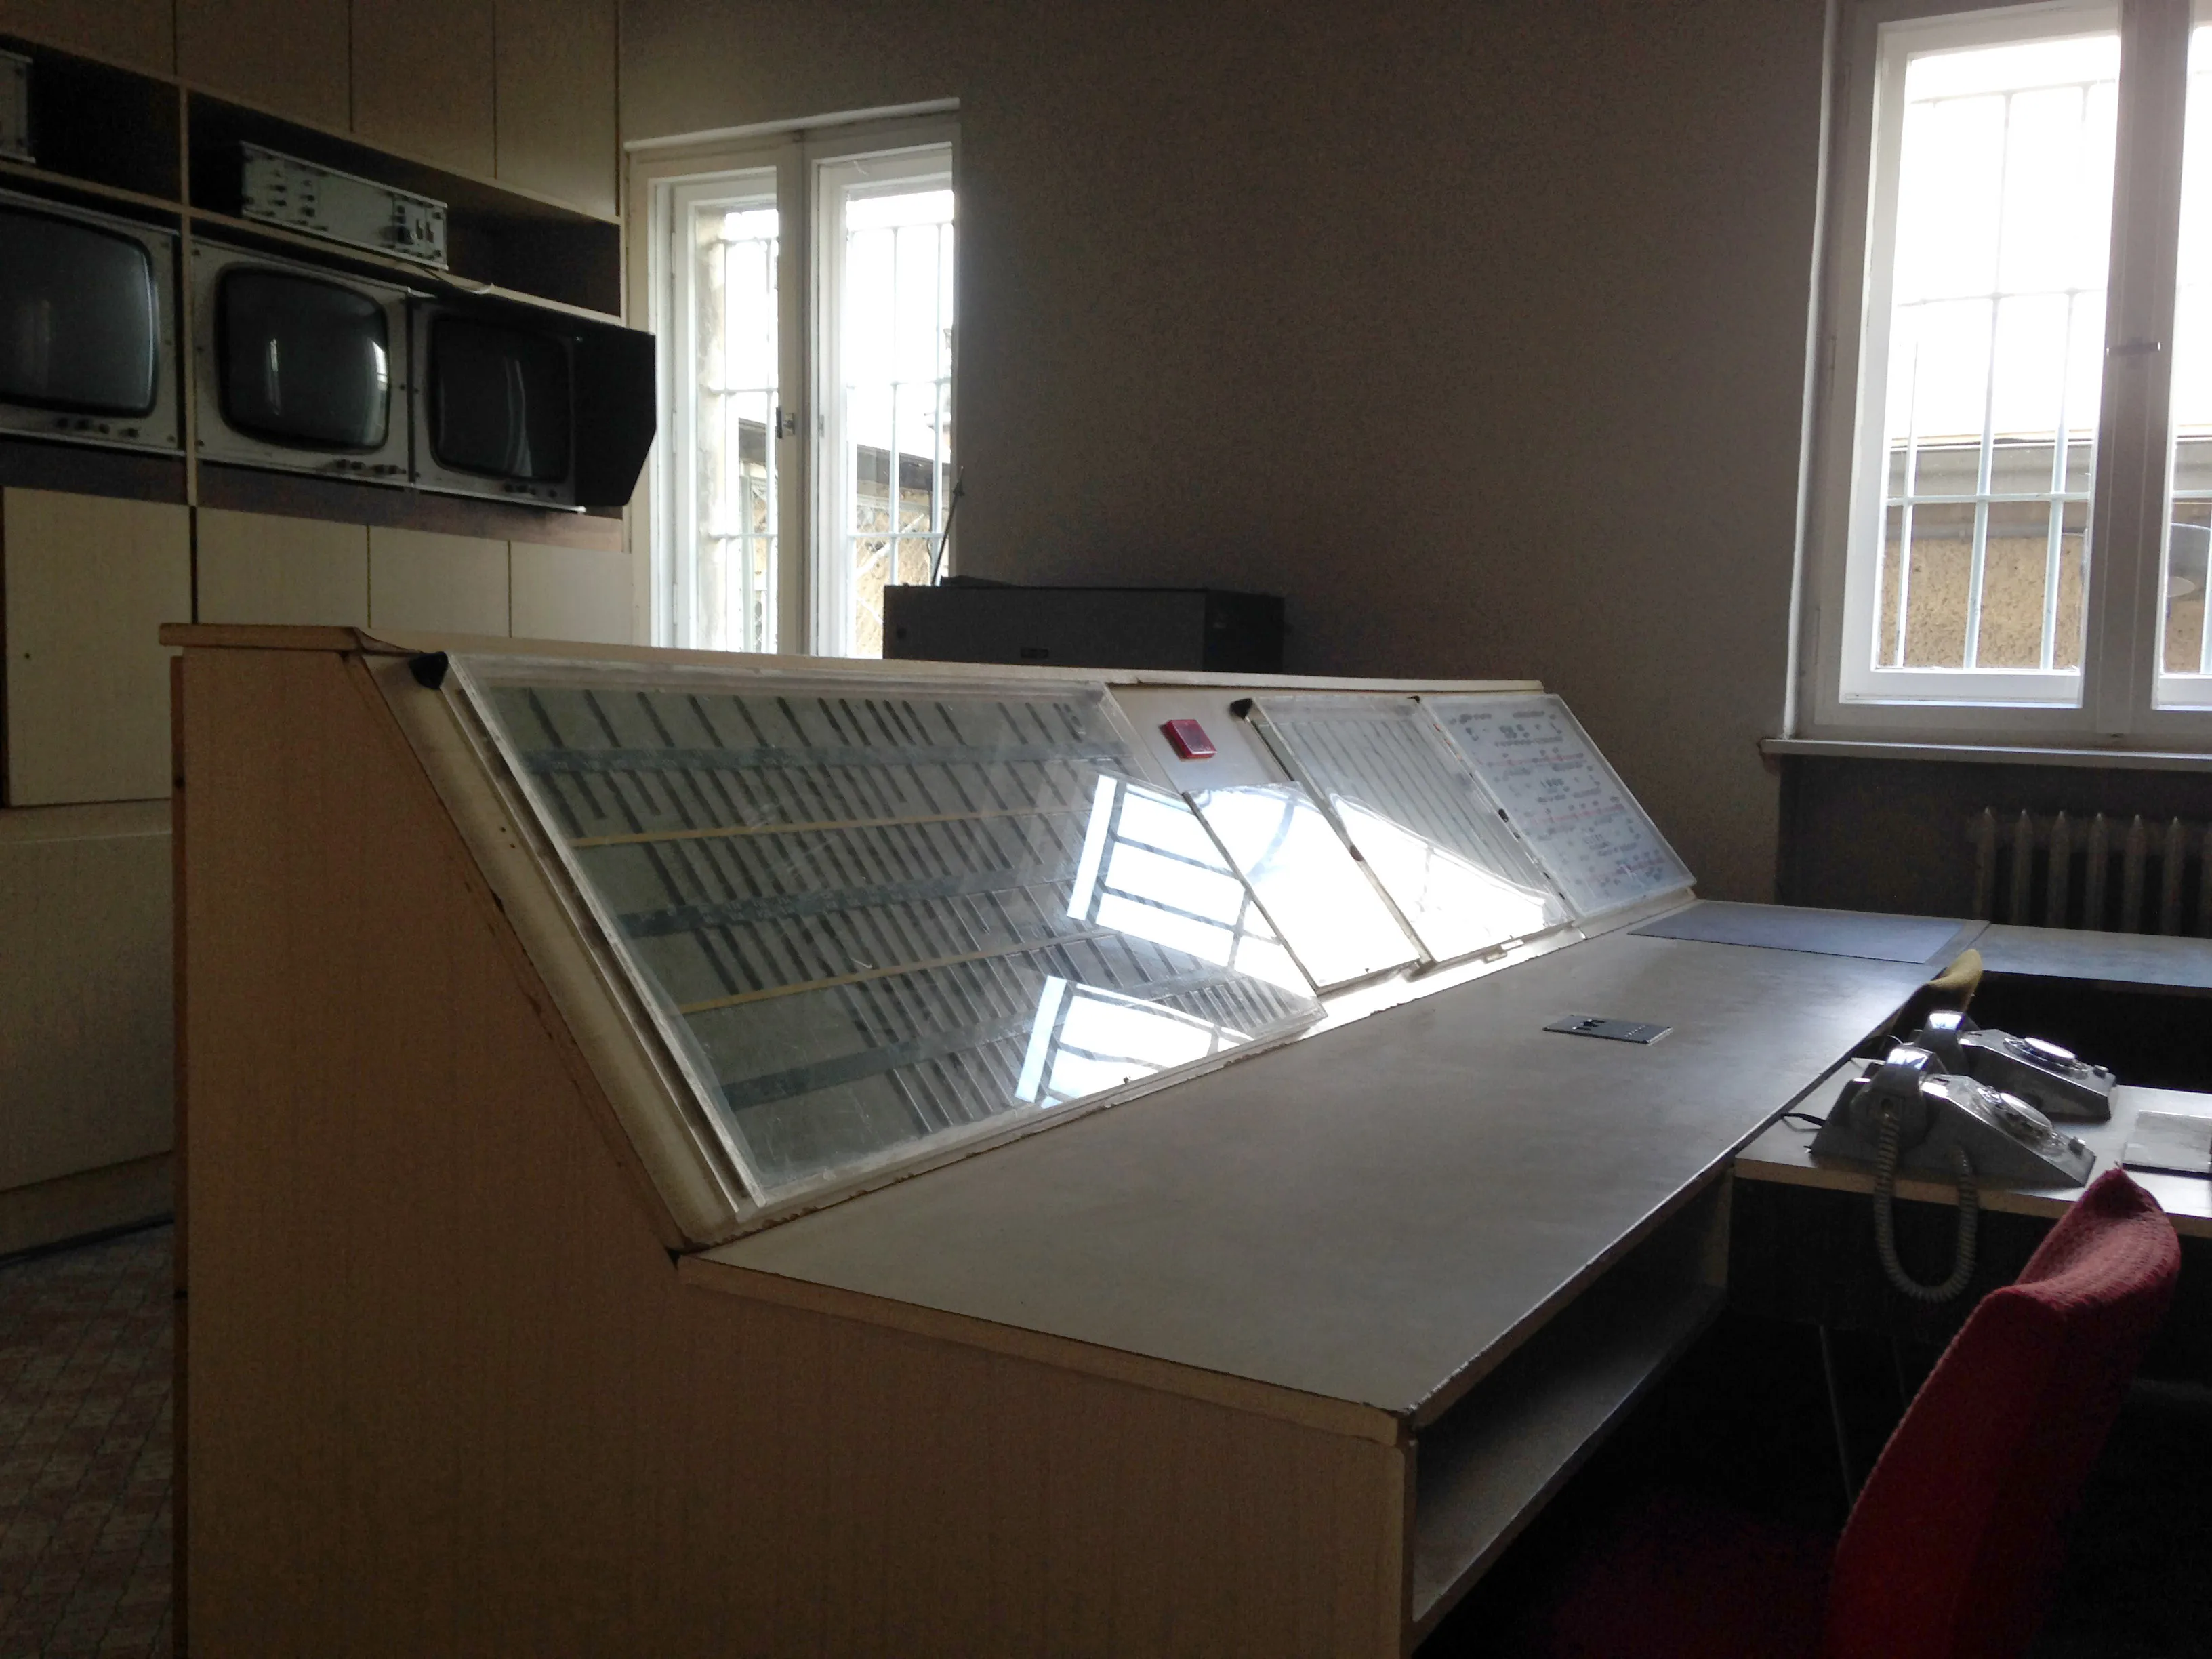
This week has been full of work on this project, including research in the BStU reading room, and making photographs at the archives at the former headquarters and the Stasi Museum. Today, for the first time, I visited The Memorial to Berlin-Hohenschönhausen, a large former prison complex which includes a former Stasi detention and interrogation center. Berlin-Hohenschönhausen began as a Nazi barrack camp for prisoners of war during WWII. After the fall of Nazi Germany it was used by the Soviet NKVD (the secret police) as a camp for interning political prisoners and former Nazis.

The facility was taken over by the GDR Ministry for State Security (MfS) in 1951. For nearly 40 years the MfS used part of it as a secret (it was not located on official city maps) detention and interrogation center. Here, over 10,000 political prisoners were detained and subjected to physical and psychological torture to gain information in preparation for sentencing by the courts.

The MfS staff who worked here were trained at the “Stasi University” (Potsdam) to destabilize and destroy the personality of their prisoners. Their methods included sleep deprivation, isolation, and other harassment that left the prisoners psychologically damaged. They also made references to prisoners’ loved ones, spouses and children, in order to coerce confessions and encourage cooperation.

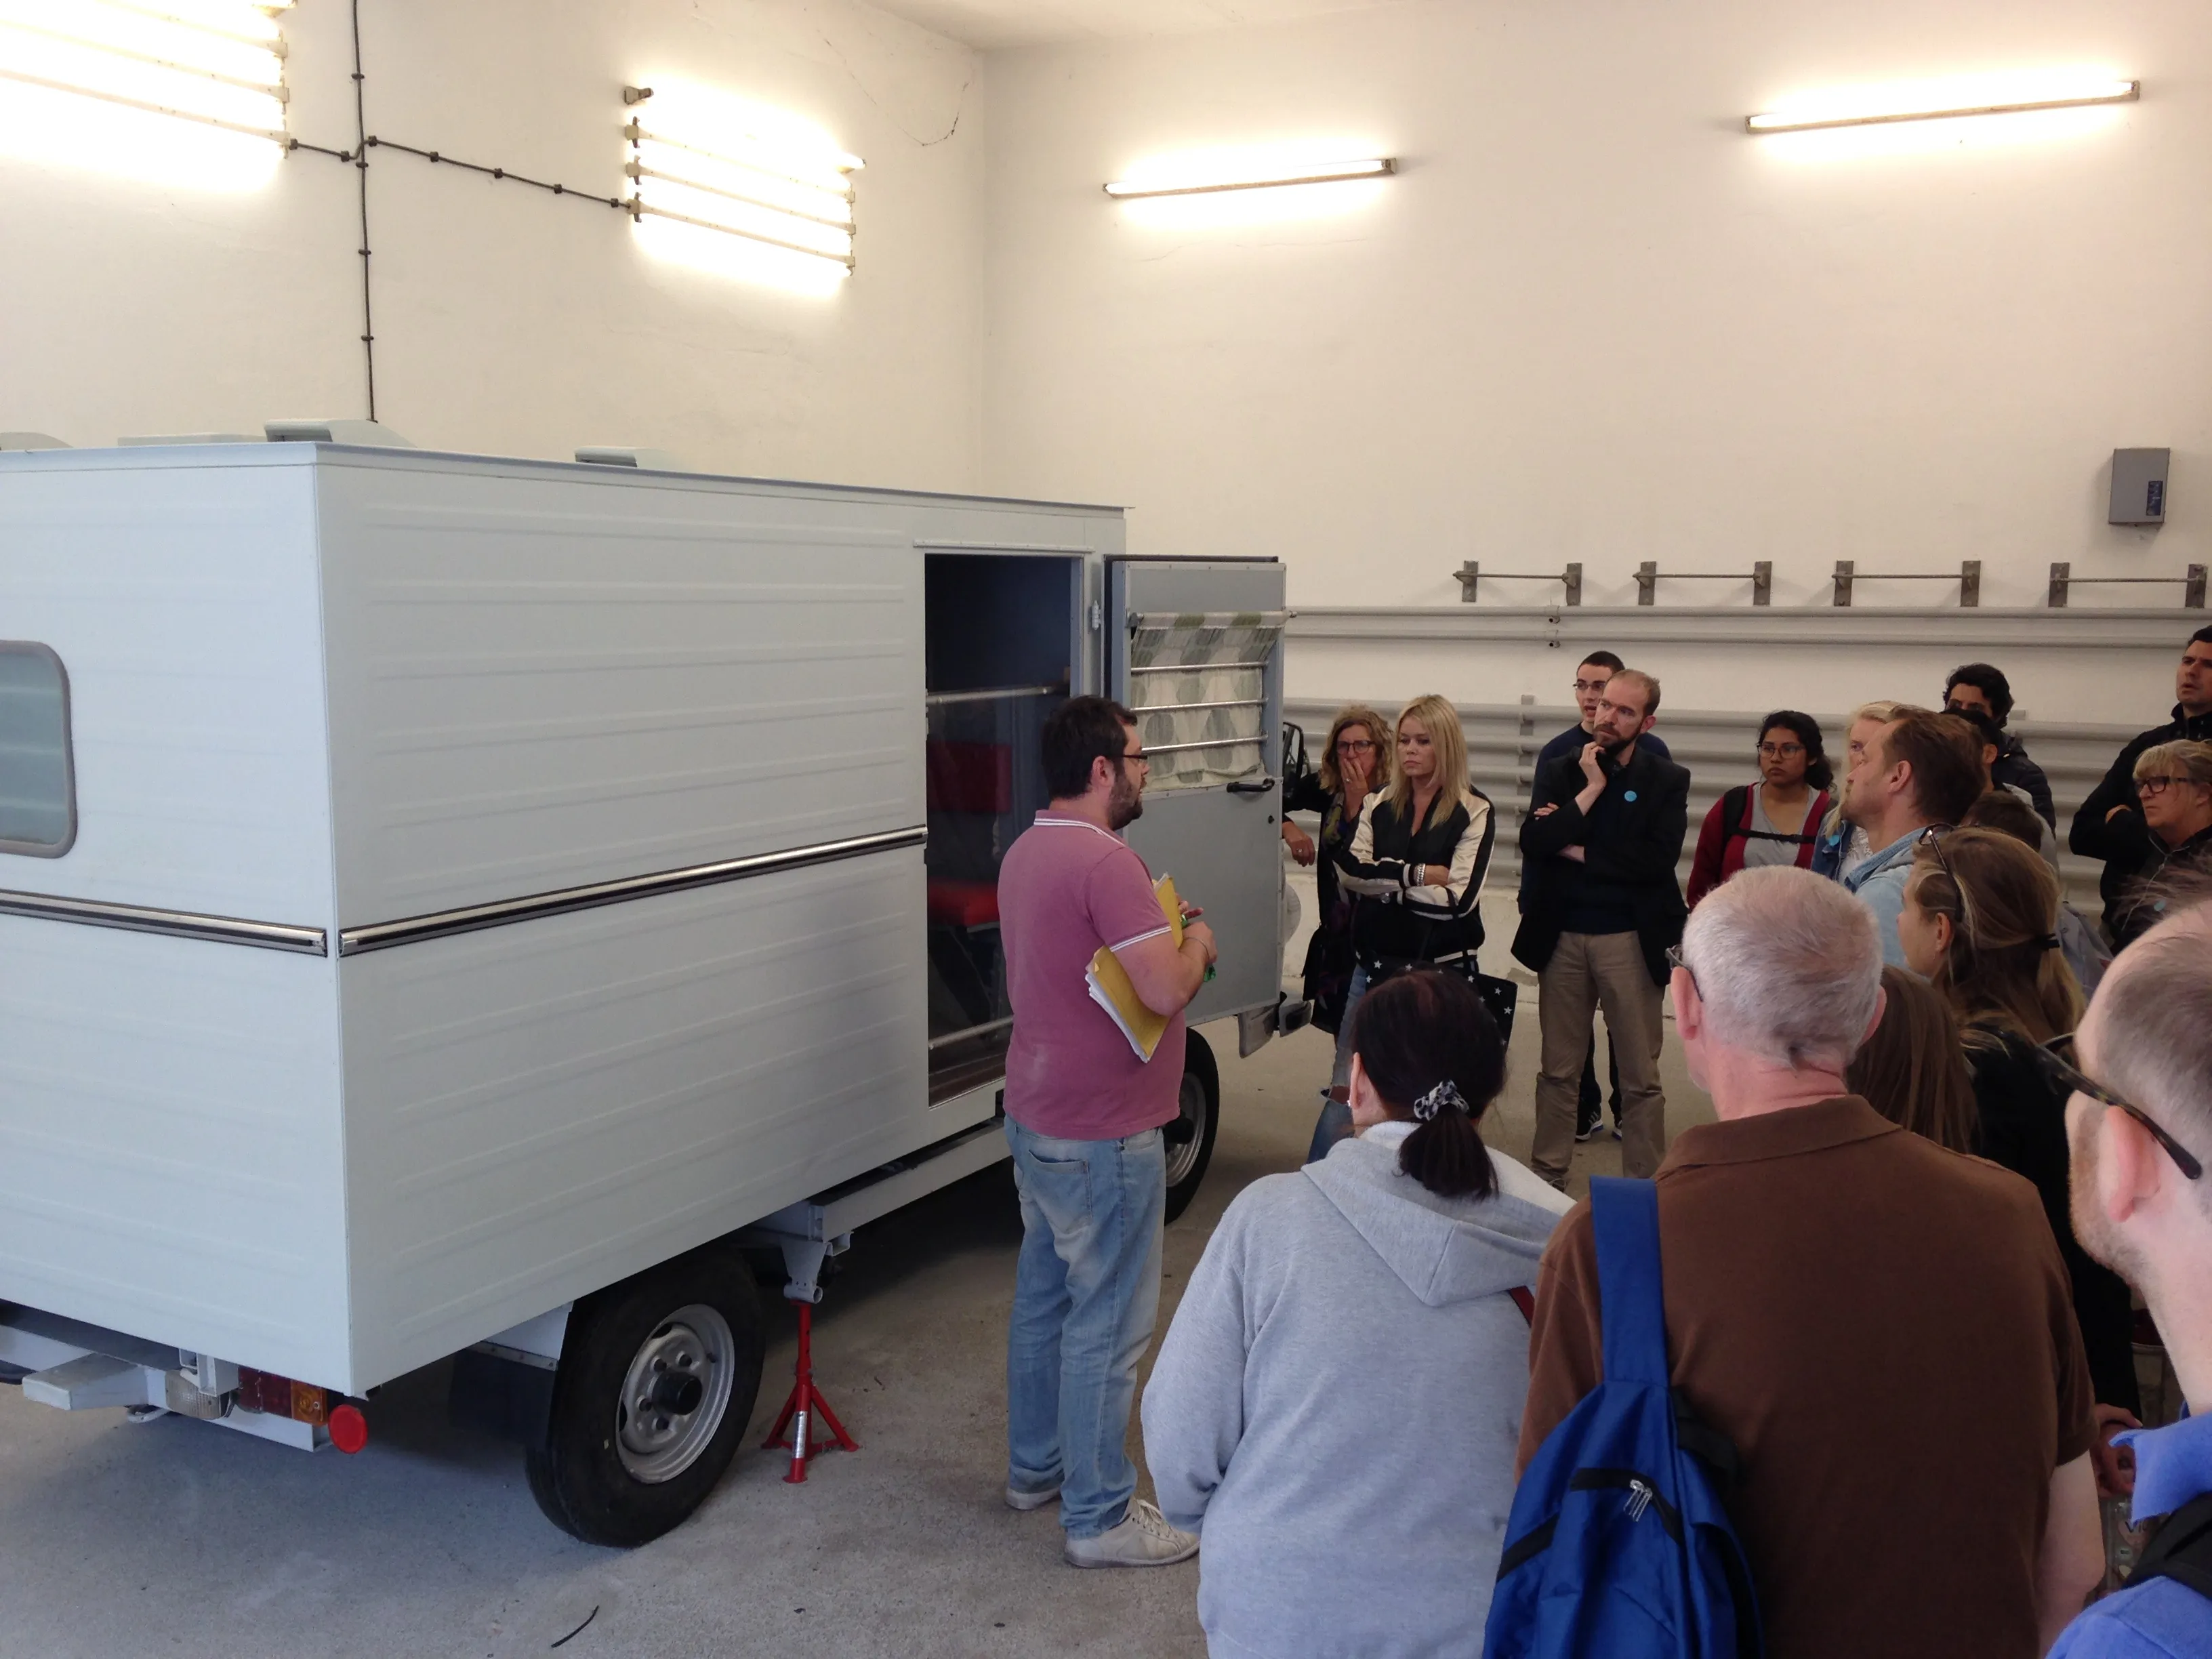
The methods for social isolation were particularly effective. Prisoners were often kidnapped and placed in a cage inside a van disguised as a delivery vehicle. The vehicle would drive around endlessly to disorient the prisoner and then arrive at a special closed-off garage in the detention center.

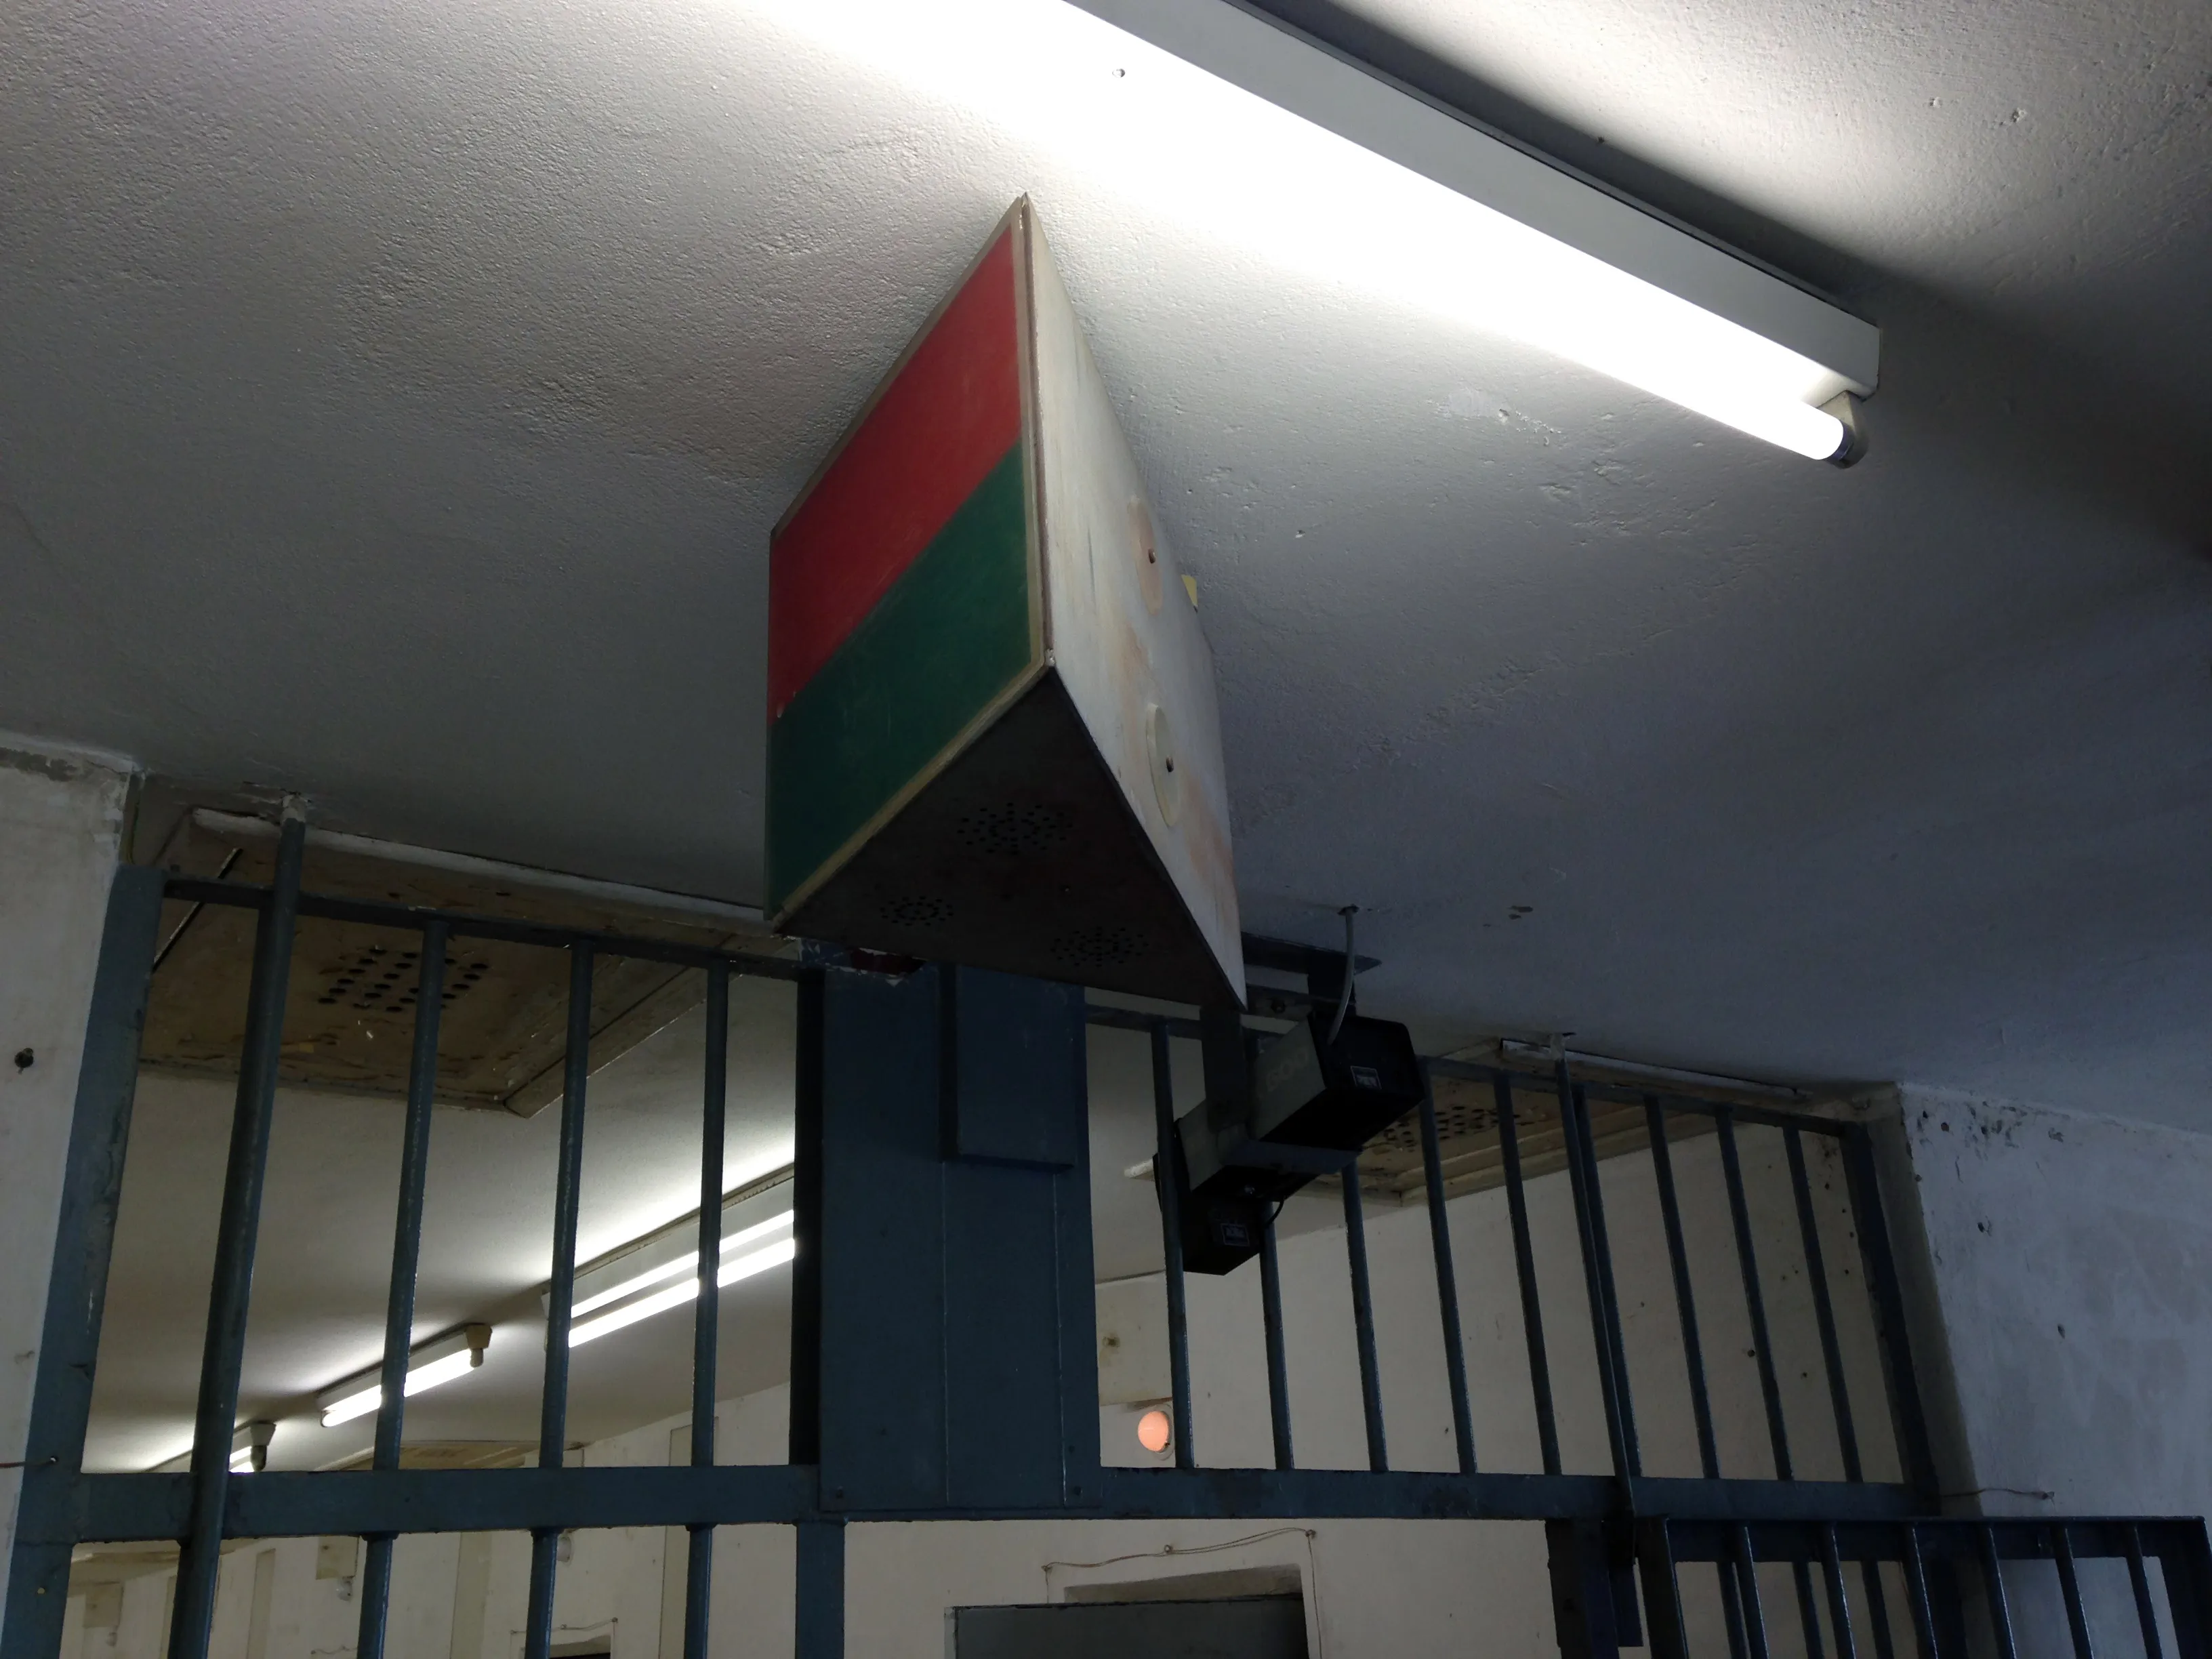
Once inside the buildings an elaborate series of electronic circuits controlled red and green lights in the hallways to direct the flow of prisoners and make certain they would never have the chance to encounter one another.

This last note offers an important comparison to today’s social networks and surveillance capitalism methodologies. In social networks, the organization benefits from the flow of information between participants. They want to stimulate their users to interact and continue generating profit by using the site, producing data, and viewing ads. The Stasi’s torture of political prisoners, on the other hand, intentionally removed all stimulation and human contact. The sensory deprivation and isolation that prisoners experienced in their cells dehumanized, weakened, and prepared them to to give up information the Stasi wanted.

Our information society has transformed the way we think about private information. While we freely give it up in exchange for social capital, companionship, and the serve the impulse to communalize our experiences, it does not mean that the social networks and corporations who deal in that data are not responsible when our information is misused. The recent revelation that the U.K. defense contractor turned data dealer, BAE, sold cyber-surveillance tools to Arab states is proof of this. BAE peddled their sophisticated total surveillance system, with a generic yet telling name, “Evident” (a marketing variation of “criminal evidence”?) to six Middle Eastern countries previously criticised for repressing their citizens. These countries can now use the tool to scour the internet for sites, blogs, and social networks for information on anyone they consider an opponent. A former BAE employee put it like this:

“You’d be able to intercept any internet traffic,” he said. “If you wanted to do a whole country, you could. You could pin-point people’s location based on cellular data. You could follow people around. They were quite far ahead with voice recognition. They were capable of decrypting stuff as well.”

Digital information is inherently insecure. It’s easy to surveill, copy, and duplicate by design. Equally, it is easy to reimplement a surveillance software system that is designed to be sold to do so. The Stasi was a terrible organization, but their work was generally confined to the GDR. There was collaboration across the USSR satellite police organizations, but their work wasn’t on a global market. Looking back at the Stasi provides this evidence; The employees and stockholders of any company that benefits from the sale of such a system to inflict human rights abuses are as guilty as the Stasi employees who worked in the offices and never directly inflicted damage. Surveillance capitalism isn’t just about the profit generated by social network ads, it includes the manufacture and sales of systems like Evident, and all those who derive profit from such decentralized institutions.

Stasi / Facebook / Big Data DAAD Day 25 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using hot air


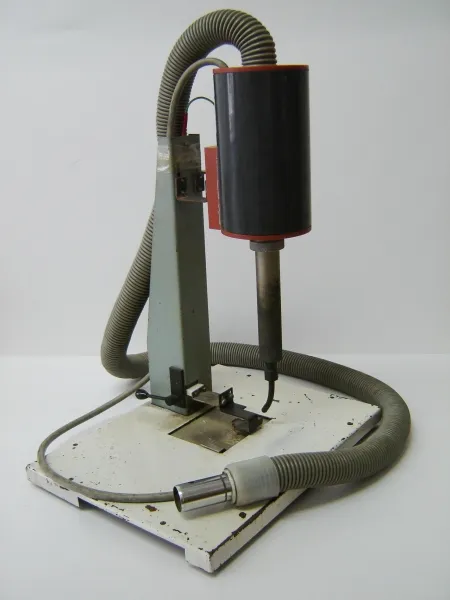
Heißluftgebläse. Credit: Museum in der Runde Ecke

The next artifact in my list is the “Heißluftgebläse”—a hot air blower constructed by the Stasi for opening envelopes and packages sealed with rubberized self-adhesive tape. Unlike the various steam methods the Stasi employed, which only worked on water-based glues and could potentially damage the contents of letters, this machine was used to focus hot, dry air directly to the flap in order to soften and release the adhesive.

Like other “hacked” machines constructed for postal surveillance the Stasi Operative-Technical Sector fashioned this blower using off the shelf, reused, and hand-made parts. In this case, they adopted a commercially-available vacuum cleaner to force air through a heating cartridge and down a steel tube towards a platform where workers laid envelopes. At the end of the tube there is a metal apparatus that could be used to focus the hot air and gently pry the envelope flap open. Impressively, the Runde Ecke index states this method be used to open up to 150 letters per hour.


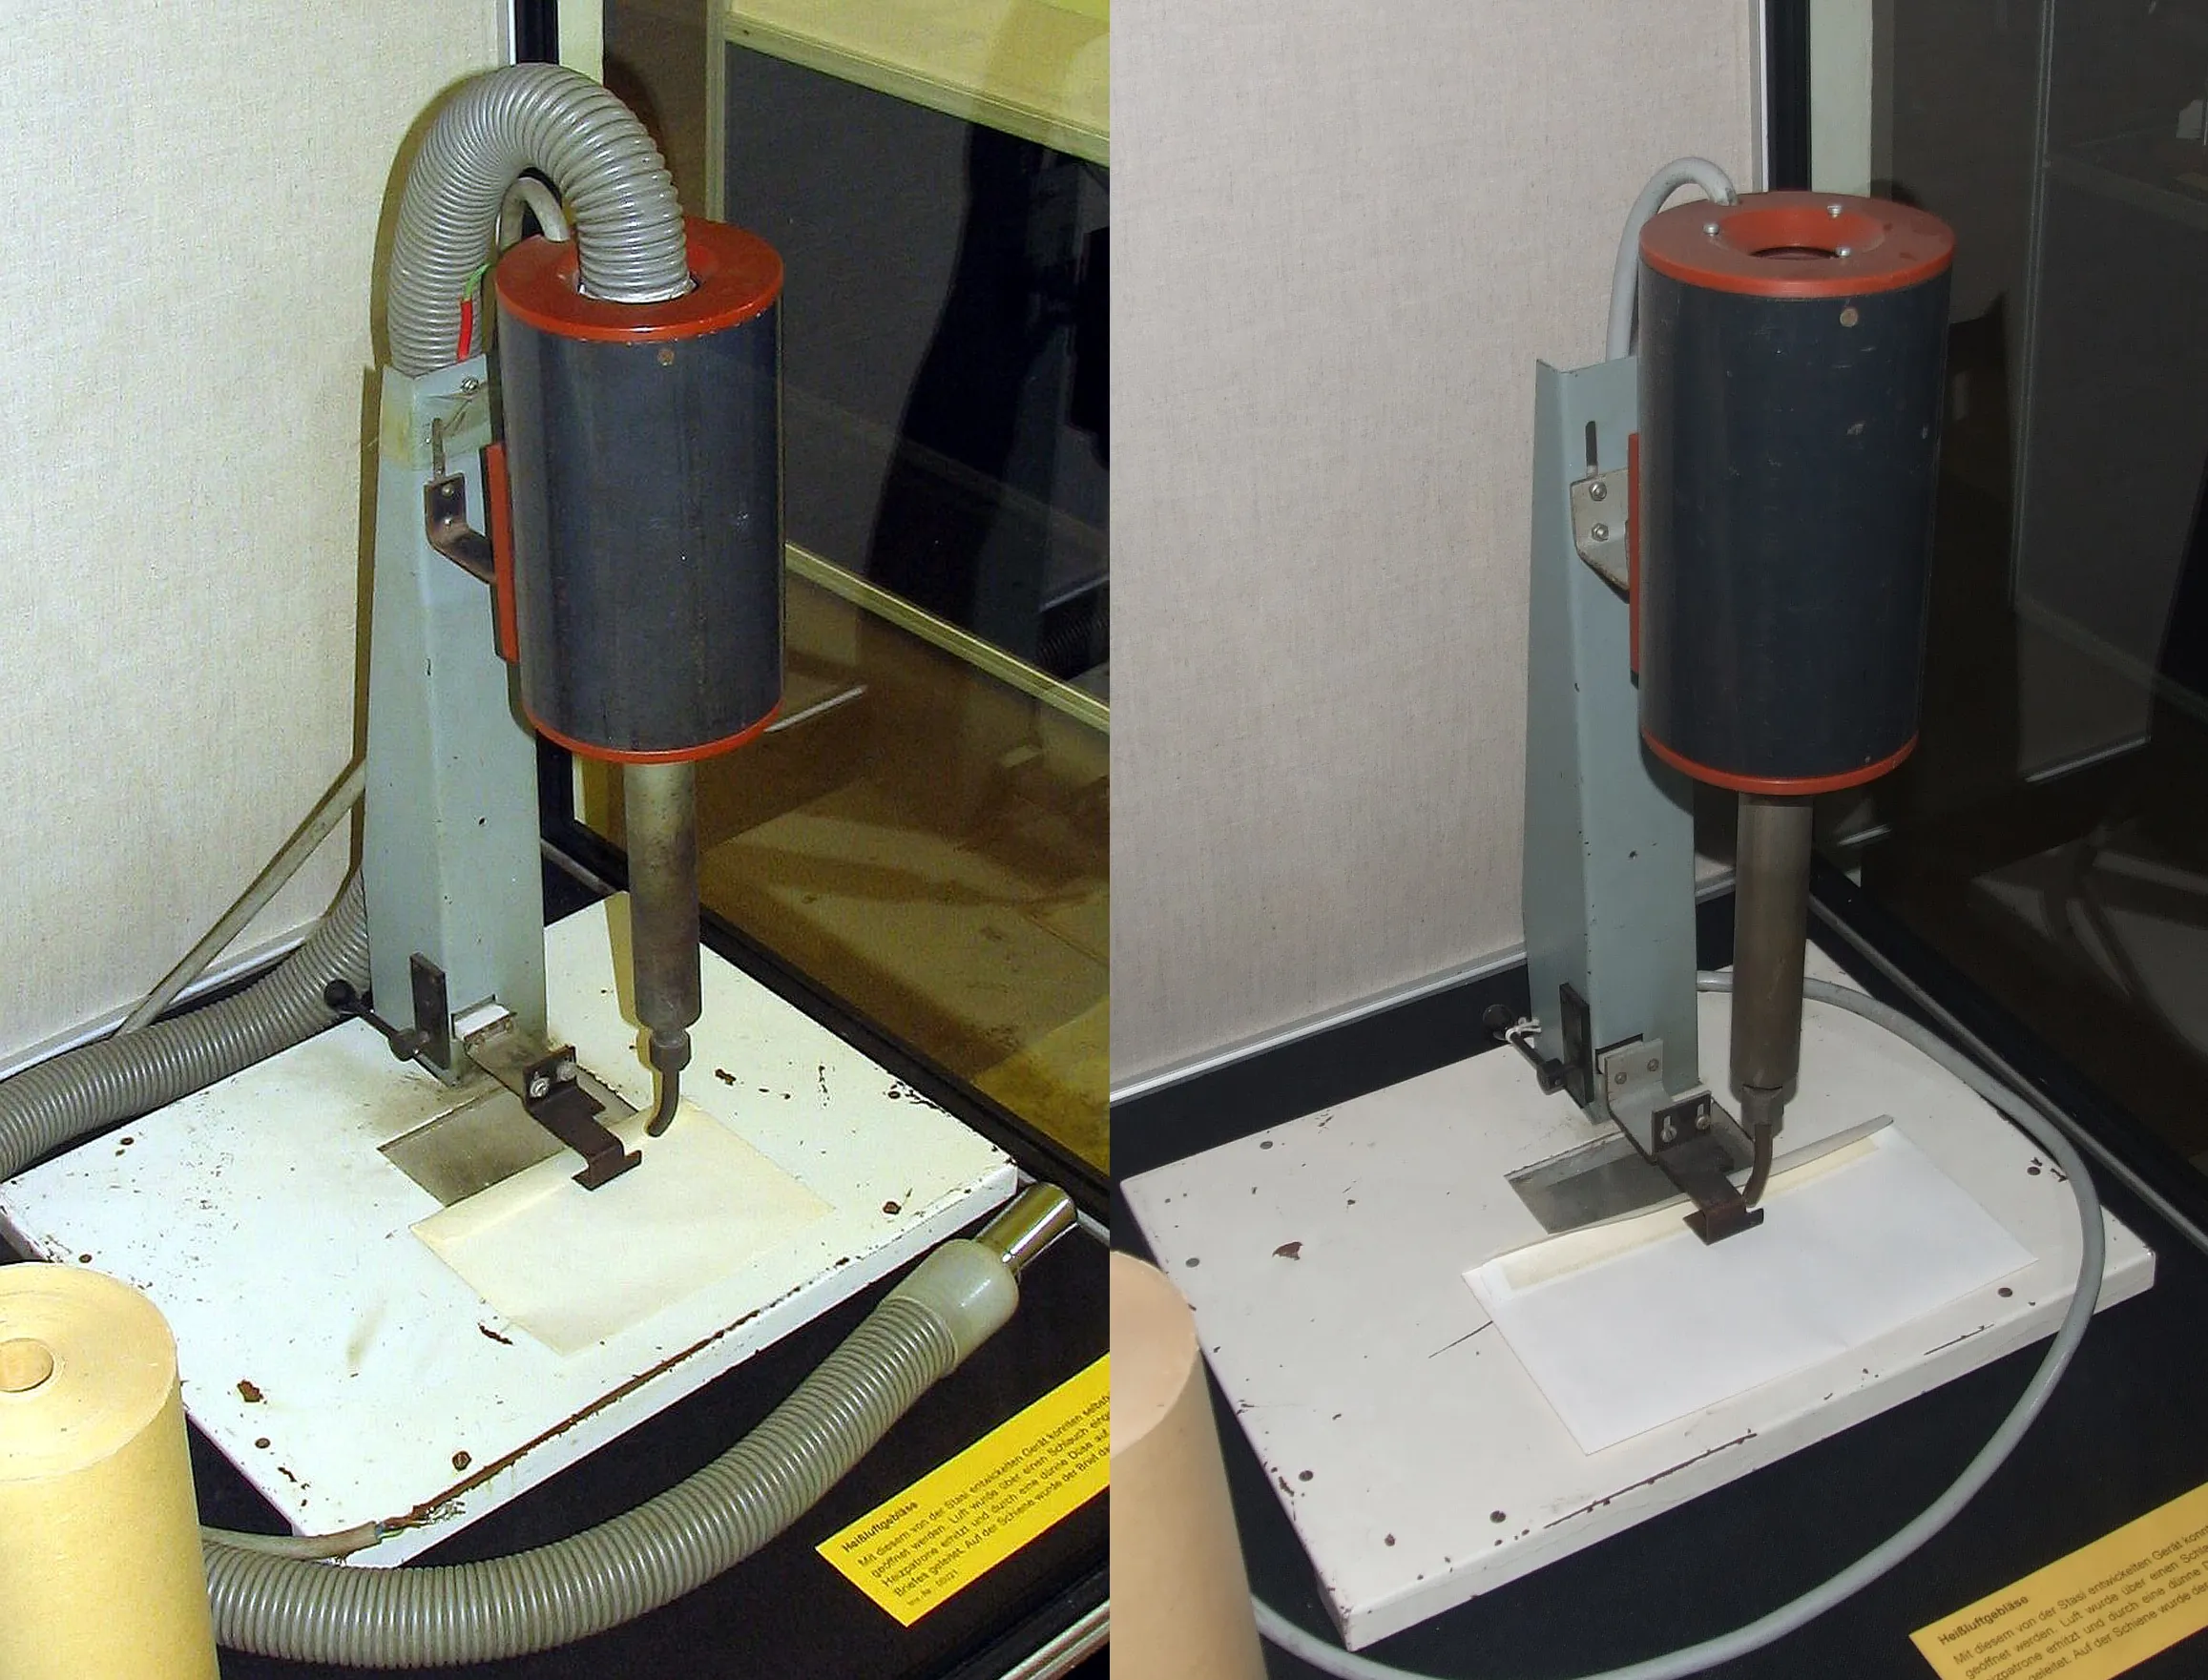
Heißluftgebläse. April and July Credit: Wikepedia user Appaloosa

I’m particularly interested in the different representations of this machine. In these two photographs, both posted by the same Wikipedia user in 2008 just months apart, it appears there were two separate machines on exhibit. This is suggested by comparing the scratches on the base and stand. Yet, while they are clearly different, they are strangely positioned in exactly the same location—an exhibition at the Museum in der Runde Ecke which contains objects found in the Leipziger district administration for state security (BVfS)—with other obvious differences. In the 22 April photo (left) the vacuum cleaner is still attached, showing how the machine was originally used. But in the 27 July image the vacuum and tape have been removed. Was it needed for cleaning in the museum? Where could it have gone? There are additional small differences that point to these being distinct machines, the most noticeable of which is that a different bracket is holding the heating apparatus.

It’s thanks to deviations like this that the telling of the story of Stasi postal surveillance continues to evolve. Aesthetic decisions that seem inconsequential—like a museum staff member replacing the device with the yellowing tape with the one that doesn’t look as disheveled—change how we are able to perceive the past. Here, those moments which make the economic and material constraints the Stasi OTS experienced while hacking and iterating across their analog surveillance devices become less clear. While, thanks to the BTsU we are fortunate to be able to dissect and interpret the methods of the Stasi, it is not possible to collect everything. This unfortunately obscures the parallels with our 21st century hacker culture that, like the Stasi, have grown into immense organizations intent on perfecting and perpetuating their power through surveillance.

  1. Heißluftgebläse zum öffnen von gummierten selbstklebenden Briefen (Inventory no. 00020). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 13, 2017.
  2. BStU. Die Stasi und das Postgeheimnis. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 24 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using cold steam


Credit: BStU

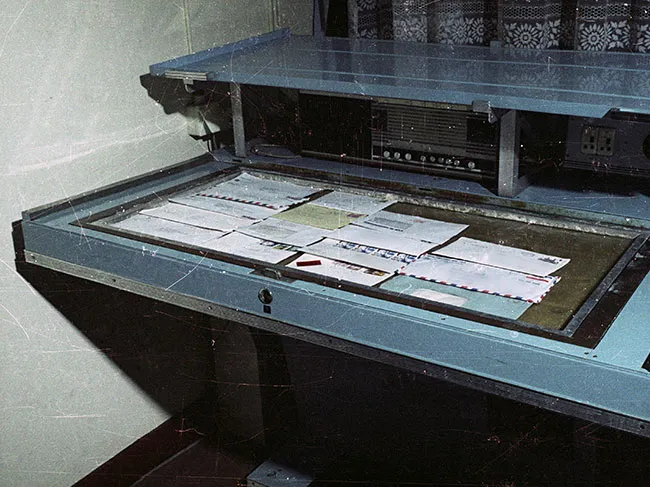
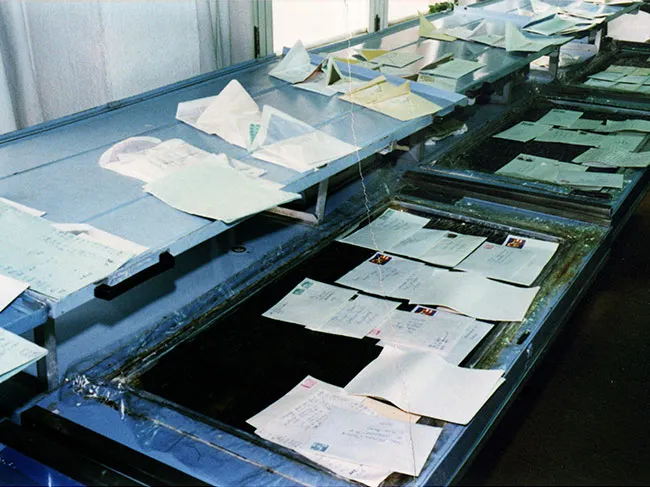
Since hot steam could damage sensitive contents like photographs, the Stasi used the C-83 (“Cellophan 83”) “cold steam” generating device to open those letters. Produced in Hungary, the C-83 used a special film (cellophane) stretched over a tray filled with distilled water. Up to 25 letters could be placed on the film, flaps down, so that when the water in the tray was heated to 50ºC the “cold steam” diffused through the film and dissolved the glue on the envelope flaps.

The procedure was time-consuming because cold steam dissolved the glue at a much slower rate than the hot steam method. Once the glue started to soften, workers had could only lift the letters off the foil for a short time in order to carefully open them using a special spatula.


Credit: BStU

It is unclear if this is an original mass-produced device or is a product modified by the Stasi OTS. It is constructed of painted sheet metal, cast plastic, and other materials that suggest it was primarily constructed in a factory, though it is possible the Stasi made modifications to assist in letter-opening.


Credit: Museum in der Runde Ecke


Credit: Museum in der Runde Ecke


Credit: Museum in der Runde Ecke

  1. Kaltdampf-Öffnungsgerät zum öffnen von Briefen (Zellofanbodengerät) (Inventory no. 00006). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 13, 2017.
  2. BStU. Die Stasi und das Postgeheimnis. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 23 – Automation in Stasi postal surveillance: Work Table for Hot Steam Opening System 532


Credit: Museum in der Runde Ecke

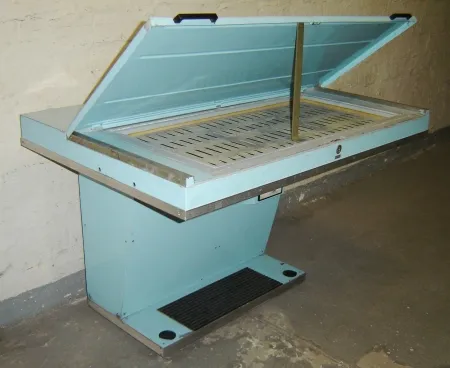
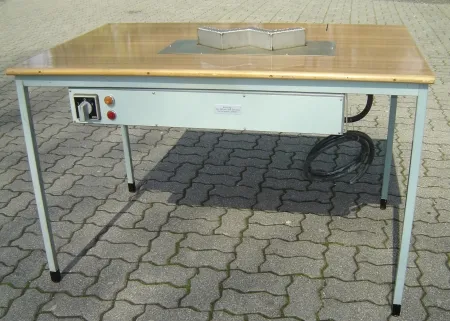
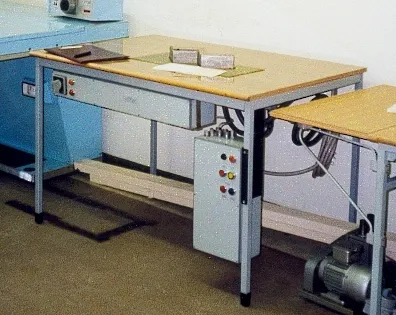
If the “W”-shaped, two-letter steam distribution grid was an “upgrade,” then the ultimate “deluxe” Stasi steam device for manually opening letters with hot water vapor is the “Arbeitstisch der Heißdampf-Öffnungsanlage 532” (English: Work Table for Hot Steam Opening System 532). This modular table was constructed for Department M by the Operational-Technical Sector (OTS) of the MfS in the late 1970’s for manually steaming open envelopes with water-soluble adhesives. The Museum in der Runde Ecke has two of these modified working tables. There is no information on whether “532” is the model number or series number (which would imply there were 531 other models!), and unfortunately I did not record the plate on the front last time in Leipzig, so I cannot confirm its contents until I return.


Credit: Museum in der Runde Ecke

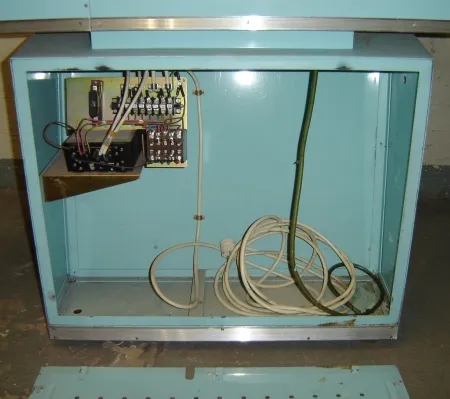
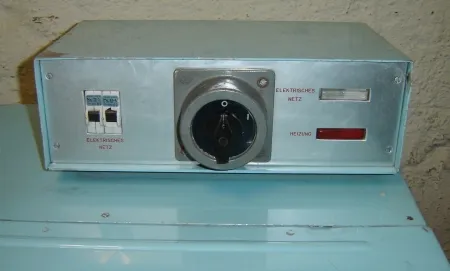
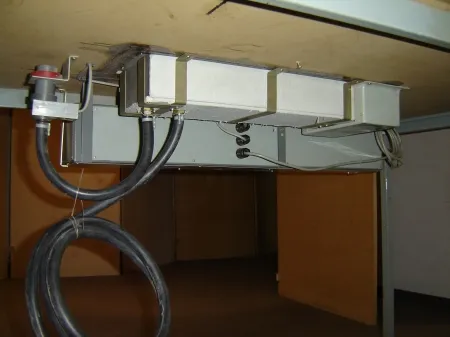
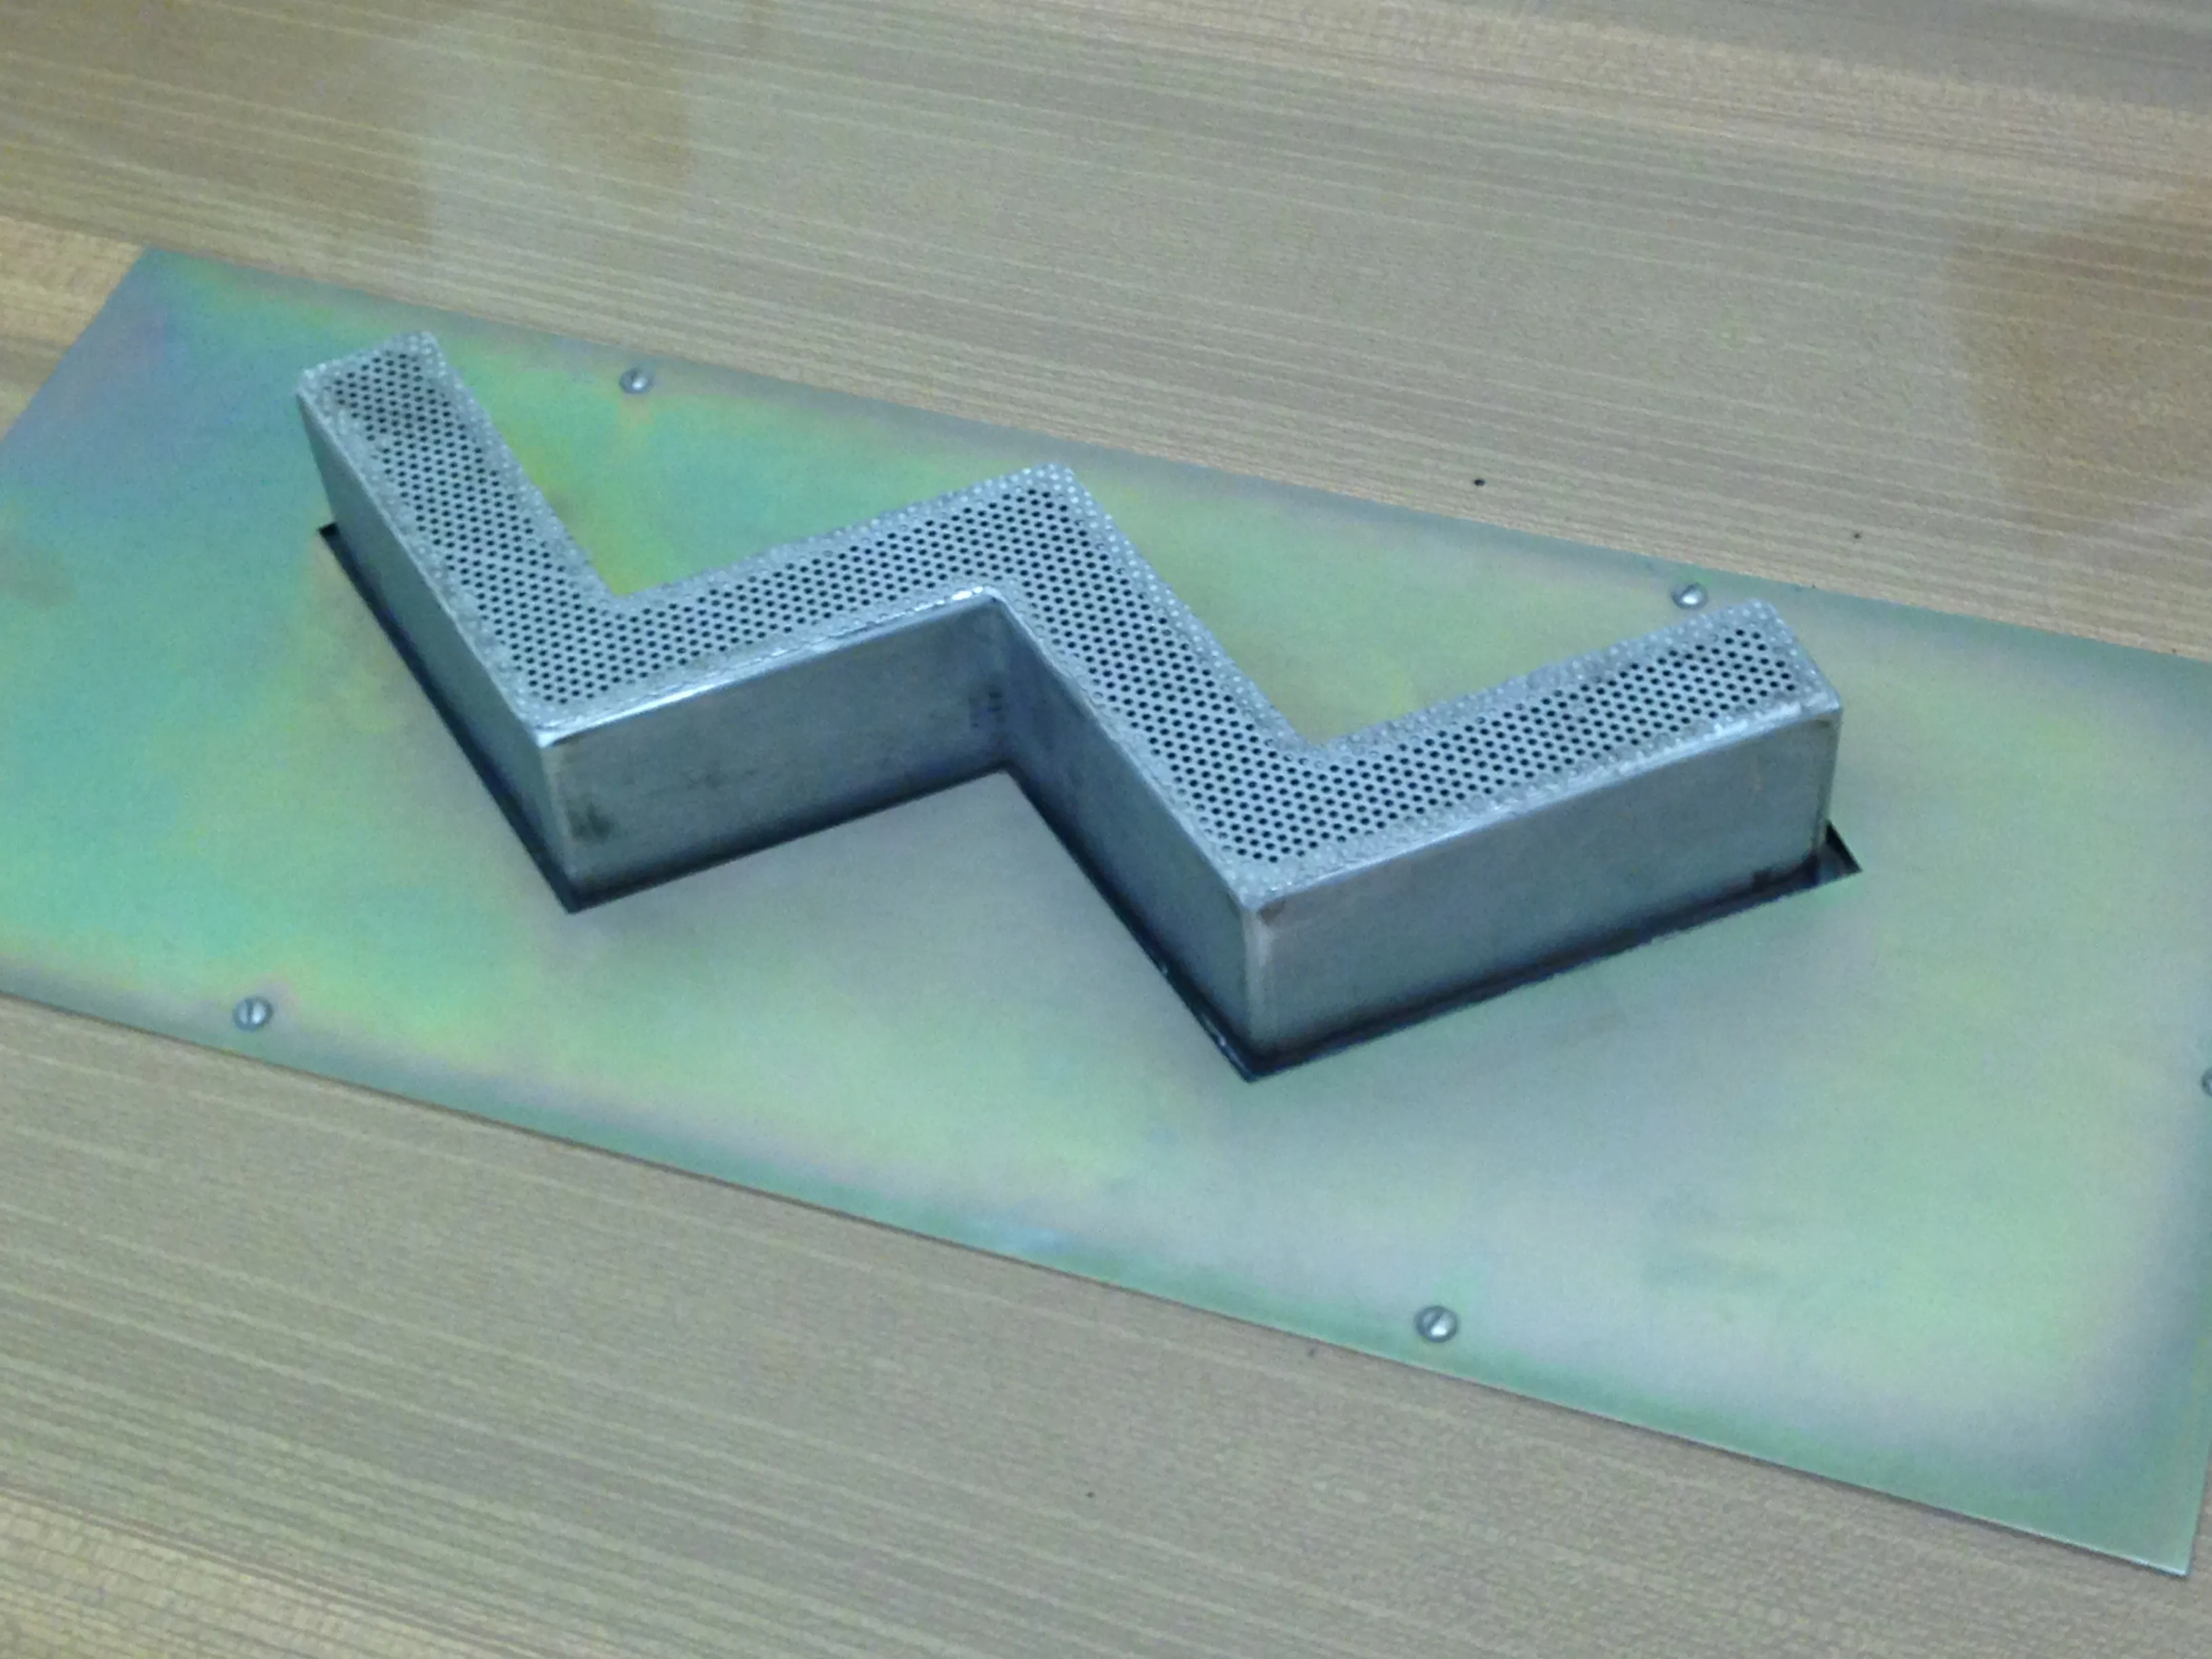
One of the Runde Ecke tables has its own power supply which could be connected to up to three other units to supply power in series (a.k.a. “daisy chaining”). In the center of each table is a “W”-shaped vapor dispersion grid on which two envelopes could be placed. Under the plate is the steam generator, which contained a heater, water storage, and float. While in operation a storage vessel for distilled water was placed underneath. The unit was operated by turning the rotary switch (positions: 0 = “off”, 1 = “pause”, and 2 = “full”) on the attached control panel. Two control lights indicated the operating state of the table, a yellow light which lit when the table was on, and a red light which illuminated when the float inside the steam generator detected that the water was low.


Credit: Museum in der Runde Ecke

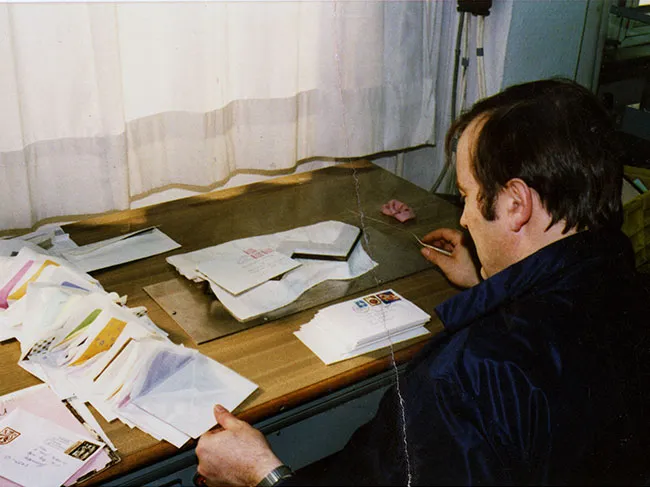
To use the table MfS staff turned the steam generator dial to the “full” position. This activated the heater inside the water receptacle. Once the water reached the correct temperature and began to evaporate the staff placed the flap of the letters on the angles of the W-shaped mesh grids. The vapor, which could reach temperatures of to 100ºC, emerged from the W and dissolved the adhesive. A towel was stretched over the opening to prevent water buildup. Up to 100 letters (between private citizens of the GDR) per hour could be opened on this device.


Stasi staff using the “Work Table for Hot Steam Opening System 532.” Credit: BStU, MfS, Dept. M, Fo 0031, figure 0003

Of the devices I’ve examined so far, this table has little outright evidence that it contains modified parts. Unlike the “hacker aesthetic” of other devices, attention has been given to the various additions to the table to match them to the original. The control panels use commercially-available switches and indicators and are constructed with sheet steel and painted to match the bluish grey steel of the tables. The “W” mesh steam dispersion grid appears to be constructed of aluminum or another treated metal that would not oxidize, and is attached to the table using a plate with measured and symmetrical fasteners. Like the Stasi organization itself, which over time refined their methods according their ideology and what was available, the sharp edges and reused parts on this transformed table are concealed to match the professionalism, efficiency, and attention to detail with which the workers were expected to perform their tasks.


Credit: Owen Mundy

  1. Work Table for Hot Steam Opening System 532 (Inventory no. 00007). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 10, 2017.
  2. Work Table for Hot Steam Opening System 532 (Inventory no. 00354). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 10, 2017.
  3. BStU. Die Stasi und das Postgeheimnis. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 22 – Automation in Stasi postal surveillance: Aufdampftopf


Credit: Museum in der Runde Ecke

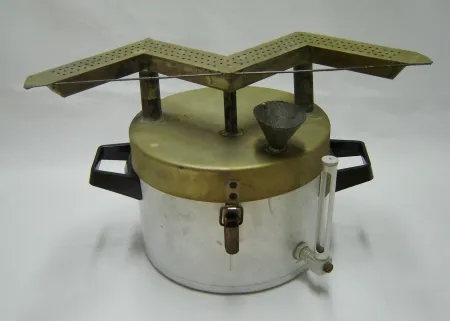
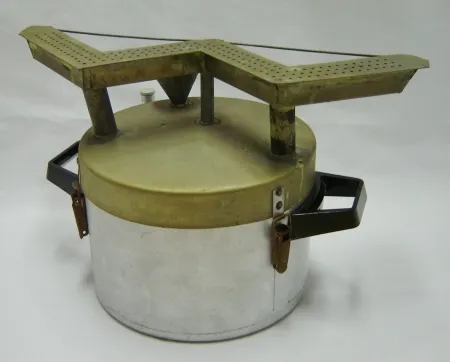
Like other devices constructed in the 1970’s and ‘80s by Department M and the Stasi OTS, this “Aufdampftopf” (“steam pot”) was fashioned using a basic household appliance as a starting point. Starting with a “cooking pot,” as it’s called in the Museum in der Runde Ecke index, the vessel was altered with a tight lid so it could be used to heat water (added via the attached funnel) and generate, collect, and disperse steam for opening letters.

The “W” shape of the vapor dispersing grid on top corresponds to the adhesive edges of, not one, but two envelopes placed end to end on the mesh. Presumably an administrator or other coworker made a human mechanical observation in the spirit of efficiency, suggesting that if the grid was expanded then workers could open two envelopes at once.

Like the Kleindampfentwickler with vapor dispersion grid on its top, the Dampfentwickler made from a steam pot also uses copper tubes and plating in its construction. Likewise, the steam pot additions exhibit a DIY aesthetic that contrasts with the mass produced original object. The copper, again chosen for its malleability and capacity to withstand water, shows signs of use in its darkening patina. It gives the steam pot the appearance of a prop for a dystopian science fiction film, or at least a reference to a real thing, inspiring one to think of a steampunk look popular among cosplayers.


Credit: Museum in der Runde Ecke

The Stasi’s practice of taking bits and pieces from whatever was available might have been based on scarcity given the economic constraints in communist GDR, but their hacked outcomes have a specific “remix aesthetic,” to borrow the term Eduardo Navas uses in his book Remix Theory: The Aesthetics of Sampling. Specifically, the Stasi’s reuse and appropriation of objects and materials towards utilitarian ends expresses itself in the same way the “sampling” of a DJ or musician might. Given the motivations for, uses of, and choices in construction of this device—to secretly open personal communications between individuals and examine their contents (which of course happens on the part of governments and corporations nowadays)—an art historian or anthropologist might term this a classic example of “early hacker”.

  1. Steam generator for opening letters (Inventory no. 00042). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 21 – Automation in Stasi postal surveillance: Kleindampfentwickler with nozzle

The Museum in der Runde Ecke in Leipzig has an amazing collection of devices found in the Leipziger district administration office (BVfS) during the dissolution of the Stasi. These are listed online in a thorough index with photos and descriptions. Their images are much better than those I was able to make through the glass of their museum displays, and while I’ve contacted the Citizen’s Committee about making new ones, they hopefully won’t mind if I reproduce some of them here in the meantime.


Credit: Museum in der Runde Ecke

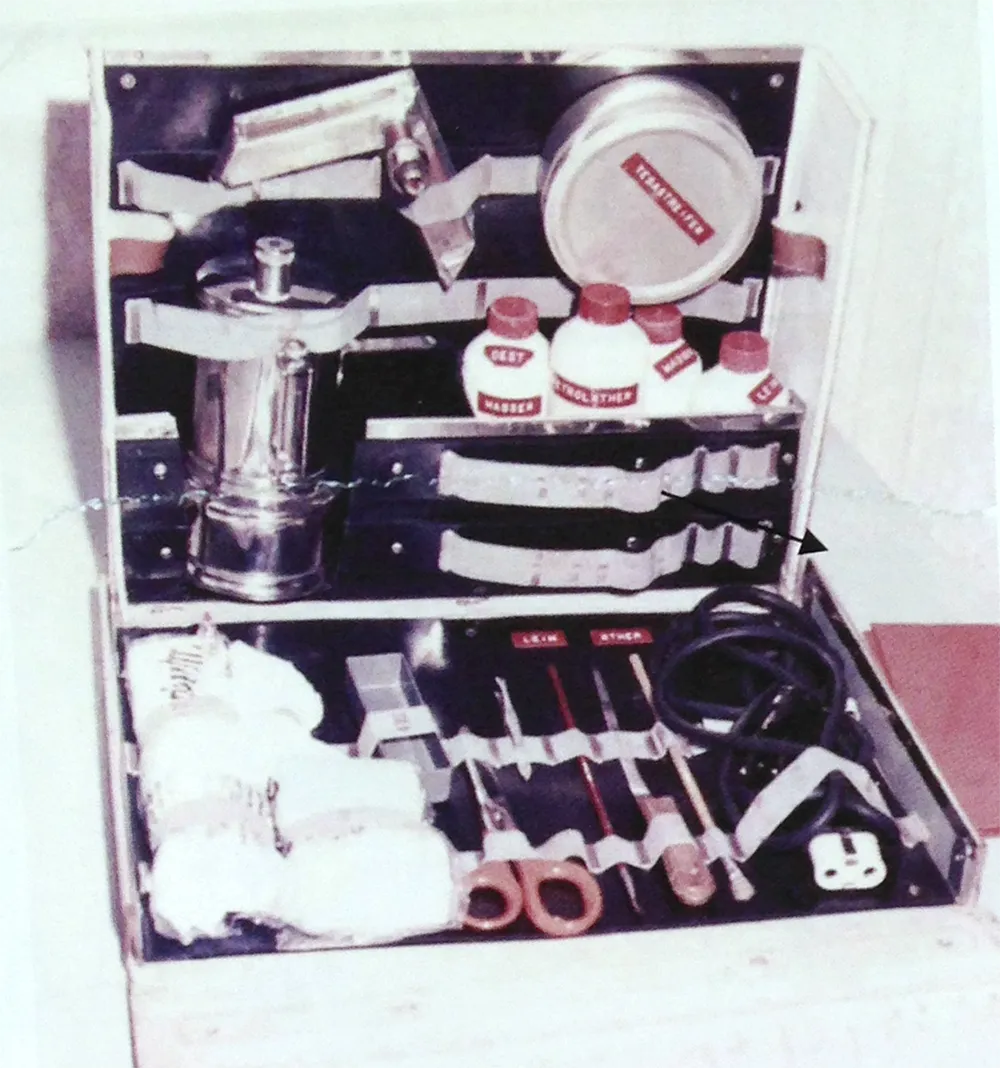
This steam generator was used, like the Kleindampfentwickler in my previous post, for opening “suspicious” letters. The Stasi Department M works directed the steam from the nozzle at the envelope to loosen the water-soluble glue on the flap. Like the Kleindampfentwickler, it was originally a mass-produced device (the Runde Ecke description states it was originally a medical inhaler). It has a glass tube indicating water level, and was stored in a case containing other working materials (which were not preserved) such as “ether, distilled water, glue, knife, scissors, brushes, adhesive strips and cleaning cloths.”
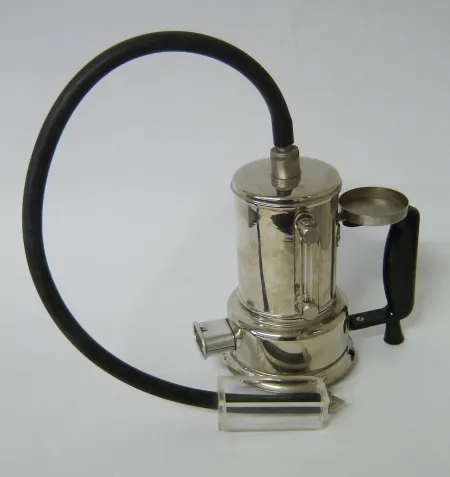
  1. Steam generator for opening letters (Inventory no. 00031). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 20 – Automation in Stasi postal surveillance: Kleindampfentwickler

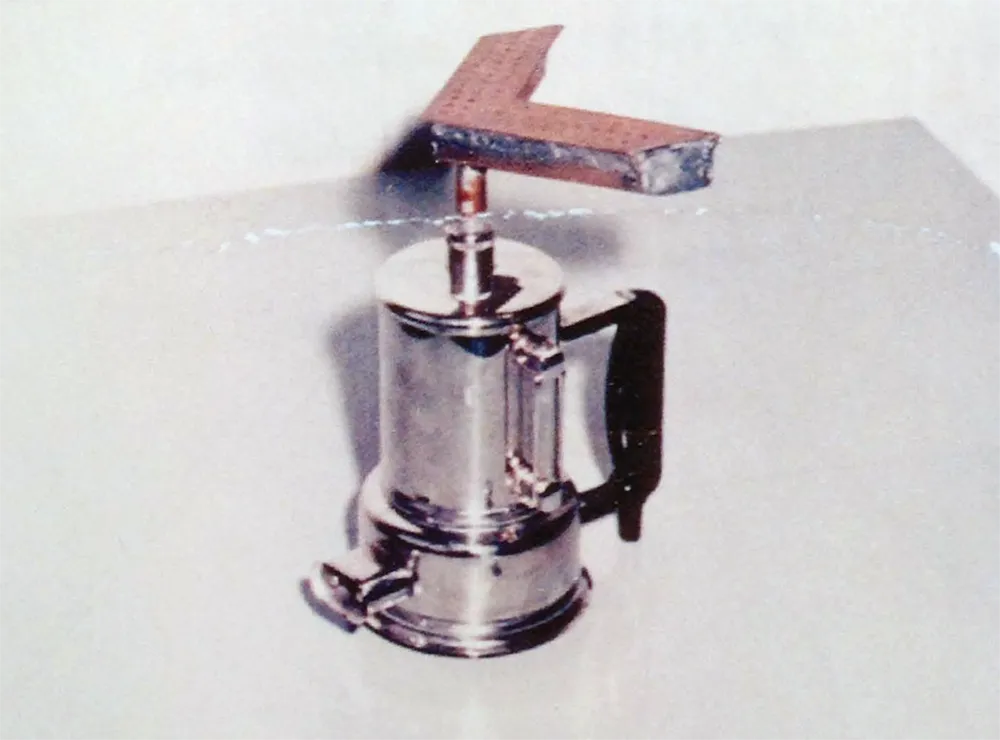
Department M, along with the Stasi OTS (Operativ-Technische Sektor), developed and implemented numerous technical tools, intelligence checks, and operational activities to speed their postal surveillance in the GDR. By the 1970’s, the department was already using various modified household appliances or industrial devices to assist in steaming open and closing letters. One example is this “Kleindampfentwickler”—a “small steam generator,” which appears to be a modified espresso maker or water boiler, with an added, V-shaped steam outlet.


The Kleindampfentwickler (Credit: BStU)

The materials and intentional flat and curved lines in the design of the chrome base and plastic handle suggest it was mass produced. The Stasi probably chose the kettle for the wide base and low placement of the electrical connection which serve to keep the center of gravity low and prevent tipping. They used a V-shape for this and other steam outlets to match the angled shape of envelope flaps. This one is designed to loosen the glue on a single envelope, while other steam outlets could accommodate more.

The crude construction of the modified steam outlet sharply contrasts with the retail-ready kettle. The choice of soldered copper for the material of the pipe leading upwards and steam outlet were probably based on what was available, water resistant, and easy to work with. Copper is used for speciality roofs and gutters, with the seams joined together using heat and solder. The joinery on the Stasi’s addition is not pretty, making it stand out against the base, but it exemplifies the experimental methodologies of the engineers who worked behind closed doors, as well as the belief the aesthetics or secrecy of their work would never be scrutinized.


The Kleindampfentwickler Operational Carrying Case (Credit: BStU)

Stasi / Facebook / Big Data DAAD Day 19 – Automation in Stasi postal surveillance: The PiD Trap

In the beginning of the 1970s most of the work of Department M was performed by hand. This labor included sorting and selecting suspicious mail, manually steaming it open, examining the contents, transcribing, copying or photographing the interior or exterior of the letter, in some cases, examining the letter for conspiratorial or stealth writing, resealing the envelope, and placing the letter back into circulation at Deutsche Post. As the secret operations heightened the suspicions during the Cold War, and with the postal service increasingly relied upon for cross-border communications thanks to the Berlin Wall preventing face to face meetings, Department M received more pressure to increase their efficiency through mechanical means.

One such machine used by the Stasi was referred to as the “PiD Trap.” This electronic device automatically scanned and screened regular letters from printed materials like newspaper excerpts, church letters, and advertisements. Like the organizational systems the Stasi employed, this apparatus made it possible to divide and focus the labor of their workers and expedited the sorting and determination of suspicious mail and “negative” or “hostile” influences from the west in the form of Politisch-ideologische Diversion (PiD). (Labrenz-Weiß, 28)

  1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

Stasi / Facebook / Big Data DAAD Day 17 – Stasi networks and Facebook Social Graph

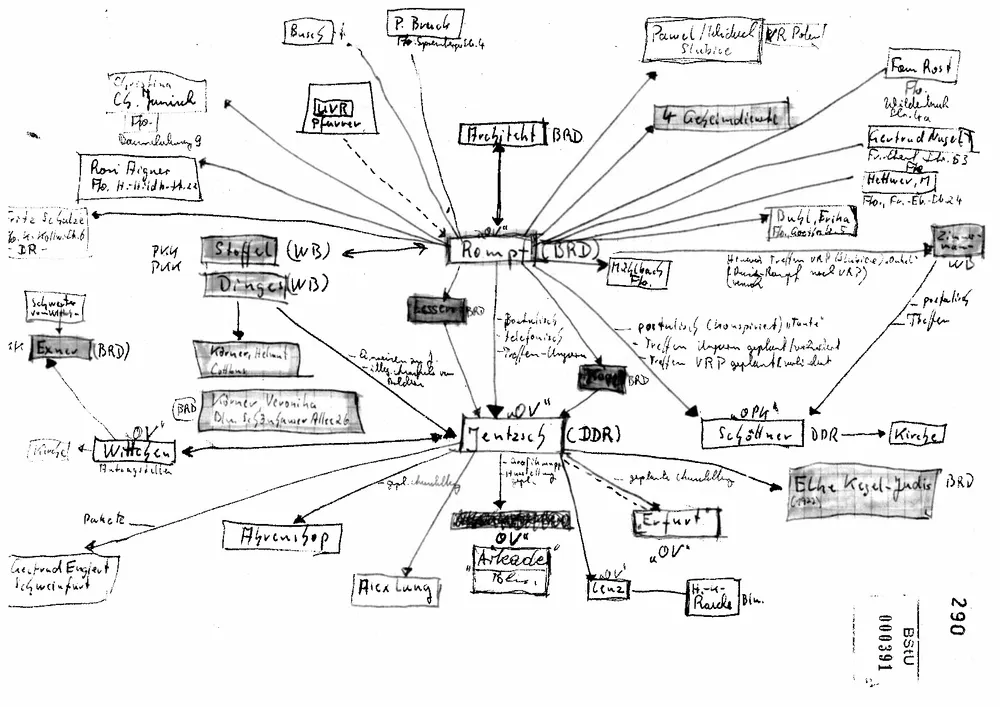
Similar to how Facebook uses a user’s connections to determine information about them, the Stasi considered all information they could gather about a person in their intelligence campaigns. They incorporated not only the contents of a target’s mail, but information about professional and personal relationships, love affairs, and organizations to which they belonged. (Reinicke, 106)


Source: ProPublica/BStU

This attention to not only the contents of a person’s postal communications, but their social connections can be evidenced in this hand-made graphic discovered at the BStU by Julia Angwin. The graphic shows forty-six connections, linking a targeted citizen to other potentially interesting persons (e.g. an aunt), places (e.g. “church”), and meetings (e.g. post, phone). Through whichever means necessary the Stasi made and utilized these connections in order to gain additional insights and institute methods of control.


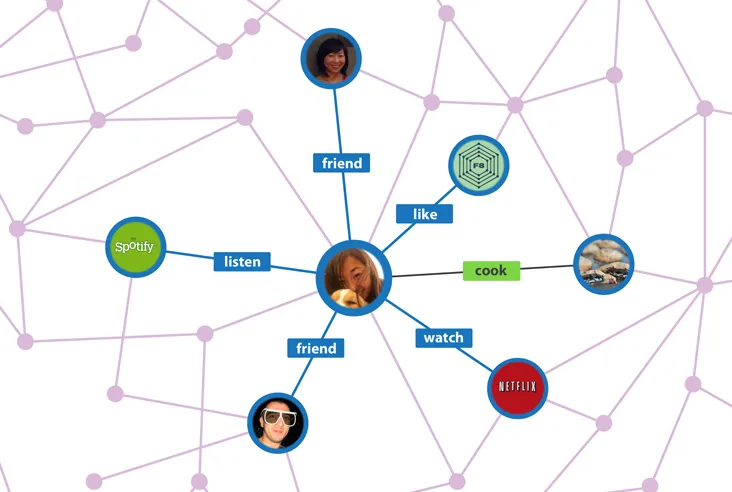
Visual explanation of Facebook Social Graph. Source: Business Insider

This image reinforces the notion that the Stasi’s work was mostly a manual, often experimental, labor. It also tells us their work in surveillance and control, which is seen as a miserable, tyrannical sort, is now standard business practice among the software-automated surveillance capitalist models of the internet used by Facebook, Google, and others. Just as Department M workers like Gerd Reinicke mined the post for intelligence and PiD, the same basic processes the Stasi developed, now used as software by Facebook, are also at work in China, Iran, and other countries to filter and control what people can say and read through elaborate censorship software systems.

  1. Hanna Labrenz-Weiß. Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.
  2. Reinicke, Gerd. “Mitlesen für den Klassenkampf: Postkontrolle der Stasi”. In: Heimliche Leser in der DDR: Kontrolle und Verbreitung unerlaubter Literatur (ed. Siegfried Lokatis). Berlin, 2008.
  3. Angwin, J. (2017). You Know Who Else Collected Metadata ? The Stasi. ProPublica, 6–8.

Stasi / Facebook / Big Data DAAD Day 16 – Notes from a former Department M surveillance operator (part2)

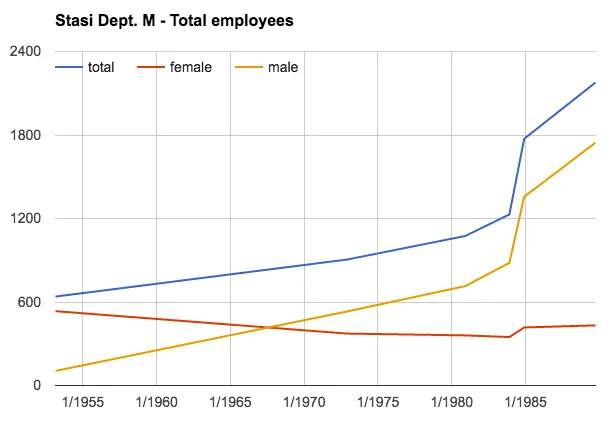
During the seven years Gerd Reinicke worked for Department M the scope of surveillance grew steadily. This is particularly evident in the 1980s, when as the government became more and more concerned of the “class struggle,” they dramatically increased the number of operators in Department M, more than doubling the size from 1980 to 1989.


Stasi Dept. M – Total employees (data from Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.)

Reinicke and his coworkers in the “Evaluation and Information” unit constantly tried to increase the “Trefferquote” or “hit rate” of material worthy of confiscation by memorizing large numbers of postal codes, names, and handwriting. Their shift managers carefully sampled the work of individual employees, checking for missed letters, which could result in punishment and disciplinary measures.

Once a citizen or group had been classified as “operationally interesting” then all their mail was withheld for inspection. Citizens of the GDR who sent private messages critical of the government or its leaders through the mail first, had their mail confiscated, and second could be brought to court on charges of “anti-state agitation” according to Section 106 of the Criminal Code of the GDR. (Reinicke, 105)

  1. Reinicke, Gerd. “Mitlesen für den Klassenkampf: Postkontrolle der Stasi”. In: Heimliche Leser in der DDR: Kontrolle und Verbreitung unerlaubter Literatur (ed. Siegfried Lokatis). Berlin, 2008.

Stasi / Facebook / Big Data DAAD Day 15 – Notes from a former Department M surveillance operator

In the essay, “Eavesdropping for the class struggle: Postal control of the Stasi,” from the book, “Secret readers in the GDR: Control and distribution of illicit literature” (ed. Siegfried Lokatis), Gerd Reinicke describes his work in the “evaluation and information” section of the Stasi’s Department M. He explains his job was to assess and classify the contents of mailings, personal letters and printed materials, and in extreme cases, make decisions about confiscation.

This work was not easy. The stream of mail was constant and so he had a limited time frame for his work. He operated in secret, but also had to consider the public perception of his decisions. While technically illegal, the government watched all mail moving within the country, as well as that leaving or arriving in the GDR. As far as the population was concerned it was an “open secret,” because they observed the effect of the government’s policy of opening mail to remove valuable items, as well any writing or media considered to be “Politisch-ideologische Diversion (PiD)” (English: “Political-ideological Diversion”)—a task which was not as clear as it might seem.

Upon his hire was told to collect information on people and facts that might be “operatively interesting” to intelligence services. But he also received instructions to remove “anything unnecessary.” This work reflects the dual role that Department M played for the SED as a surveillance and control mechanism. On one hand, they watched for communications between spies or dissidents, but they were often a censorship apparatus.

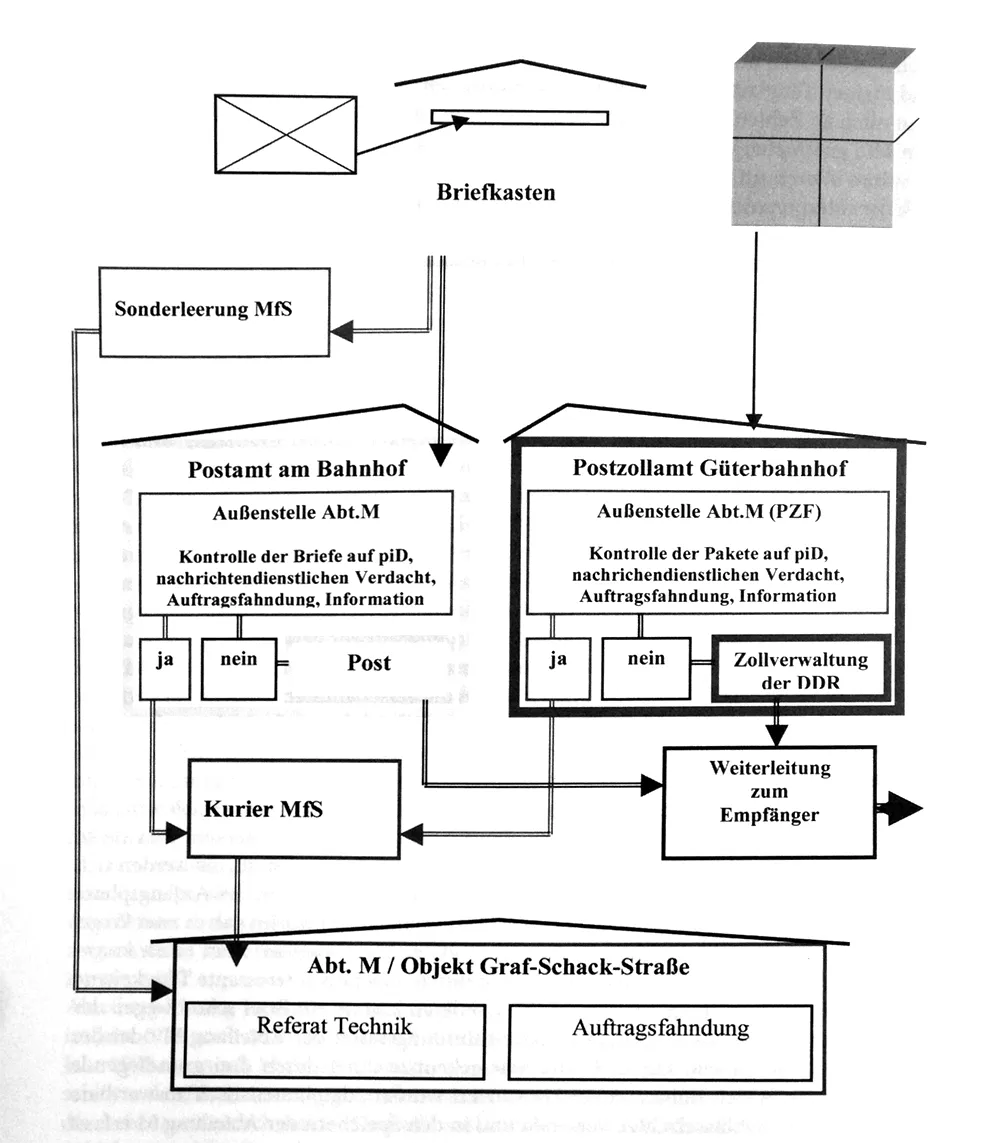
This flowchart shows the three basic categories by which mail was classified, and subclassified, specifically, as “messages suspicious of being intelligence communications,” “messages suspicious of being PiD,” and “messages determined to be ‘interesting content’.” The assignment into of any of these categories determined further routing into the Department M machinery.


Heimliche Leser in der DDR: Kontrolle und Verbreitung unerlaubter Literatur (ed. Siegfried Lokatis)

These broad definitions also underline the ambiguity in how their surveillance and censorship was officially applied. For example, in dealing with Western and dissident literature, these instructions were followed in different ways. Sometimes operators were generous in their interpretation of “class struggle appropriate” materials, while other times he characterizes their subjective interpretation as “petty.”

  • Hanna Labrenz-Weiß. Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.
  • Reinicke, Gerd. “Mitlesen für den Klassenkampf: Postkontrolle der Stasi”. In: Heimliche Leser in der DDR: Kontrolle und Verbreitung unerlaubter Literatur (ed. Siegfried Lokatis). Berlin, 2008.
  • Stasi / Facebook / Big Data DAAD Day 14 – Department M OibE groups

    Thanks to the implementation of index cards across the MfS, Department M had access to sender and receiver addresses, contacts, relatives, etc. to inform their surveillance work. By 1970, the department had instituted the following operational steps for examining mail. Numbers 3–6 were considered highly secretive and operations were performed under the codename “Eagle Flight”.

    1. Check if the sender or recipient existed in the police card index
    2. Establish an “Operational Comparison Card” to record information found in the mailing
    3. In the case of a suspicious mailing, carry out a search of the mail box
    4. Create photographic documentation of letterheads
    5. Compare the handwriting or typewriting font, spelling, etc. of the letter head. Identify any stealth writing.
    6. Form a special “OibE” group to check mail boxes.

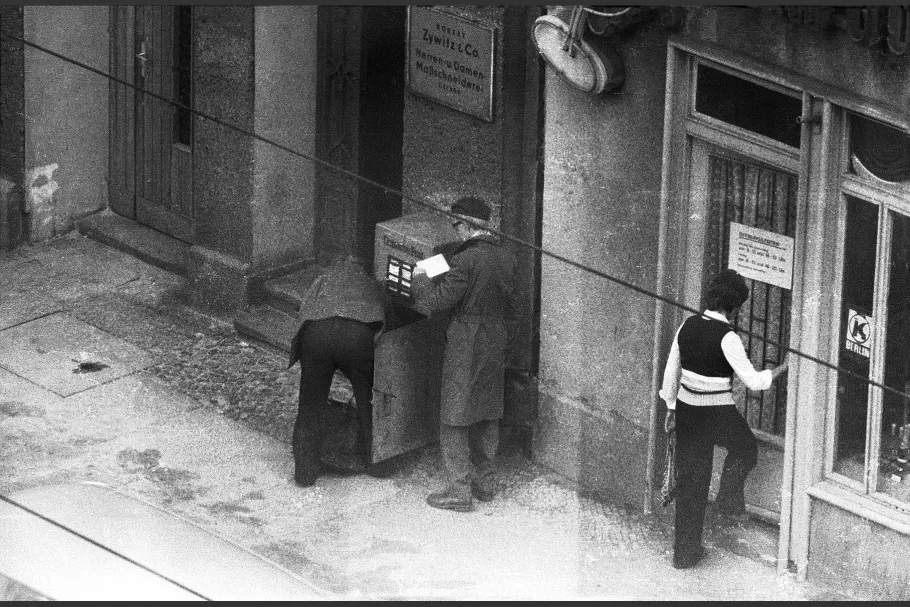
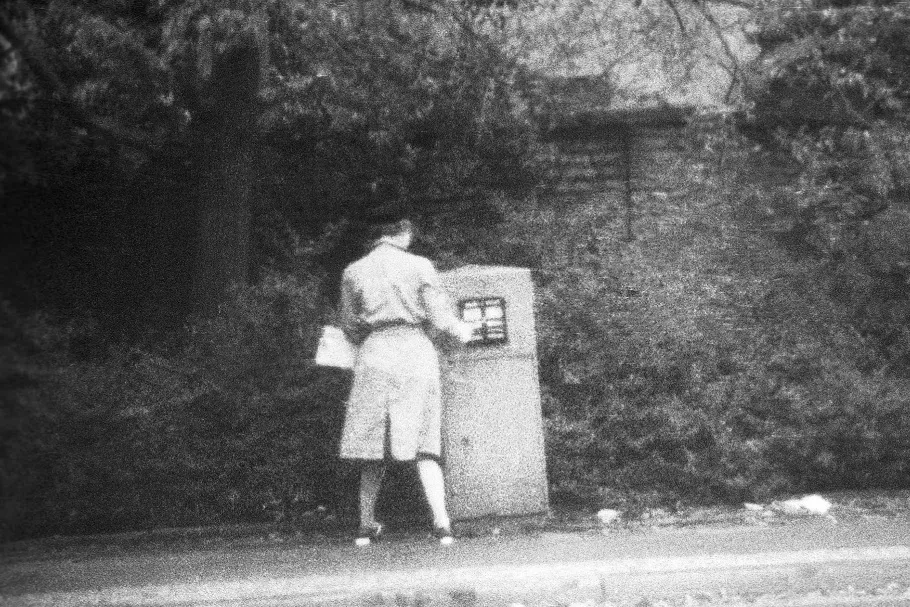
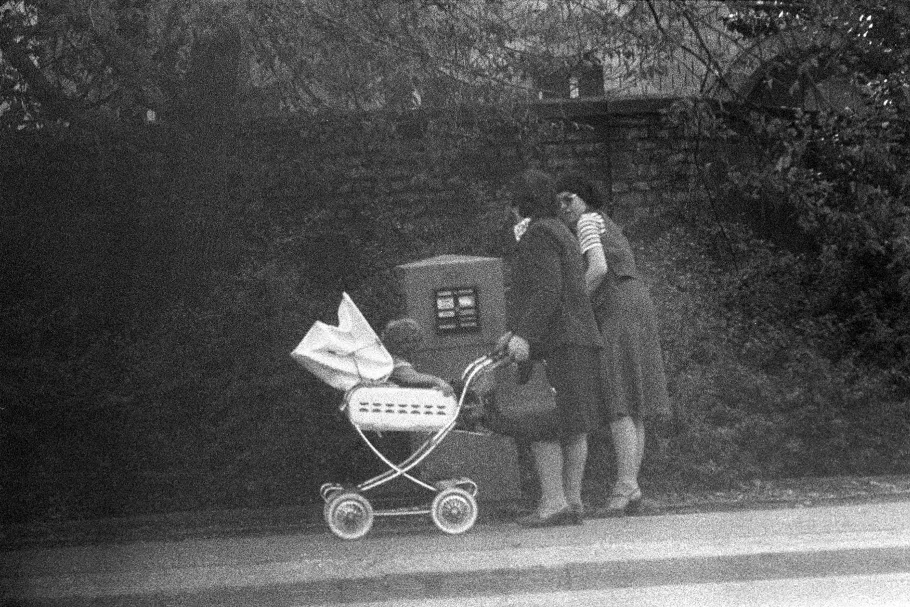
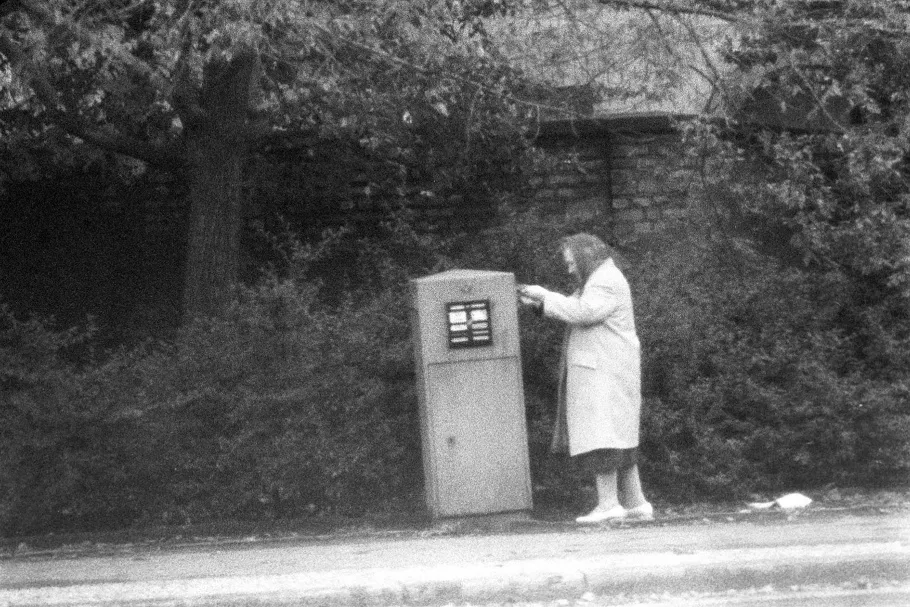
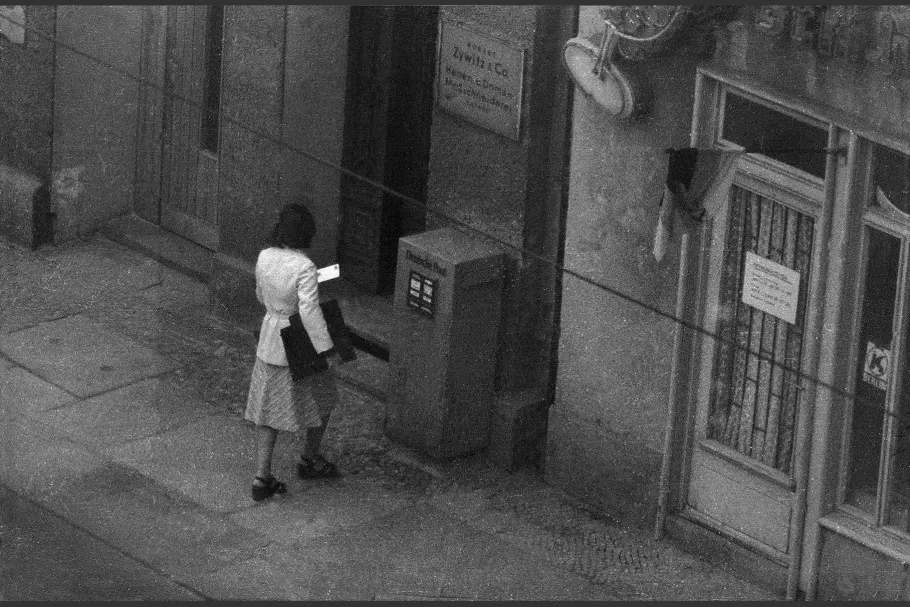
    Offizieren im besonderen Einsatz (OibE) (English: Officers in Special Operations) groups were formed specifically to monitor, and in some cases, empty mailboxes under the cover of the Deutsche Post uniforms and vehicles. They photographed persons of interest as they dropped mail off, and then opened the mail boxes and examined the contents of letters before they even reached the post office. Photographic records of their work exist, and were presented in the exhibition, “Ein offenes Geheimnis. Post- und Telefonkontrolle in der DDR” (English: “An open secret. Postal and telephone control in the GDR”) (Labrenz-Weiß, 22–24)


    Source: BStU

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 13 – The Stasi’s Electronic Databases

    The number of cards in the Stasi indexes grew to an incredible 39,000,000 by 1989. In order to provide constant access to this massive material data system they created various special storage units and containers as it expanded. The current mechanical powered card indexes in place at the BTsU were found after the end of the GDR and are still in use in order to meet requests of citizens who wish to view the data the Stasi kept on them.


    Mechanical index card file organization system used by the Stasi.

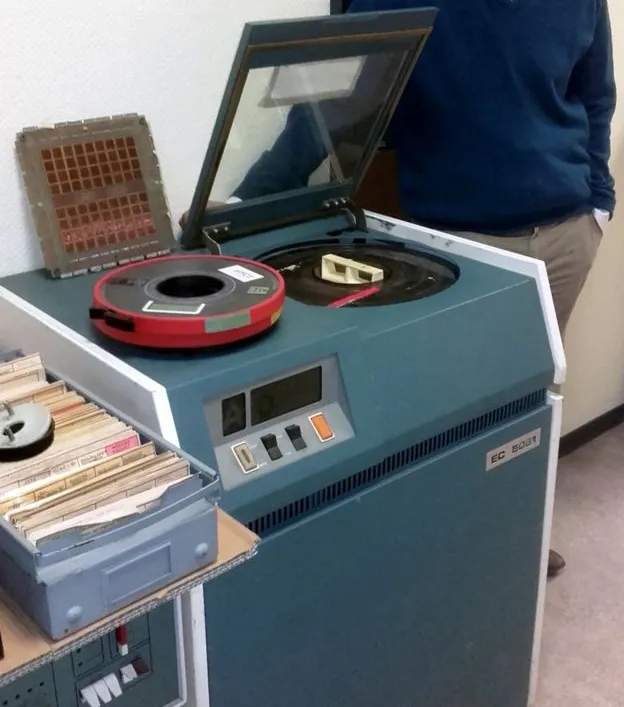
    Beginning in the 1960s, the MfS also used various electronic databases to track citizens.* These databases were never fully implemented as a primary source of storage because computing and software available in the GDR at the time, even machines stolen or purchased in the west, were unreliable. For six years the Stasi mirrored essential data from the F16 personal card into an electronic format. In 1975, Department XII, responsible for central data collection, information and storage, introduced the “System of automatic pre-selection” (SAVO) which allowed workers to verify that a person was “not yet recorded” in the system. This considerably reduced the time it took for verification, however it still required a substantial 12–21 days for a process to complete.

    By 1986 SAVO 2.0 was introduced providing printing functionality, increased capacity—now containing all data from the F16 card—and reducing search times to 1–6 days. It also provided teletype connections eliminating the need for couriers and allowing multiple agencies (passport control, tourism, etc.) to use the same data source simultaneously. (The Key to Power, 6) While this greatly modernized the surveillance workflow of the Stasi, it continued to act only as a duplicate of the F16 card, which was still faster for priority inquiries, and less susceptible to errors.


    A computer used by the Stasi. Source: BBC

    The logic for these implementations is echoed in modern database planning and use. While redundancy is employed for backups and increasing access speed across global networks, there is still a “master” copy of all data, or in the case of distributed system, automated processes (software) that merge and maintain distributed data into a master. Like the Stasi’s decision to completely mirror portions of the F16 system, modern systems use whichever implementation is most reliable for the master, while summarizations of that data may be “pushed” to other indexes for faster retrieval.

    The Stasi’s use of multiple systems, as well as the F16 and F22 card also preempt the concept of “joins”, which is a powerful feature in relational database management systems (RDBMS), to allow various pieces of data to be spread out across multiple indexes. Like the registration number on the F16/22 cards, records from multiple discrete RDBMS can be “joined” by matching a single identification field in order to supply additional, or limit access to other data, when performing queries.

    Multiple other computerized database systems were developed or used by the Stasi, including SOUD, a collection of information on the “enemy” shared between the GDR, Bulgaria, Cuba, Poland, the USSR, Czechoslovakia, Hungary, and Vietnam. The most expansive of all their electronic indexes, was the central database of personal data (ZPDB). Introduced in 1981, by the end it contained records on over 1,320,000 people, 417,000 situations, 558,000 objects, and numerous related information.

    The desire to track not just people, but occurrences and objects is directly visible in the largest person tracking organization today. In Facebook’s “Social Graph”, introduced in 2007, any person, place, thing, event, anything that can be named, is recorded in a massive attempt to commodify everything and our connections to it. Like the Stasi ZPDB, everything in the Facebook Social Graph is indexed by a unique identification string as single record, which Facebook considers a “node,” with links or “edges” that connect them. These definitions are based on Facebook’s desire to do data science on the their information, applying statistics and other mathematical operations from graph theory in order to understand their data and predict (and manipulate) the behavior of users.

    *Regrettably, all electronic databases and their magnetic storage was destroyed not long after the end of the GDR. Meaning, BStU staff now use the original paper F16 card system to provide services to the public.

    1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.

    Stasi / Facebook / Big Data DAAD Day 12 – The VSH card system

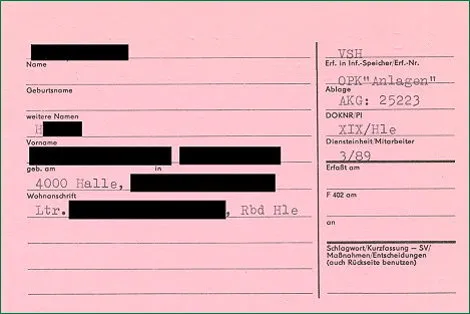
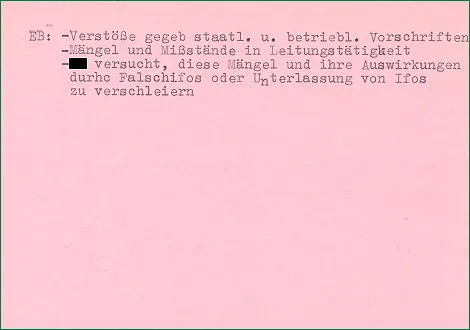
    The VSH index card system was yet another data storage method developed by the Stasi for monitoring and controlling the population. Introduced in 1974, the system used a red F401 card for all “secretly policed” persons, and a corresponding white F402 information card once that person was captured and began informing for the MfS. The system contained information not included on the Kerbloch index, for example, specifics deemed to be “operationally significant” like that person’s activity in the MfS, and ensured the flow of information on persons of interest across operational departments, districts, and facility services. The VSH files enormously expanded the number of persons surveilled, and were the most important cards used by operational service units until the end of the MfS. (The Key to Power, 6)


    Front of the pre-compaction, search and map card. Source: BStU


    Back of the pre-compression, search and map card. Source: BStU

    The VSH cards were divided into 15 categories ( PK ):

    • PK 1: Staff and agents of the enemy intelligence services
    • PK 2: Senior staff of the centers of political and ideological diversion
    • PK 3: Members of terrorist organizations and individual terrorists
    • PK 4: Members of Zionist hostile immigrant, clerical and other organizations
    • PK 5: persons who carried out orders from hostile intelligence agencies, centers of the political-ideological diversion, Zionistically hostile immigrant, clerical and other organizations against the states of the socialist community
    • PK 6: People unmasked as enemies of the opponent
    • PK 7: people who had not offered the information that was real
    • PK 8: persons who carried out provocative actions on the territories of the states of the socialist community as well as against their representatives and citizens
    • PK 9: Persons who were expelled from the states of the socialist community
    • PK 10: People who had committed particularly dangerous crimes
    • PK 11 diplomats and employees of diplomatic and consular missions of NATO , Japan and the People’s Republic of China
    • PK 12: correspondent of NATO -Mitgliedsländer, Japan and the People’s Republic of China
    • PK 13: Employees of trade and economic representatives
    • PK 14: Members of organizations that have been engaged in international smuggling on a large scale
    • PK 15: Persons whose activities were directed at a damage to the economy of the states of the socialist community
    1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.
    2. BStU: ( VSH ) of the Central Evaluation and Information Group ( ZAIG )
    3. BStU: Pre-compacting, search and identification card ( VSH ) of Division 1

    Stasi / Facebook / Big Data DAAD Day 11 – Kerblochkarten


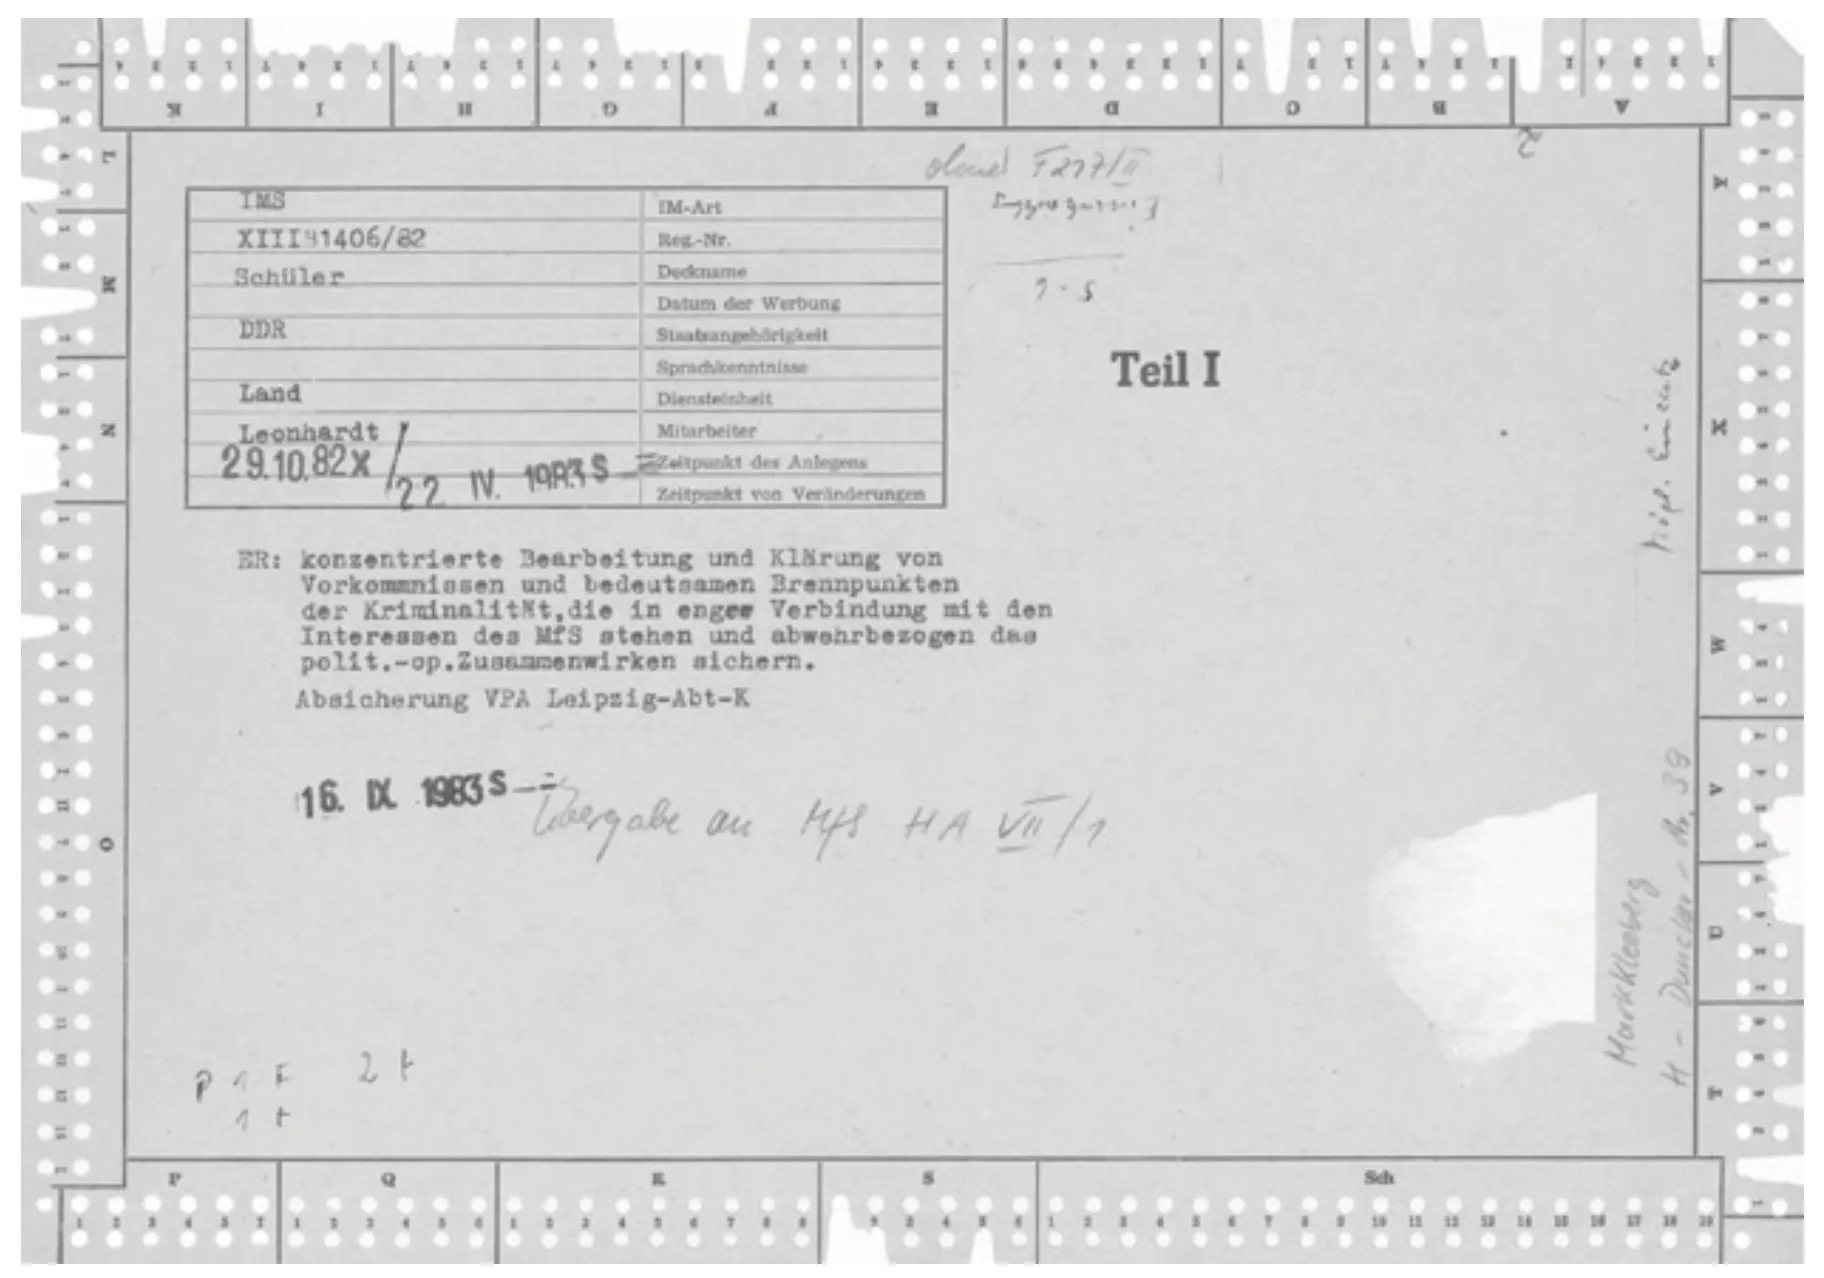
    A Stasi Kerbloch card

    The Stasi used several other card systems to assist their postal surveillance. The Kerblochkarten (English: Kerbloch cards) system allowed storage of data encoded as a series of hand-made notches. Like other punch card systems, groups of cards could then be automatically processed by a machine based on the presence of notches and a predefined key. The Kerbloch card system made it possible to perform statistical evaluations and targeted searches on up to 350 cards/persons at a time. Importantly, this card amended the functionality of the the F16 cards and allowed the Stasi to quickly search for potential informants by querying characteristics relevant to a particular job. While anyone who has used a computer spreadsheet software today would take this sorting and searching functionality for granted, this was a highly useful tool for the Stasi, which by 1989 had amassed over 39 million index cards. (The Key to Power, 5)

    1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.
    2. BStU: Kerblochkarten (KK)

    Stasi / Facebook / Big Data DAAD Day 10 – Card systems of the Stasi

    The early days of the Stasi were marked by the development of new systems for monitoring the population. In the 1950s, having already incorporated a post-WWII file system used for denazification, the MfS implemented three new index card types to track citizens, all of which were stored in a central card index. These cards were distinguished by color and used to track persons considered hostile to the state (form A1 which was yellow), official staff (form B1, later replaced by the blue and grey F19), and persons who were arrested (the red, form C1).

    While official staff had titles and were on the payroll, the Stasi used hundreds of “unofficial staff.” These “Inoffizielle Mitarbeiter” (or IMs) were either foreign citizens who turned over valuable information like trade secrets, or domestic informants who spied on their colleagues, neighbors, and relatives (and sometimes even spouses). While money was a primary motivation, they were compelled for a number of other reasons, including blackmail, ideological commitments to the GDR, or gifts other than money, like lavish vacations, prostitutes, and official state awards. In fact, the Stasi implemented an impressive number of medals and rewards in order to convince both IMs and official staff to maintain loyalty and faithfully contribute their labor to the state. (Macrakis, loc 386) These awards are not unlike the loyalty cards, badges, and other gamification tactics that today’s corporations employ across their databases of customers in order to increase brand allegiance and sales.

    Similar to modern software development, the Stasi index card systems, like many of their methods over the years, were constantly being reworked and improved with each new iteration. For example, while the previous system used separate cards to track “enemies” and “friends,” as the Stasi learned to coerce those formerly consider hostile into becoming secret informants it became necessary to track persons who evolved into “frenemies of the state.”

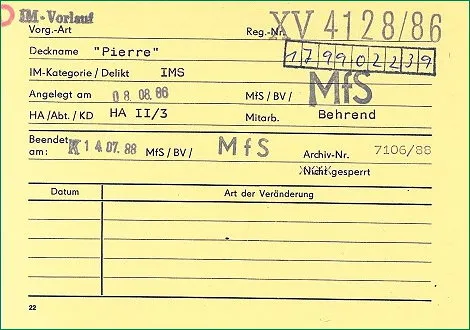
    This situation presented a particular problem, as the Stasi needed to record and track personal data on these people, but their real identities needed to be protected should they agree to turn over valuable information. For these persons the Stasi implemented a separate “transaction card” (F22) that augmented the standard cards. The change updated the yellow card (F16, formerly A1), which contained the real name, address, birth date and place, occupational status, workplace or school, and the red card (F18, formerly C1), used for those arrested, which contained this information, as well as a mugshot, a visual description, and data related to their crime, and added a registration number if they were a Stasi informer or agent. (The Key to Power, 3–4)


    The central operation card “F22” Credit: BStU

    The new “transaction card” (F22) recorded Stasi informants only by this registration number, as well as a secret code name and name of the case officer who managed the agent. Finding the real name of a Stasi operative meant matching not only the registration numbers on these cards, but additional comparisons, because many agents purposely shared registration numbers to add extra layers of secrecy. (Macrakis, 78) This method is similar in theory to modern relational database lookup tables, where a user’s personally identifiable information (PII) is separated and protected from data dumps containing so-called “anonymized data” , or public key encryption, where data is transmitted securely by performing mathematical operations on it using a combination of a unique private and public key.

    1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.
    2. Macrakis, Kristie. Seduced by Secrets: Inside the Stasi’s Spy-Tech World (Kindle Location 1615). Cambridge University Press.
    3. Jason Koebler This Visualization of NYC’s Taxis Shows the Promise and Pitfalls of Big Data Motherboard (2014)
    4. Alex Hern New York taxi details can be extracted from anonymised data, researchers say The Guardian (2014)

    Stasi / Facebook / Big Data DAAD Day 9 – MfS Department M (1960’s developments)

    The implementation of zip codes across West Germany in 1961 made it much easier to monitor postal traffic between east and west. The Berlin Wall was erected in that same year, leading to a heightening of Cold War suspicions and increased emphasis on monitoring movement of information between east and west.

    The 1960’s also saw the various reorganizations and new leaders, including Lieutenant-Colonel Walter Mehrbach, whose years of experience in the postal service led to the development of the first training manual for Department M, and certification courses in mail surveillance at the MfS Law School in Potsdam. (Labrenz-Weiß, 21)

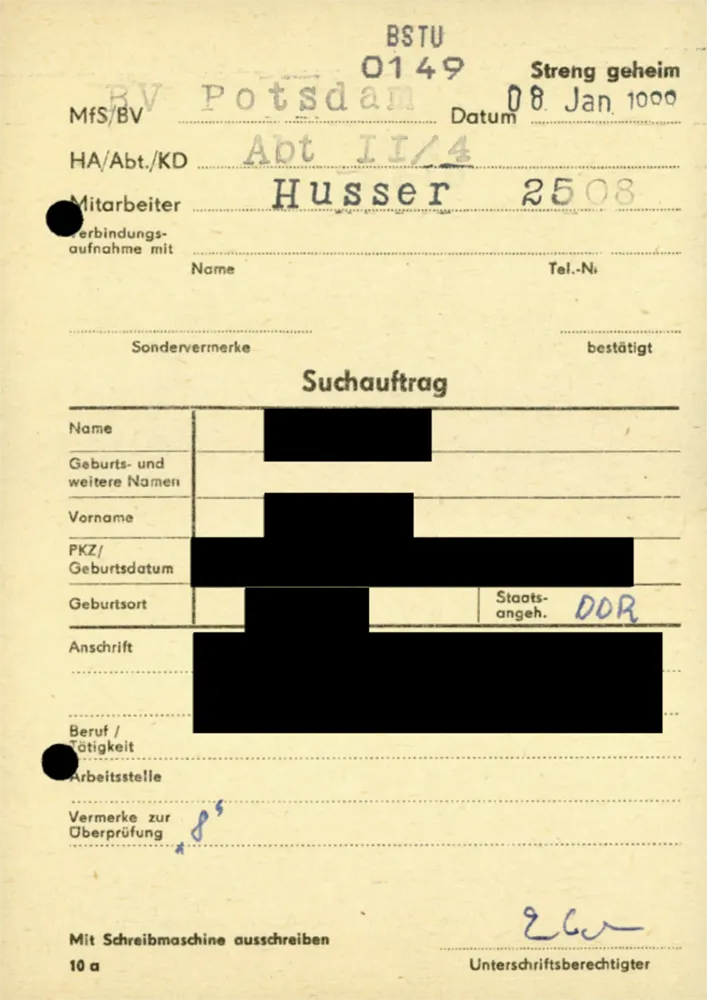
    As Department M grew in the 1960’s, so too did the amount of mail they examined and information they recorded. This demand for intelligence required constantly expanding data storage methods, which led the department to develop a card system for efficient alphabetical sorting and identification of people, places, and objects on both sides of the East/West German border. (Labrenz-Weiß, 19) I’ll dig in a little deeper over the next few days on these cards, for now a photo from my BStU archive research last summer:


    BStU: MfS, BV, Potsdam, Abt II 764 pg 6

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 8 – MfS Department M (A captured letter from the BStU archives)

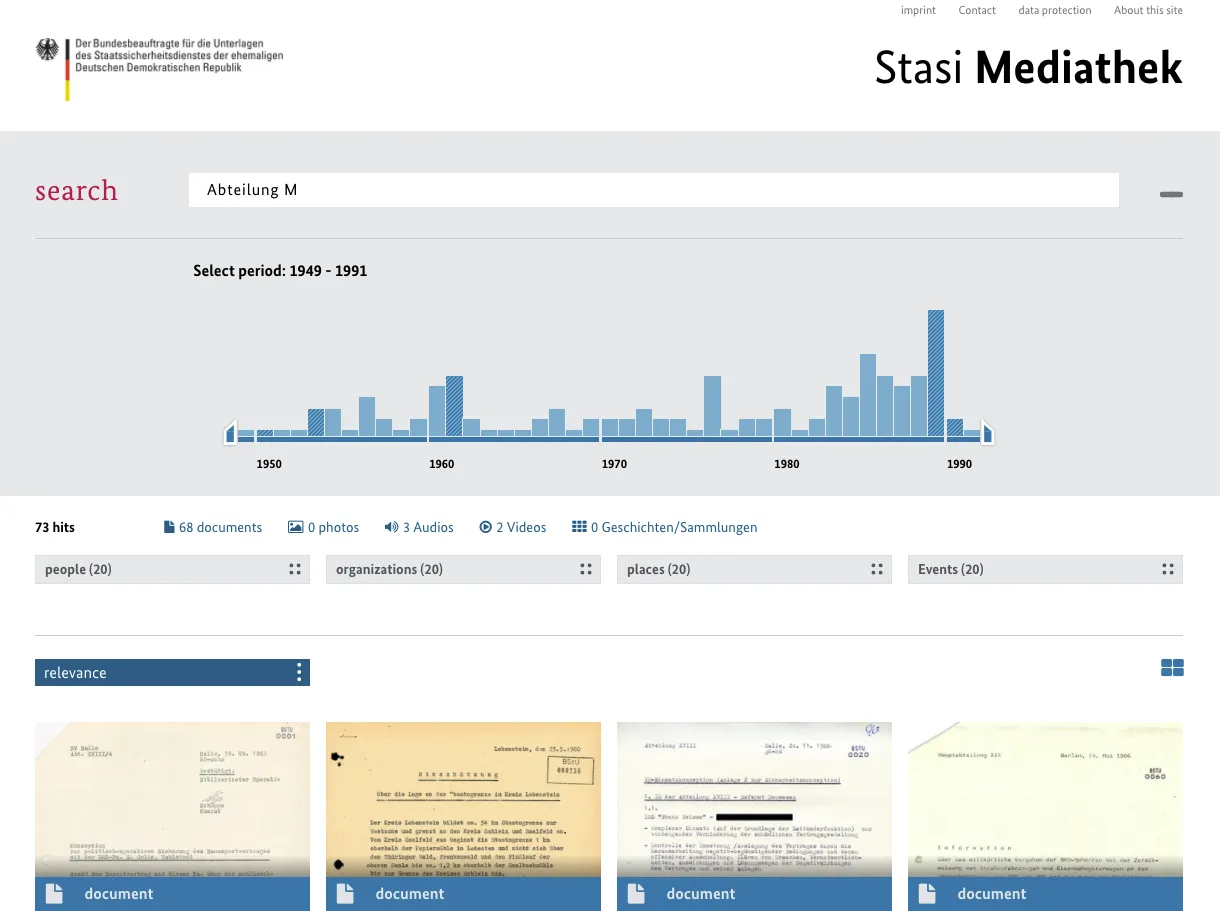
    The Stasi Mediathek website published by the BStU is an amazing resource. One can search for example “Abteilung M” (English: Department M) and find a range of digitized original documents related to the Stasi’s postal surveillance.

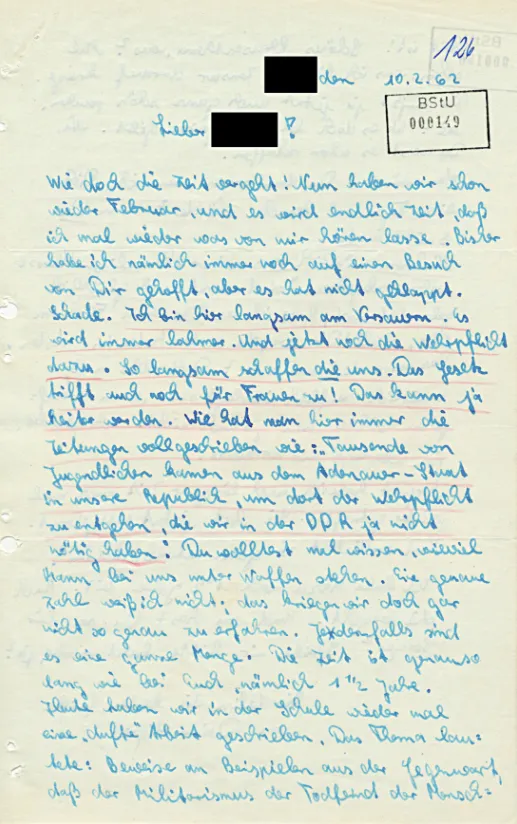
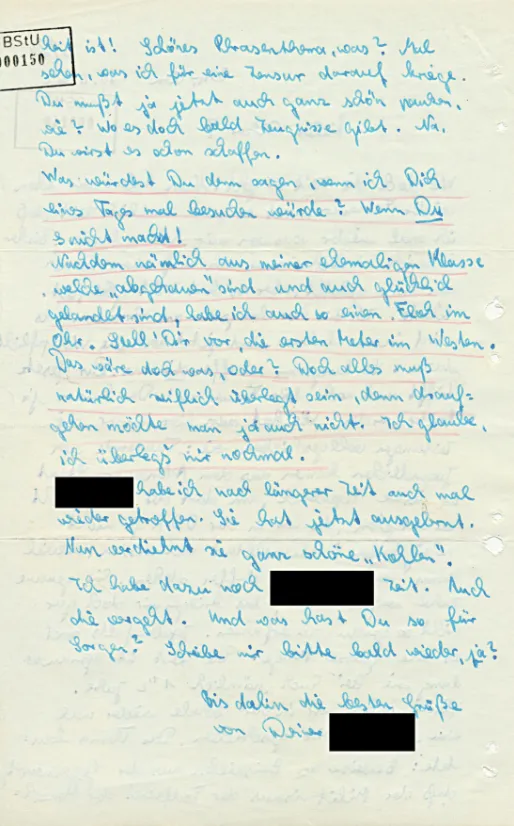
    Stasi / Facebook / Big Data DAAD Day 8 – MfS Department M (A captured letter from the BStU archives)

    This is an example of a letter that the Stasi Department M removed from the Deutsche Post in 1962. In the letter an East German student writes to her friend in the west about her dissatisfaction with the militarism and compulsory conscription in the east and says she is considering fleeing the GDR. Surely the Stasi placed her under a watchful eye due to the information they found through their postal surveillance. It’s also interesting the Stasi one, removed the letter altogether from the postal stream, likely in order to prevent negative sentiments from appearing in western press, and two, kept the document, perhaps as evidence against her at a later date, or potentially also as a result of the thoroughness of the bureaucratic surveillance system they had developed. An English translation can be found at the above link as well. (BStU)

    Stasi / Facebook / Big Data DAAD Day 7 – MfS Department M (Development of working methods)

    In the early years of the Department M, or Division VI as it was known at the time, there was no vocational training so the few dozen employees had to conceive of their own workflows. At that time, the standard set for workers who examined the contents of mail was to read “500 letters per person for each working hour.” Post control took place in special rooms of selected central post offices, where employees of Division VI covertly intercepted and opened mail. The onsite locations helped to ensure the Stasi could accumulate as much intelligence as possible while causing the lowest acceptable delay in the Paketstrom (English: packet stream). (Labrenz-Weiß, 13)

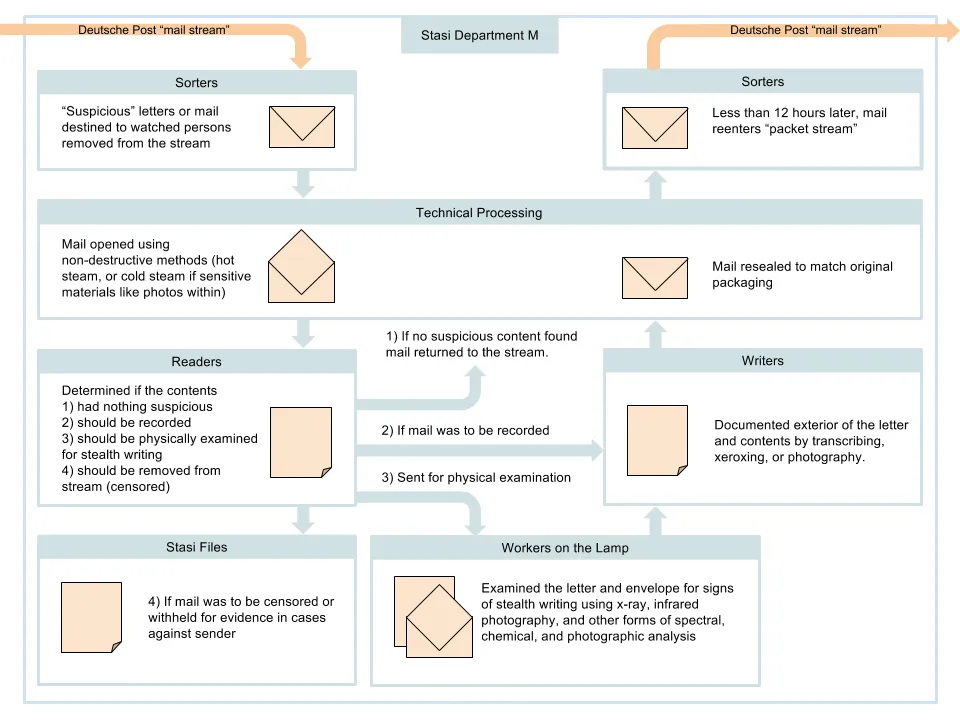
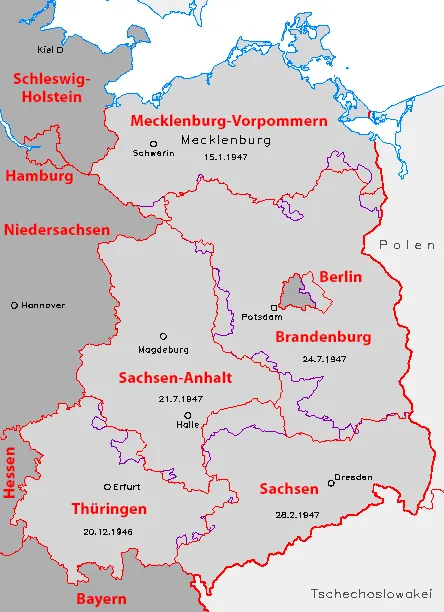
    By 1952 Department M was established and locations for inspection were formalized. The five GDR states (see previous blog post) were divided into 14 districts in order to increase efficiency by moving postal control structurally closer to sender and receiver. Various statutes were established by the MfS allowing for inspection of the post in order to prevent sedition inspired by western influence, as well as to carry out censorship through interception of materials. The process for post control was also more precisely defined and subdivided into specific working groups for: 1) Sorting mail by size; 2) Technical processing; 3) Readers; 4) Writers; and 5) Employees at the lamp.
    Units responsible for “Sorting” the mail passed any letters or parcels that appeared suspicious, as well as all mail destined for persons or organizations under postal control, to “Technical processing” where it was opened using steam or other nondestructive methods. It was then sent to “Readers” who sent letters to the “Writers” once it was determined the contents were worthy of being transcribed. The Writers had the job of recording the documents, preparing reports for each day, and passing information with clues for espionage, sabotage, or, after the addition of the Berlin wall, plans for escape, to relevant departments.
    “The work on the lamp” investigated suspicious consignments in a dark room under a quartz lamp in order to identify clandestine forms of communication like secret writing on the surface of paper, or other methods including invisible ink. If found these documents were then passed to the OTS, or Operational-Technical Sector of the MfS, for special investigation.
    These early divisions of labor served to increase efficiency much in the same way Henry Ford had done at the beginning of the century when he introduced the assembly line. Equally, the divisions helped Stasi employees to become more knowledgeable and specialized in their work, eventually developing machines to augment, improve, and speed up their tasks. (Labrenz-Weiß, 16–17)

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 6 – MfS Department M (postal control selection)

    Stasi Department M workers removed enormous amounts of mail from Deutsche Post each day for inspection. Mail was identified visually based on handwriting, types of letters, or specific addresses. Surveillance of mail was technically illegal in the GDR. Still, mail was withheld on an official basis “in order to prevent attacks” by western intelligence agencies, presumably using “threats and explosives.” This led to the inspection of all incoming and outgoing mail to press agencies, embassies and consulates of NATO countries, and other western correspondence.

    Unofficially, in the interest of multiple surveillance, control and censorship possibilities for the Stasi, everything possible was scrutinized, both foreign and domestic. The postal inspections contributed intelligence on GDR and foreign citizens who were suspected of spying for the west. They allowed the Stasi to filter information the citizens of the GDR were allowed to access, share, or communicate to the outside world. The Stasi intercepted undesirable books, seditious content, and other materials with the ultimate goal of preventing public protests, or other conspiratorial activities. While the goal of Department M was to return the mail collected for inspection back to Deutsche Post within a 12-hour window, many deliveries were seized and never returned. This massive operation naturally resulted in frequent delays in delivery or damage to letters or parcels, which including those that never arrived, led the public to become increasingly aware of the ongoing postal inspection.

    Finally, the postal surveillance provided the Stasi with information about the mood of the population in the GDR, by examining personal communications, as well as messages sent between in companies and institutions. Reports prepared by administrators in Department M on population mood included information on economic and political sentiment and specifically targeted demographic groups (Labrenz-Weiß, 13) across specific geographic locations and social strata in the GDR in order to give the best possible assessment. For example, the following population groups are described in BStU documents

    • Brandenburg: 1,000 workers each at the East coaster and the Brandenburg Steel Works, and 1,000 old and new builders
    • Mecklenburg: 1,000 workers of the shipyards, 500 students and 50 teachers of the University of Rostock, and 1,000 old and new builders
    • Saxony-Anhalt: 1,000 workers of the chemical industry and of Magdeburg heavy machinery construction, 800 students and 100 faculty members of the Martin Luther University Hall, and 1,000 old and new farmers in Altmark
    • Saxony: 1,000 workers of the Stahlwerk Riesa as well as tradesmen / merchants, and 800 students and 100 lecturers from the University of Leipzig
    • Thuringia: 1,000 workers of the Unterwellenborn steelworks, Zeiss works in Jena and tradesmen, and 800 students and 100 professors of the Jena University


    East Germany’s State borders established after WWII 1945-1947 in violet. In red the borders of the new states established during reunification. Source: Wikipedia

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

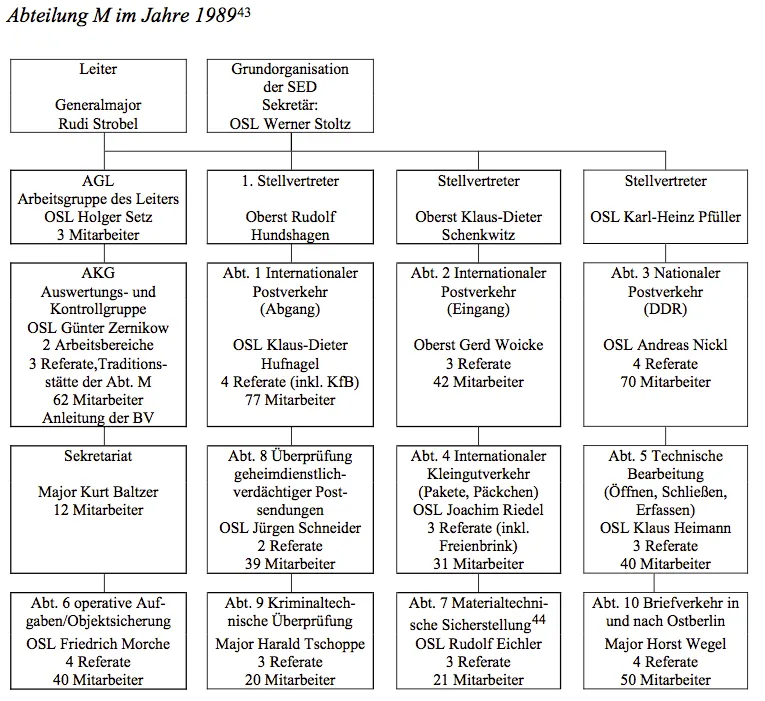
    Stasi / Facebook / Big Data DAAD Day 5 – MfS Department M (Organizational structure overview)

    Stasi / Facebook / Big Data DAAD Day 5 – MfS Department M (Organizational structure overview)

    In 1989 Department M had 10 divisions, which were subdivided into 36 units. The head office, which consisted of 8 divisions and their corresponding units, was located in East Berlin. The divisions were organized based on mail destinations (western, non-communist countries for example), types of mail (like parcels or telegrams), or function within the scope of the work of the Department. Specific units were tasked with selecting mail for examination, while in technical processing units the selected mail was opened, examined, documented, and closed again by their respective units. Other units in Department M were assigned to inspecting customs declarations, maintaining secrecy, or operational engineering, where design, manufacturing, and maintenance of the technology took place. (Labrenz-Weiß, 8–10)

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 4 – MfS Department M (the workers)

    The Stasi surveilled the post of the GDR for nearly 40 years, starting with the founding in 1950, until the fall of 1989 when the Berlin wall fell. The number of workers in Department M rose from a few dozen in the beginning, to nearly 2,200 by the end. The largest office occupied two buildings in the massive Stasi headquarters complex in Berlin-Lichtenburg and included almost 500 employees, with the remaining 1,700 spread across 15 district administration offices. (Polzin, 105)

    While the ratio of women to men in Department M shrank over the years possibly due to the increasing focus on technology and automation, it was consistently at least twice that of the entire MfS. In the beginning 80% of Department M employees were women, compared with 25% in the MfS, while in the 1960s 40% were women compared to 14%. In 1989 only 20% of Department M employees were women. (Labrenz-Weiß, 5)

    Employees were subject to numerous specialized training to prepare them for their work. This included courses on typography, x-ray certification, and photography for those performing inspections. Employees who were integrated with Deutsche Post received information like electronic training for working with telegraph devices, operating postal vehicles, and other knowledge related to the movement of mail and parcels. Those employees charged with the development of specialized equipment for Department M studied engineering, paper technology, air and refrigeration systems, and the mechanics around the movement of postal and newspaper materials. (Labrenz-Weiß, 6)

    While Department M employees were physically embedded in Deutsche Post locations, their activities there were considerably constrained in order to ensure the secrecy of their work. For example, they were required to sit in closed groups in the cafeterias in order to avoid direct contact with actual postal workers. Official contacts were only allowed with Stasi officers already embedded in the post control system special operations.

    1. Arno Polzin, Postal Inspection, Telephone Surveillance and Signal Intelligence in Daniela Münkel (eds.), State Security: A Reader on the GDR Secret Police, Berlin 2016.
    2. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 3 – MfS Department M

    The Ministry for State Security’s Department M was tasked with “postal control”, or the inspection of domestic and international letters and packages. They conducted their work thanks to cooperation with Deutsche Post which, as another state institution concerned with “security of the state,” was subject to the same politics and power infrastructure of the single party system of the DDR (1). Consequently, the Department M had access to every letter and parcel which traveled throughout East Germany by inserting itself in the logistical operations of the postal system. The Stasi reserved special rooms or entire floors within the Deutsche Post buildings, which were off limits to regular post workers.

    In Berlin, Department M had offices in the post office at Nordbahnhof, in the central telegraph office on Oranienburger Strasse and in the railway post office at Ostbahnhof. These rooms used by the MfS were designated “Department 12” of the German Postal Service, both internally and officially.(2)

    1. Arno Polzin, Postal Inspection, Telephone Surveillance and Signal Intelligence in Daniela Münkel (eds.), State Security: A Reader on the GDR Secret Police, Berlin 2016.
    2. Hanna Labrenz-Weiß: Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 2 – The Stasi’s automatic letter opener invention

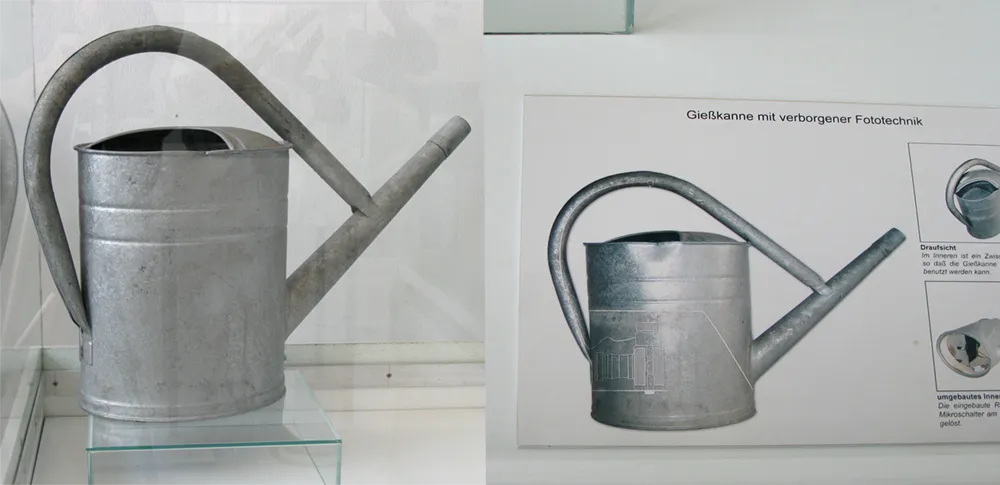
    The former East Germany’s Ministry for State Security (more popularly referred to as the MfS or “Stasi”) is widely known for the inventive and clandestine gadgets that appear in films like Das Leben der Anderen (English: The Lives of Others) or on exhibit at the Stasi Museum in Berlin. Some of my favorites from the museum are the cameras disguised as everyday, boring objects. Take this watering can with a hidden camera.

    Imagine a sweet old Oma in her garden, tipping the can just so, with the intention of spying on the grandma next door. This technologically-enabled interpersonal collection of data of our “friends” was very much like how Facebook operates today. The Stasi used blackmail to infiltrate networks and get people to give up their neighbors, while Facebook coerces us in different ways; for example, through algorithms that implore us to post details from our private lives in order to build up one’s cultural capital and sense of self worth. I’ll explore this connection more in later weeks, particularly in reference to a special type of behind the scenes inventions of the Stasi: a series of machines that automatically opened personal letters and closed and resealed them after their contents were examined.

    In this project, a central question is what do the motivations and methods of this machine, which was used to intercept and automate the secret unpacking and examination of personal information of letters between private citizens, tell us about how the software used by the NSA for monitoring citizens around the globe? Or about the even more secretive methods of Google or Facebook as they examine our personal information in order to influence our behavior? Until tomorrow.

    Stasi / Facebook / Big Data DAAD Day 1 – Willkommen in Deutschland

    This is the first post in a long time. Over the next two months I will add one every day while I’m working on a new stage of an ongoing project I began in Berlin in 2010. I haven’t posted like this in a while. I find it extremely helpful to share and collect research, create an arc for the work, and of course to stay focused. While the project will evolve as I add content to this space, I’ll share the essential bits from my plans here:

    This proposal for a DAAD grant will support research and a series of writings and visualizations that examine how the technological inventions of the East German Ministry for State Security preempt Facebook, the NSA, and the world of Big Data. I will work at Humboldt University and the Stasi Records Agency (BStU) in Berlin and the Museum at the Round Corner in Leipzig, researching and documenting the schematics and actual machines developed by the Stasi for surveillance. With this knowledge I will frame an investigation that uses the analog devices of the Stasi to lend insight into the methods implemented today as software by social media, advertising groups, and intelligence agencies in the service of domestic surveillance and censorship.
    I feel super fortunate to be able to continue this project I started almost seven years ago thanks to support from the German Academic Exchange Service or DAAD (German: Deutscher Akademischer Austauschdienst) and Prof. Dr. Wolfgang Ernst at the Institute of Musicology and Media Studies at Humboldt University Berlin.
    Stasi / Facebook / Big Data DAAD Day 1 – Willkommen in Deutschland

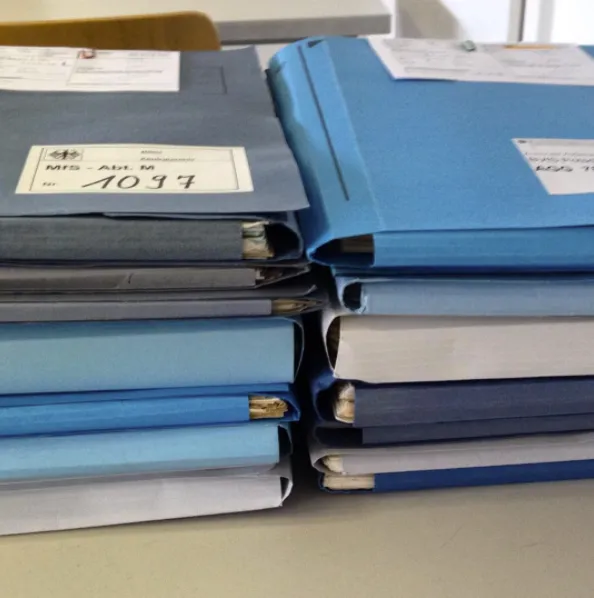
    Stasi files at the BStU. These are not the personal files the Stasi collected, but notes, diagrams, and parts lists detailing the inventions and processes developed during the Stasi’s almost 40 year reign.

    Free Market Privacy

    On March 18, 2016 I was invited to speak at the Austrian Federal Chancellery on the state of data privacy laws and culture in the U.S. I then took part in a panel discussion with, among other participants, Mr. Max Schrems from Europe v. Facebook.

    In addition how laws differed from those in the E.U. I also shared my Fulbright research, including a new concept I’ve been working on called “Free Market Privacy,” where data security is only provided to users only because it benefits the companies holding their data. Instead of a basic human right enshrined by the constitution, privacy is a byproduct of capitalist pursuits.

    Free Market Privacy

    Free Market Privacy

    English translation:

    Invitation to the event on the occasion of the 10th European Data Protection Day

    Transatlantic traffic after the Safe Harbour decision of the ECJ
    Friday, March 18 2016
    Federal Chancellery, congress hall, Ballhausplatz 2, 1010 Wien

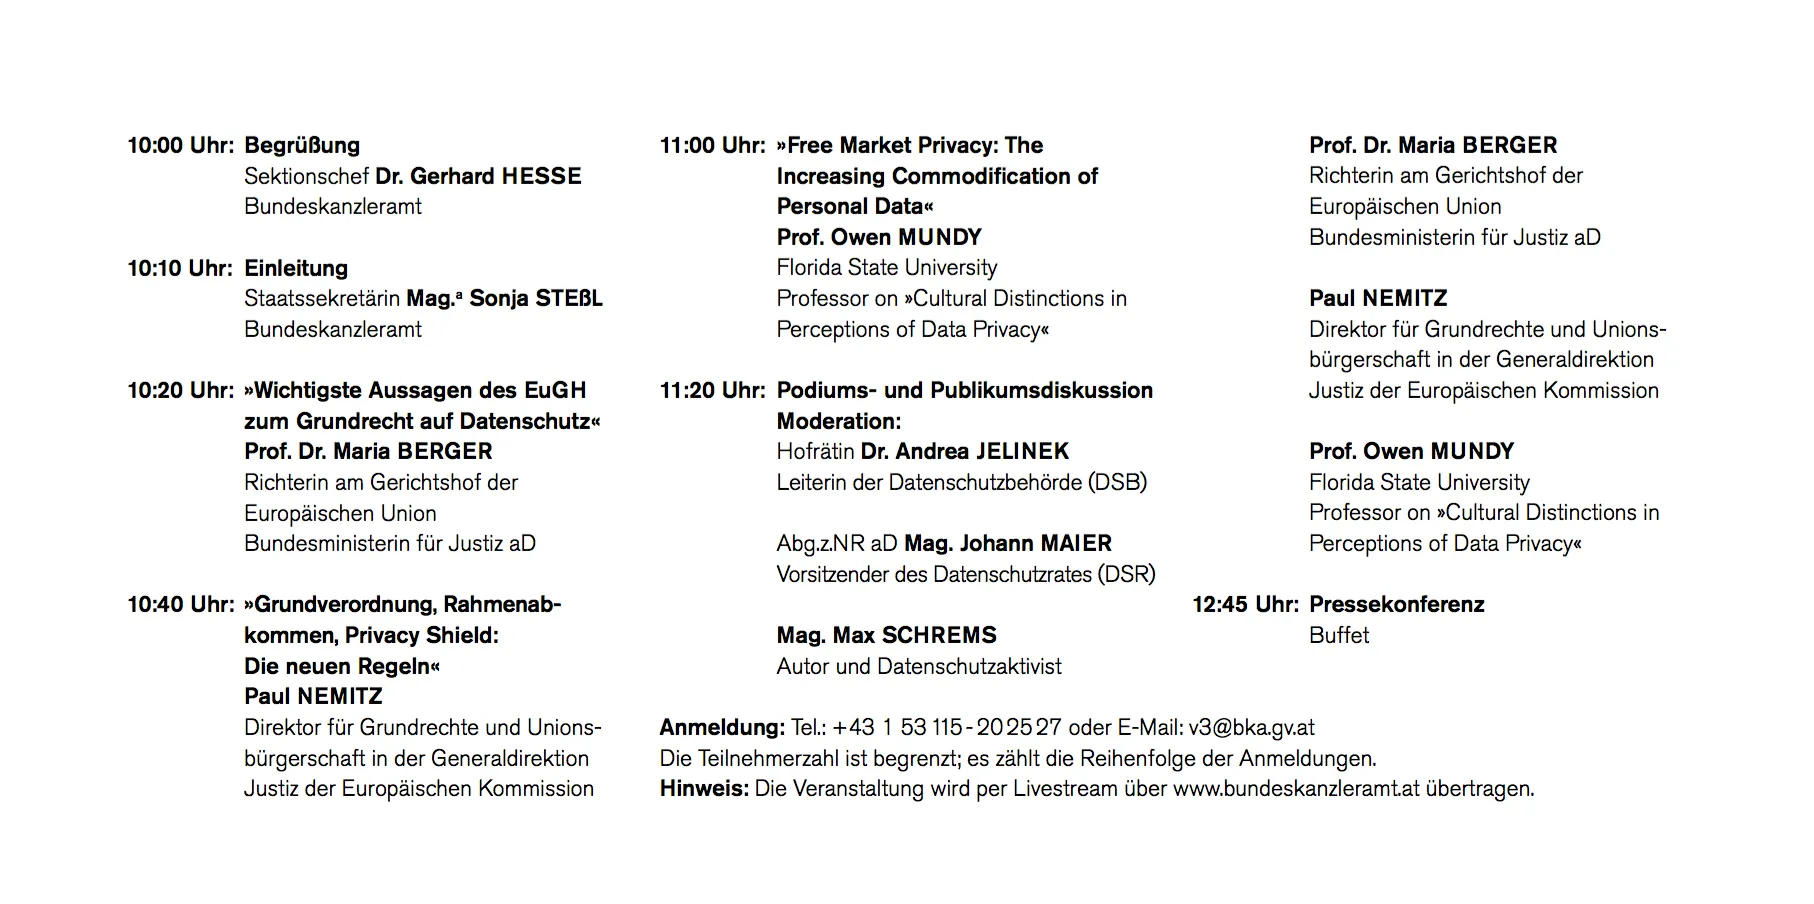
    10:00 Welcome
    Section Chief Dr. Gerhard HESSE, Federal Chancellery

    10:10: Introduction
    State Secretary Mag Sonja Stessl, Federal Chancellery

    10:20: “The most important statements of the ECJ on fundamental right to data”
    Prof. Dr. Maria BERGER, Judge at the Court of the European Union Federal Minister of Justice aD

    10:40: “basic Regulation, Framework Agreement, Privacy Shield: The new rules”
    Paul NEMITZ, Director for Fundamental Rights and Citizenship in the Directorate General for Justice of the European Commission

    11:00: “Free Market Privacy: The Increasing Commodification of Personal Data”
    Prof. Owen MUNDY, Florida State University
    Professor on “Cultural Distinctions in Perceptions of Data Privacy”

    11:20: Panel and audience discussion Moderator:

    Councillor Dr. Andrea JELINEK
    Head of the Data Protection Authority (DPA)

    Abg.z.NR aD Mag. Johann MAIER
    Chairman of the Data Protection Council (DSR)

    Mag. Max SCHREMS
    Author and privacy activist

    Prof. Dr. Maria BERGER
    Judge at the Court of the European Union Federal Minister of Justice aD

    Paul NEMITZ
    Director for Fundamental Rights and Citizenship in the Directorate General for Justice of the European Commission

    Prof. Owen MUNDY
    Florida State University
    Professor on “Cultural Distinctions in Perceptions of Data Privacy”

    12:45: Press conference

    Registration: Tel .: +43 1 53115-20 25 27 or email: v3@bka.gv.at
    The number of participants is limited; it counts the order of registration.
    Note: The event will be broadcast via live stream on www.bundeskanzleramt.at.

    Beautiful Data II @ Metalab at Harvard University

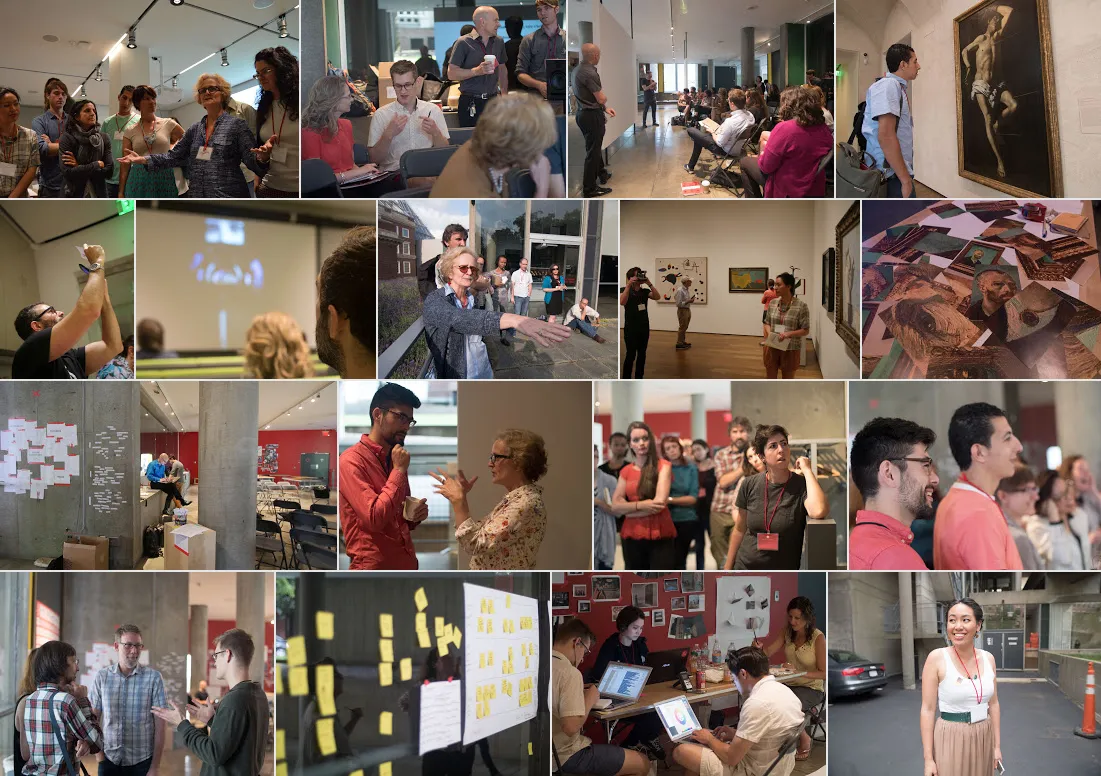
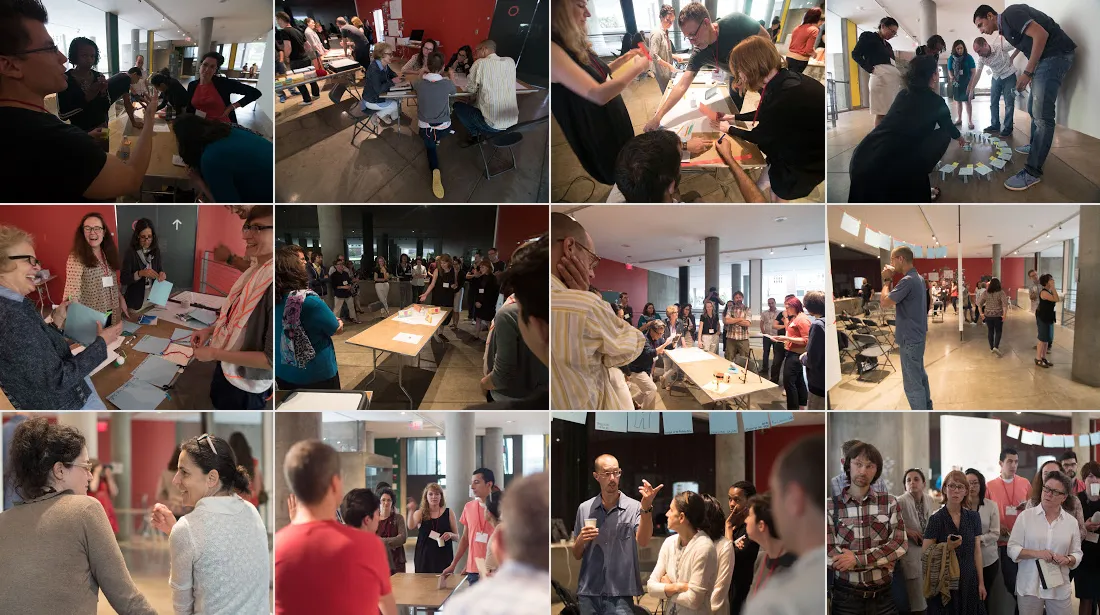
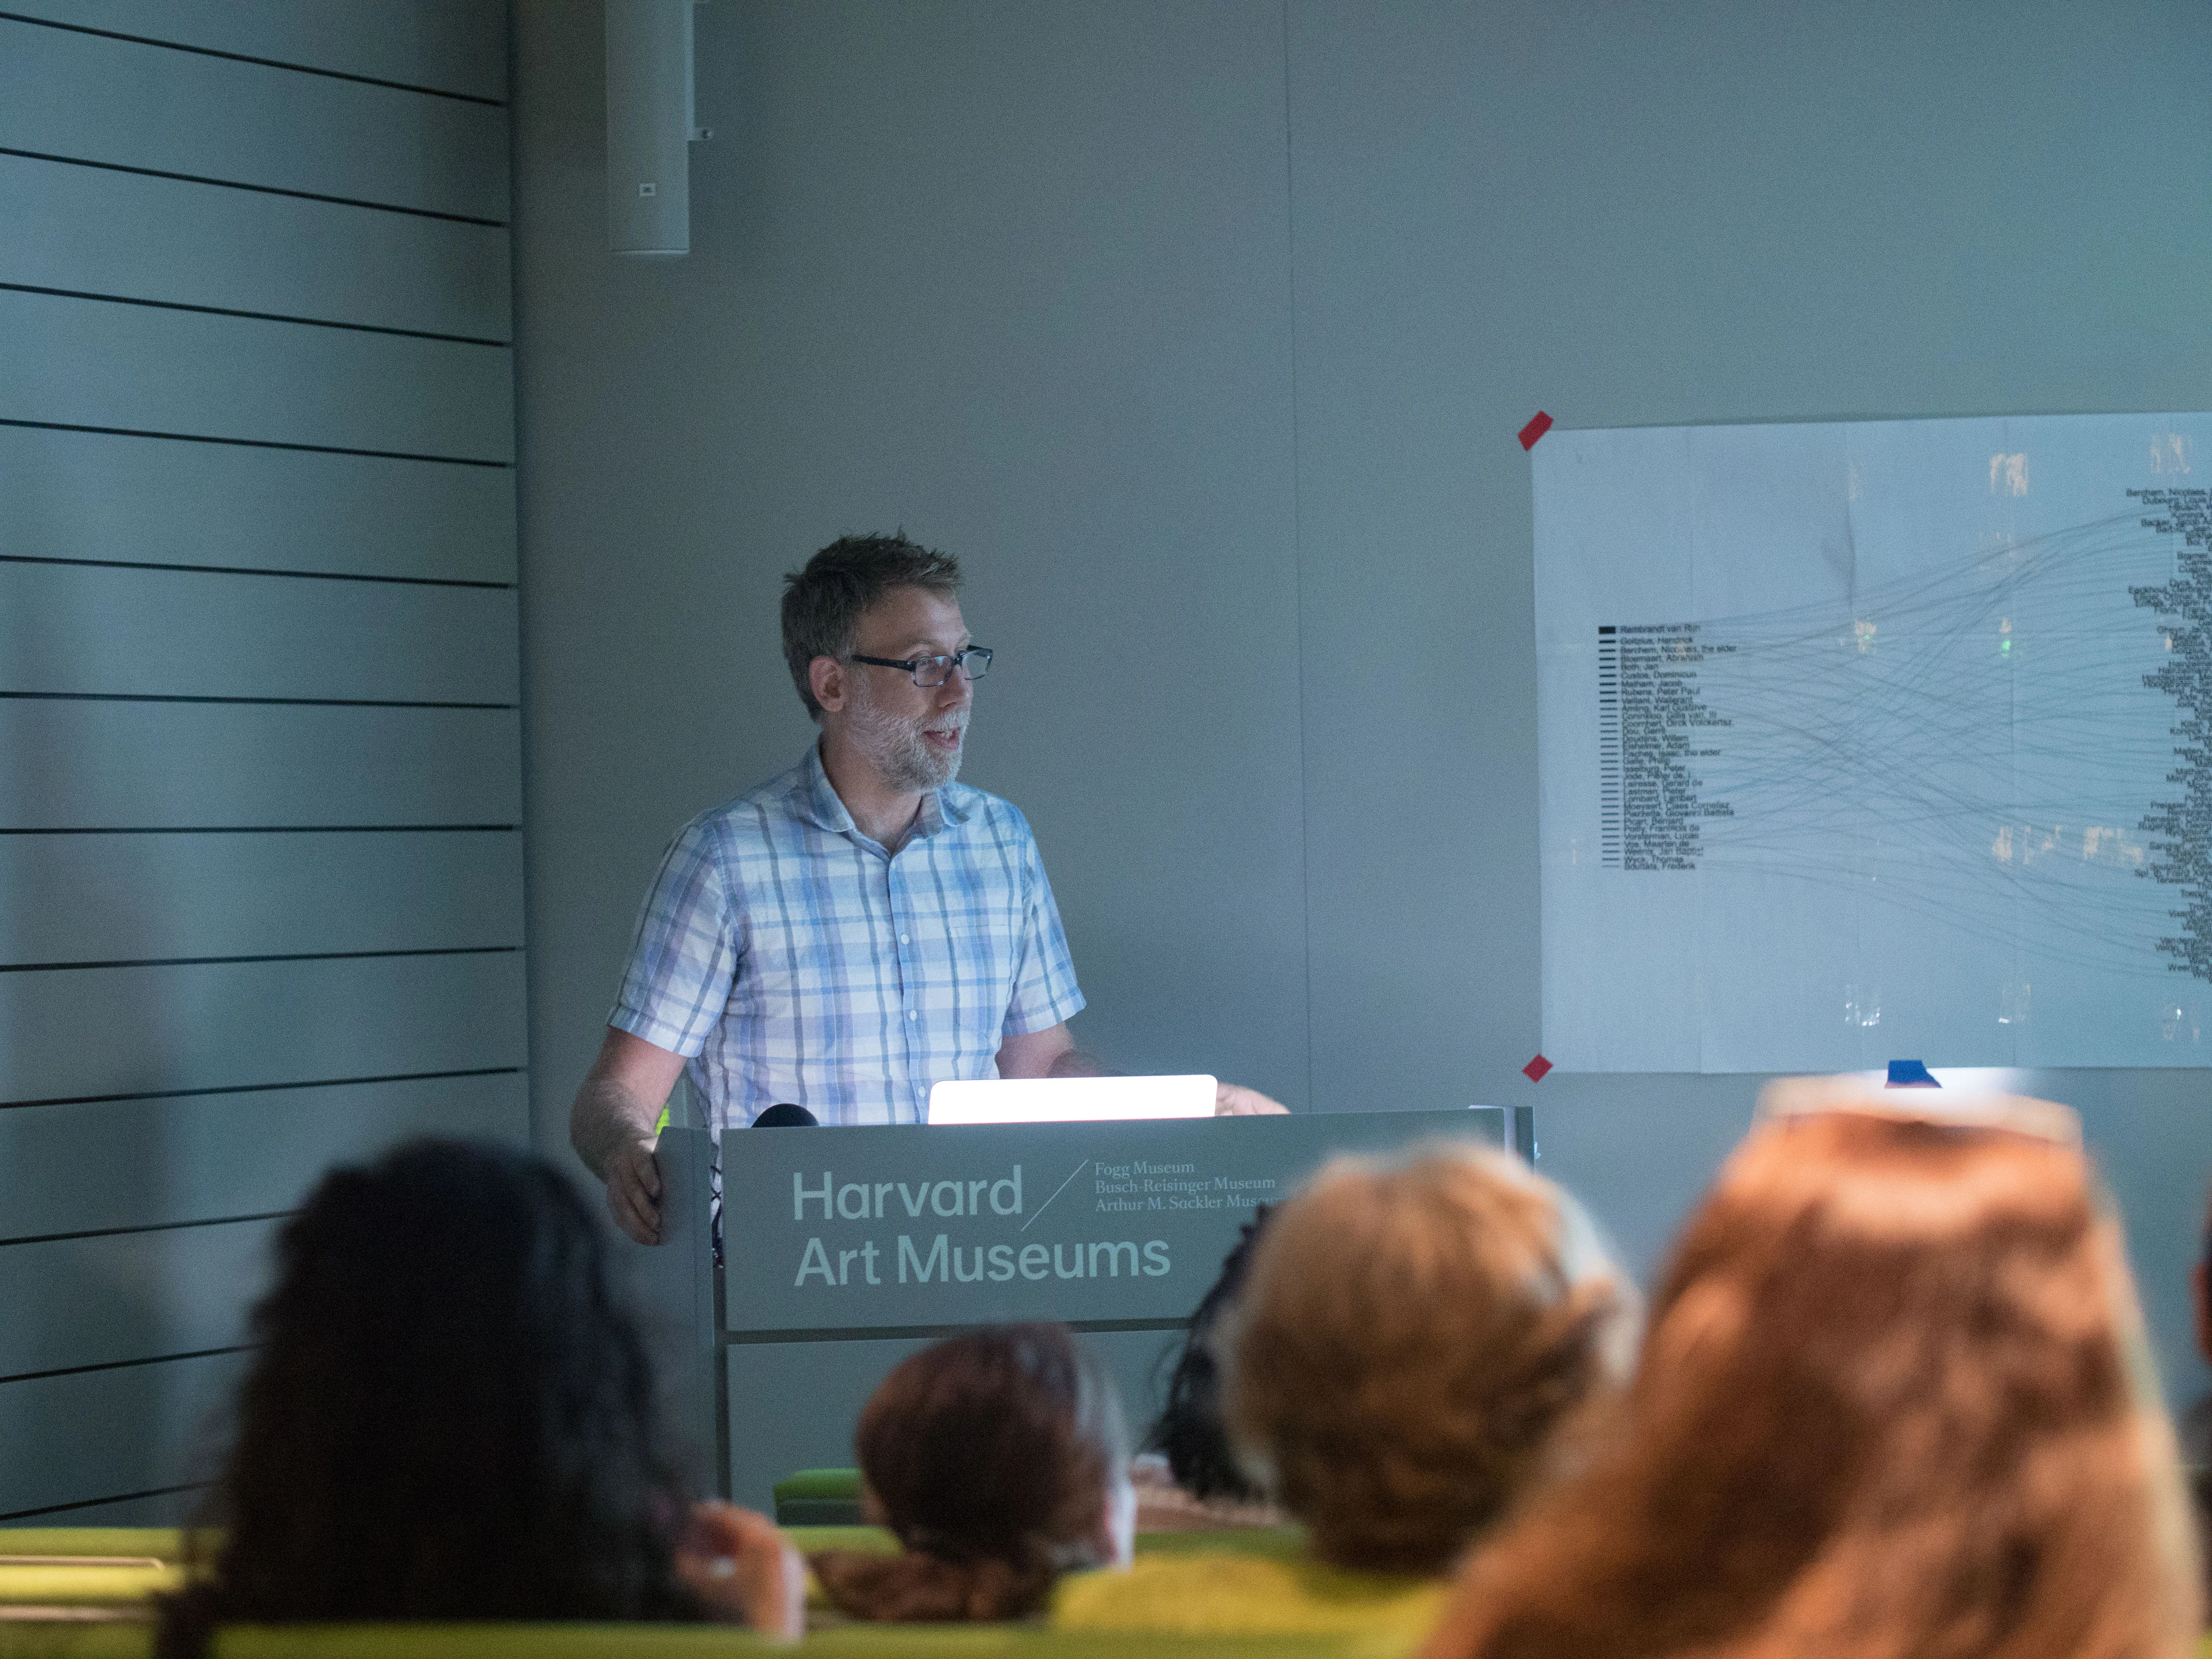
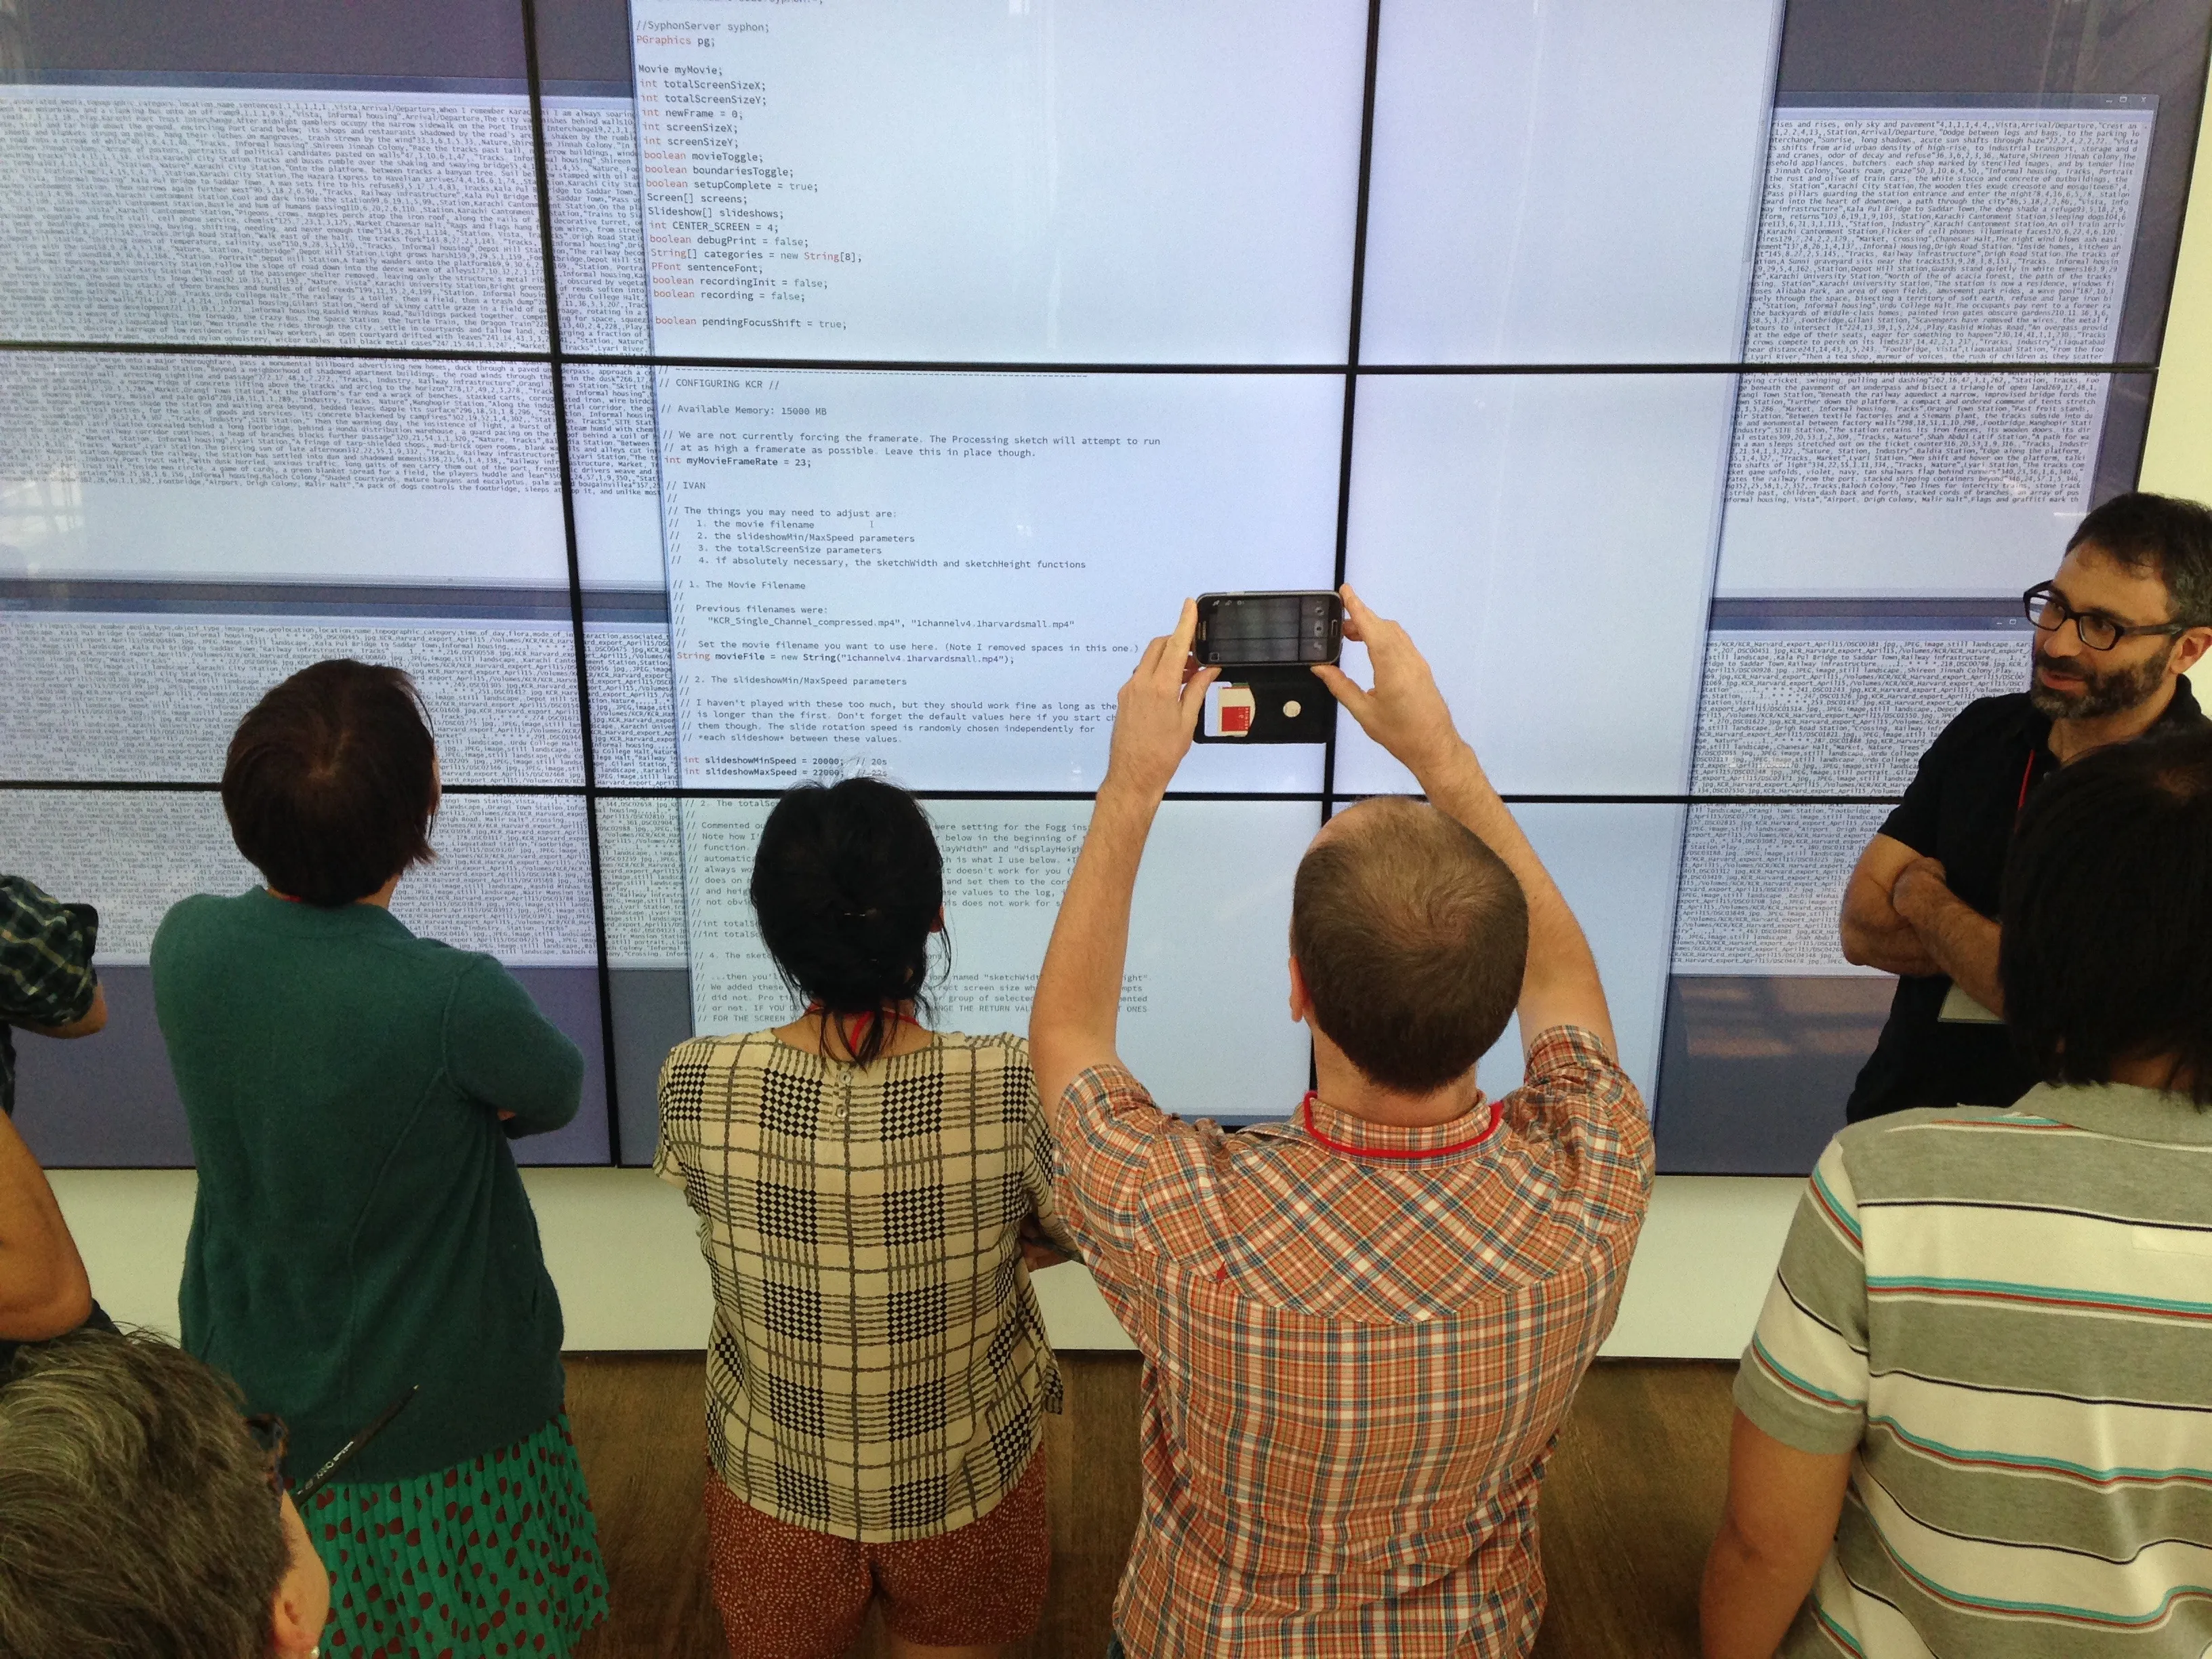
    This month found me at the excellent Beautiful Data II workshop at the MetaLab at Harvard University sponsored by the Getty Foundation. Participants worked together in the Carpenter Center and Harvard Art Museum under the theme “Telling Stories About Art with Open Collections.”

    Beautiful Data II @ Metalab at Harvard University

    There were presentations by known visualization and museums experts, breakout sessions exploring how to represent problem data and collections, and talks by participants and Metalab staff and fellows, including a wonderful group of artists, curators, designers, and scholars in attendance.

    Beautiful Data II @ Metalab at Harvard University

    Here are a few of the many highlights starting with this nerdy shot of me…

    P1030056

    P1000822


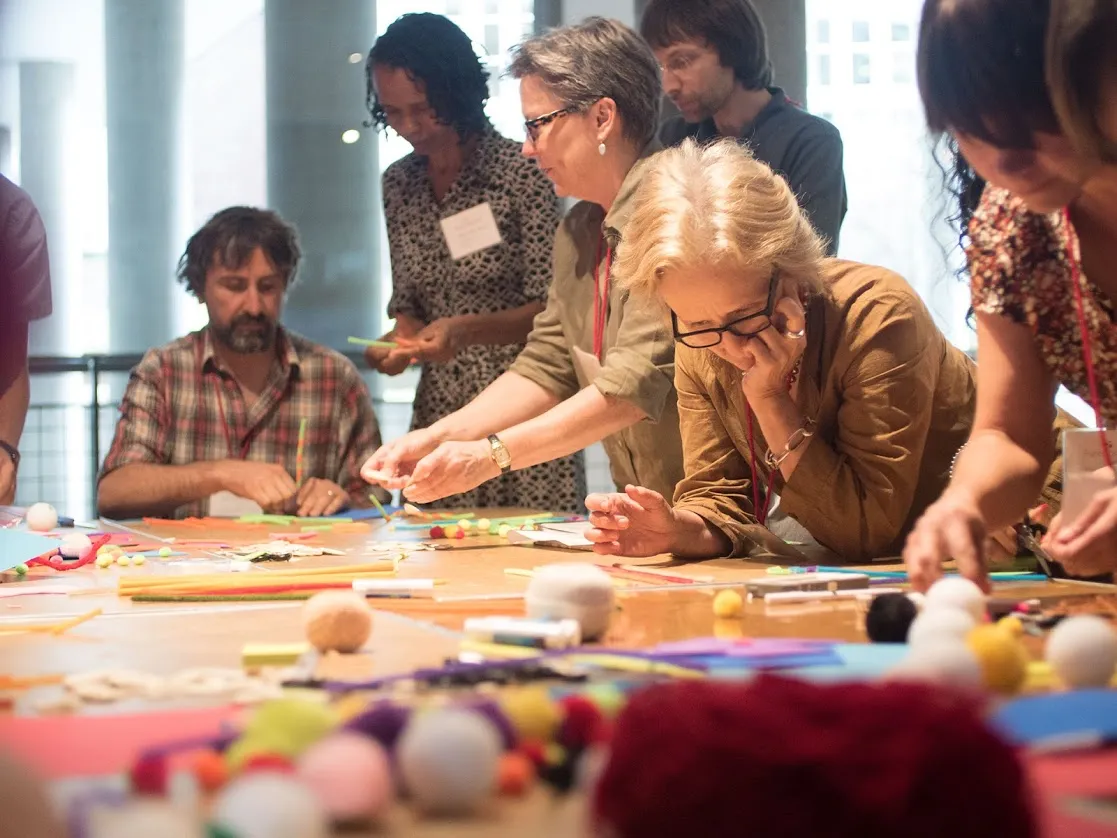
    Data Therapy workshop with Rahul Bhargava (slides1, slides2).

    Beautiful Data II @ Metalab at Harvard University


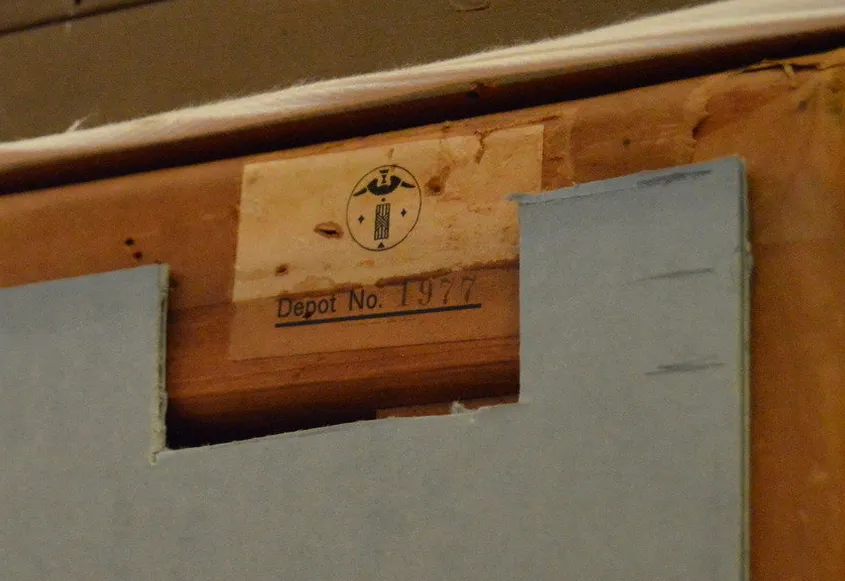
    Learning about provenance at the Harvard Art Museum (note stamp declaring Nazi property)

    This spanking cat statuette from the Cooper Hewitt collection.
    Colour Lens produced at Beautiful Data I.
    Presentation by Seb Chan Director of Digital at Cooper Hewitt.
    Memory Slam by Nick Montfort.
    Meow Met Chrome extension shows cats from the Met Museum in new tabs.

    IMG_3966


    Behind the scenes of Ivan Sigal‘s Karachi Circular Railway, Harvard Art Museum Lightbox.

    The Life and Death of Data by Yanni Loukissas.
    Ben Rubin discussing his and works by Mario Klingemann, Ryoji Ikeda, Jer Thorp and others.
    William James Twitter Bot by Rachel Boyce.


    Cold Storage documentary by Jeffrey Schnapp, Cristoforo Magliozzi, Matthew Battles, et al.

    Cooper Hewitt Font Specimen
    Cooper Hewitt typeface by Chester Jenkins


    “Unicode” by Jörg Piringer shows all 49571 displayable characters in the unicode range.

    *Most photos by Metalab staff

    Term vs. Term for Digital Public Library of America hackathon

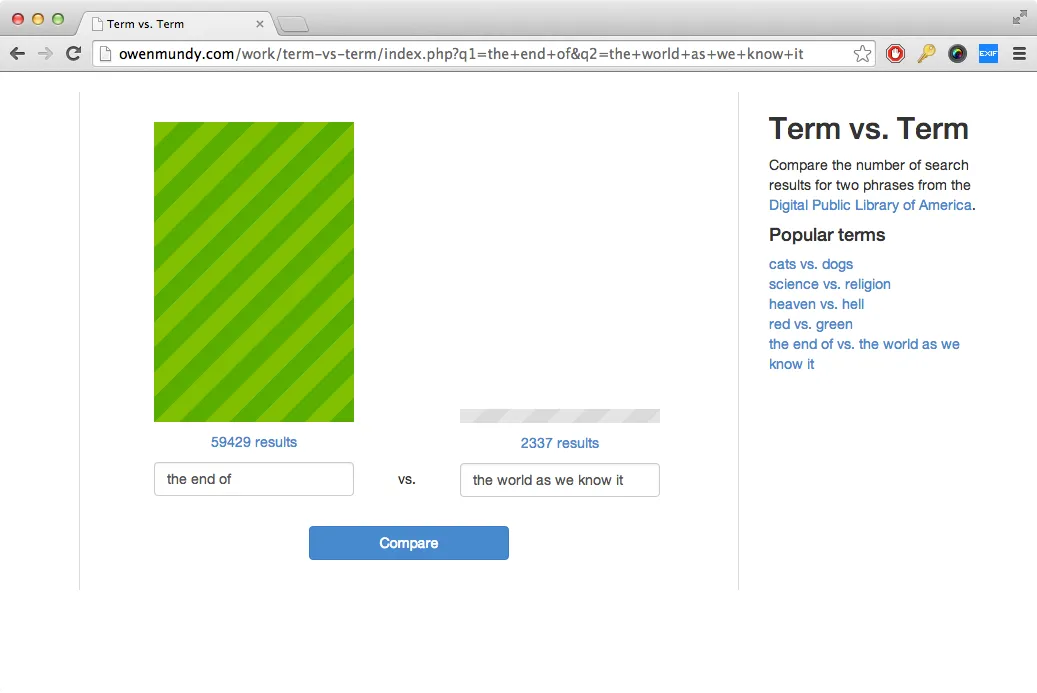
    I made a small app to compare the number of search results for two phrases from the Digital Public Library of America for a hackathon / workshop here at Florida State next week.

    http://owenmundy.com/work/term-vs-term

    dpla term vs term

    Digital Humanities Hackathon II – Digital Public Library of America

    Monday, April 21, 2:00-3:30 p.m.
    Strozier Library, Scholars Commons Instructional Classroom [MAP]

    The Digital Scholars Reading and Discussion Group will simulate its second “hackathon” on April 21, allowing participants to learn more about the back-end structure of the Digital Public Library of America. With its April 2013 launch, the DPLA became the first all-digital library that aggregates metadata from collections across the country, making them available from a single point of access. The DPLA describes itself as a freely available, web-based platform for digitized cultural heritage projects as well as a portal that connects students, teachers, scholars, and the public to library resources occurring on other platforms.

    From a critical point of view, the DPLA simultaneously relies on and disrupts the principles of location and containment, making its infrastructure somewhat interesting to observe.

    In this session, we will visit the DPLA’s Application Programming Interface (API) codex to observe some of the standards that contributed to its construction. We will consider how APIs function, how and why to use them, and who might access their metadata and for what purposes. For those completely unfamiliar with APIs, this session will serve as a useful introduction, as well as a demonstration of why a digital library might also want to serve as an online portal. For those more familiar with APIs, this session will serve as an opportunity to try on different tasks using the metadata that the DPLA aggregates from collections across the country.

    At this particular session, we are pleased to be joined by Owen Mundy from FSU Department of Art and Richard Urban from FSU College of Communication and Information, who have considered different aspects of working with APIs for projects such as the DPLA, including visualization and graphics scripting, and developing collections dashboards.

    As before, the session is designed with a low barrier of entry in mind, so participants should not worry if they do not have programming expertise or are still learning the vocabulary associated with open-source projects. We come together to learn together, and all levels of skill are accommodated, as are all attitudes and leanings.

    Participants are encouraged to explore the Digital Public Library of America site prior to our meeting and to familiarize themselves with the history of the project. Laptops will be available for checkout, but attendees are encouraged to bring their own.

    “The Earth Observation Guide” – Post Media Lab notes

    I’m back from Lüneberg, Germany and already missing the simplicity of traveling by train as well as the pleasure of fine wurst. However I had an engaging few days at the Post Media Lab’s Taking Care of Things!. The event began with a keynote by Kelly Dobson from RISD, followed by a tour of Stadtarchive the next morning. Then we broke off into groups to address various topics around archives, art, media, and politics.

    I worked in the Measure Drones group with colleagues, Kristian Lukic, Moritz Queisner, Boaz Levin, Daniel Herleth, Adam Kaplan, Frédéric Eyl, and Oliver Lerone Schultz (one of the coordinators of Taking Care of Things along with Christina Kral). Together, over the course of two days, we worked together to conceive, research, write, illustrate, and design a booklet called “The Earth Observation Guide.” This is not a history of art about drones, nor does it try to tackle the whole subject. Rather it is more akin to a time capsule that preserves a moment in time before drones are widespread. It acts as a guidebook, recording what is known about their past and present, illustrating shifts and concerns, and addressing how humans might understand their future. Here are some images of the presented work on the third day:

    IMG_5074

    IMG_140115_PML+HoL+CDC_Taking-Care-of-Things_Stadtarchiv-Lueneburg_0434-XL

    IMG_5070

    IMG_140115_PML+HoL+CDC_Taking-Care-of-Things_Stadtarchiv-Lueneburg_0596-XL

    I also somehow managed to get my mug in the newspaper in Lüneberg. I think it says “American professor launching spy drones in Germany” or some such thing.

    IMG_5062

    The group examining 16th century drawings of salt mines from the archive.

    IMG_5058

    After Douglas Davis – The World’s First Collaborative Sentence

    After Douglas Davis – The World’s First Collaborative Sentence

    README for After Douglas Davis
    ==============================

    Statement
    ————–

    The World’s First Collaborative Sentence was created by Douglas Davis in 1994 and donated to the Whitney Museum of American Art in 1995. Much like today’s blog environments and methods for crowdsourcing knowledge, it allowed users to contribute practically any text or markup to a never-ending sentence with no limits on speech or length.

    At some point the sentence stopped functioning, and in early 2012 the Whitney Museum undertook a “preservation effort” to repair and relaunch the project. Measures were taken during the “restoration” to stay true to the original intent of the artist, leaving dead links and the original code in place.

    During the preservation the curators placed small sections of garbled ASCII text from the project on Github with the hope that others would “fork” the data and repair the original. However, the Whitney Museum did not succeed in realizing that the collaborative culture of the net Davis predicted has actually arrived. This is evident not only through sites like Wikipedia, Facebook, and Tumblr, but the open source movement, which brings us Linux, Apache, and PHP, the very technologies used to view this page, as well as others like Firefox, Arduino, Processing, and many more.

    In the spirit of open source software and artists like Duchamp, Levine, runme.org and Mandiberg, on September 5, 2013, I “forked” Douglas Davis’ Collaborative Sentence by downloading all pages and constructing from scratch the functional code which drives the project. I have now placed this work on Github with the following changes:

    1. All pages are updated to HTML5 and UTF-8 character encoding
    2. The functional code was rewritten from scratch including a script to remove malicious code
    3. The addition of this statement

    I was originally disappointed the Whitney Museum didn’t place the full source code in the public domain. What better way to make it possible for artists and programmers to extend the life of Davis’ project by learning from, reusing, and improving the original code than to open source this work? Though, possibly like Davis, my motivation is largely in part an interest in constructing a space for dialog, framing distinct questions and new possibilities, and waiting to see what happens from this gesture.

    Included software
    ————–
    HTML Purifier http://htmlpurifier.org/

    Live version
    ————–
    Enter After Douglas Davis

    About the author
    ————–
    Owen Mundy http://owenmundy.com/

    Give Me My Data visualizations / tutorials

    I received two separate emails recently sharing images and sample code for visualization projects produced with the help of Give Me My Data. I’m happy to share them both here:

    Give Me My Data

    Alex Hornbake posted a visualization mapping Facebook friend locations and connections in D3. You can view it here and there’s a Gist with all the code here. His image shows where his connections are located, or have move to or from. As abstract and beautiful as the image is, one can still make out a rough outline of the United States and even guess at specific cities like Atlanta, New York, Miami, and Los Angeles.

    Rik Van Bruggen, of Neo Technology, used the “mutual friends graph” to create an interactive neo4j graph database. Following is more information from the tutorial he produced.

    Ever since Facebook promoted its “graph search” methodology, lots of people in our industry have been waking up to the fact that graphs are über-cool. Thanks to the powerful query possibilities, people like Facebook, Twitter, LinkedIn, and let us not forget, Google have been providing us with some of the most amazing technologies. Specifically, the power of the “social network” is tempting many people to get their feet wet, and to start using graph technology. And they should: graphs are fantastic at storing, querying and exploiting social structures, stored in a graph database.

    The first step to take was to get access to my own facebook data. Obviously there is the facebook graph api, but I hope that by now you would realise that is just not my cup of tea. Sounded to exhausting :) … So: I found myself a little tool that would allow me to download the data from facebook, in a workable format. Give me my data provides a number of different export options, but I chose the “Mutual Friends Network Graph – as it would give me most info with regards to my actual social network.

    png;base64ad8e402bc7ee51e

    Facebook’s God complex: No data for the “wicked”

    I was quoted recently in a TechCrunch article about the ongoing battle between Google and Facebook to draw users to their respective social networking services. In the article, The Only Backdoor Left To Sneak Your Facebook Friends Into Google+ Is Yahoo, Erick Schonfeld writes:

    ‘Over the weekend, Facebook blocked a Google Chrome extension called the Facebook Friend Exporter. And in fact, Facebook changed its OAuth 2.0 API in such a way that it “suddenly removed email addresses from the queries without warning,” says Owen Mundy, creator of Give Me My Data. Other data can still be exported, just not your friends’ email addresses.’ [1]

    I wanted to clarify something about the above because my contribution is slightly vague. I also wanted to elaborate for other developers and people interested in how to get their data, specifically the email addresses *out* of Facebook.

    Getting your data our of Facebook is a hot issue right now with the emergence of Google+. It’s important to be able to preserve your data, especially in the event you want to exit Facebook, or prepare for its possible demise. I think most people don’t care which social networking software they use, as long as they can stay in touch with their friends. Many depend on Facebook to keep their friends’ contact information up to date. Their friends’ phone numbers, emails, and physical addresses may have changed, but they can still be found on Facebook.

    This is one great benefit of Facebook, but I think they’ve come to take a higher-than-thou approach to user data. For example, if I use a single software on my computer to manage contact data for my friends, send them messages with pictures, etc., I am not locked-into a contract with the machine nor the software. I physically have the device that stores this data in my possession, and therefore can do whatever I like with it—assuming I can wrangle my data out of it.

    Picture 31

    One of the great benefits of the cloud is access, right? Wrong. Facebook has a god’s eye view regarding the matter of our data. The view from on high is that they can do whatever benefits Facebook, not necessarily the user. So they continue profiting from our activity while protecting it’s evidence from any company/person/software which could compromise their lead in social networking. Unfortunately this includes us, so we are ultimately at their mercy.

    But Facebook is not a merciless God. They don’t charge to use their service or store my data. This is the tradeoff. We sacrifice privacy—our right to not be tracked, advertised to, or sniffed by governments—in order to play games, have stupid political debates, and post pictures of our kids. So, they have the right to allow or prevent access to this information, regardless of whether it is right.

    Regarding getting email addresses of your contacts, as far as I know, there are three ways to mass export your friends’ contact data, only one of which is currently allowed by Facebook.

    Hacking

    The Facebook Friend Exporter, created by Mohamed Mansour, is a browser extension that works independent of the Facebook API. It scrapes your friends’ contact data from the Facebook pages you visit and exports them as CSV. First, Facebook’s rules here for reusing this type of data are not exactly clear. While they don’t explicitly ban saving the contact info of your friends, the have a catch-all statement that tries to set guidelines for doing so. One could argue by accepting your friend request a user has already consented to sharing with you.

    “If you collect information from users, you will: obtain their consent, make it clear you (and not Facebook) are the one collecting their information, and post a privacy policy explaining what information you collect and how you will use it.” [2]

    One thing that is clear is the method the Facebook Friend Exporter extension uses is banned according to Facebook’s Statement of Rights and Responsibilities:

    “You will not collect users’ content or information, or otherwise access Facebook, using automated means (such as harvesting bots, robots, spiders, or scrapers) without our permission.” [2]

    And as expected, Facebook has taken measures to prevent Mansour’s app from working.

    “Mansour says that Facebook removed emails from their mobile site, which were critical to the original design of his extension. He told me that the company had implemented a throttling mechanism: if you visit any friend page five times in a short period of time, the email field is removed.” [3]

    This is not the first time Facebook has referenced their Statement of Rights and Responsibilities to take measures to keep user data from hackers, artists, or competitors. In 2010 they served moddr and other makers of the Web 2.0 Suicide Machine with a cease and desist letter to prevent them from providing a service for Facebook users to delete their accounts. The letter, which claimed the project was guilty of “Soliciting users’ Facebook login information; Accessing a Facebook account belonging to someone else; Collecting Facebook users’ content or information using automated means such as scripts or scrapers without Facebook’s permission” was possibly effective. Currently only users of MySpace, LinkedIn and Twitter can commit “virtual suicide.”

    face2facebook_diagram

    The Face to Facebook (see image on left) project by Paolo Cirio and Alessandro Ludovico stole one-million Facebook profiles, filtered them with face-recognition software, and then posted them on a fake dating website sorted by facial characteristics. From a statement by the makers:

    “Everybody can steal personal data and re-contextualize it in a completely unexpected context. And that shows, once more, how fragile and potentially manipulable the online environment actually is.”

    I agree, and I like the project. But in a public work such as this it’s hard to argue, in my opinion, that this project will help the average web user. While many may reconsider the type of information they post, more than likely they will think this project is another example of the “bad guys” (a.k.a. hackers) doing bad things. While it critiques, in a very amusing and relevant way, the issue of online privacy, it leaves the user feeling violated, not necessarily thoughtful. As a work of protest it encounters the same problem that holding a giant sign in someone’s face that says “go to hell”—It makes it hard for the other person to see your perspective when you do that.

    While I appreciated the fun jab and reference to FaceMash, Facebook did not see the humor in the project. The creators received cease and desist letters and were threatened with multiple lawsuits from Facebook’s lawyers. And in a final spiteful measure, Facebook deleted their profiles [4]. Apparently the rule is, what happens on Facebook, stays on Facebook.

    Using the API

    While I was sure that in the past my app, Give Me My Data, was able to retrieve a user’s friend’s email address, when I tested it after the Facebook Friend Exporter news broke I found no emails. Looking around the web I can’t find any evidence that Facebook ever allowed this data to be accessed. While you can still export all other data from your Facebook profile using Give Me My Data, this tiny and important string of characters with an ‘@’ is one essential component Facebook won’t allow. Likely, the policy was spurred by spam prevention, but given the above, it has the added bonus of blocking an exodus of users from Facebook.

    In any case when you run the following FQL (Facebook Query Language) against their API it doesn’t error. This means the field exists, but they have written a custom script to remove it from the results.

    SELECT first_name, middle_name, last_name, email
    FROM user
    WHERE uid IN (SELECT uid2 FROM friend WHERE uid1 = me())

    Becoming a Preferred Developer

    In the article above, Schonfeld also explains how users can access their Facebook friend’s contact info by first importing it into a Yahoo! account and then exporting a CSV which can be imported into Google+ (or anything for that matter). I believe that Yahoo! belongs to the Facebook Preferred Developer Consultant Program which gives them access above and beyond regular developers:

    “Facebook provides PDCs with increased access to its employees and training. PDCs are expected to abide by program expectations around policy compliance, integration quality, and high-level cooperation with Facebook.” [6]

    Whatever kind of cooperation it is that Facebook is giving these preferred developers, one can be sure it includes access to data Facebook considers sensitive, like email addresses. While Yahoo! is not listed as a preferred developer on the Facebook page above, they have access to the emails so they clearly have some kind of arrangement.

    Google, on the other hand, most definitely does not. This is not the first time Google and Facebook have gotten into a scuffle over sharing (or lack of) data. Late in 2010 Google stated they would no longer allow Facebook and other services access to their users’ data unless Facebook or the other service allowed data to be accessed by Google. [7]

    In closing, we already know everyone wants our data. All the clicks, likes, comments, photos, and video we incur or upload are tracked, analyzed, and ultimately compiled and sold to advertisers or others in the business of molding consumer (or political) behavior. We’ve come a long way since Gutenberg, but just like when he was alive, it seems there will always be powerful groups in control of the media of the day. And, even with the utopian promise of a democratic internet, information continues to be manipulated or hidden in order to keep them powerful.

    Notes

    1. Schonfeld, Erick, “The Only Backdoor Left To Sneak Your Facebook Friends Into Google+ Is Yahoo,” Jul 5, 2011, http://techcrunch.com/2011/07/05/google-facebook-friends-yahoo/
    2. “Statement of Rights and Responsibilities,” Facebook, last revised April 26, 2011, http://www.facebook.com/terms.php
    3. Protalinski, Emil, “Facebook blocks Google Chrome extension for exporting friends,” July 5, 2011 http://www.zdnet.com/blog/facebook/facebook-blocks-google-chrome-extension-for-exporting-friends/1935
    4. “Angry Victims and Eager Business Partners React to the “Face to Facebook” Art Stunt,” ARTINFO, February 11, 2011 http://www.artinfo.com/news/story/36963/status-update-angry-victims-and-eager-business-partners-react-to-the-face-to-facebook-art-stunt/
    5. Gayathri, Amrutha, “Why Facebook’s Acts of Desperation Are Not Enough to Stop Google+,” International Business Times, July 6, 2011, http://www.ibtimes.com/articles/174946/20110706/google-plus-facebook-chrome-extension-block-facebook-friends-exporter-disable-social-network-yahoo-b.htm
    6. “Facebook Preferred Developer Consultant Program FAQ,” http://developers.facebook.com/preferreddevelopers/#FAQ
    7. Oreskovic, Alexei, “Google bars data from Facebook as rivalry heats up,” Reuters, Nov 5, 2010, http://www.reuters.com/article/2010/11/05/us-google-facebook-idUSTRE6A455420101105

    12 apps to track, share, and visualize personal data

    When it comes to personal data everyone’s first concern is usually privacy. But a lot of us want to share our data too, with friends, colleagues, and even complete strangers. While numbers have been used for centuries to improve the way we manufacture and do business, using them to quantify our personal lives is a recent phenomenon.

    I’ve been thinking about this because one of my goals in creating Give Me My Data was to inspire others to reuse their data, and respond with images and objects they created. But I’m learning if you don’t know a programming language your choices are somewhat scattered and intimidating.

    In a recent email exchange with Nicholas Felton, creator of daytum.com and other quality data products, I asked him what other user data sharing and/or visualization web applications he might have encountered while working on daytum.

    Included in this article are the three apps he mentioned with my research plus nine additions of my own. All of the apps I mention help users access their own data to track, share, and/or visualize it either by recording it themselves or exporting it from another software. There’s a table at the end of the article to summarize and compare each.

    Picture 24

    Give Me My Data givememydata.com free

    First, to give some context, Give Me My Data is a Facebook application that helps users export their data out of Facebook for reuse in visualizations, archives, or any possible method of digital storytelling. Data can be exported in common formats like CSV, XML, and JSON as well as customized network graph formats.

    Status: operational, in-development

    Picture 1

    Daytum daytum.com free/$$

    And to further contextualize, I’ll also address Daytum, an online app that allows users to collect, categorize, and share personal or other data. You can add any data that can be quantified or written down and organize and display it in many forms including bar and pie charts, plain text, and lists. There’s also a mobile site for quick submissions from your device or you can use their iphone app.

    Status: operational, but not currently being developed

    Picture 2

    Geckoboard geckoboard.com $$

    Geckoboard is a hosted real-time status board for all sorts of business (or personal) data. You can view web analytics, CRM, support, infrastructure, project management, etc., in one interface, on your computer or smart phone. To see data from other web services in your “dashboard” you add “widgets”—choose from a large list of APIs, give permissions, configure a variety of options, and see your data in a customized graph. Note though, this service is only for presenting data that is hosted elsewhere, and only in this interface. If you like looking at numbers all day, this is for you.

    Status: operational

    Picture 9

    Track-n-Graph trackngraph.com free/$$

    Track, graph, and share any information you can think of: your weight, gas mileage, coffee consumption, anything. The design is a little awkward, the graphs don’t display in Chrome or Safari (Mac), and as far as I can tell there’s no API, but the site seems very useful for storing and making simple graphs of your personal data. There are also various “templates” you can reuse to keep track of data like the Workout Tracker, which has fields for gender and age in addition to minutes you worked out, all of which are important in figuring other data (e.g. calories).

    Status: operational

    Picture 3

    your.flowingdata.com your.flowingdata.com/ free

    your.flowingdata lets you record your personal data with Twitter. With it you can collect, interact, customize views, and determine privacy by sending private tweets to your account. This project is created by Nathan Yau who writes Flowing Data and studies statistics at UCSD.

    Status: operational, in-development

    Picture 4

    mycrocosm mycro.media.mit.edu free

    Mycrocosm is a web service that allows you to track and share data and statistical graphs from the minutiae of daily life. Mycrocosm was developed by Yannick Assogba of the Sociable Media Group of the MIT Media Lab.

    Status: operational, but not currently being developed

    Picture 6

    ManyEyes www-958.ibm.com free

    ManyEyes is a project by the IBM Research and the IBM Cognos software group. On Many Eyes you can upload your own data and create visualizations, and view, discuss, and rate other’s visualizations and data sets. It is a great concept but it hasn’t evolved much since its original launch. In fact I’m finding the visualization technology has slowly devolved, leaving only about 20% of visualizations actually displaying (Chrome 12.0 on OSX 10.5.8 if folks are reading).

    Status: operational

    Picture 20

    Fitbit fitbit.com $99.95

    The Fitbit is a hardware device which tracks your motions and sleep throughout each day. This data can be uploaded and visualized on their website to realize information about your daily activities like calories burned, steps taken, distance traveled and sleep quality. The Fitbit contains a 3D motion sensor like the one found in the Nintendo Wii and plugs into a base station to upload the data.

    Status: operational

    Picture 25

    Personal Google Search History google.com/history free

    When I first saw this application on the Google site I was immediately alarmed. The amount of data they have collected is staggering; for example, “Total Google searches: 36323.” (since Jan 2006) This is a fantastic picture into the life of a user and what they are reading, watching, responding to. It’s like another, admittedly less manicured version, of Facebook. Instead of creating a profile, I am being profiled.

    The privacy implications are serious here, which is probably why you have to login again to view it. It is also why a user’s search history draws the interest of interface artist, Johannes P. Osterhof, who is in the process of exploring the line between private and public data, as well as the even further-evaporated division between surveillance and social networks, in his one-year-long search history-made public project, simply titled, Google.

    But, as everyone probably already knows, these big companies are making money and providing services. Google has the resources to take your privacy seriously. Well, kind of, because it mostly doesn’t fit into their business model to not track people.

    Status: operational

    Picture 23

    Google Takeout google.com/takeout free

    Speaking of funding, I’m quite impressed by this project. Google Takeout is developed by an engineering team at Google called the Data Liberation Front who take their jobs very seriously. In addition to their Google Takeout project, which allows you to export some of your data from Google, they have a really great website with current information about getting access to the data you store with Google.

    Status: operational, in-development

    Picture 18

    gottaFeeling gottafeeling.com free/$$

    gottaFeeling is an iphone application that allows you to track and share your feelings. It’s a simple concept, and while loaded down with a lot of rhetoric, reminds me of the amazing, “We Feel Fine.”

    Status: in-development

    Picture 5

    BuzzData buzzdata.com unsure

    Finally, I’ll end with BuzzData, a data-publishing platform that encourages the growth of communities around data. Not yet public, I’ve received a private taste of what this app will do, and it looks like it will be pretty cool. Think a mashup between Github and ManyEyes.

    Status: still in-development, not public

    So I’ll end with the table I created in my research. There are obviously many more types of ways to keep and manage data that I haven’t addressed here, but this is a good start. For further reading check out the Quantified Self blog/user community/conference created by Gary Wolf, who also authored, The Data-Driven Life, the New York Times article linked above.

    track/ uploadcustom data typesvisualizepublishprivacyexportmobile uploadAPIpricelimits

    Give Me
    My Data

    yesyesn/anoyesyesn/anofreenone

    Daytum

    yesyesyesyes$$yesmobile site and iphone appnofree / $4/ monthfree account limited by amount

    Geckoboard

    noyesyesnoyesnon/aonly for viewing$9-$200
    / month
    number of users

    Track-n-Graph

    yesyesyesyesyesnoweb-basednofree / $25 per yearfree account limited by amount

    your. flowingdata

    yesyesyesyesyesyesvia twittervia twitterfreenone

    mycrocosm

    yesyesyesyesyesnoweb-basedemail-basedfreenone

    ManyEyes

    yesyesyesyesnoyesnonofreenone

    Buzzdata

    yesyesyesyesyesyesemail?????????

    Google Web History

    yesn/ayesyesyesyesyesnofreenone

    Google Takeout

    yesyesn/an/ayesyesn/anofreenone

    Fitbit

    yesyesyesyesyesyesyesyes$100 / website is freefree web account limited by amount

    gottaFeeling

    yesnonoyesyesnoiphonenofreenone
    track/uploadCan you track or upload your own data?
    custom data typesDoes the a support custom data types?
    visualizeCan you create visualizations with the app?
    publishCan you publish your data with the software?
    privacyAre there options for keeping your data private while using the app?
    exportCan you export the data back out?
    mobile uploadAre there options to track or upload data from a device?
    APIIs there an Application Program Interface that allows you to write code to manage data?
    priceIs there a free version?
    limitsWhat limits are imposed on the free version?

    Update: Check out Google Guages and other Google Charts.

    12 apps to track, share, and visualize personal data

    Review: Memoirs of a Spymaster by Markus Wolf and Anne McElvoy

    wolf

    This is a review for the 1997 autobiography of Markus Wolf, the former head of East Germany’s foreign intelligence department.

    Wolf’s story begins with a fascinating personal history, particularly, regarding his father who was a communist and their exile from Nazi Germany in Moscow. After the end of WWII and the downfall of the Third Reich Wolf returns to Germany, to Berlin, taking a position first as a journalist in the Soviet Zone and later taking a position and rising through the ranks of the party. He eventually becomes and serves for 30 years as head of the foreign intelligence division, the Hauptverwaltung Aufklärung (HVA) (en. Main Reconnaissance Administration), within the Ministry for State Security.

    I found the writing articulate, though it often provides too much detail. It is especially riddled with justifications for controversial actions on the part of himself or the DDR. For example, there is a whole chapter devoted to Willy Brandt, the Chancellor of West Germany who resigned when one of his aides was exposed as an East German spy.

    For all the dull details of his bureaucratic life …

    “Vast stretches of this work were very boring. Intelligence is essentially a banal trade of sifting through huge amounts of random information in a search for a single enlightening gem or illuminating link.” (101)

    … the book also contains a unique historical perspective of WWII and the two German states during the Cold War. It also has many other interesting facts about pre-digital-computer surveillance including methods for protecting identities of spies and ways to physically transfer secret messages. One example, which would be easy with a computer’s ability to generate pseudo-random numbers, was the use of bank note serial numbers for random numbers in cryptographic messaging. He mentions often that he was not a fan of the use of the computer to automate details of record-keeping or gathering because he felt computer records could to easily be stolen and put into the wrong hands.

    “The problem with technical intelligence is that its essentially information without evaluation.” (284)

    In closing, I recommend this book to anyone interested in the historic details of East Germany’s Ministry for State Security. I’ll end with a few choice quotes which point to the author’s wisdom and ability for critical self-reflection.

    “The dividing line between freedom fighters and terrorists is usually determined by which side you are on.” (279)

    “No secret service can ever be democratic nor, … open to constant scrutiny.” (282)

    Germany and Google Street View

    This week I have been enjoying the blurred images of German buildings whose owners have chosen to opt-out of Google Street View. Infamous moments in the country’s history have led Germans to take privacy very seriously; especially when it comes to information about their residences. Unlike the United States, where data privacy is an opt-out option, Germany law states that, “citizens must opt-in to have their data collected in any way.” (1). In fact, there is a document detailing the rights of the “data subject” in the German Federal Data Protection Act which serves “to protect the individual against his right to privacy being impaired through the handling of his personal data.”

    An even more powerful gesture are the very public images that have resulted from this protection. While they serve a specific function—to obscure identifying aspects of buildings, faces, etc.—they also communicate very effectively the message that individuals should have the right to decide how their data is used. This gets to the heart of the Give Me My Data app—to prompt this sort of discussion. It is then ironic that Google, a company whose revenue is based almost completely on advertising opportunities made possible by aggregating and re-representing data, has inadvertently brought us this message.

    I was excited to find my own apartment building in Berlin has been removed.

    Picture 15

    Picture 14

    Another building down the street

    Picture 1

    Helge Denker, a reporter with the German daily, Das Bild, has found a clever way to opt-out.

    helge

    Facebook’s recommended privacy settings should emphasize more not less

    Facebook’s “Privacy Settings” always seem to be a work in progress. One thing they do consistently is default to less privacy overall, thus more sharing of your information on their site. For a website that depends on user-generated content the motivation to encourage sharing is clear enough. Still, why do they use the word “privacy” if they’re not actually embracing the idea?

    For example, a recent update introduces a table with degrees of privacy from less to more (left to right). Types of data are listed in rows, while access is shown in the columns, with Everyone to Friends Only, again left to right.

    fb_more

    Curious about what Facebook “Recommended” settings were, I clicked and am sharing the screenshot below. I am not surprised to see that they wish me to open-up all content I generate; status messages, posts, images, etc. and discourage allowing anyone I don’t know to comment on posts (probably as spam prevention).

    fb_less

    I have been thinking about privacy quite a bit this week, developing ideas for what next to do with Give Me My Data, and providing an interview about social media for Naked on Pluto (along with the likes of Marc Garrett and Geert Lovink). Plus I went to see the “geek hero story” The Social Network at the Babylon Cinema last night.

    Anyway, after all this thinking about Facebook’s past, I’m curious about its future, and how it will continue to try to hold on to the #1 social networking website position that Friendster and MySpace lost so quickly. The API, games, etc could be expected, but the Facebook Connect tools that are so prevalent now, even on Yelp, a site I figured could make it without schlepping, were a surprise.

    Facebook Connect, a jquery “widget” that allows you to login to other websites using your Facebook ID, is clever and eerie at once. It allows Facebook to track you when you are not even on their site, and make sure you stay loyal. If that sounds sinister, well it is. What other purpose could there be for making available a service with the single purpose of mediating every interaction or bit of content you add to the web? It seems at first like OpenID, and it is, except that its run by a multi-billion dollar social media corporation.

    Reading list for August 2010

    About to embark on some new projects here in Berlin. Here’s my reading list at the moment…

    free

    Free: The Future of a Radical Price
    by Chris Anderson
    July 7th 2009 by Hyperion

    Traditional economics operates under fundamental assumptions of scarcity–there’s only so much oil, iron, and gold in the world. But the online economy is built upon three cornerstones: processing power, hard drive storage, and bandwidth–and the costs of all these elements are trending toward zero at an incredible rate.

    The Exploit

    The Exploit: A Theory of Networks
    by Alexander R. Galloway, Eugene Thacker
    October 1st 2007 by Univ Of Minnesota Press

    “The Exploit is that rare thing: a book with a clear grasp of how networks operate that also understands the political implications of this emerging form of power. It cuts through the nonsense about how ‘free’ and ‘democratic’ networks supposedly are, and it offers a rich analysis of how network protocols create a new kind of control. Essential reading for all theorists, artists, activists, techheads, and hackers of the Net.” —McKenzie Wark, author of A Hacker Manifesto

    gw_cover_front

    Group Work
    by Temporary Services
    New York, NY: Printed Matter. 2007

    Based on a pamphlet published by Temporary Services in 2002 titled Group Work: A Compilation of Quotes About Collaboration from a Variety of Sources and Practices, this publication provides a multitude of perspectives on the theme of Group Work by practitioners of artistic group practice from 1960s to the present.

    Automata: Counter-Surveillance in Public Space paper on the Public Interventions panel at ISEA2010

    isea2010_logo_klein

    ISEA2010 RUHR Conference in Dortmund, Germany

    P26 Public Interventions
    Tue 24 August 2010
    15:00–16:30h
    Volkshochschule Dortmund, S 137a
    Moderated by Georg Dietzler (de)

    • 15:00h | Owen Mundy (us): Automata: Counter-Surveillance in Public Space
    • 15:20h | Christoph Brunner (ch/ca), Jonas Fritsch (dk): Balloons, Sweat and Technologies. Urban Interventions through Ephemeral Architectures
    • 15:40h | Georg Klein (de): Don’t Call It Art! On Artistic Strategies and Political Implications of Media Art in Public Space
    • 16:00h | Georg Dietzler (de): Radical Ecological Art and No Greenwash Exhibitions

    About my talk:

    Automata is the working title for a counter-surveillance internet bot that will record and display the mutually-beneficial interrelationships between institutions for higher learning, the global defense industry, and world militaries. Give Me My Data is a Facbook application that help users reclaim and reuse their Facebook data. The two projects, both ongoing, address important issues surounding contemporary forms of communication, surveillance, and control.

    Recent and ongoing projects

    Howdy, it’s been awhile since I last shared news about recent and ongoing projects. Here goes.

    close-your-eyes-ac-direct-me-14_1000h

    1. You Never Close Your Eyes Anymore

    You Never Close Your Eyes Anymore is an installation that projects moving US Geological Survey (USGS) satellite images using handmade kinetic projection devices.

    Each device hangs from the ceiling and uses electronic components to rotate strips of satellite images on transparency in front of an LED light source. They are constructed with found materials like camera lenses and consumer by-products and mimic remote sensing devices, bomb sights, and cameras in Unmanned Aerial Vehicles.

    The installation includes altered images from various forms of lens-based analysis on a micro and macro scale; land masses, ice sheets, and images of retinas, printed on reflective silver film.

    On display now until July 31 at AC Institute 547 W. 27th St, 5th Floor
    Hours: Wed., Fri. & Sat.: 1-6pm, Thurs.: 1-8pm

    New video by Asa Gauen and images
    http://owenmundy.com/site/close_your_eyes

    2. Images and video documentation of You Never Close Your Eyes Anymore will also be included in an upcoming Routledge publication and website:

    Reframing Photography: Theory and Practice
    by Rebekah Modrak, Bill Anthes
    ISBN: 978-0-415-77920-3
    Publish Date: November 16th 2010
    http://www.routledge.com/books/details/9780415779203/

    gmmdlogo

    3. Give Me My Data launch

    Give Me My Data is a Facebook application designed to give users the ability to export their data out of Facebook for any purpose they see fit. This could include making artwork, archiving and deleting your account, or circumventing the interface Facebook provides. Data can be exported in CSV, XML, and other common formats. Give Me My Data is currently in public-beta.

    Website
    http://givememydata.com/

    Facebook application
    http://apps.facebook.com/give_me_my_data/

    logo_nyt

    4. Give Me My Data was also covered recently by the New York Times, BBC, TechCrunch, and others:

    Facebook App Brings Back Data by Riva Richmond, New York Times, May 1, 2010
    http://gadgetwise.blogs.nytimes.com/2010/05/01/facebook-app-brings-back-data/

    Picture 6

    5. yourarthere.net launch

    A major server and website upgrade to the yourarthere.net web-hosting co-op for artists and creatives. The new site allows members of the community to create profiles and post images, tags, biography, and events. In addition to the community aspect, yourarthere.net is still the best deal going for hosting your artist website.

    Website
    http://yourarthere.net

    More images
    http://owenmundy.com/site/design_yourarthere_net

    americans_nwfsc_0033_1000w

    6. The Americans

    The Americans is currently on view at the Northwest Florida State College in Niceville, FL. It features a new work with the same title.

    More images
    http://owenmundy.com/site/the-americans

    bb101_schematic_oblique

    7. Your Art Here billboard hanger

    I recently designed a new billboard hanging device and installed it in downtown Bloomington, IN with the help of my brother Reed, and wife Joelle Dietrick.

    Stay tuned here for news about Your Art Here and the new billboard by Joelle Dietrick.
    http://www.facebook.com/pages/Your-Art-Here/112561318756736

    lockheedmartin.com_sitemap_20091214_red_800w

    8. Finally, moving to Berlin for a year on a DAAD fellowship to work on some ongoing projects, including Automata.

    More images
    https://owenmundy.com/blog/2010/07/new-automata-sitemaps/

    I’ll be giving a paper about Automata at the upcoming ISEA2010 conference in Ruhr, Germany.
    http://www.isea2010ruhr.org/conference/tuesday-24-august-2010-dortmund

    Many thanks to Chris Csikszentmihályi, Director of the Center for Future Civic Media http://civic.mit.edu/ , for inviting me to the MIT Media Lab last August to discuss the project with his Computing Culture Group: http://compcult.wordpress.com/

    Schematic for You Never Close Your Eyes Anymore

    “Open sourcing” the schematic for the electronic components for You Never Close Your Eyes Anymore.

    Picture 5

    Products:

    RBBB boards (Arduino clone)
    custom-designed circuits
    – female headers
    – TIP31 transistor
    – 6-wire Unipolar Stepper motor (48 step Nippon Electric Pulse Motor)
    – ULN2803A Darlington Array
    – hook-up wire
    – various resistors
    – LEDs
    used camera lenses
    aluminum “flat bar”
    hose clamps
    rubber wine corks
    various mounting hardware

    New yourarthere.net website is live

    After 4 months the new yourarthere.net website and member-run content management system is now live. Thanks to Braylin and Brittany Morales, Beth Lee, and Chris Cumbie for all their hard work.

    The site is valid XHTML/CSS and runs on PHP/MySQL using the Codeigniter framework. All the details from our research from inception onward are archived here.

    This site is based around the idea that members should have control of the content on the website. Every member has a profile where they can add images, text, tags, and events to promote their artwork or group. Members can create a new profile for every domain they host with yourarthere.nets.

    Picture 6

    Picture 8

    Give Me My Data updates

    Give Me My Data is a Facebook application that helps you reclaim and reuse your facebook data. It is currently in-development but starting to receive an amazing amount of traffic from Facebook users. Apparently the developers at Facebook made a change to the interface this week leaving many users unable to find or display specific information they had added to their pages. Give Me My Data helps users circumvent the problems they are having with the interface by giving them another way to access their data.

    Due to the amount of questions I have received about the application I decided to launch a new website to share information about it here: givememydata.com

    website_20100428

    app_20100428


    Facebook application interface

    stats_20100428_map


    Visitors from this week (via statcounter)

    The application profile page
    Use the application

    Letter in Support of Ricardo Dominguez and Brett Stalbaum

    commentary_t352

    To whom it may concern,

    I write this letter in support of Professors Ricardo Dominguez and Brett Stalbaum, and their collaborators at the Bang.Lab at the University of California, San Diego. The criminalization of the research conducted by Dominguez and Staulbaum can and should be expected by xenophobic and racist outsiders in the San Diego community, but I was appalled to hear that the University of California is not whole-heartedly supporting Professors Dominguez and Stalbaum in the wake of recent hateful and threatening responses to their current work.

    As a logistical tool, one could argue their Transborder Immigrant Tool will be only as effectual as the amount of GPS-enabled cell phones that can be made available in the area. Consider especially their demographic primarily includes human beings that would take the chance to cross miles of desert by foot, risking starvation and death, in order to find a better life. While efforts may be made to help the logistics of this project, this is not a group you would expect to have income to acquire such devices.

    I think most importantly their research should be looked at as a humanitarian gesture to bring into light an important problem in this geographic region. The inequality between classes in this area, drawn along racial and political boundaries, has caused a deep resentment on both sides of the border. Professor Dominguez and Stalbaum’s tool, while it takes the form of a functional opportunity to save the lives of other human beings, is as much a cultural product that initiates a very public conversation about an important issue, and suggests at the heart of the problem is the inability for some groups to consider the well-being of others.

    It is important the University of California facilitate this conversation and acknowledge the contribution this project makes to the fields of visual arts, human computer interaction, and cultural studies, and support the work of Professors Dominguez and Stalbaum in a time when they need it most.

    Sincerely,

    Owen Mundy
    Assistant Professor
    Department of Art
    Florida State University
    omundy@fsu.edu

    Masters of Visual Arts, 2008
    University of California, San Diego

    Learn more about the issue
    http://bang.calit2.net/

    As usual, a perspective on past issues related to this problem in the area will help contextualize this one.

    Learn about Herbert Marcuse and his problems with San Diego/UCSD in this documentary
    http://video.google.com/videoplay?docid=-5311625903124176509#

    Even more related, David Avalos, Elizabeth Cisco, and Louis Hock’s Art Rebate project which garnered all kinds of dissidence from the San Diego community, was intended specifically to bring into the public eye an important and overlooked part of the local economy—that of wages and labor of migrant workers.
    http://findarticles.com/p/articles/mi_m2479/is_n1_v22/ai_15627403/

    Articles
    UC San Diego professor who studies disobedience gains followers — and investigators, LA Times

    Other letters

    Temporary Services in Chicago
    http://www.temporaryservices.org/current_services.html#dominguez

    Cheap, low-wattage studio lighting (part 2)

    The florescent bulbs and light kit arrived this week and it was good to see the results of my research. I only found one problem in that the 105W (400W incandescent equivalent) daylight-balanced florescent bulbs were so large the base of the bulb prevented them from fitting into the fixtures.

    studioLights_pt2_01

    studioLights_pt2_02

    studioLights_pt2_03

    I expected they would be bigger than usual, but (in the photos) its amazing how much larger they are than a standard 15W (40W equivalent) florescent bulb. To reiterate, the part you screw into the fixture is a standard (E26) Edison Screw type cap, the same type found on most home incandescent and CFL bulbs.

    studioLights_pt2_04

    studioLights_pt2_05

    I was able to solve the problem for less than $5 at the local big box hardware store with two $2 fixture extenders, and luckily the rod of the reflector umbrellas just barely clear the big bulbs.

    studioLights_pt2_07

    studioLights_pt2_08

    The fixtures are made to carry 250W so it is fine that my bulbs only draw 105W each. The adjustable mount for the lamp fixtures, however, are a little precarious. They are not made to support the weight of these larger bulbs along with the umbrellas so I had to tighten them more than usual. In the future I may find a better solution, but for this project they will do fine.

    studioLights_pt2_06

    studioLights_pt2_09

    Here are some initial tests with the kit and bulbs. These were shot with one light in Camera Raw with a Canon G9, ASA 100, f/3.2 @ 1/13 between 6-10′ from the lights.

    studioLights_pt2_10

    studioLights_pt2_11

    And these at f/4 @ 1/13 with both lights at around the same distance.

    studioLights_pt2_12

    studioLights_pt2_13

    Cheap, low-wattage studio lighting (part 1)

    Update on the photo studio project: I still need a flag and pole (any ideas?) but some advice from a friend and additional research has yielded a great inexpensive lighting option.

    48853

    The Smith-Victor KT-500U Photoflood Tungsten Light Kit with Umbrellas (B&H # SMKT500 Mfr # 401430) looks like a decent and affordable kit, about 50% of which can be found at any hardware store sans brands. But 250W is a lot of energy to waste on heat, and the Tungsten 3200ºK has a 20 hour life span, which is very short. While the daylight bulb only has a four-hour lifespan!

    It has been a while since I researched studio lighting, but with developments in CFLs and LEDs you can now get high lumen, always-on lights, that don’t waste energy and create so much heat that it makes it uncomfortable to work with them.

    So instead of the incandescent bulbs, I found these CFLs. They are daylight-balanced (6500ºK), 105W (400W incandescent equivalent), and have a 8000 hour life span, all for less than $30 each. Photo geeks and indoor growers also agree that the spectrum good.

    So for less than $200 I’m looking at a decent set of lights that doesn’t require a light meter (I have a grey card) and doesn’t get hot. It’s quite bright, but I can move it back or bounce it off or through the umbrella.

    Photography (Basic) NAVEDTRA 12700

    navedtra_7-7_ruleofthirds

    I’m working on a new project to recreate a military portrait studio encountered during my previous life as a Navy photographer. In June 2010 I will install it in a solo exhibition at Holzhauer Gallery, Northwest Florida State College in Niceville, Florida, nestled neatly at the edge of Eglin Air Force Base, the “largest air base in the free world.” (quoted from a display at the nearby Air Force Armament Museum)

    The project is inspired by rediscovering the Navy photo manual that was issued to me in April 1993 when I entered A-school at the Defense Photography School in Pensacola, FL. The inspiration for this project comes from chapter 7. There are also a lot of great illustrations and photographs including:

    • Page 5-2 has drawings of “photo techniques.”
    • Page 4-30 has an image (from a 4×5 view camera) of the school I went to.
    • Page 6-12 has an example of the old “grip and grin” ceremony.

    More updates on the project will follow soon.

    navedtra_7-16_fulllengthphoto

    navedtra_5-2

    Lost in place: iPhone screenshots of grid system

    IMG_1399

    IMG_1402

    Two screenshots from my phone depicting the grid underneath the Google Map graphics which are tiled to create the map interface. Clearly, the “virtual GPS” technology on my first-generation iPhone has often been helpful in finding my way. But what happens when it fails and you are literally lost in space? The social landscape, politics, climate, language(s), culture are what we analyze to understand “where” we are. Without these points of reference how can we create an idea of place? In this case, the simple query, “Tallahassee,” can be enough for any individual slightly immersed in Southern culture to create a perception of this place.

    My retina, photographed at Ars Electronica in Linz

    Below is the image and text from the email response to an interactive exhibit at Ars Electronica in Linz where you can photograph your retina.

    image

    This retina photo was taken in the BrainLab of the Ars Electronica Center Linz, Austria.
    We would like to welcome you at the Museum of the Future! More information at: www.aec.at/center

    Best regards,
    Your Ars Electronica Team

    Notes on MIT Media Lab _res_ summer 2009

    This summer I worked at the MIT Media Lab on my Automata project, an internet bot and online application that makes visible hidden relationships of power.

    Some photos and notes from time at MIT Media Lab with Chris Csikszentmihályi.

    IMG_0924

    New edition to Media Lab

    IMG_0922

    Strange

    IMG_0935

    Boston Contemporary

    IMG_0944

    MIT Sailing, free for students.

    IMG_0953

    Chris Csikszentmihályi

    IMG_0978

    Me on the Mystic River

    IMG_0982

    Chris’ robot kayak.