Tag: surveillance

Stasi / Facebook / Big Data DAAD Day 28 – The Stasi Archive and BStU

After some traveling and conferences and development sprints on other projects I have time this week to come back to the Stasi work. The first post is about the Stasi Records Agency (BStU), whose full name (in English) is the impressive, “Federal Commissioner for the Records of the State Security Service of the former German Democratic Republic”.
Stasi / Facebook / Big Data DAAD Day 28 – The Stasi Archive and BStU


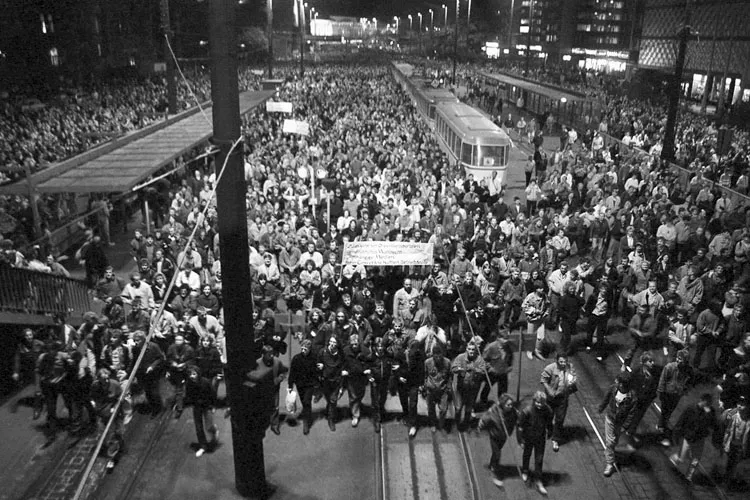
Monday Demonstration in Leipzig on 16 October 1989

At the end of 1989 the Peaceful Revolution spread across the former East Germany. These protests led to the opening of the border via the emotional breaking apart of the Berlin Wall, as well as the end of the reign of the SED government, and with it, the Stasi.

During the transition protesters realized the Stasi agencies were destroying the files that could incriminate them. Groups of citizens occupied Stasi offices across East Germany and sealed the buildings to prevent further destruction of information. On January 15, 1990, citizens gained access and occupied the Berlin headquarters of the Stasi.

After German reunification the BStU was established to preserve the archives and investigate the past of the Stasi. Since January 1992 they have provided a service to allow citizens to view the Stasi files that concern them.

In Berlin the BStU is located at 31 Karl-Liebknecht-Straße, with the files appropriately continuing to be located in the former Stasi headquarters on Frankfurter Allee in Lichtenberg. Here are some photos I took inside the archives in the former Stasi headquarters.
Stasi / Facebook / Big Data DAAD Day 28 – The Stasi Archive and BStU


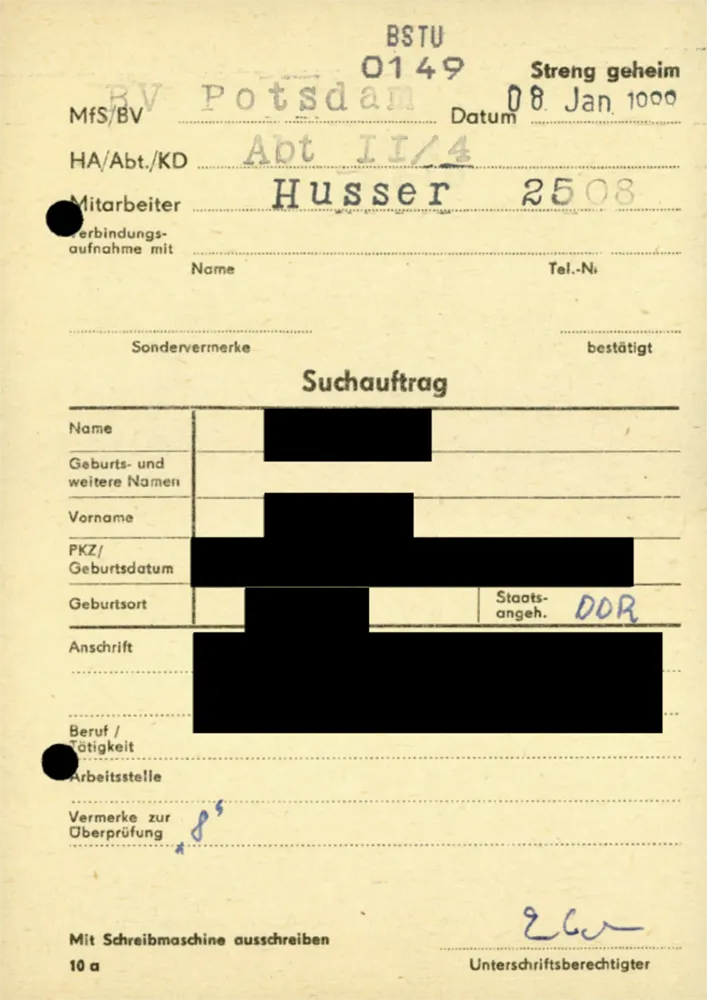
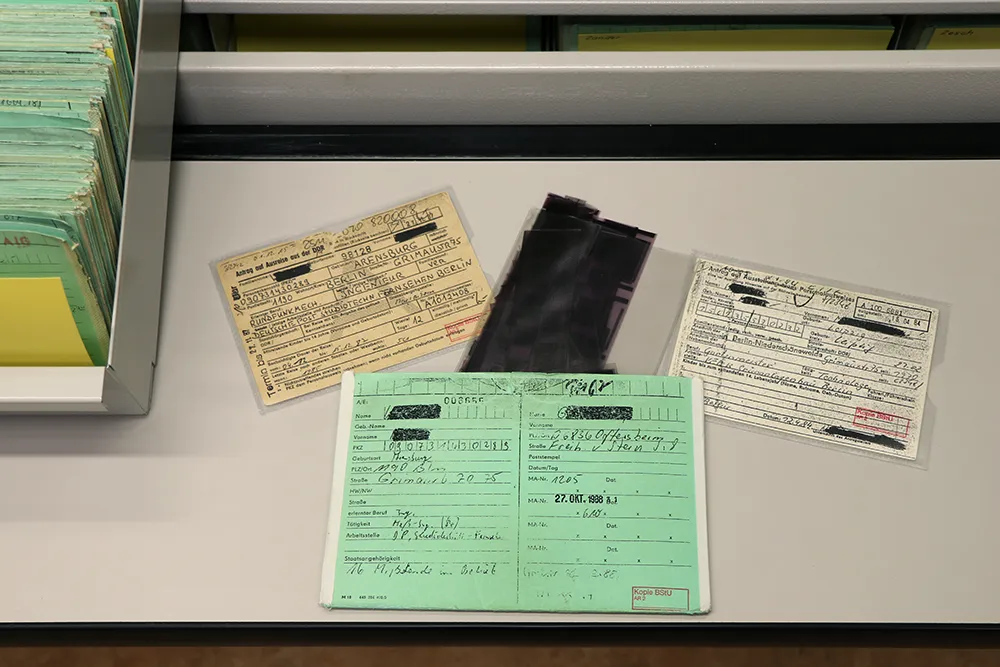
An example card from the Stasi card index now used to locate information for citizens wanting to know what data the Stasi collected, Stasi Records Agency, 2017
Stasi / Facebook / Big Data DAAD Day 28 – The Stasi Archive and BStU


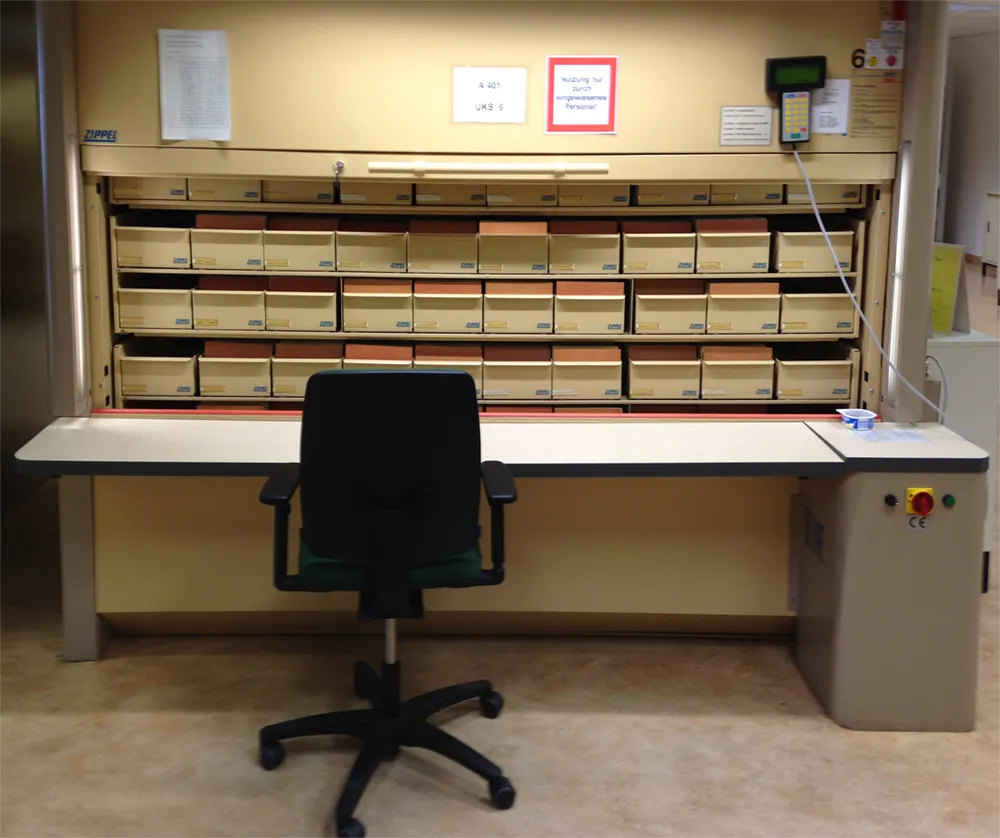
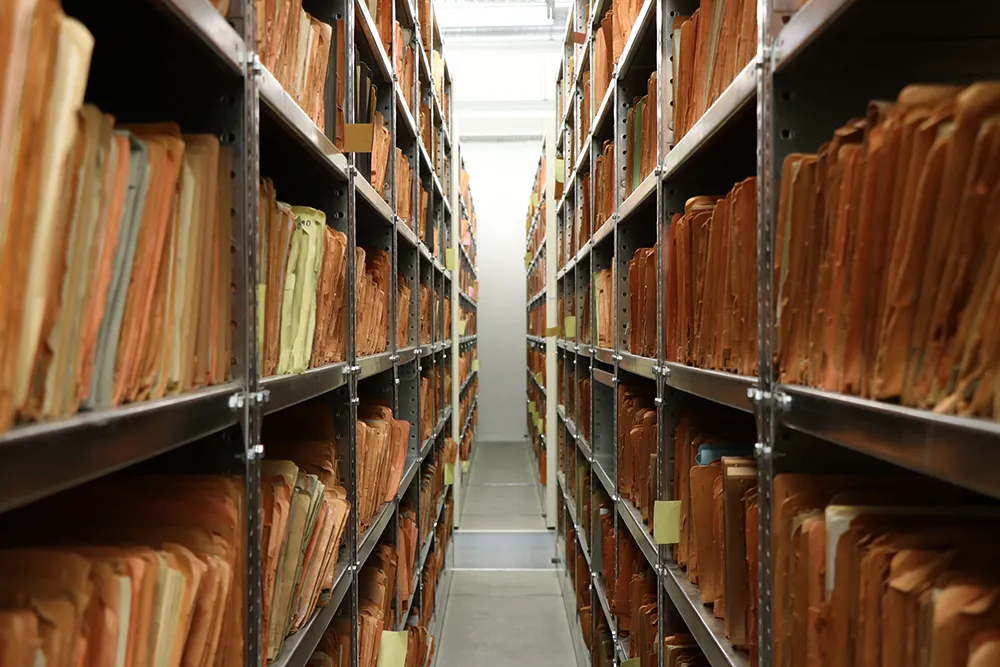
Shelves of citizen files now open to view by the citizens the Stasi surveilled, Stasi Records Agency, 2017
Stasi / Facebook / Big Data DAAD Day 28 – The Stasi Archive and BStU


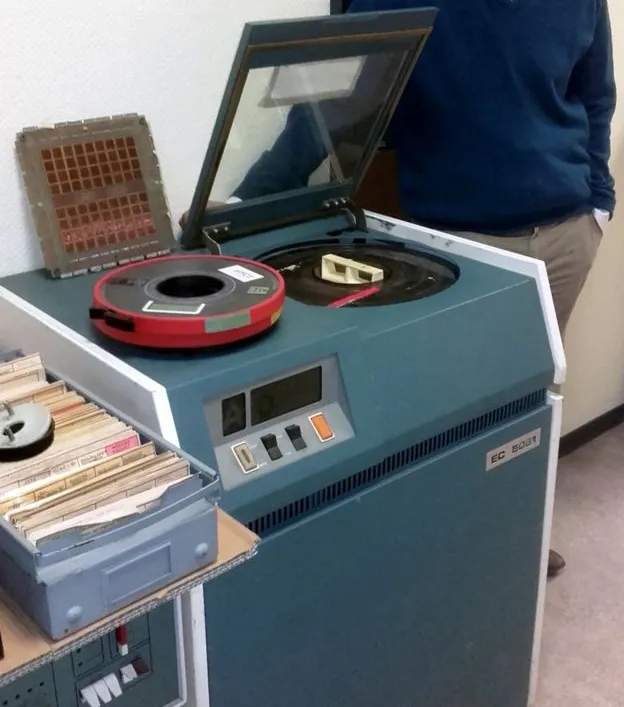
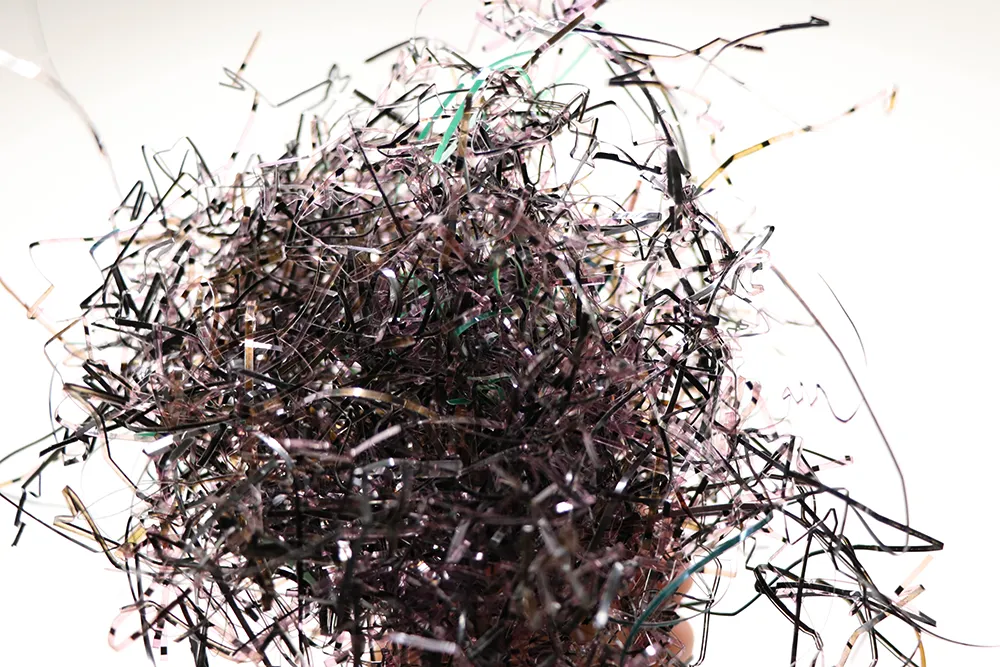
Microfiche shredded by Stasi agents, Stasi Records Agency, 2017
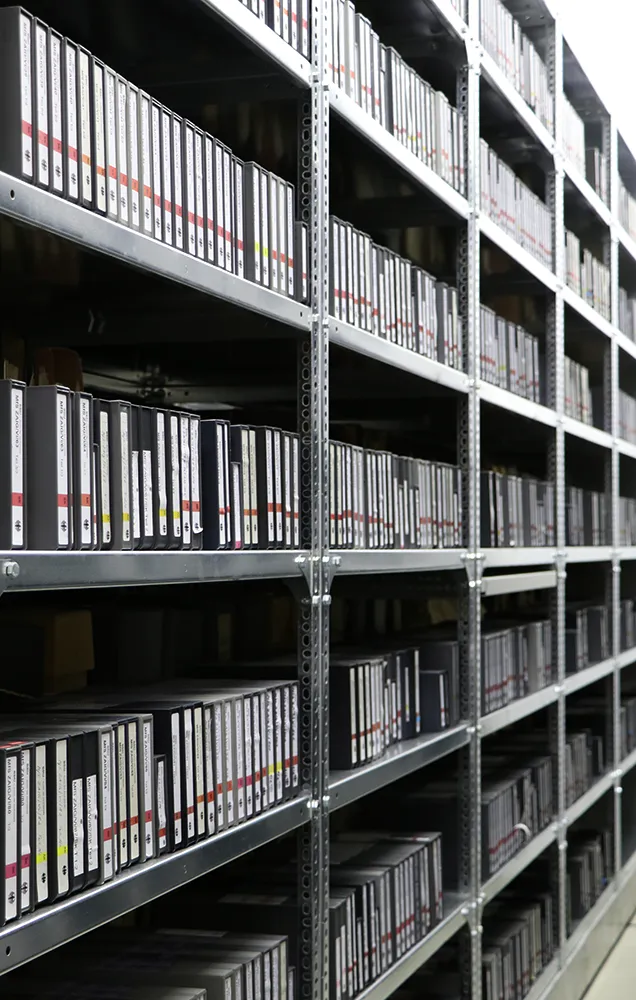
Stasi / Facebook / Big Data DAAD Day 28 – The Stasi Archive and BStU


Shelves of surveillance video, Stasi Records Agency, 2017

In addition to providing access to citizen’s files, the BStU assists scholars by allowing viewing of other Stasi documents. In my case, their staff helped me to find and view schematics of postal surveillance machines prepared by the Stasi OTS.
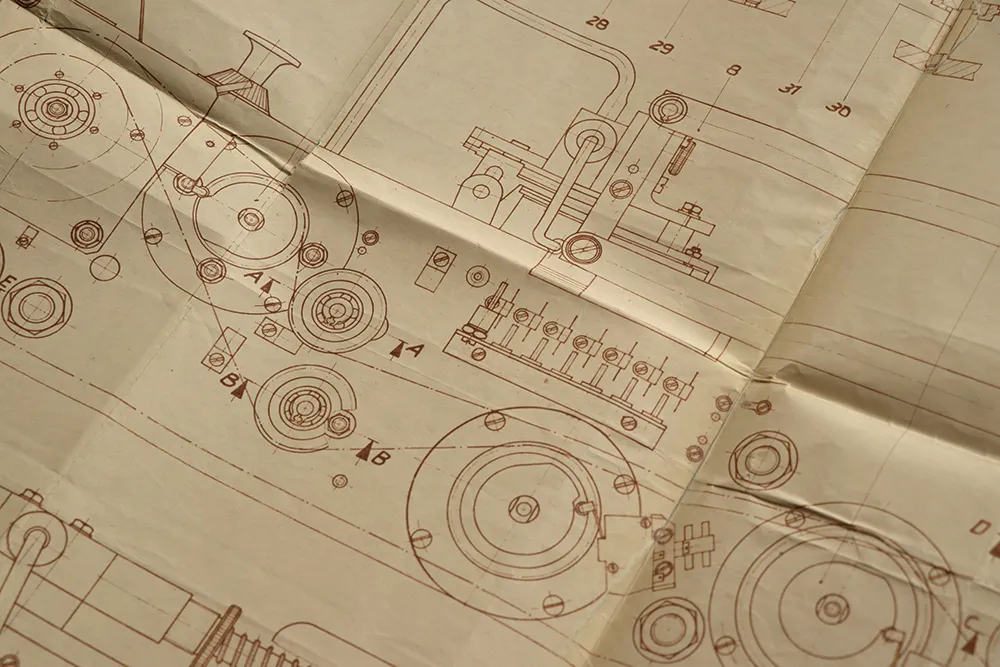
Stasi / Facebook / Big Data DAAD Day 28 – The Stasi Archive and BStU


Detail of the Stasi Automatic Letter Closing Machine schematic, Stasi Records Agency, 2017

The BStU also has a thorough library at the Karl-Liebknecht-Straße location. Unlike the Stasi documents, which require one to make an application as a scholar, the library is open to the public.
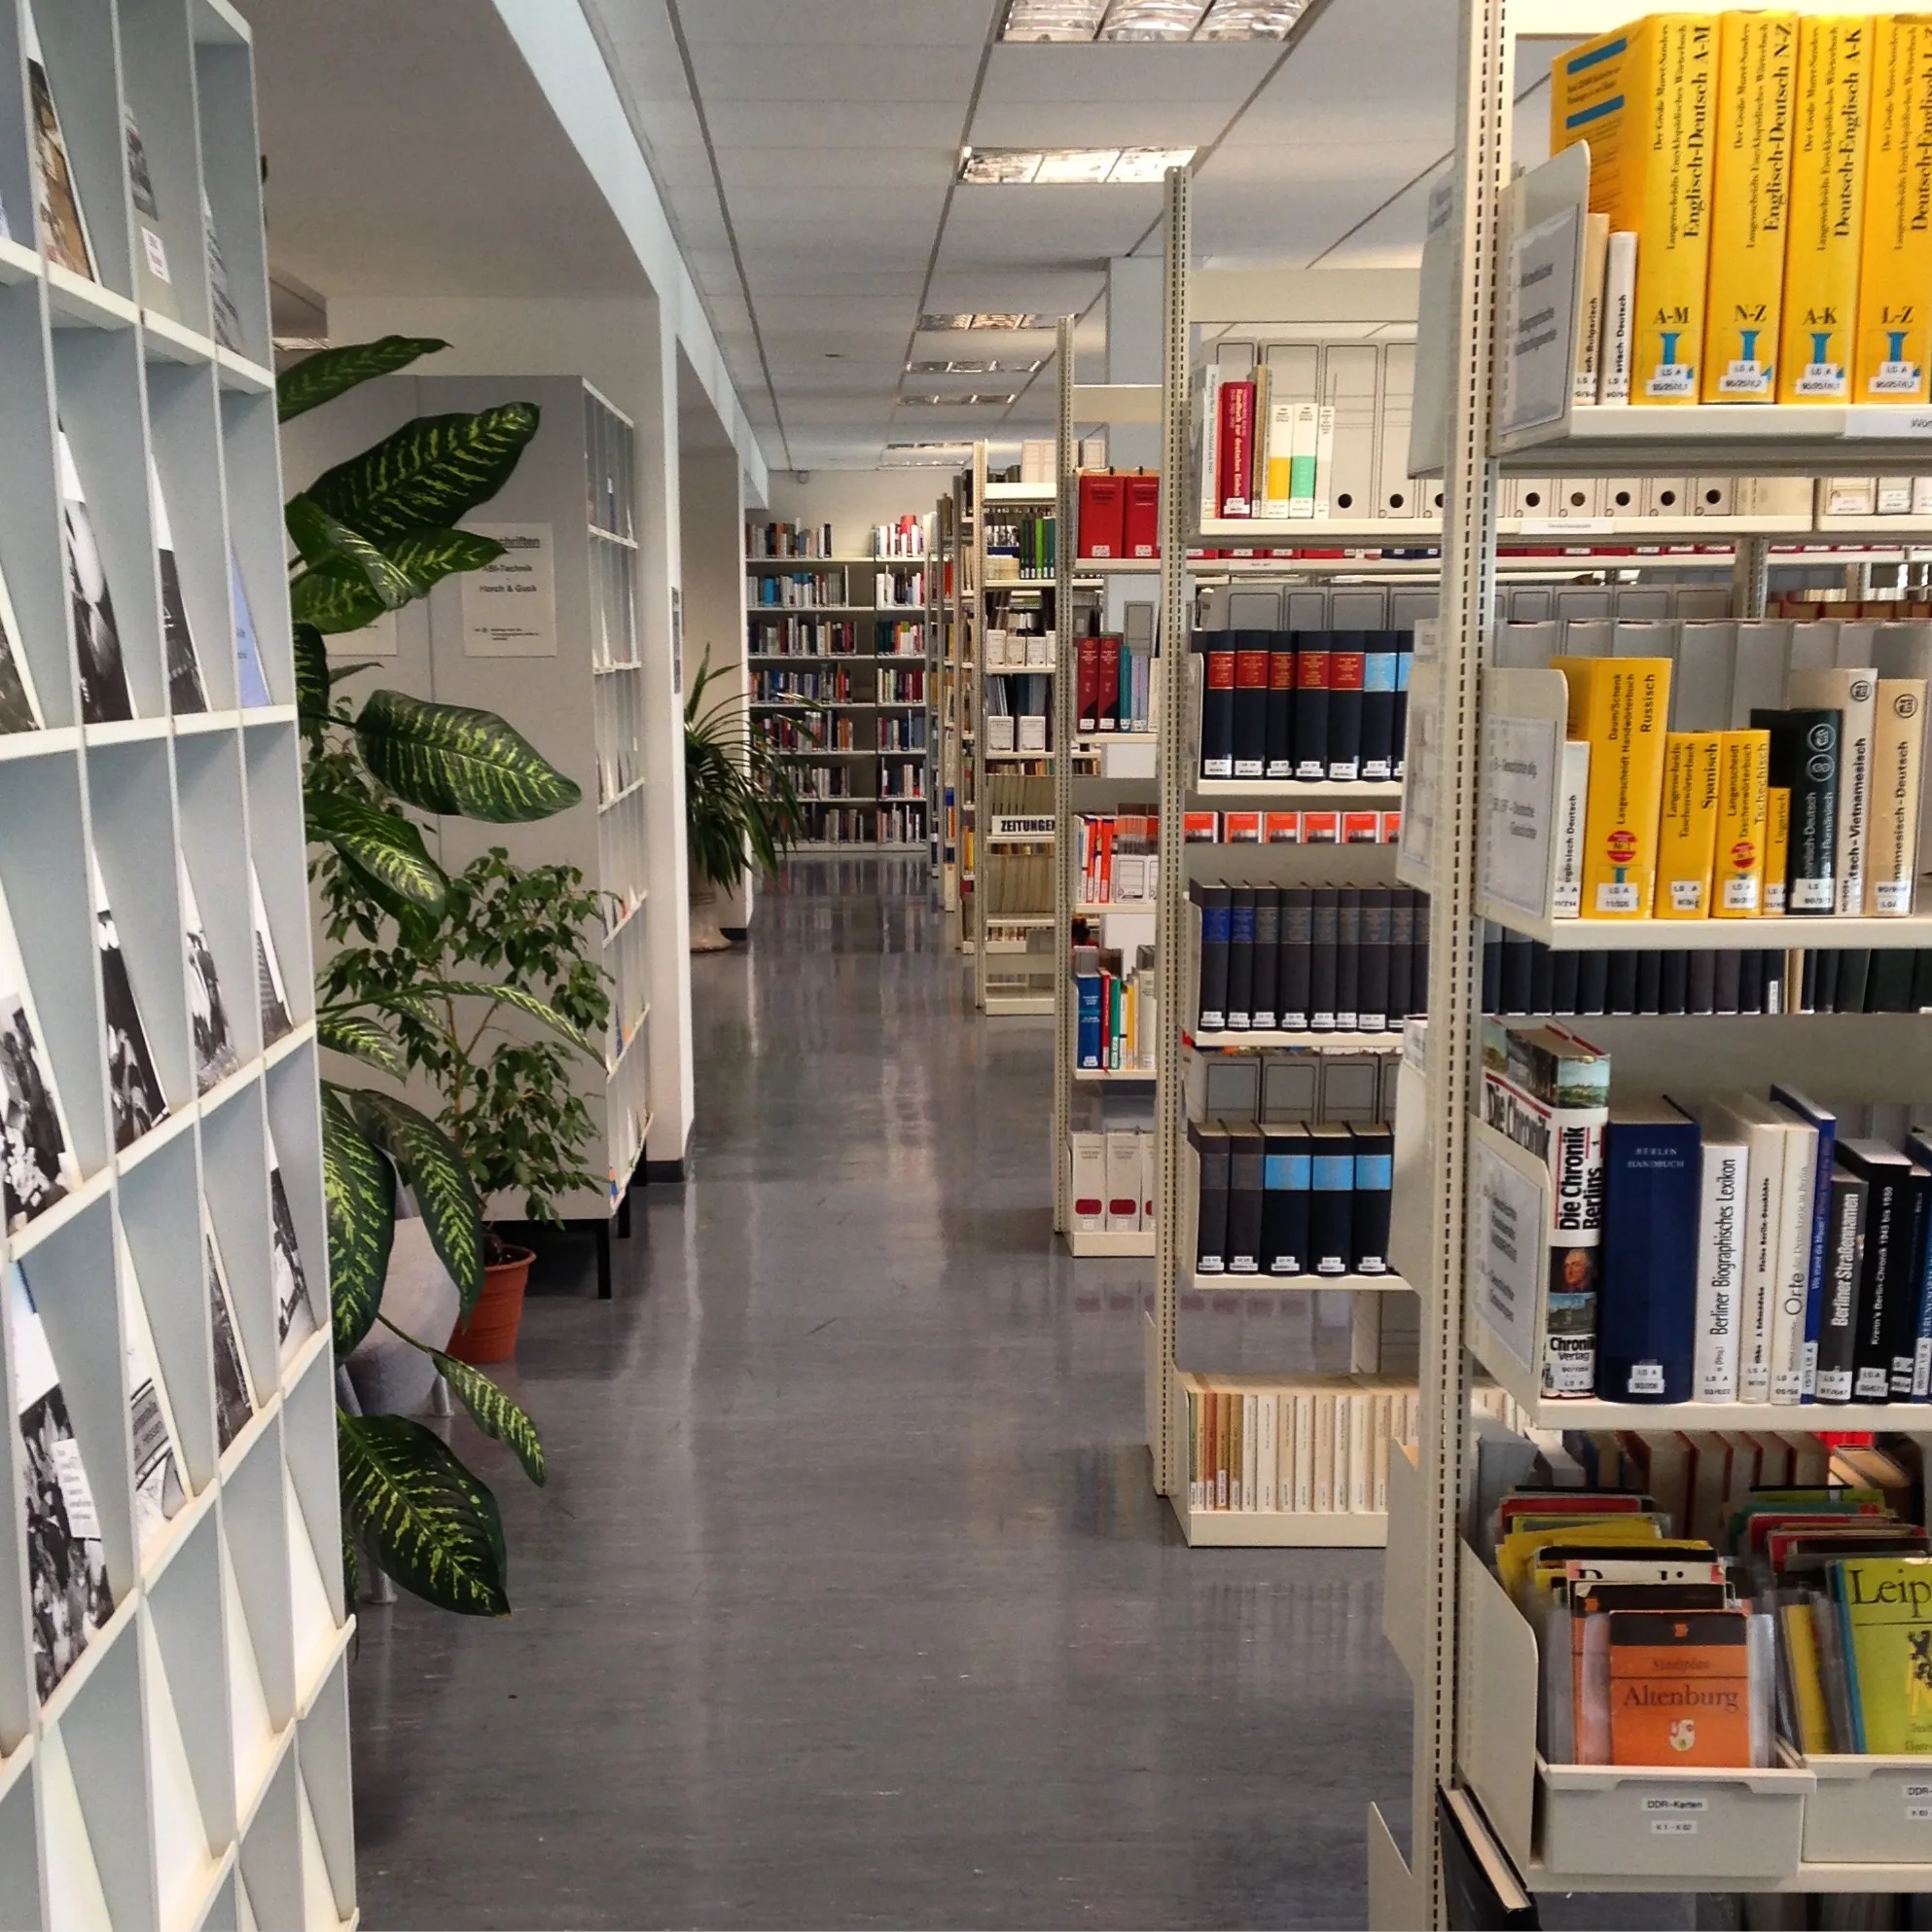
Stasi / Facebook / Big Data DAAD Day 28 – The Stasi Archive and BStU


The BStU library, 2017

A Deutsche Welle report on the Stasi archives, 2010
Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie

Yesterday I headed to the Museum für Fotografie to see two exhibitions on surveillance.

The Field Has Eyes. Images of the Surveillant Gaze includes 75 prints, books, photographs and examples of optical apparatus to present a visual and cultural history of the controlling gaze from the 16th to the 20th century. I don’t have many images because ironically the museum of photography does not allow photographs.

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie


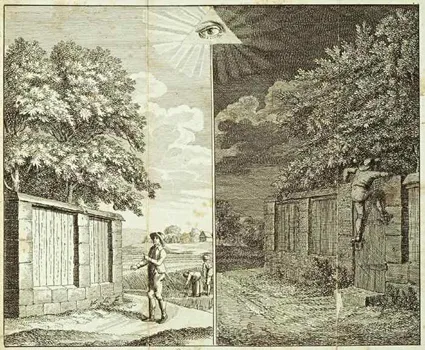
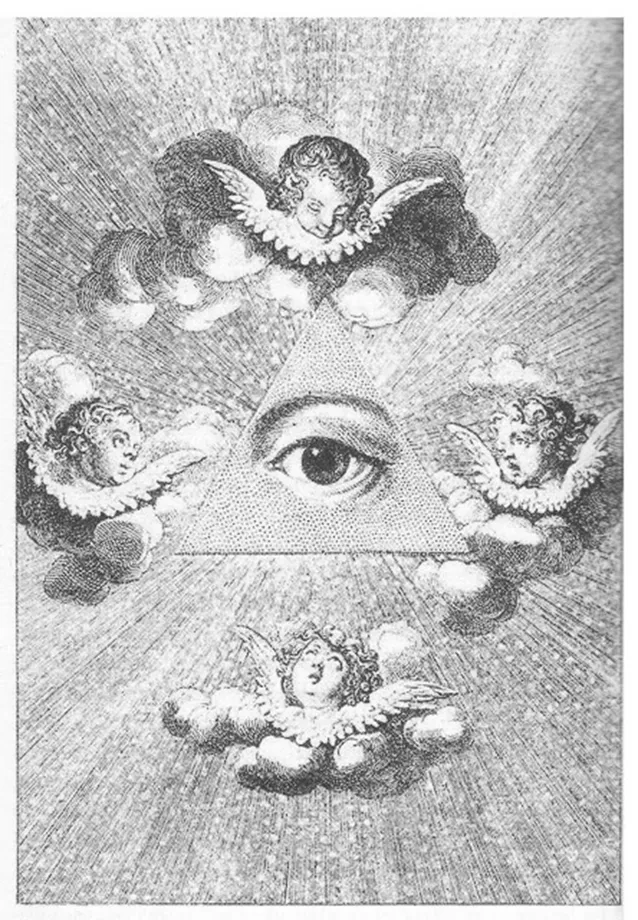
Daniel Chodowiecki. The Eye of Providence. 1787. Etching, 4 x 5′”

Still, I was able to track down many works online. An example is this one, which focuses on the “all seeing eye” of God as a heavenly entity that watches over everyone like Daniel Chodowiecki’s The Eye of Providence (1787).

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie


Johann Paul Pöhlmann. Gottes Augen schauen auch in die heimlichen Winkel (English: “God’s eyes also look into the secret angles”), Kupferstich: 135 x 165 mm, 1809

This view of God as a watcher later evolved into a sort of big brother figure like in Gottes Augen schauen auch in die heimlichen Winkel (English: “God’s eyes also look into the secret angles”), a copperplate by Johann Paul Pöhlmann from 1809. Here the all seeing eye is essentially a surveillance camera, encouraging potential law breakers to heed the warning that their bad deeds won’t go unpunished. This sort of indoctrination was easily transferred to messages from political bodies wishing to keep the behavior of their citizens inline as nation states emerged.

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie

Watching You, Watching Me. A Photographic Response to Surveillance shows works by 10 contemporary artists using photography to address surveillance. This exhibition was sponsored by the Open Society Foundation.

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie


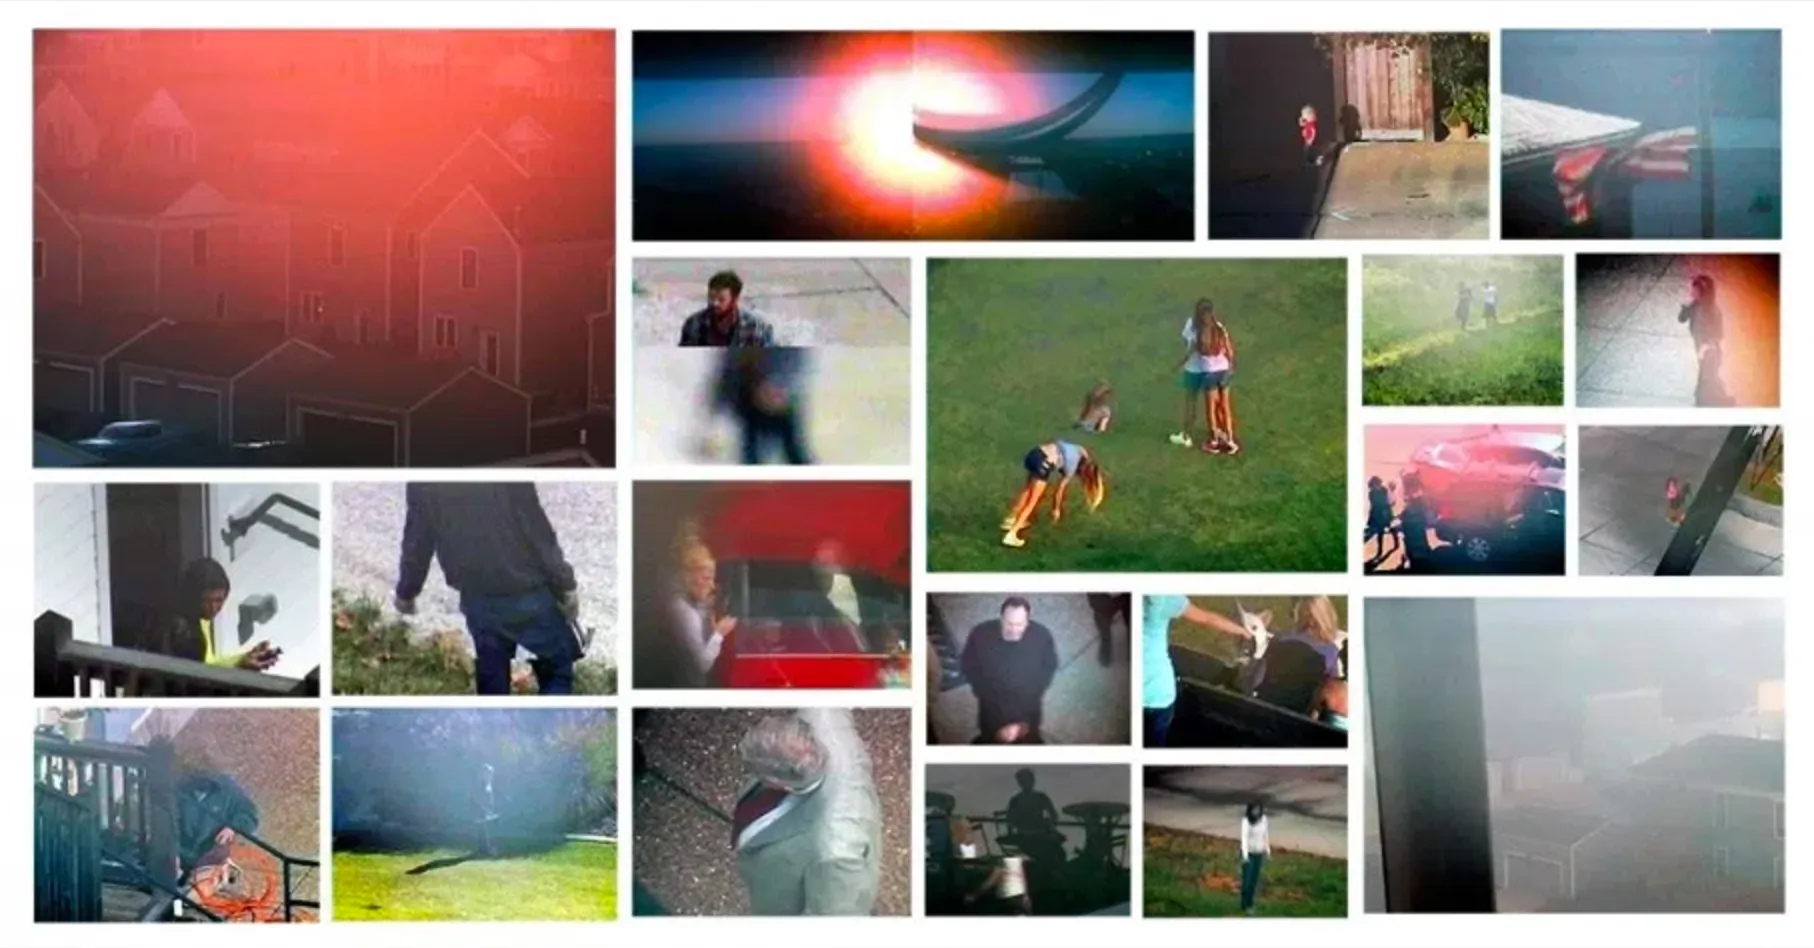
Andrew Hammerand. The New Town. 2013.

In Andrew Hammerand’s The new town (2013), the artist captured surveillance images from a camera placed in the center of an idealized planned community in the American Midwest. These are haunting and beautiful reminders of the gaze of the all seeing eye, and the inability to escape from it in even the most ideal locations.

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie


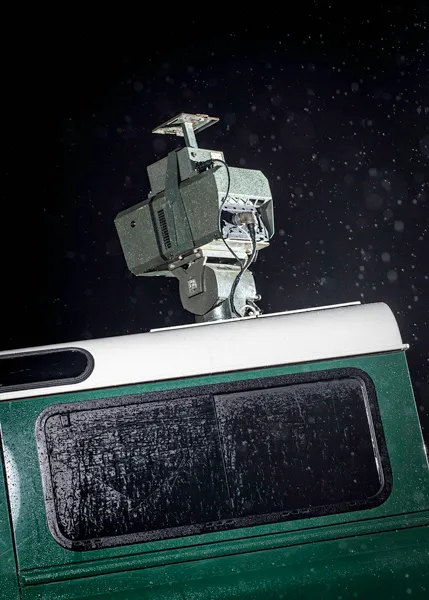
Julian Roeder. Thermal Imaging Camera, Northern Greece, 2012, Archival Pigment Print, 152 x 109 cm

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie


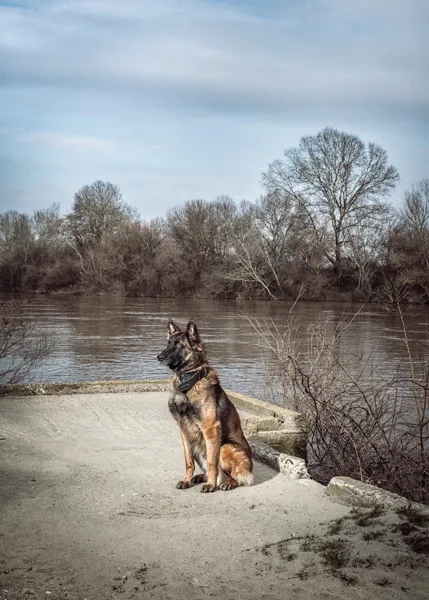
Julian Roeder. Tracking Dog, Northern Greece, 2012, Archival Pigment Print, 152 x 109 cm

Julian Roeder’s Mission and Task (2012) consists of images of the technology and people working in contemporary surveillance at the border of the Schengen zone.

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie


Mari Bastashevski & Privacy International. Private Interests. 2014

Mari Bastashevski & Privacy International presented photographs and evidence of Central Asian governments use of electronic surveillance technologies to spy on activists and journalists, domestically and abroad, in order to clamp down on dissent and to reinforce their political
control. This installation included the stories of several Uzbekistan journalists and lawyers who were surveilled, intimidated, and threatened with prison for their work. This project is covered in detail in this PDF.

Stasi / Facebook / Big Data DAAD Day 27 – Exhibits on surveillance at Museum für Fotografie


Hasan Elahi. Thousand Little Brothers.

In response to questioning by the FBI in suspicious post-9/11 USA, Hasan Elahi created Thousand Little Brothers which includes 32,000 photographs he made during his ongoing project to give the FBI every detail of his life, especially the mundane.

Both exhibitions are up until 2 July, 2017.

Stasi / Facebook / Big Data DAAD Day 26 – Gedenkstätte Berlin-Hohenschönhausen

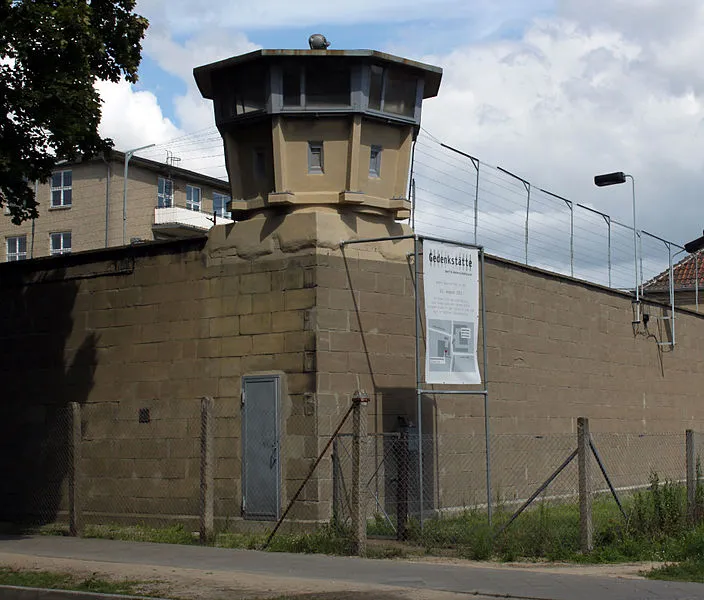
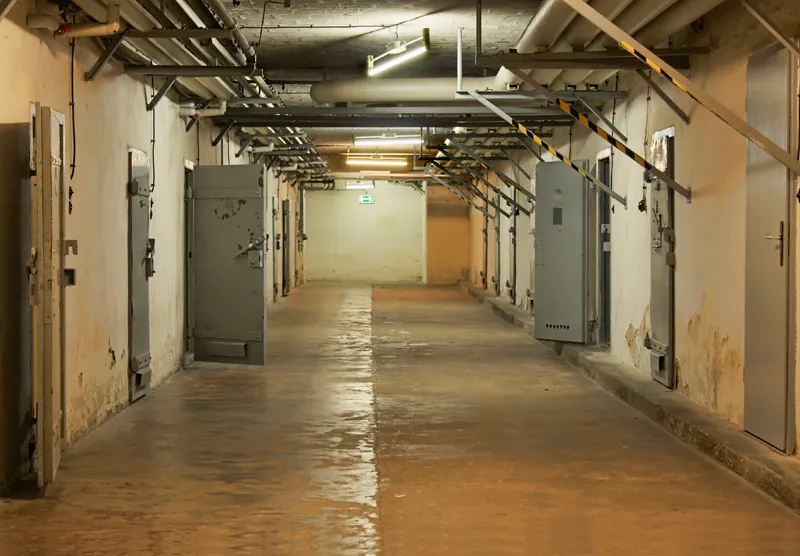
This week has been full of work on this project, including research in the BStU reading room, and making photographs at the archives at the former headquarters and the Stasi Museum. Today, for the first time, I visited The Memorial to Berlin-Hohenschönhausen, a large former prison complex which includes a former Stasi detention and interrogation center. Berlin-Hohenschönhausen began as a Nazi barrack camp for prisoners of war during WWII. After the fall of Nazi Germany it was used by the Soviet NKVD (the secret police) as a camp for interning political prisoners and former Nazis.

Stasi / Facebook / Big Data DAAD Day 26 – Gedenkstätte Berlin-Hohenschönhausen

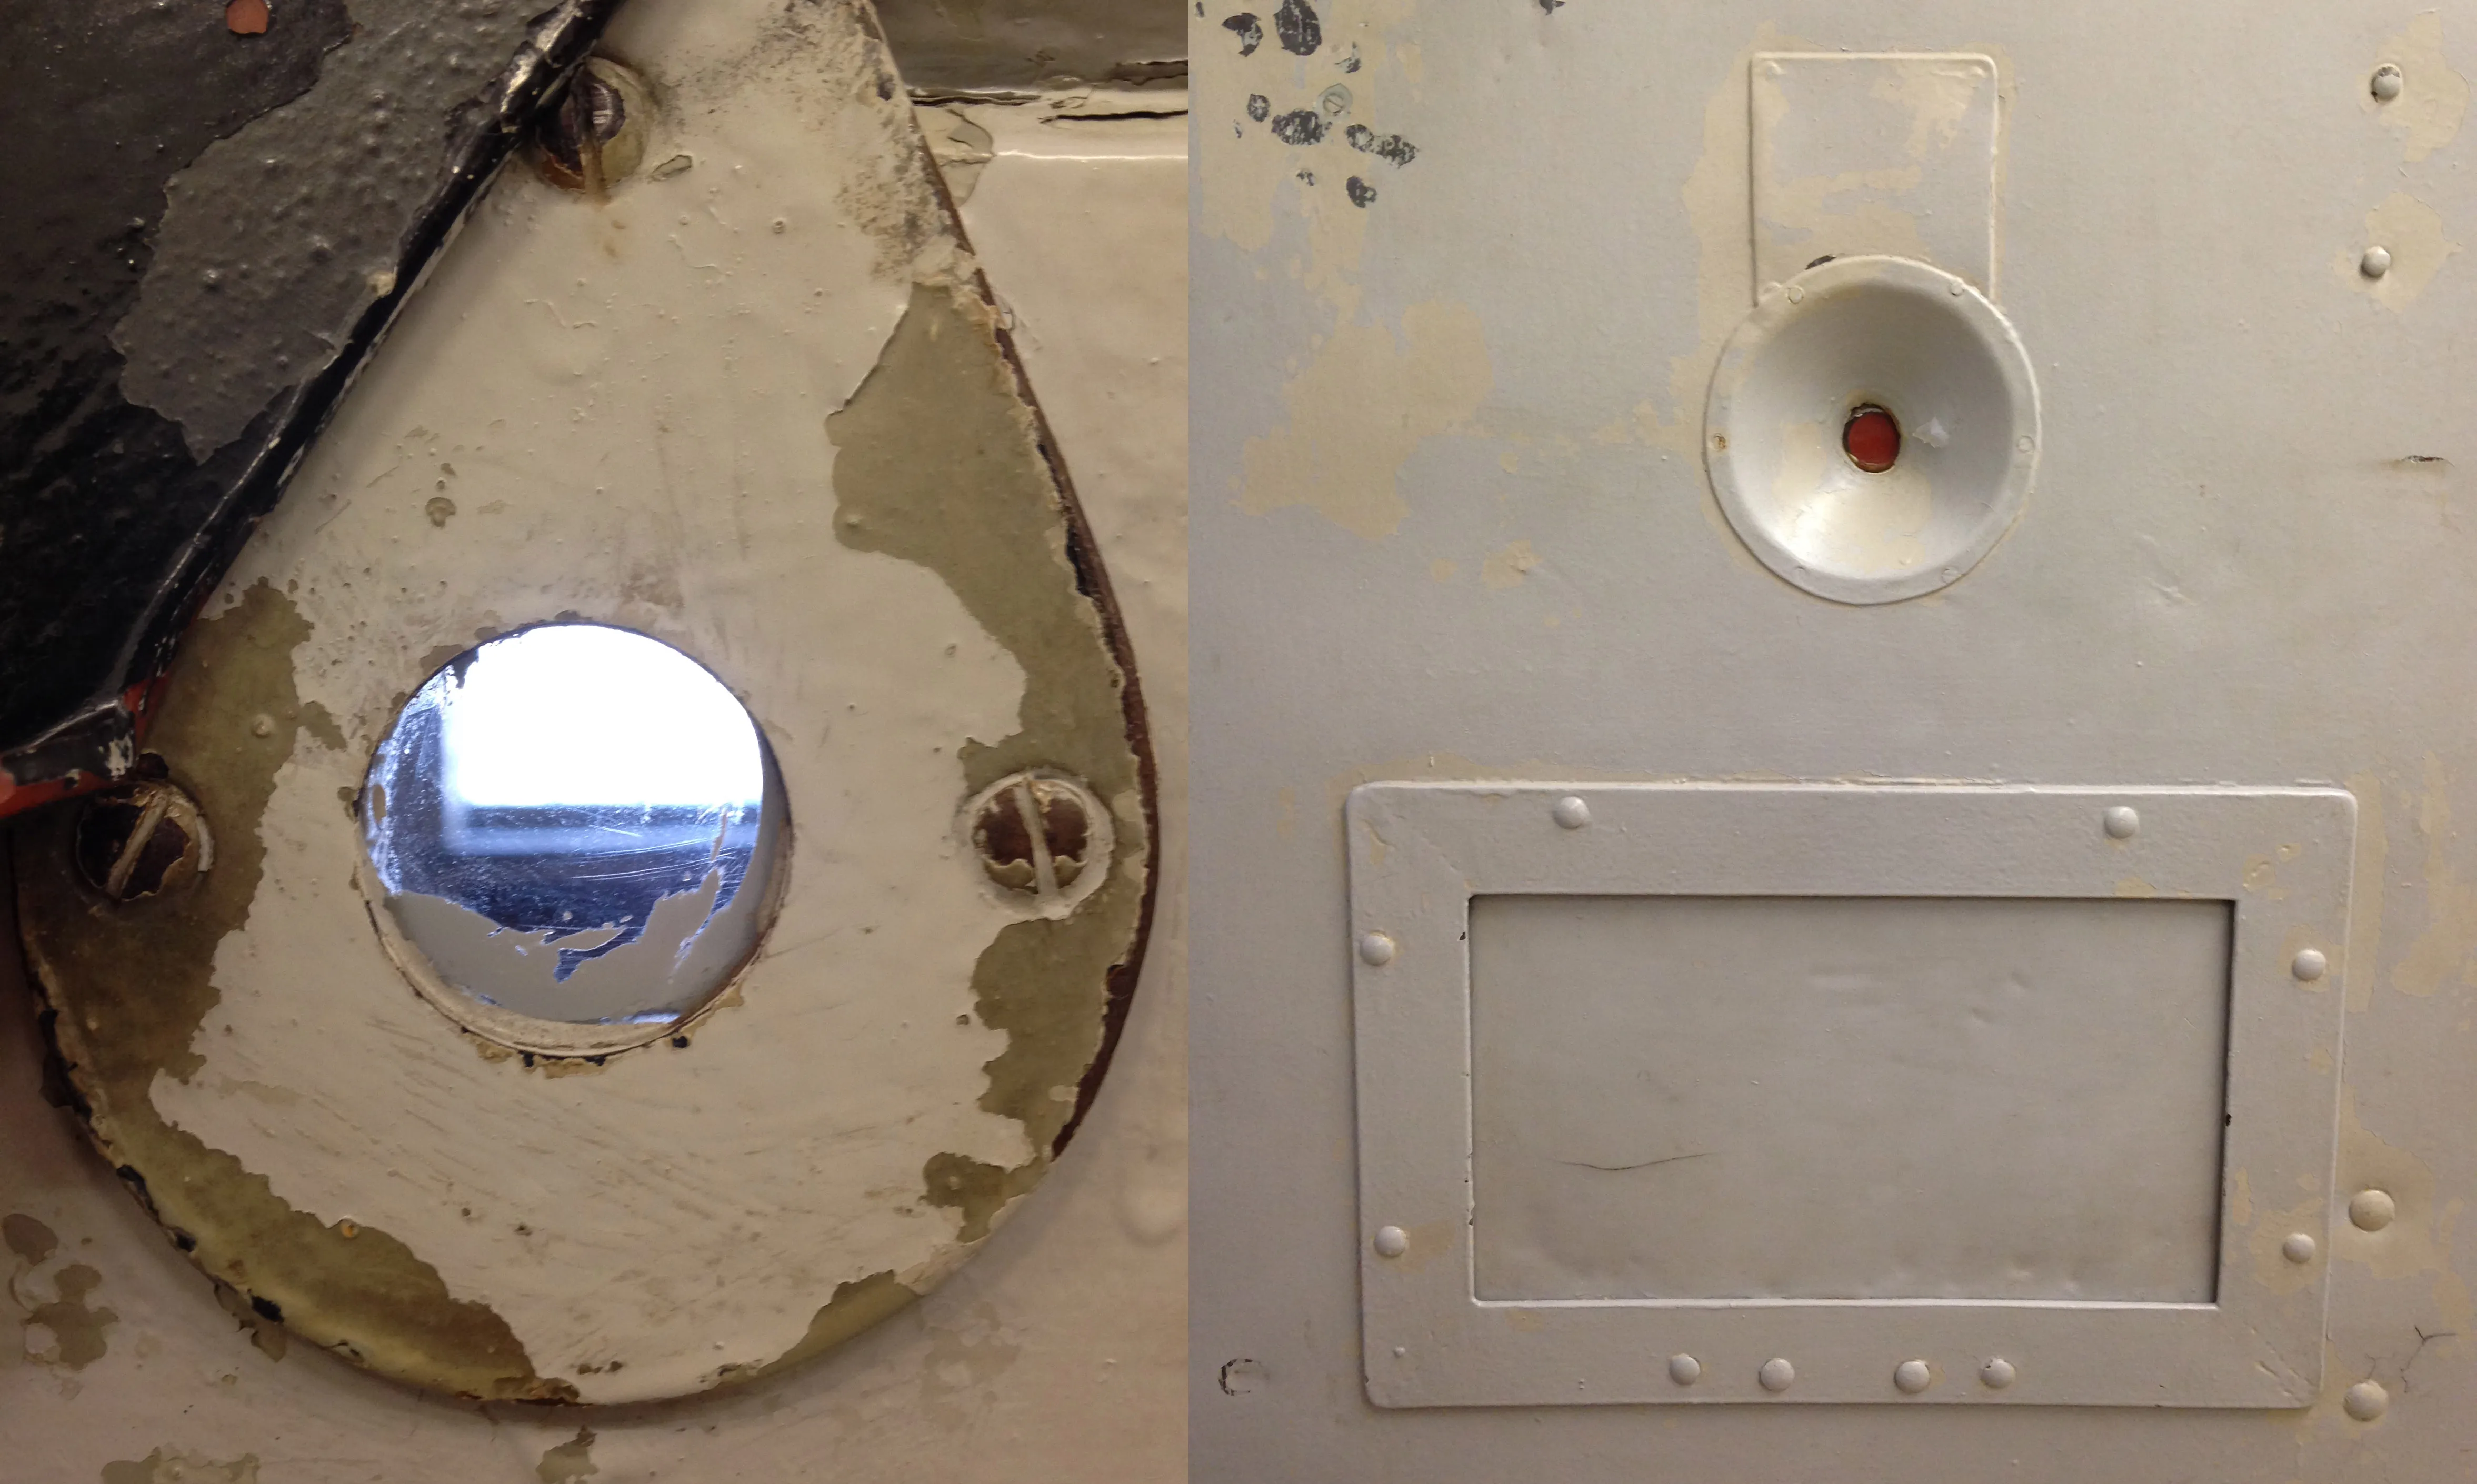
The facility was taken over by the GDR Ministry for State Security (MfS) in 1951. For nearly 40 years the MfS used part of it as a secret (it was not located on official city maps) detention and interrogation center. Here, over 10,000 political prisoners were detained and subjected to physical and psychological torture to gain information in preparation for sentencing by the courts.

Stasi / Facebook / Big Data DAAD Day 26 – Gedenkstätte Berlin-Hohenschönhausen

Stasi / Facebook / Big Data DAAD Day 26 – Gedenkstätte Berlin-Hohenschönhausen

The MfS staff who worked here were trained at the “Stasi University” (Potsdam) to destabilize and destroy the personality of their prisoners. Their methods included sleep deprivation, isolation, and other harassment that left the prisoners psychologically damaged. They also made references to prisoners’ loved ones, spouses and children, in order to coerce confessions and encourage cooperation.

Stasi / Facebook / Big Data DAAD Day 26 – Gedenkstätte Berlin-Hohenschönhausen

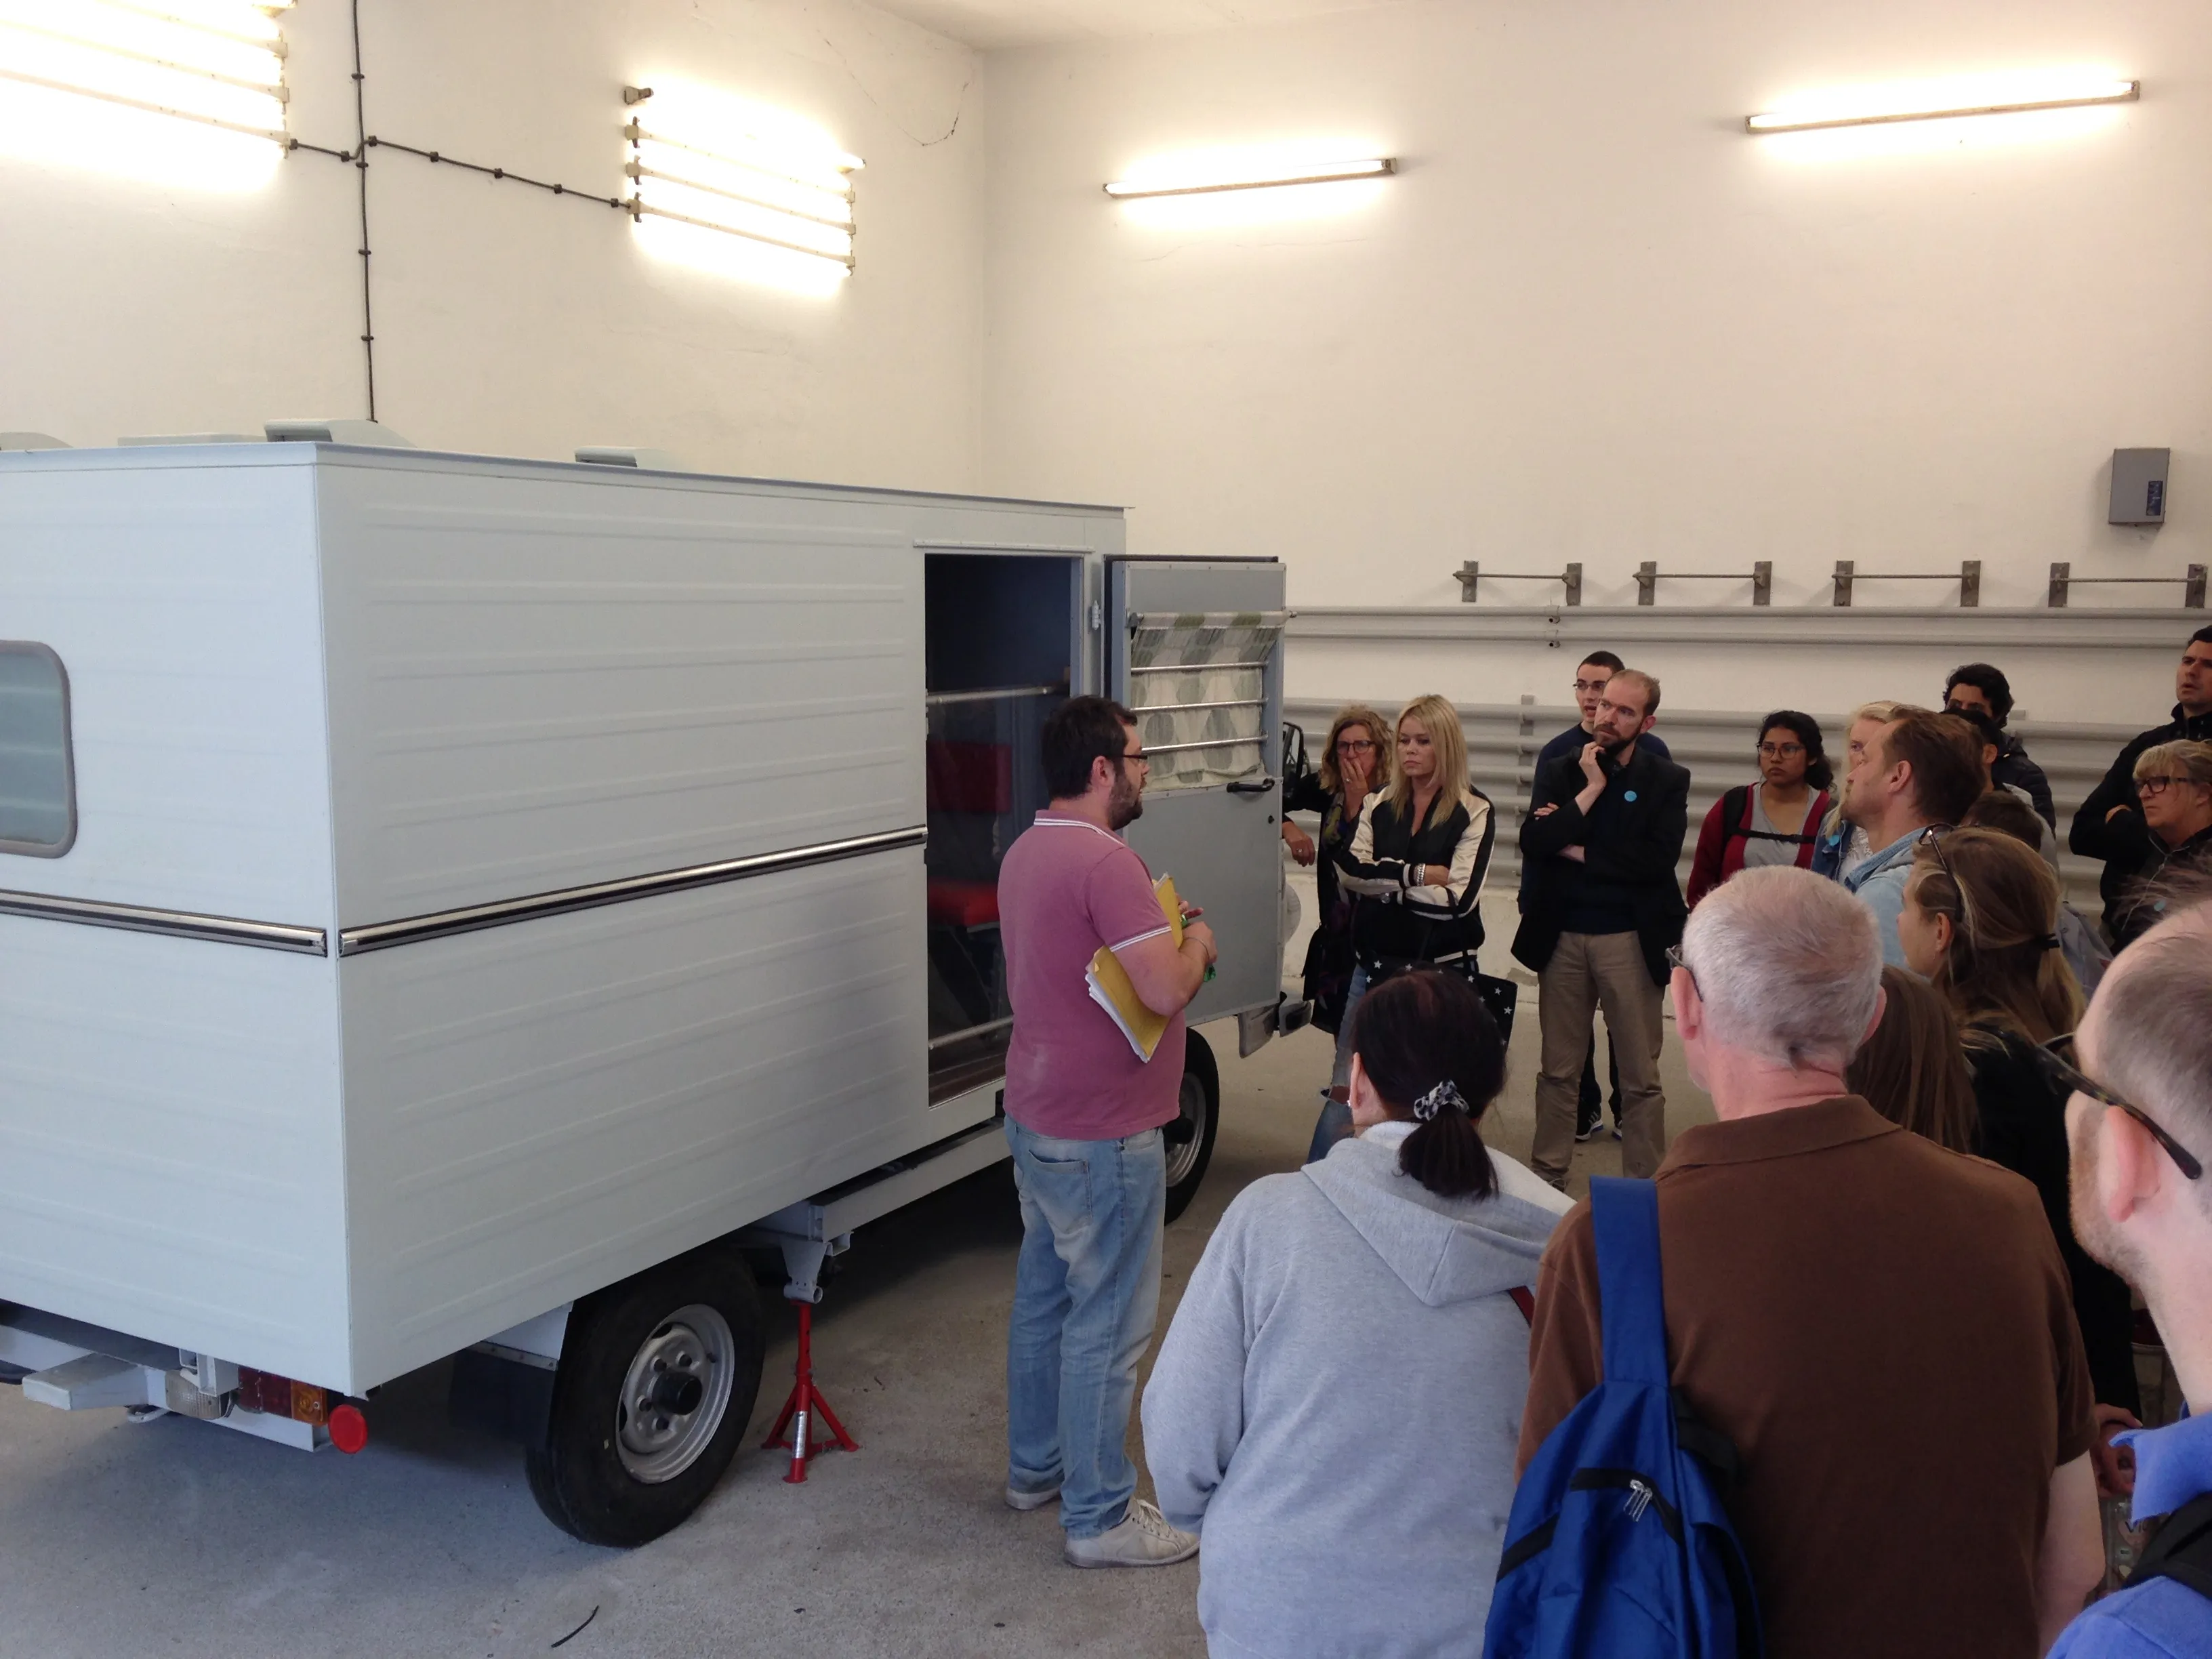
The methods for social isolation were particularly effective. Prisoners were often kidnapped and placed in a cage inside a van disguised as a delivery vehicle. The vehicle would drive around endlessly to disorient the prisoner and then arrive at a special closed-off garage in the detention center.

Stasi / Facebook / Big Data DAAD Day 26 – Gedenkstätte Berlin-Hohenschönhausen

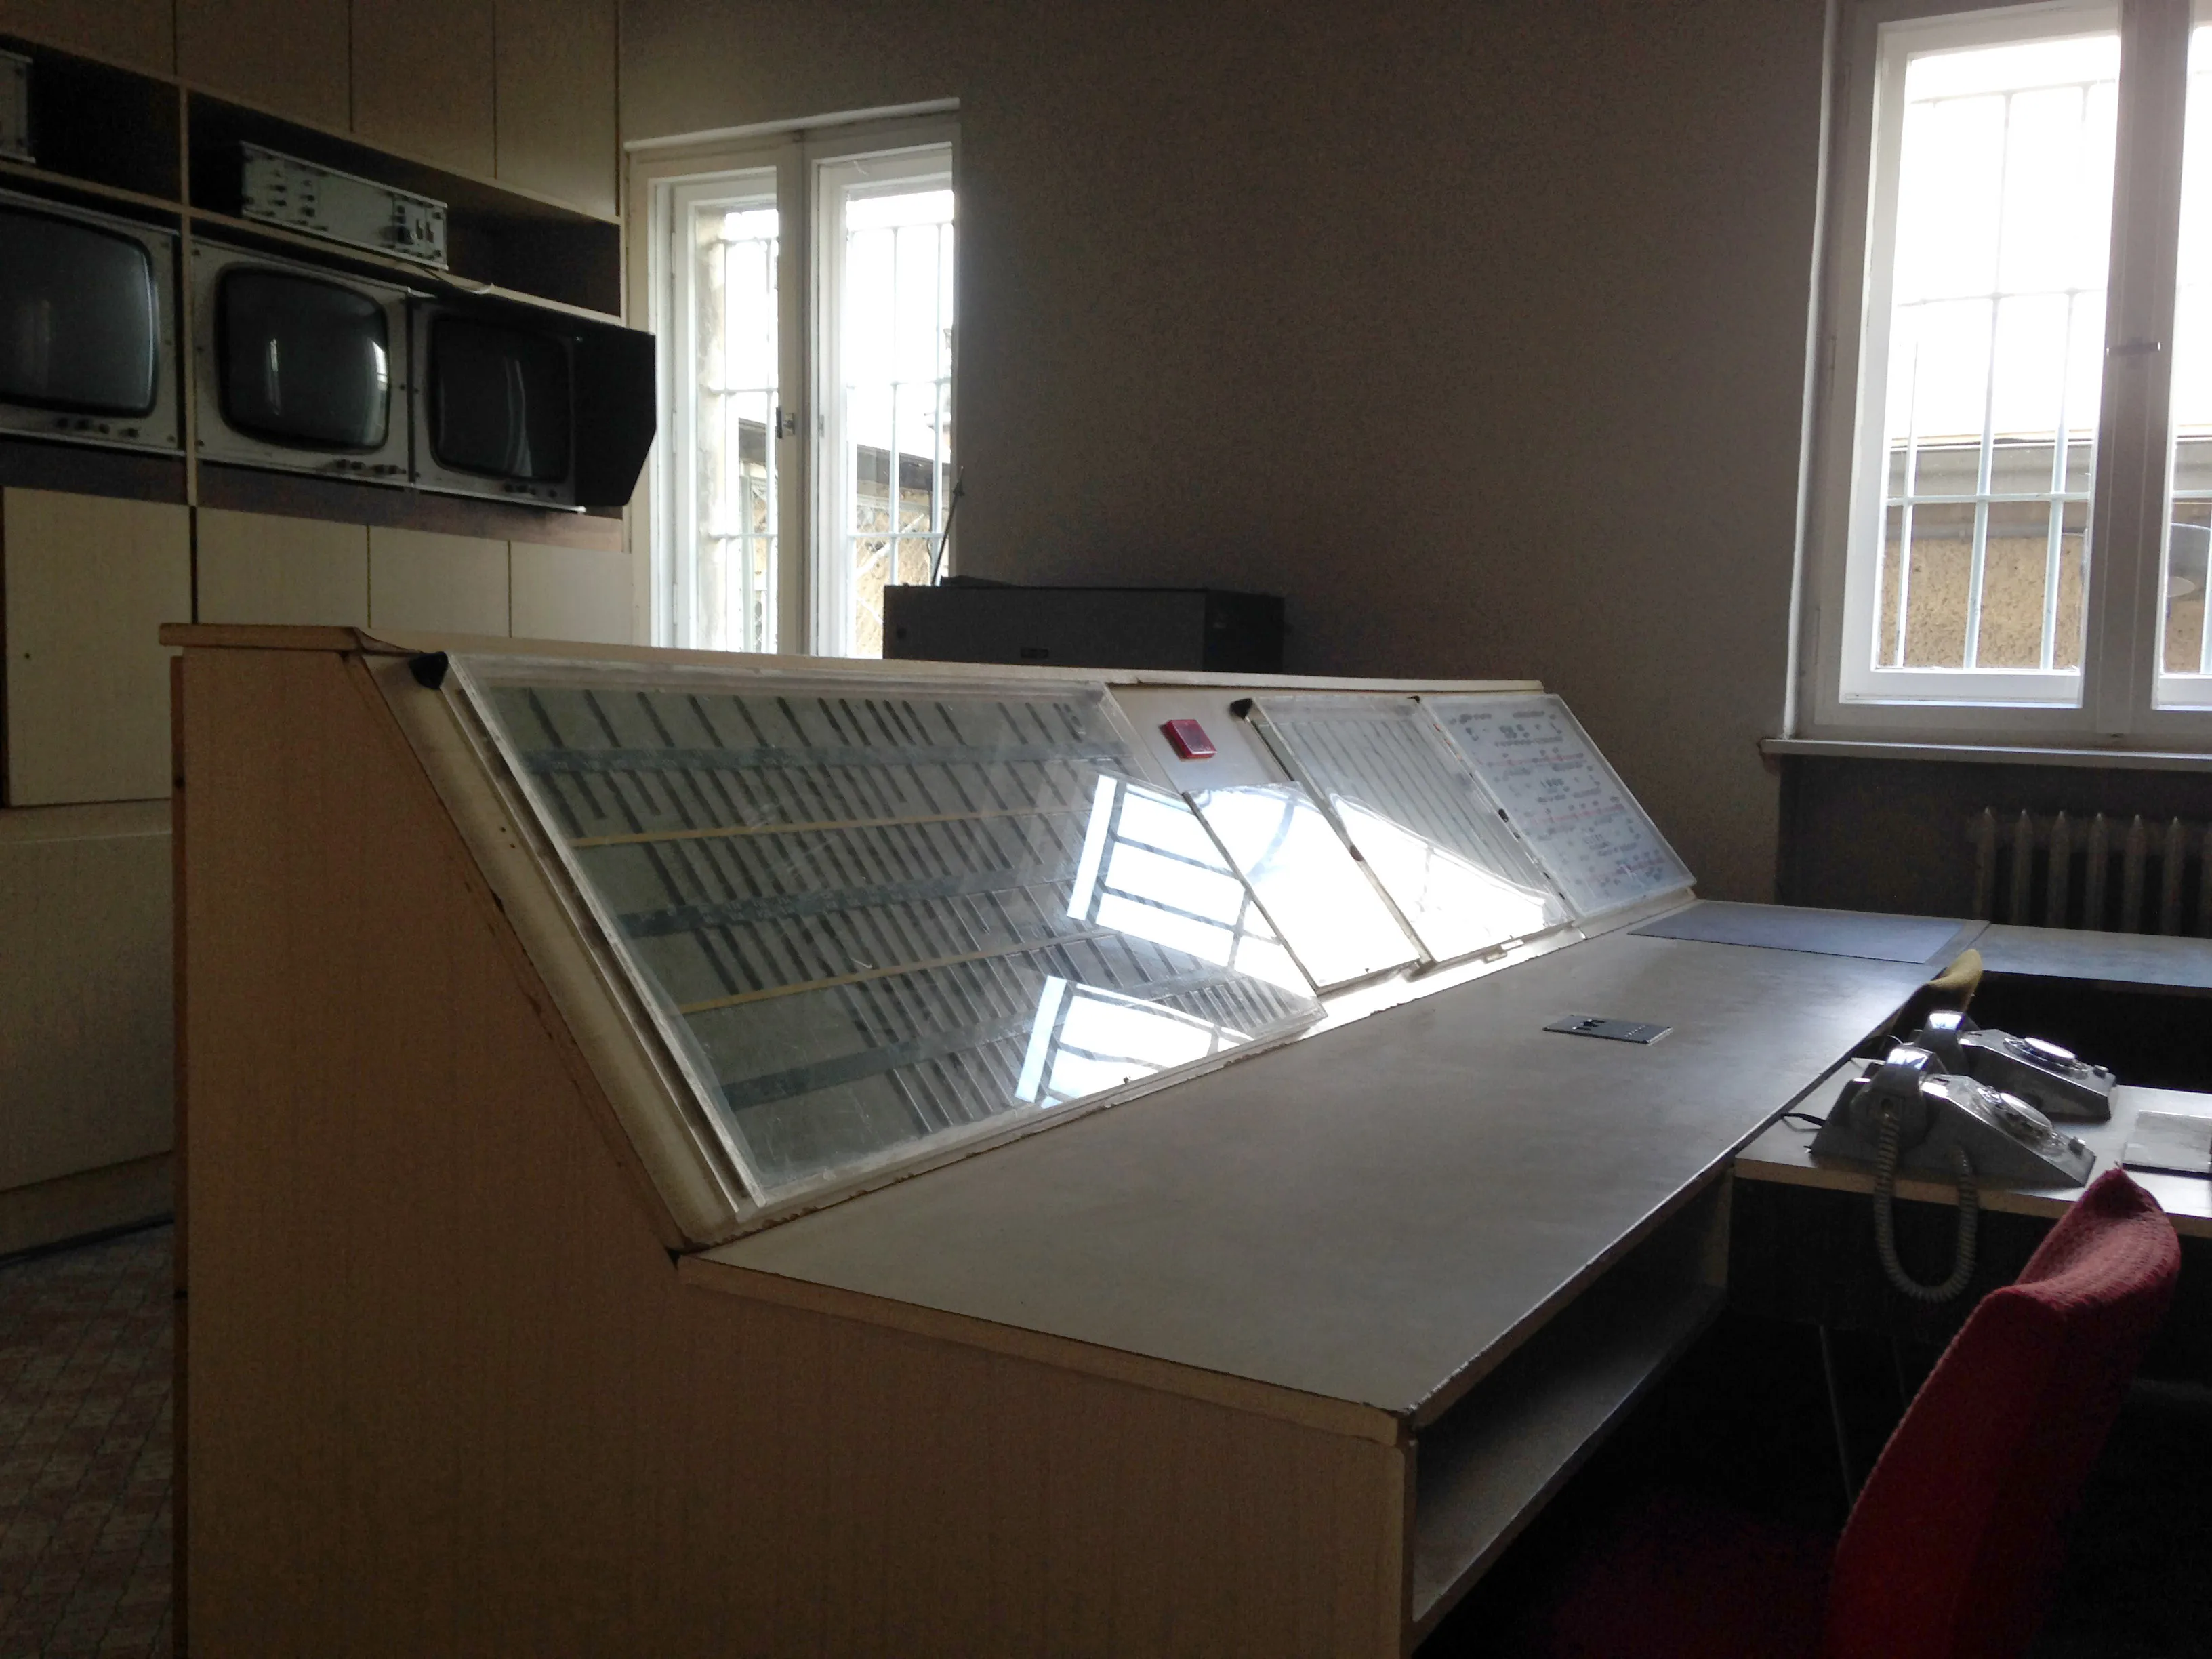
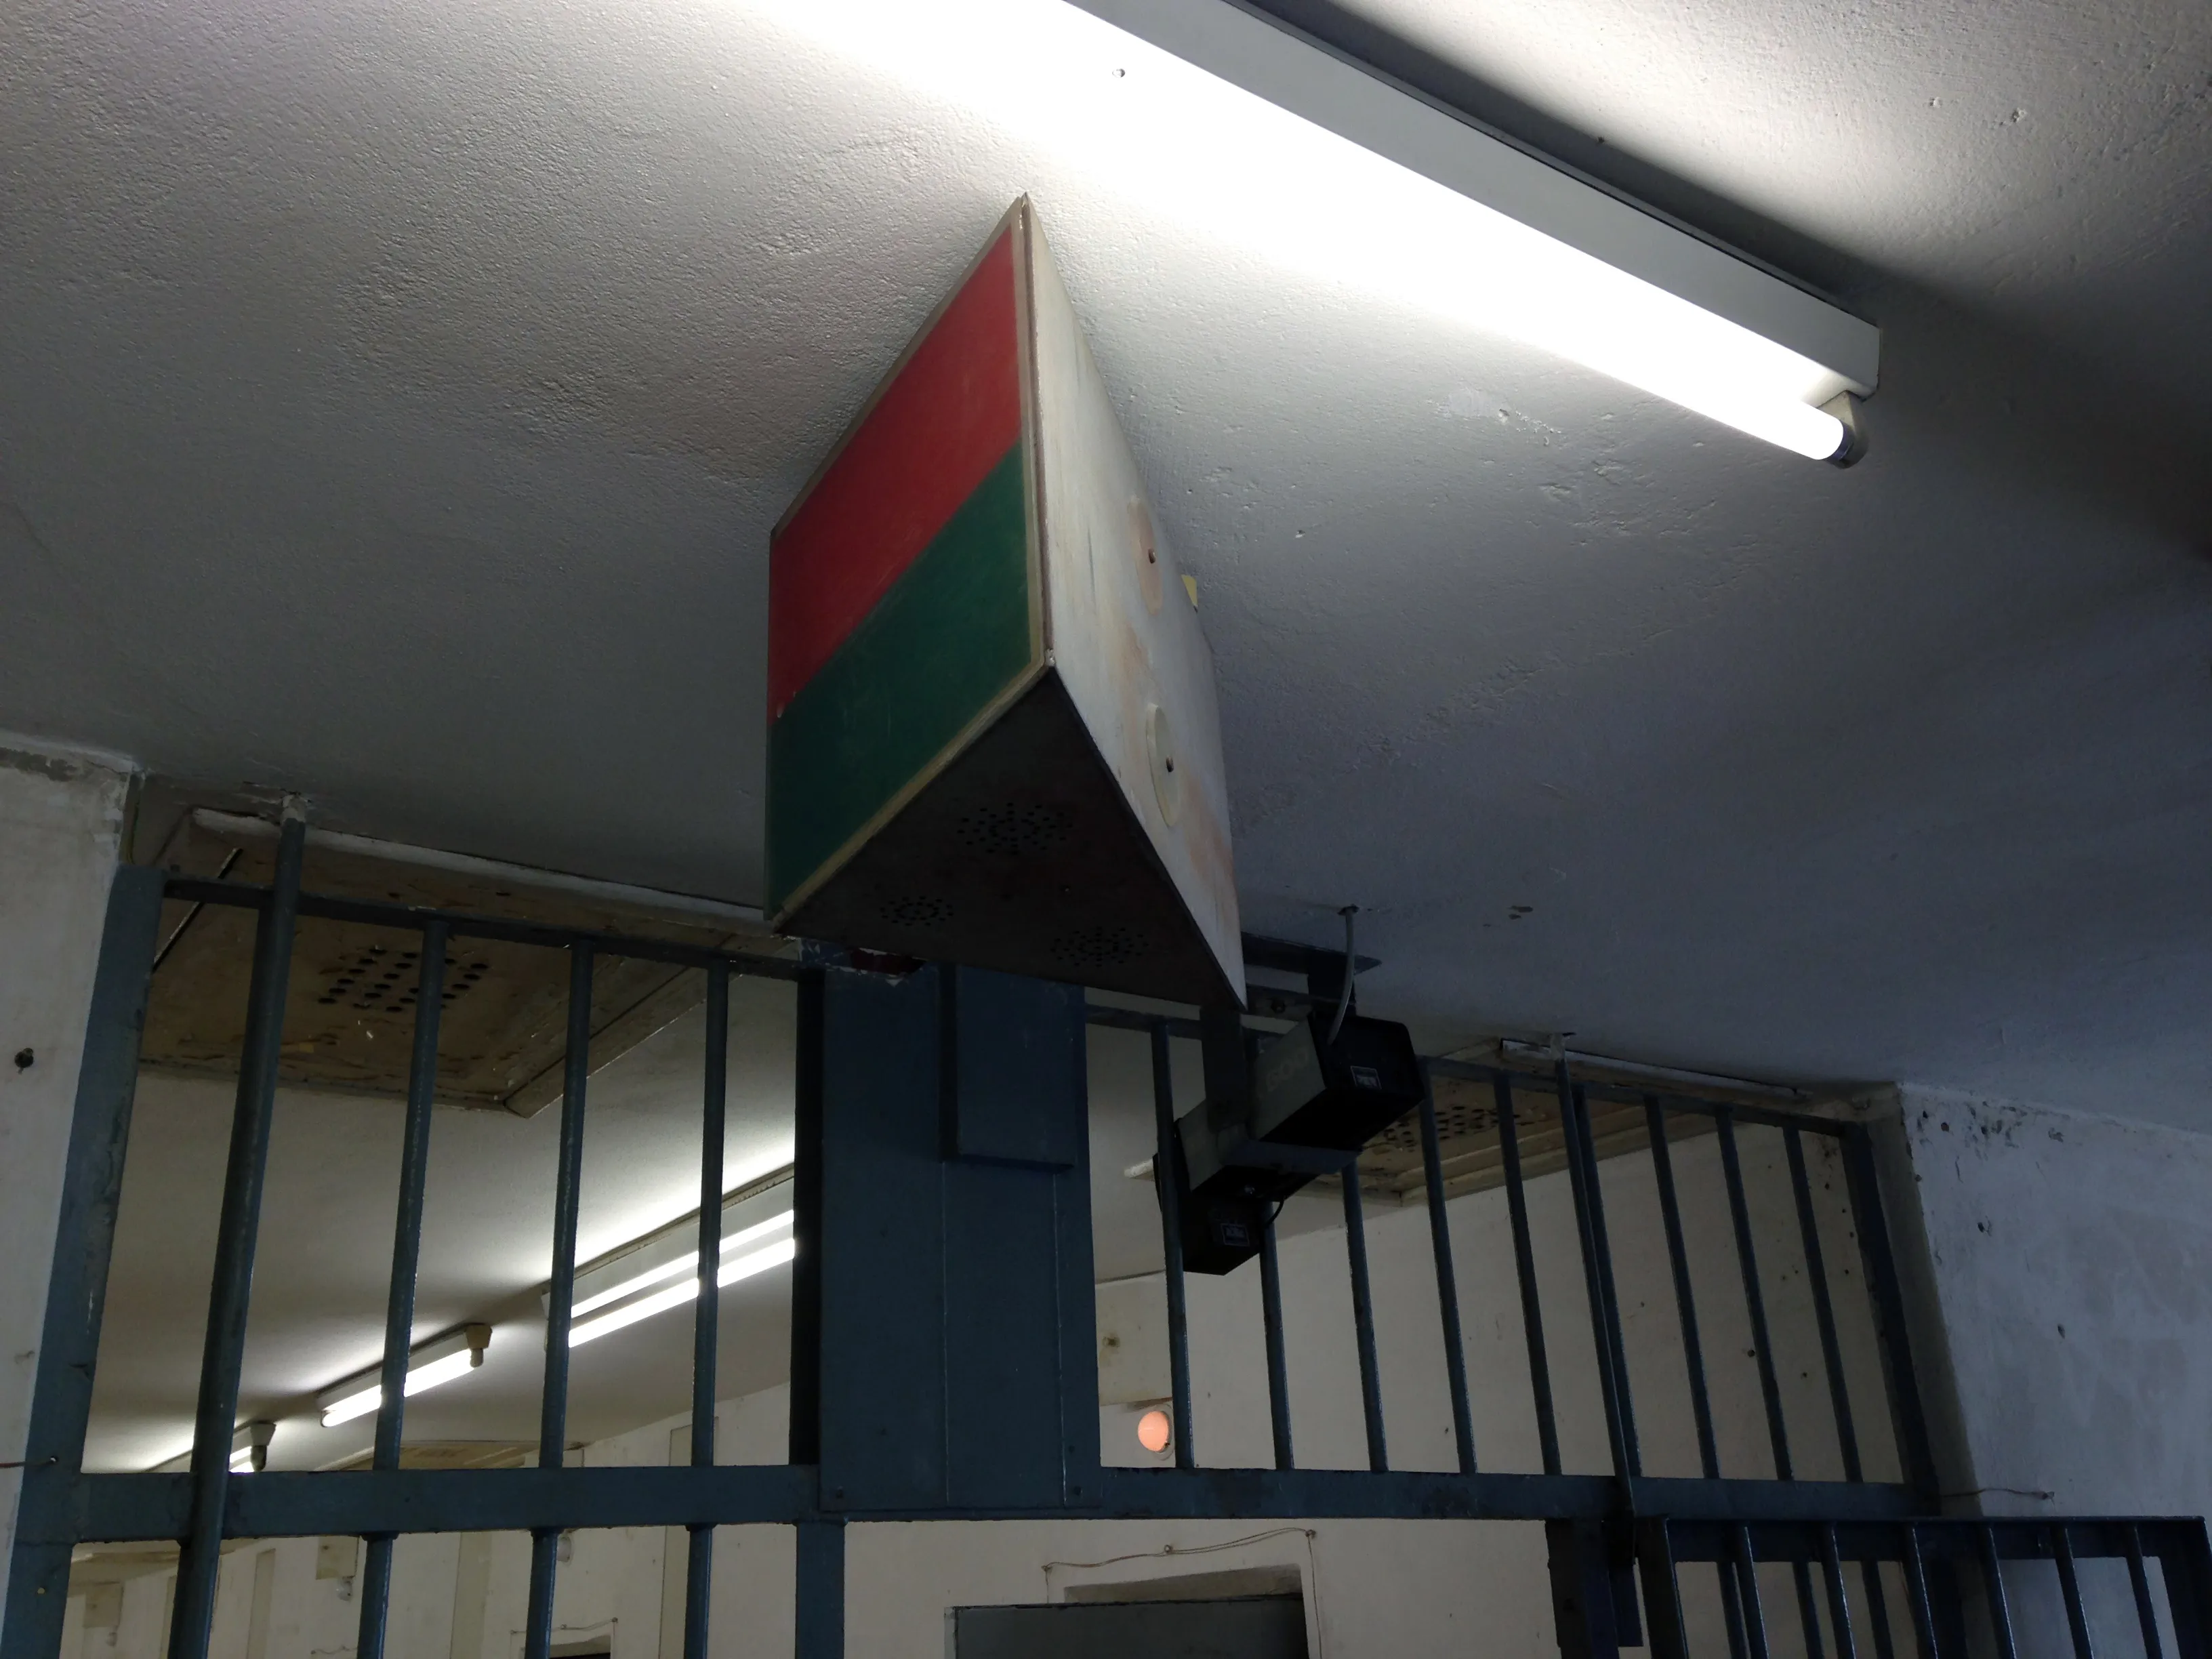
Once inside the buildings an elaborate series of electronic circuits controlled red and green lights in the hallways to direct the flow of prisoners and make certain they would never have the chance to encounter one another.

Stasi / Facebook / Big Data DAAD Day 26 – Gedenkstätte Berlin-Hohenschönhausen

This last note offers an important comparison to today’s social networks and surveillance capitalism methodologies. In social networks, the organization benefits from the flow of information between participants. They want to stimulate their users to interact and continue generating profit by using the site, producing data, and viewing ads. The Stasi’s torture of political prisoners, on the other hand, intentionally removed all stimulation and human contact. The sensory deprivation and isolation that prisoners experienced in their cells dehumanized, weakened, and prepared them to give up information the Stasi wanted.

Our information society has transformed the way we think about private information. While we freely give it up in exchange for social capital, companionship, and the serve the impulse to communalize our experiences, it does not mean that the social networks and corporations who deal in that data are not responsible when our information is misused. The recent revelation that the U.K. defense contractor turned data dealer, BAE, sold cyber-surveillance tools to Arab states is proof of this. BAE peddled their sophisticated total surveillance system, with a generic yet telling name, “Evident” (a marketing variation of “criminal evidence”?) to six Middle Eastern countries previously criticised for repressing their citizens. These countries can now use the tool to scour the internet for sites, blogs, and social networks for information on anyone they consider an opponent. A former BAE employee put it like this:

“You’d be able to intercept any internet traffic,” he said. “If you wanted to do a whole country, you could. You could pin-point people’s location based on cellular data. You could follow people around. They were quite far ahead with voice recognition. They were capable of decrypting stuff as well.”

Digital information is inherently insecure. It’s easy to surveill, copy, and duplicate by design. Equally, it is easy to reimplement a surveillance software system that is designed to be sold to do so. The Stasi was a terrible organization, but their work was generally confined to the GDR. There was collaboration across the USSR satellite police organizations, but their work wasn’t on a global market. Looking back at the Stasi provides this evidence; The employees and stockholders of any company that benefits from the sale of such a system to inflict human rights abuses are as guilty as the Stasi employees who worked in the offices and never directly inflicted damage. Surveillance capitalism isn’t just about the profit generated by social network ads, it includes the manufacture and sales of systems like Evident, and all those who derive profit from such decentralized institutions.

Stasi / Facebook / Big Data DAAD Day 26 – Gedenkstätte Berlin-Hohenschönhausen

Stasi / Facebook / Big Data DAAD Day 25 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using hot air

Stasi / Facebook / Big Data DAAD Day 25 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using hot air


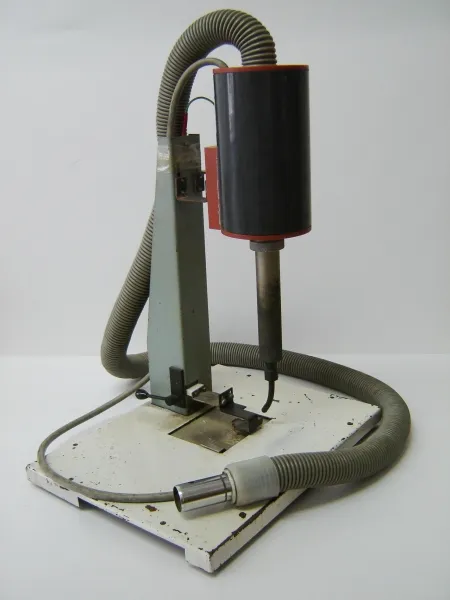
Heißluftgebläse. Credit: Museum in der Runde Ecke

The next artifact in my list is the “Heißluftgebläse”—a hot air blower constructed by the Stasi for opening envelopes and packages sealed with rubberized self-adhesive tape. Unlike the various steam methods the Stasi employed, which only worked on water-based glues and could potentially damage the contents of letters, this machine was used to focus hot, dry air directly to the flap in order to soften and release the adhesive.

Like other “hacked” machines constructed for postal surveillance the Stasi Operative-Technical Sector fashioned this blower using off the shelf, reused, and hand-made parts. In this case, they adopted a commercially-available vacuum cleaner to force air through a heating cartridge and down a steel tube towards a platform where workers laid envelopes. At the end of the tube there is a metal apparatus that could be used to focus the hot air and gently pry the envelope flap open. Impressively, the Runde Ecke index states this method be used to open up to 150 letters per hour.

Stasi / Facebook / Big Data DAAD Day 25 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using hot air


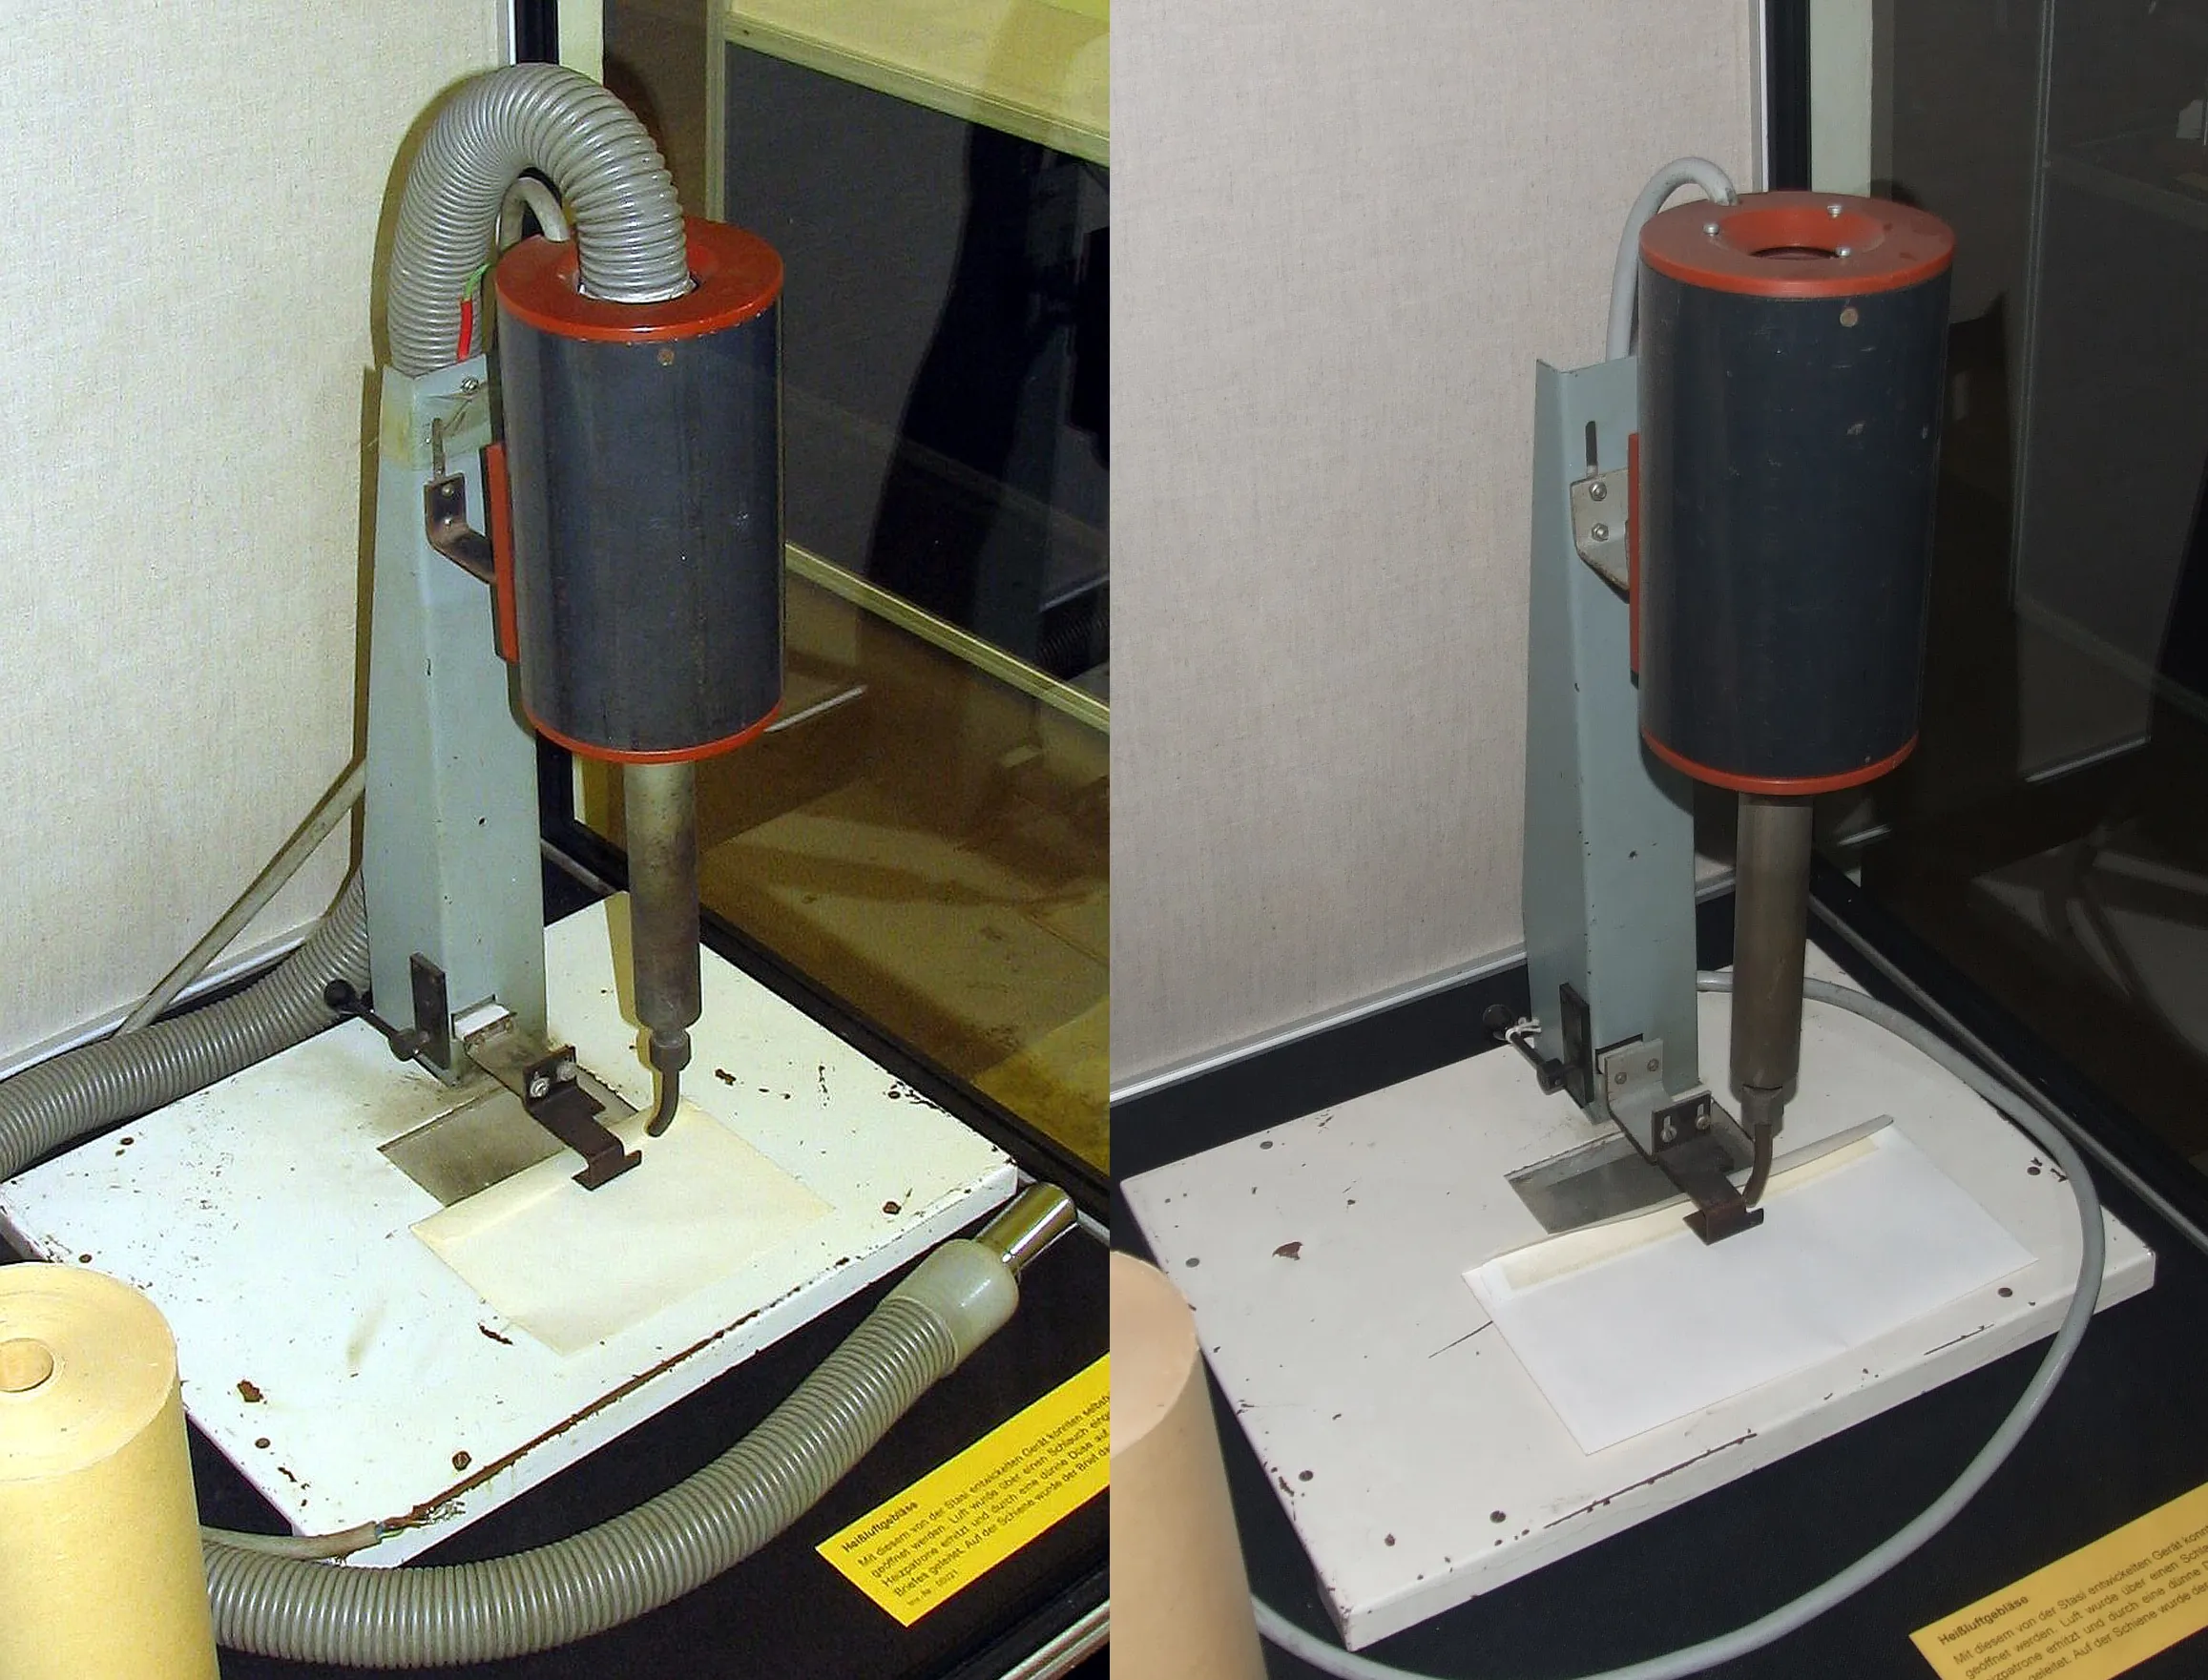
Heißluftgebläse. April and July Credit: Wikipedia user Appaloosa

I’m particularly interested in the different representations of this machine. In these two photographs, both posted by the same Wikipedia user in 2008 just months apart, it appears there were two separate machines on exhibit. This is suggested by comparing the scratches on the base and stand. Yet, while they are clearly different, they are strangely positioned in exactly the same location—an exhibition at the Museum in der Runde Ecke which contains objects found in the Leipziger district administration for state security (BVfS)—with other obvious differences. In the 22 April photo (left) the vacuum cleaner is still attached, showing how the machine was originally used. But in the 27 July image the vacuum and tape have been removed. Was it needed for cleaning in the museum? Where could it have gone? There are additional small differences that point to these being distinct machines, the most noticeable of which is that a different bracket is holding the heating apparatus.

It’s thanks to deviations like this that the telling of the story of Stasi postal surveillance continues to evolve. Aesthetic decisions that seem inconsequential—like a museum staff member replacing the device with the yellowing tape with the one that doesn’t look as disheveled—change how we are able to perceive the past. Here, those moments which make the economic and material constraints the Stasi OTS experienced while hacking and iterating across their analog surveillance devices become less clear. While, thanks to the BTsU we are fortunate to be able to dissect and interpret the methods of the Stasi, it is not possible to collect everything. This unfortunately obscures the parallels with our 21st century hacker culture that, like the Stasi, have grown into immense organizations intent on perfecting and perpetuating their power through surveillance.

  1. Heißluftgebläse zum öffnen von gummierten selbstklebenden Briefen (Inventory no. 00020). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 13, 2017.
  2. BStU. Die Stasi und das Postgeheimnis. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 24 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using cold steam

Stasi / Facebook / Big Data DAAD Day 24 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using cold steam


Credit: BStU

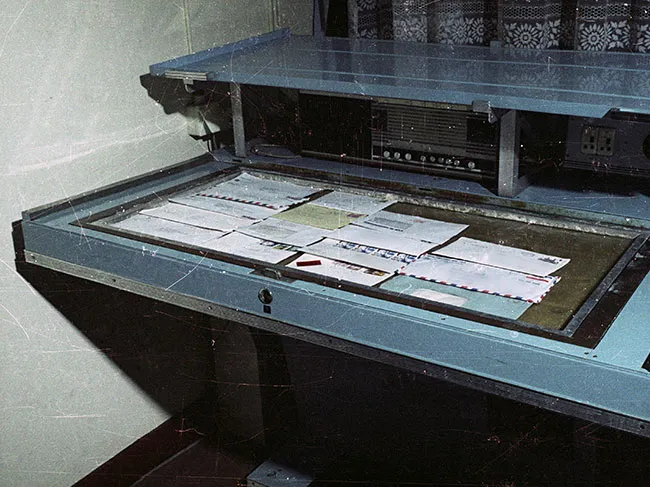
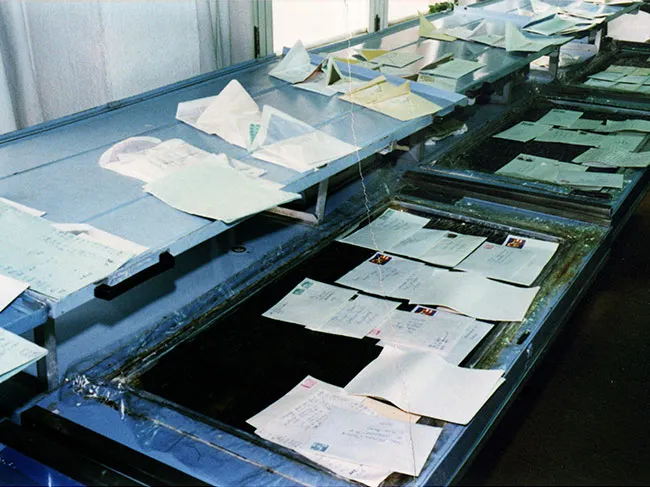
Since hot steam could damage sensitive contents like photographs, the Stasi used the C-83 (“Cellophan 83”) “cold steam” generating device to open those letters. Produced in Hungary, the C-83 used a special film (cellophane) stretched over a tray filled with distilled water. Up to 25 letters could be placed on the film, flaps down, so that when the water in the tray was heated to 50ºC the “cold steam” diffused through the film and dissolved the glue on the envelope flaps.

The procedure was time-consuming because cold steam dissolved the glue at a much slower rate than the hot steam method. Once the glue started to soften, workers had could only lift the letters off the foil for a short time in order to carefully open them using a special spatula.

Stasi / Facebook / Big Data DAAD Day 24 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using cold steam


Credit: BStU

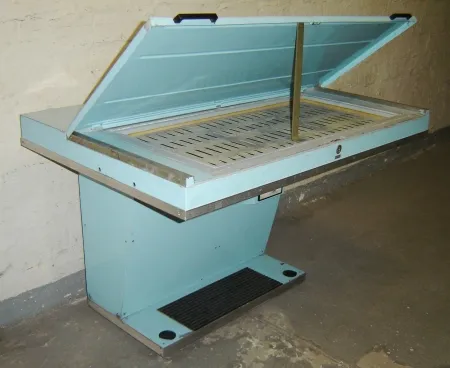
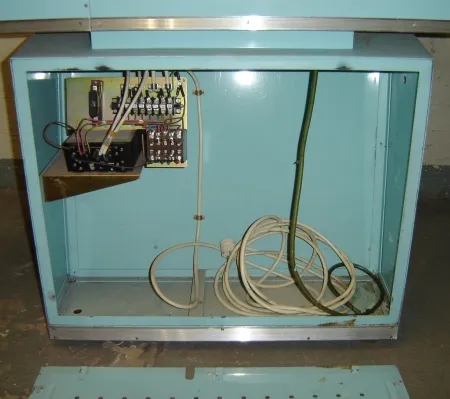
It is unclear if this is an original mass-produced device or is a product modified by the Stasi OTS. It is constructed of painted sheet metal, cast plastic, and other materials that suggest it was primarily constructed in a factory, though it is possible the Stasi made modifications to assist in letter-opening.

Stasi / Facebook / Big Data DAAD Day 24 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using cold steam


Credit: Museum in der Runde Ecke

Stasi / Facebook / Big Data DAAD Day 24 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using cold steam


Credit: Museum in der Runde Ecke

Stasi / Facebook / Big Data DAAD Day 24 – Automation in Stasi postal surveillance: Opening letters with sensitive materials using cold steam


Credit: Museum in der Runde Ecke

  1. Kaltdampf-Öffnungsgerät zum öffnen von Briefen (Zellofanbodengerät) (Inventory no. 00006). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 13, 2017.
  2. BStU. Die Stasi und das Postgeheimnis. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 23 – Automation in Stasi postal surveillance: Work Table for Hot Steam Opening System 532

Stasi / Facebook / Big Data DAAD Day 23 – Automation in Stasi postal surveillance: Work Table for Hot Steam Opening System 532


Credit: Museum in der Runde Ecke

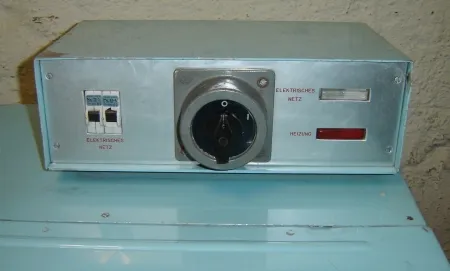
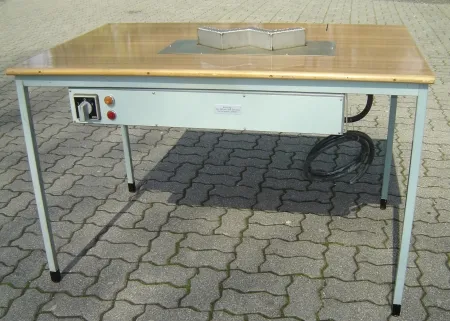
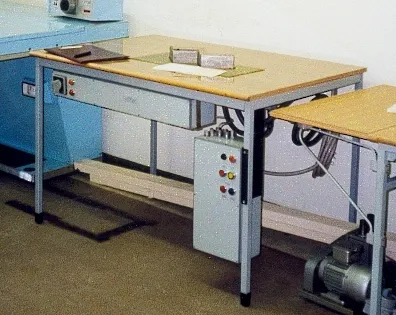
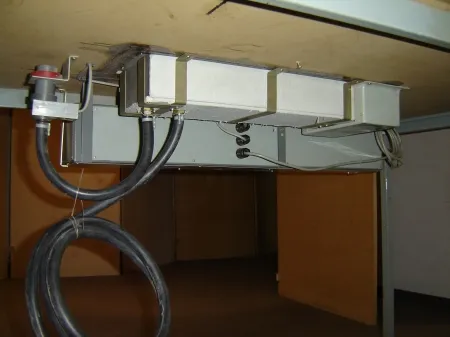
If the “W”-shaped, two-letter steam distribution grid was an “upgrade,” then the ultimate “deluxe” Stasi steam device for manually opening letters with hot water vapor is the “Arbeitstisch der Heißdampf-Öffnungsanlage 532” (English: Work Table for Hot Steam Opening System 532). This modular table was constructed for Department M by the Operational-Technical Sector (OTS) of the MfS in the late 1970’s for manually steaming open envelopes with water-soluble adhesives. The Museum in der Runde Ecke has two of these modified working tables. There is no information on whether “532” is the model number or series number (which would imply there were 531 other models!), and unfortunately I did not record the plate on the front last time in Leipzig, so I cannot confirm its contents until I return.

Stasi / Facebook / Big Data DAAD Day 23 – Automation in Stasi postal surveillance: Work Table for Hot Steam Opening System 532


Credit: Museum in der Runde Ecke

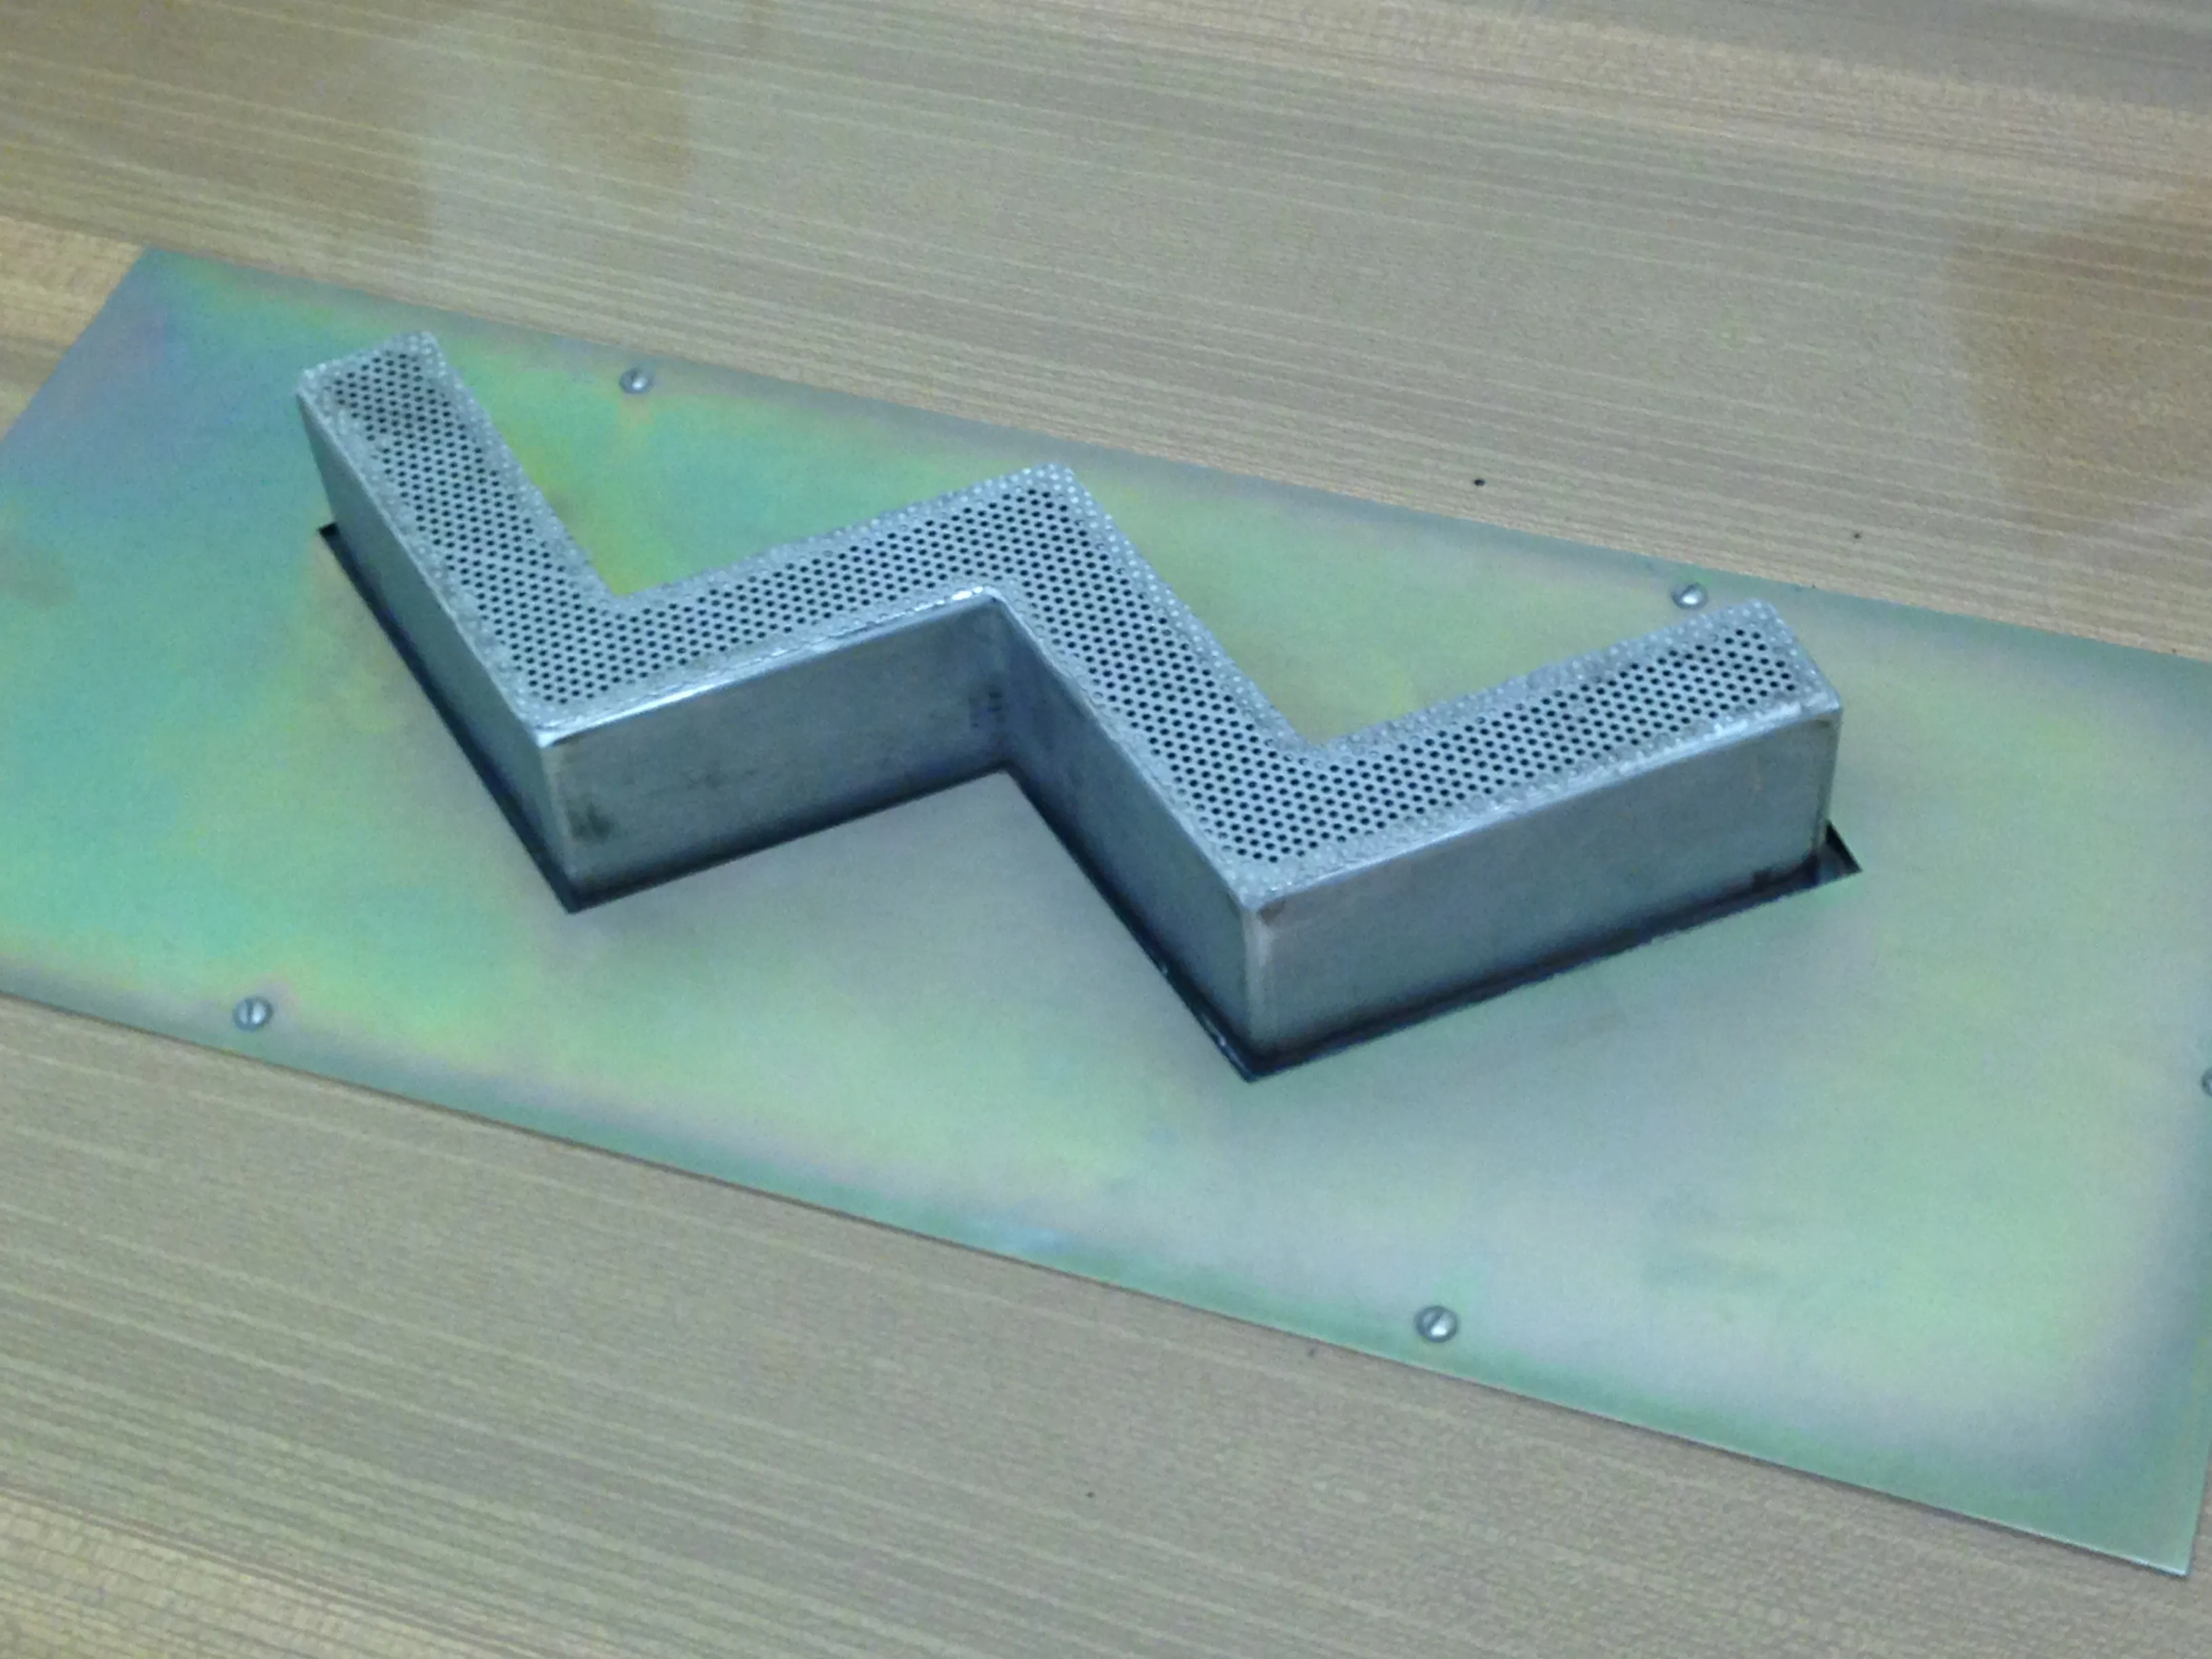
One of the Runde Ecke tables has its own power supply which could be connected to up to three other units to supply power in series (a.k.a. “daisy chaining”). In the center of each table is a “W”-shaped vapor dispersion grid on which two envelopes could be placed. Under the plate is the steam generator, which contained a heater, water storage, and float. While in operation a storage vessel for distilled water was placed underneath. The unit was operated by turning the rotary switch (positions: 0 = “off”, 1 = “pause”, and 2 = “full”) on the attached control panel. Two control lights indicated the operating state of the table, a yellow light which lit when the table was on, and a red light which illuminated when the float inside the steam generator detected that the water was low.

Stasi / Facebook / Big Data DAAD Day 23 – Automation in Stasi postal surveillance: Work Table for Hot Steam Opening System 532


Credit: Museum in der Runde Ecke

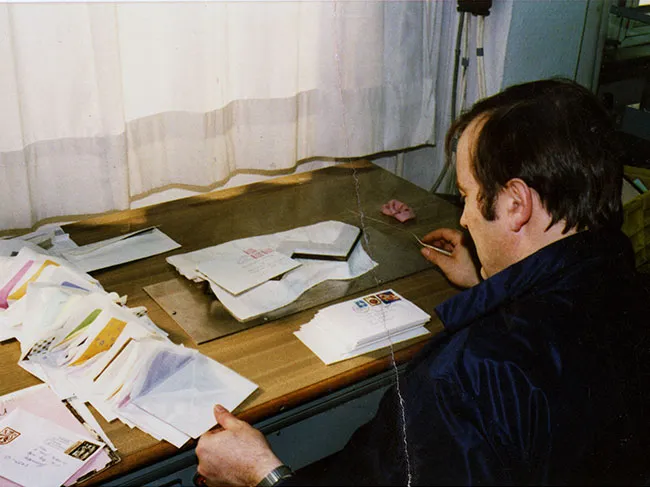
To use the table MfS staff turned the steam generator dial to the “full” position. This activated the heater inside the water receptacle. Once the water reached the correct temperature and began to evaporate the staff placed the flap of the letters on the angles of the W-shaped mesh grids. The vapor, which could reach temperatures of to 100ºC, emerged from the W and dissolved the adhesive. A towel was stretched over the opening to prevent water buildup. Up to 100 letters (between private citizens of the GDR) per hour could be opened on this device.

Stasi / Facebook / Big Data DAAD Day 23 – Automation in Stasi postal surveillance: Work Table for Hot Steam Opening System 532


Stasi staff using the “Work Table for Hot Steam Opening System 532.” Credit: BStU, MfS, Dept. M, Fo 0031, figure 0003

Of the devices I’ve examined so far, this table has little outright evidence that it contains modified parts. Unlike the “hacker aesthetic” of other devices, attention has been given to the various additions to the table to match them to the original. The control panels use commercially-available switches and indicators and are constructed with sheet steel and painted to match the bluish grey steel of the tables. The “W” mesh steam dispersion grid appears to be constructed of aluminum or another treated metal that would not oxidize, and is attached to the table using a plate with measured and symmetrical fasteners. Like the Stasi organization itself, which over time refined their methods according their ideology and what was available, the sharp edges and reused parts on this transformed table are concealed to match the professionalism, efficiency, and attention to detail with which the workers were expected to perform their tasks.

Stasi / Facebook / Big Data DAAD Day 23 – Automation in Stasi postal surveillance: Work Table for Hot Steam Opening System 532


Credit: Owen Mundy

  1. Work Table for Hot Steam Opening System 532 (Inventory no. 00007). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 10, 2017.
  2. Work Table for Hot Steam Opening System 532 (Inventory no. 00354). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 10, 2017.
  3. BStU. Die Stasi und das Postgeheimnis. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 22 – Automation in Stasi postal surveillance: Aufdampftopf

Stasi / Facebook / Big Data DAAD Day 22 – Automation in Stasi postal surveillance: Aufdampftopf


Credit: Museum in der Runde Ecke

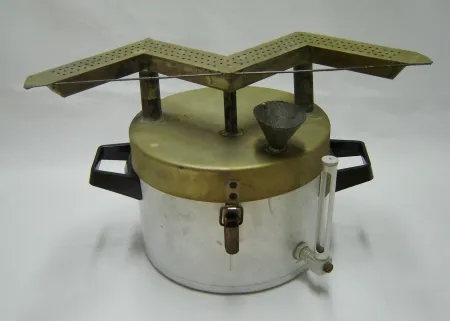
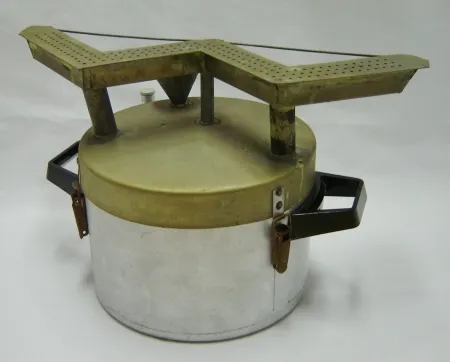
Like other devices constructed in the 1970’s and ‘80s by Department M and the Stasi OTS, this “Aufdampftopf” (“steam pot”) was fashioned using a basic household appliance as a starting point. Starting with a “cooking pot,” as it’s called in the Museum in der Runde Ecke index, the vessel was altered with a tight lid so it could be used to heat water (added via the attached funnel) and generate, collect, and disperse steam for opening letters.

The “W” shape of the vapor dispersing grid on top corresponds to the adhesive edges of, not one, but two envelopes placed end to end on the mesh. Presumably an administrator or other coworker made a human mechanical observation in the spirit of efficiency, suggesting that if the grid was expanded then workers could open two envelopes at once.

Like the Kleindampfentwickler with vapor dispersion grid on its top, the Dampfentwickler made from a steam pot also uses copper tubes and plating in its construction. Likewise, the steam pot additions exhibit a DIY aesthetic that contrasts with the mass produced original object. The copper, again chosen for its malleability and capacity to withstand water, shows signs of use in its darkening patina. It gives the steam pot the appearance of a prop for a dystopian science fiction film, or at least a reference to a real thing, inspiring one to think of a steampunk look popular among cosplayers.

Stasi / Facebook / Big Data DAAD Day 22 – Automation in Stasi postal surveillance: Aufdampftopf


Credit: Museum in der Runde Ecke

The Stasi’s practice of taking bits and pieces from whatever was available might have been based on scarcity given the economic constraints in communist GDR, but their hacked outcomes have a specific “remix aesthetic,” to borrow the term Eduardo Navas uses in his book Remix Theory: The Aesthetics of Sampling. Specifically, the Stasi’s reuse and appropriation of objects and materials towards utilitarian ends expresses itself in the same way the “sampling” of a DJ or musician might. Given the motivations for, uses of, and choices in construction of this device—to secretly open personal communications between individuals and examine their contents (which of course happens on the part of governments and corporations nowadays)—an art historian or anthropologist might term this a classic example of “early hacker”.

  1. Steam generator for opening letters (Inventory no. 00042). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 21 – Automation in Stasi postal surveillance: Kleindampfentwickler with nozzle

The Museum in der Runde Ecke in Leipzig has an amazing collection of devices found in the Leipziger district administration office (BVfS) during the dissolution of the Stasi. These are listed online in a thorough index with photos and descriptions. Their images are much better than those I was able to make through the glass of their museum displays, and while I’ve contacted the Citizen’s Committee about making new ones, they hopefully won’t mind if I reproduce some of them here in the meantime.

Stasi / Facebook / Big Data DAAD Day 21 – Automation in Stasi postal surveillance: Kleindampfentwickler with nozzle


Credit: Museum in der Runde Ecke

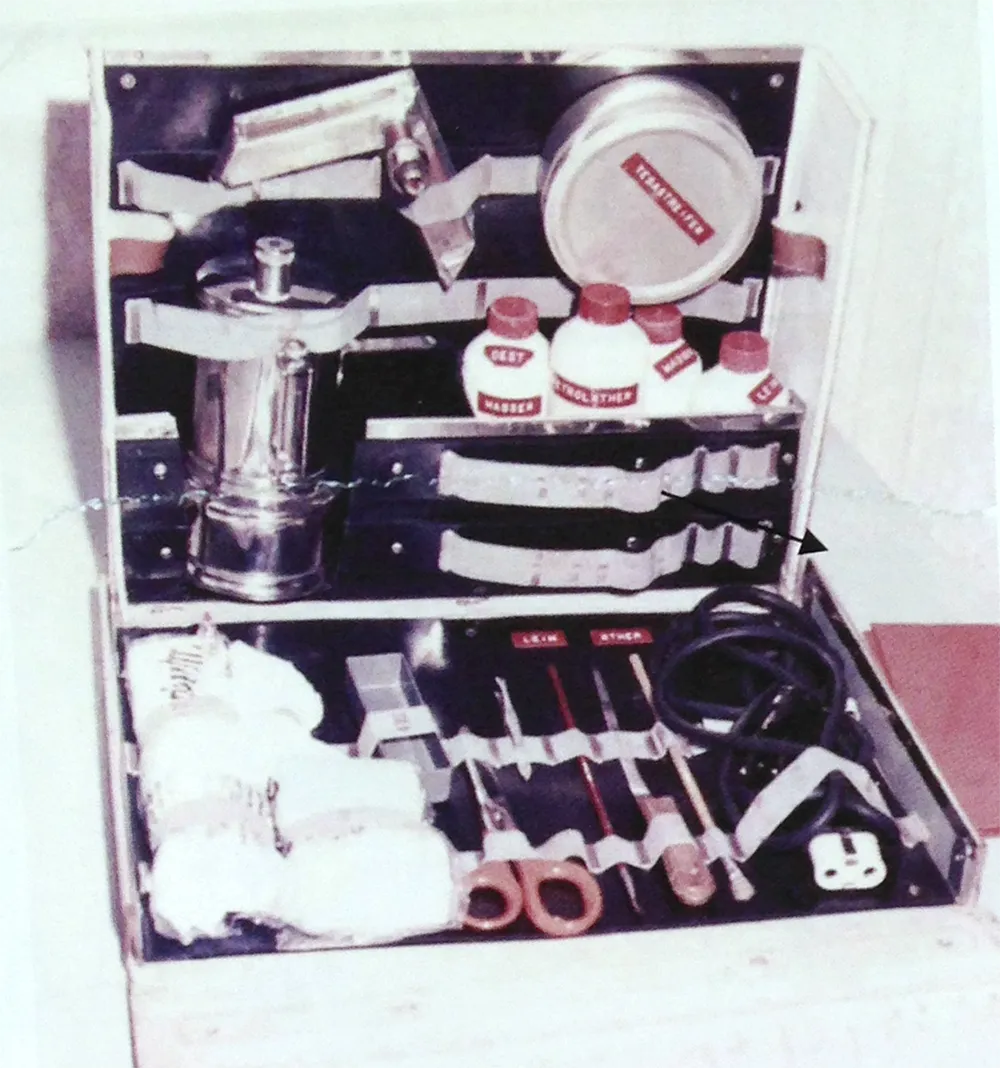
This steam generator was used, like the Kleindampfentwickler in my previous post, for opening “suspicious” letters. The Stasi Department M works directed the steam from the nozzle at the envelope to loosen the water-soluble glue on the flap. Like the Kleindampfentwickler, it was originally a mass-produced device (the Runde Ecke description states it was originally a medical inhaler). It has a glass tube indicating water level, and was stored in a case containing other working materials (which were not preserved) such as “ether, distilled water, glue, knife, scissors, brushes, adhesive strips and cleaning cloths.”

  1. Steam generator for opening letters (Inventory no. 00031). Objekt- und Fotodatenbank Online im Museum in der Runden Ecke. Accessed June 10, 2017.

Stasi / Facebook / Big Data DAAD Day 20 – Automation in Stasi postal surveillance: Kleindampfentwickler

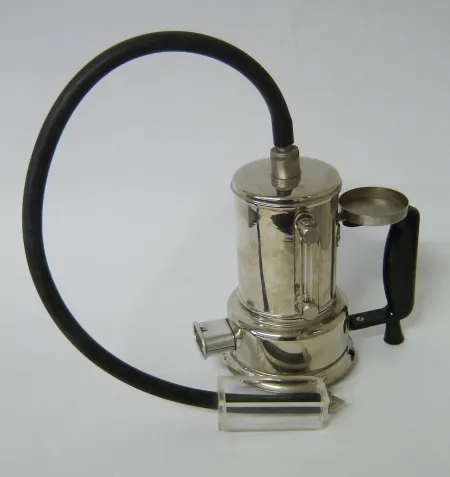
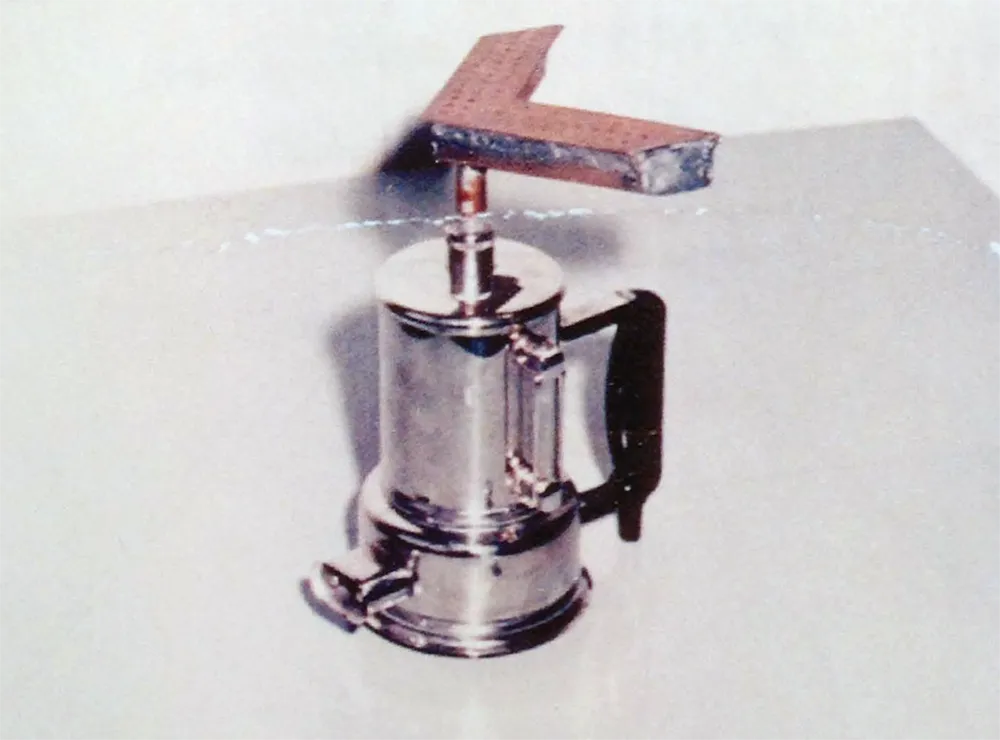
Department M, along with the Stasi OTS (Operativ-Technische Sektor), developed and implemented numerous technical tools, intelligence checks, and operational activities to speed their postal surveillance in the GDR. By the 1970’s, the department was already using various modified household appliances or industrial devices to assist in steaming open and closing letters. One example is this “Kleindampfentwickler”—a “small steam generator,” which appears to be a modified espresso maker or water boiler, with an added, V-shaped steam outlet.

Stasi / Facebook / Big Data DAAD Day 20 – Automation in Stasi postal surveillance: Kleindampfentwickler


The Kleindampfentwickler (Credit: BStU)

The materials and intentional flat and curved lines in the design of the chrome base and plastic handle suggest it was mass produced. The Stasi probably chose the kettle for the wide base and low placement of the electrical connection which serve to keep the center of gravity low and prevent tipping. They used a V-shape for this and other steam outlets to match the angled shape of envelope flaps. This one is designed to loosen the glue on a single envelope, while other steam outlets could accommodate more.

The crude construction of the modified steam outlet sharply contrasts with the retail-ready kettle. The choice of soldered copper for the material of the pipe leading upwards and steam outlet were probably based on what was available, water resistant, and easy to work with. Copper is used for speciality roofs and gutters, with the seams joined together using heat and solder. The joinery on the Stasi’s addition is not pretty, making it stand out against the base, but it exemplifies the experimental methodologies of the engineers who worked behind closed doors, as well as the belief the aesthetics or secrecy of their work would never be scrutinized.

Stasi / Facebook / Big Data DAAD Day 20 – Automation in Stasi postal surveillance: Kleindampfentwickler


The Kleindampfentwickler Operational Carrying Case (Credit: BStU)

Stasi / Facebook / Big Data DAAD Day 19 – Automation in Stasi postal surveillance: The PiD Trap

In the beginning of the 1970s most of the work of Department M was performed by hand. This labor included sorting and selecting suspicious mail, manually steaming it open, examining the contents, transcribing, copying or photographing the interior or exterior of the letter, in some cases, examining the letter for conspiratorial or stealth writing, resealing the envelope, and placing the letter back into circulation at Deutsche Post. As the secret operations heightened the suspicions during the Cold War, and with the postal service increasingly relied upon for cross-border communications thanks to the Berlin Wall preventing face to face meetings, Department M received more pressure to increase their efficiency through mechanical means.

One such machine used by the Stasi was referred to as the “PiD Trap.” This electronic device automatically scanned and screened regular letters from printed materials like newspaper excerpts, church letters, and advertisements. Like the organizational systems the Stasi employed, this apparatus made it possible to divide and focus the labor of their workers and expedited the sorting and determination of suspicious mail and “negative” or “hostile” influences from the west in the form of Politisch-ideologische Diversion (PiD). (Labrenz-Weiß, 28)

  1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

Stasi / Facebook / Big Data DAAD Day 17 – Stasi networks and Facebook Social Graph

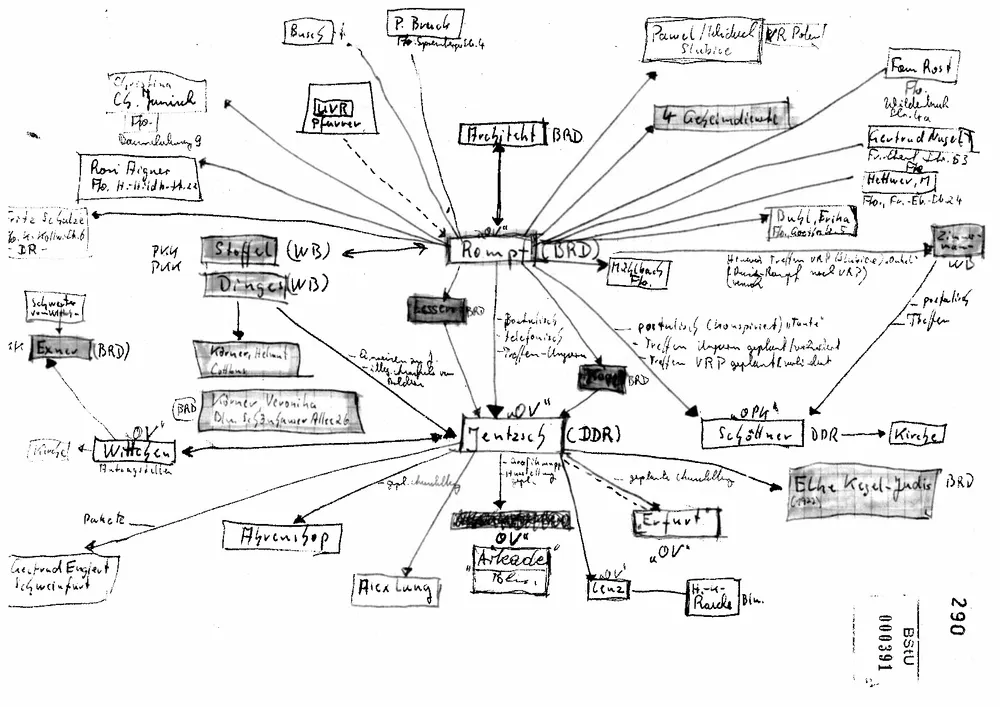
Similar to how Facebook uses a user’s connections to determine information about them, the Stasi considered all information they could gather about a person in their intelligence campaigns. They incorporated not only the contents of a target’s mail, but information about professional and personal relationships, love affairs, and organizations to which they belonged. (Reinicke, 106)

Stasi / Facebook / Big Data DAAD Day 17 – Stasi networks and Facebook Social Graph


Source: ProPublica/BStU

This attention to not only the contents of a person’s postal communications, but their social connections can be evidenced in this hand-made graphic discovered at the BStU by Julia Angwin. The graphic shows forty-six connections, linking a targeted citizen to other potentially interesting persons (e.g. an aunt), places (e.g. “church”), and meetings (e.g. post, phone). Through whichever means necessary the Stasi made and utilized these connections in order to gain additional insights and institute methods of control.

Stasi / Facebook / Big Data DAAD Day 17 – Stasi networks and Facebook Social Graph


Visual explanation of Facebook Social Graph. Source: Business Insider

This image reinforces the notion that the Stasi’s work was mostly a manual, often experimental, labor. It also tells us their work in surveillance and control, which is seen as a miserable, tyrannical sort, is now standard business practice among the software-automated surveillance capitalist models of the internet used by Facebook, Google, and others. Just as Department M workers like Gerd Reinicke mined the post for intelligence and PiD, the same basic processes the Stasi developed, now used as software by Facebook, are also at work in China, Iran, and other countries to filter and control what people can say and read through elaborate censorship software systems.

  1. Hanna Labrenz-Weiß. Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.
  2. Reinicke, Gerd. “Mitlesen für den Klassenkampf: Postkontrolle der Stasi”. In: Heimliche Leser in der DDR: Kontrolle und Verbreitung unerlaubter Literatur (ed. Siegfried Lokatis). Berlin, 2008.
  3. Angwin, J. (2017). You Know Who Else Collected Metadata ? The Stasi. ProPublica, 6–8.

Stasi / Facebook / Big Data DAAD Day 16 – Notes from a former Department M surveillance operator (part2)

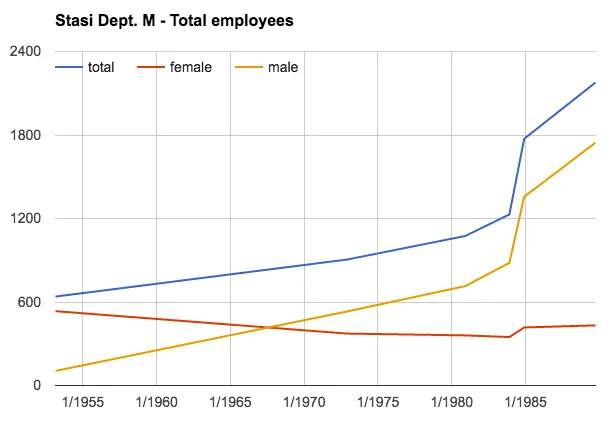
During the seven years Gerd Reinicke worked for Department M the scope of surveillance grew steadily. This is particularly evident in the 1980s, when as the government became more and more concerned of the “class struggle,” they dramatically increased the number of operators in Department M, more than doubling the size from 1980 to 1989.

Stasi / Facebook / Big Data DAAD Day 16 – Notes from a former Department M surveillance operator (part2)


Stasi Dept. M – Total employees (data from Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.)

Reinicke and his coworkers in the “Evaluation and Information” unit constantly tried to increase the “Trefferquote” or “hit rate” of material worthy of confiscation by memorizing large numbers of postal codes, names, and handwriting. Their shift managers carefully sampled the work of individual employees, checking for missed letters, which could result in punishment and disciplinary measures.

Once a citizen or group had been classified as “operationally interesting” then all their mail was withheld for inspection. Citizens of the GDR who sent private messages critical of the government or its leaders through the mail first, had their mail confiscated, and second could be brought to court on charges of “anti-state agitation” according to Section 106 of the Criminal Code of the GDR. (Reinicke, 105)

  1. Reinicke, Gerd. “Mitlesen für den Klassenkampf: Postkontrolle der Stasi”. In: Heimliche Leser in der DDR: Kontrolle und Verbreitung unerlaubter Literatur (ed. Siegfried Lokatis). Berlin, 2008.

Stasi / Facebook / Big Data DAAD Day 15 – Notes from a former Department M surveillance operator

Stasi / Facebook / Big Data DAAD Day 15 – Notes from a former Department M surveillance operator

In the essay, “Eavesdropping for the class struggle: Postal control of the Stasi,” from the book, “Secret readers in the GDR: Control and distribution of illicit literature” (ed. Siegfried Lokatis), Gerd Reinicke describes his work in the “evaluation and information” section of the Stasi’s Department M. He explains his job was to assess and classify the contents of mailings, personal letters and printed materials, and in extreme cases, make decisions about confiscation.

This work was not easy. The stream of mail was constant and so he had a limited time frame for his work. He operated in secret, but also had to consider the public perception of his decisions. While technically illegal, the government watched all mail moving within the country, as well as that leaving or arriving in the GDR. As far as the population was concerned it was an “open secret,” because they observed the effect of the government’s policy of opening mail to remove valuable items, as well any writing or media considered to be “Politisch-ideologische Diversion (PiD)” (English: “Political-ideological Diversion”)—a task which was not as clear as it might seem.

Upon his hire was told to collect information on people and facts that might be “operatively interesting” to intelligence services. But he also received instructions to remove “anything unnecessary.” This work reflects the dual role that Department M played for the SED as a surveillance and control mechanism. On one hand, they watched for communications between spies or dissidents, but they were often a censorship apparatus.

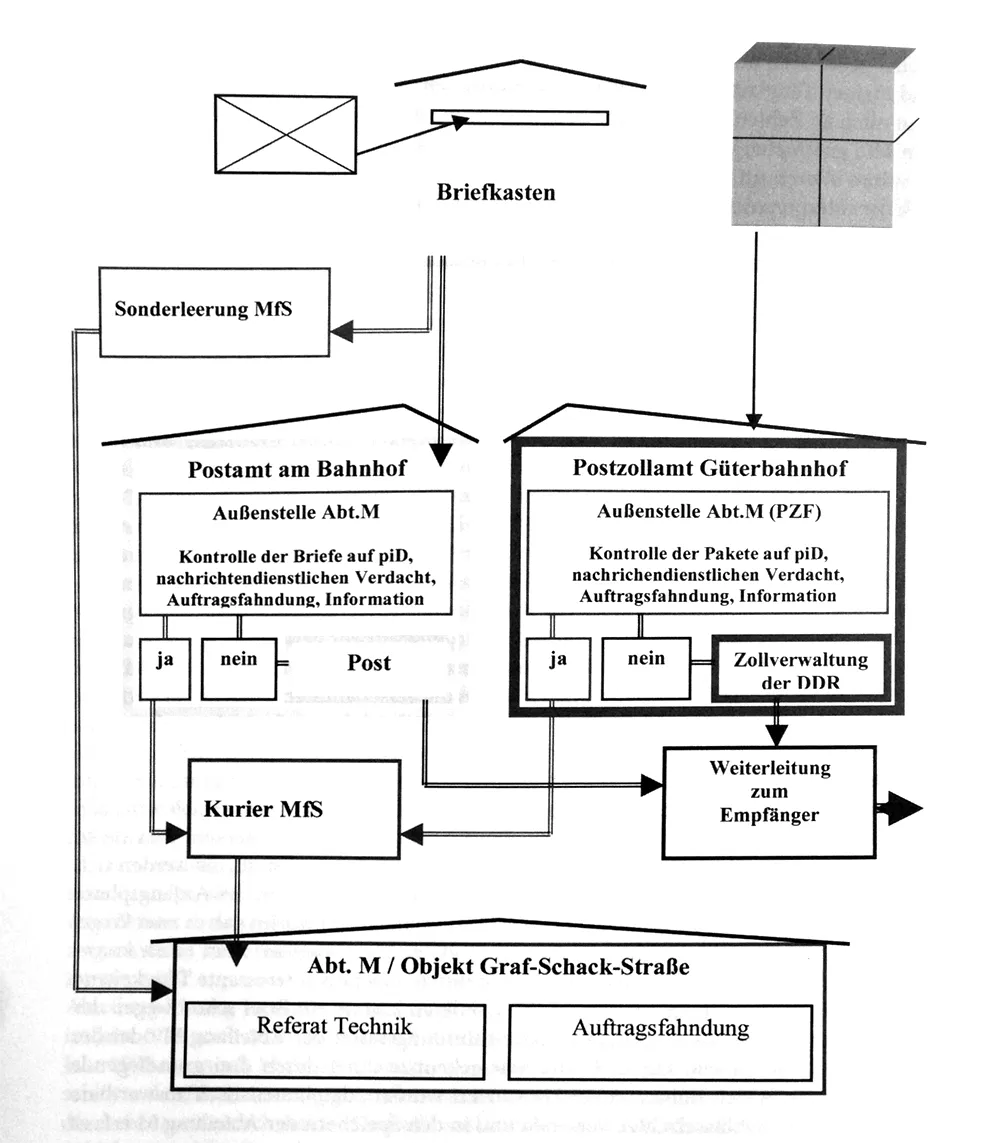
This flowchart shows the three basic categories by which mail was classified, and subclassified, specifically, as “messages suspicious of being intelligence communications,” “messages suspicious of being PiD,” and “messages determined to be ‘interesting content’.” The assignment into of any of these categories determined further routing into the Department M machinery.

Stasi / Facebook / Big Data DAAD Day 15 – Notes from a former Department M surveillance operator


Heimliche Leser in der DDR: Kontrolle und Verbreitung unerlaubter Literatur (ed. Siegfried Lokatis)

These broad definitions also underline the ambiguity in how their surveillance and censorship was officially applied. For example, in dealing with Western and dissident literature, these instructions were followed in different ways. Sometimes operators were generous in their interpretation of “class struggle appropriate” materials, while other times he characterizes their subjective interpretation as “petty.”

  • Hanna Labrenz-Weiß. Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.
  • Reinicke, Gerd. “Mitlesen für den Klassenkampf: Postkontrolle der Stasi”. In: Heimliche Leser in der DDR: Kontrolle und Verbreitung unerlaubter Literatur (ed. Siegfried Lokatis). Berlin, 2008.
  • Stasi / Facebook / Big Data DAAD Day 14 – Department M OibE groups

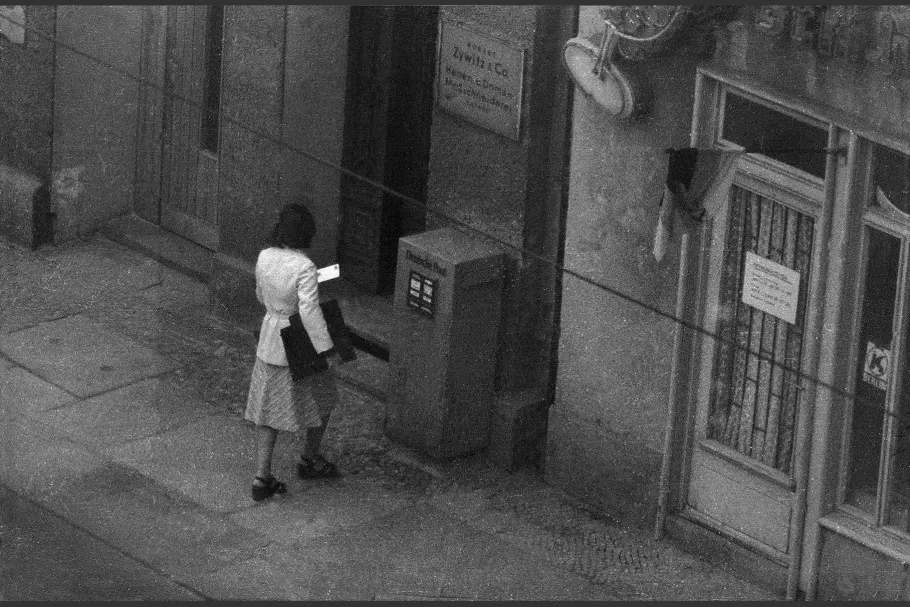
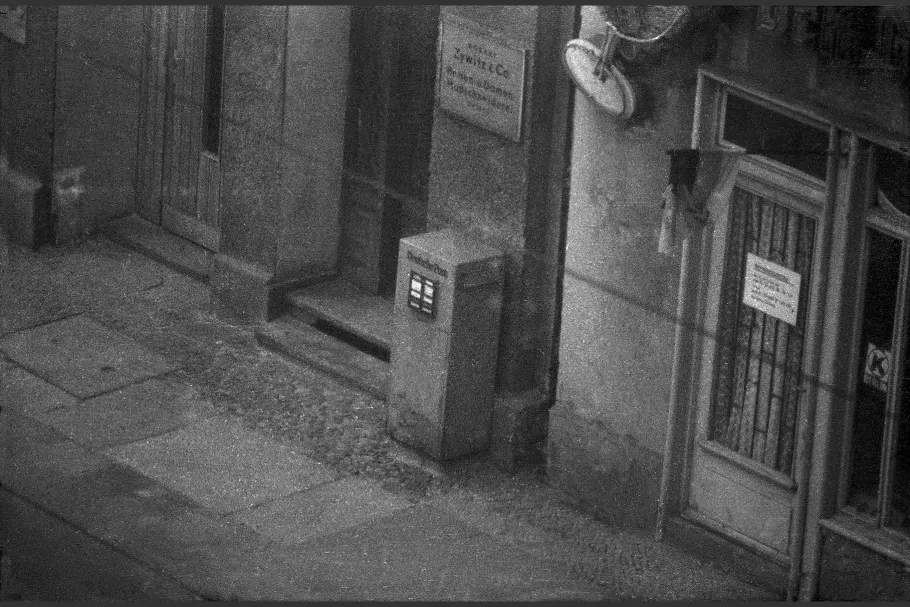
    Thanks to the implementation of index cards across the MfS, Department M had access to sender and receiver addresses, contacts, relatives, etc. to inform their surveillance work. By 1970, the department had instituted the following operational steps for examining mail. Numbers 3–6 were considered highly secretive and operations were performed under the codename “Eagle Flight”.

    1. Check if the sender or recipient existed in the police card index
    2. Establish an “Operational Comparison Card” to record information found in the mailing
    3. In the case of a suspicious mailing, carry out a search of the mail box
    4. Create photographic documentation of letterheads
    5. Compare the handwriting or typewriting font, spelling, etc. of the letter head. Identify any stealth writing.
    6. Form a special “OibE” group to check mail boxes.

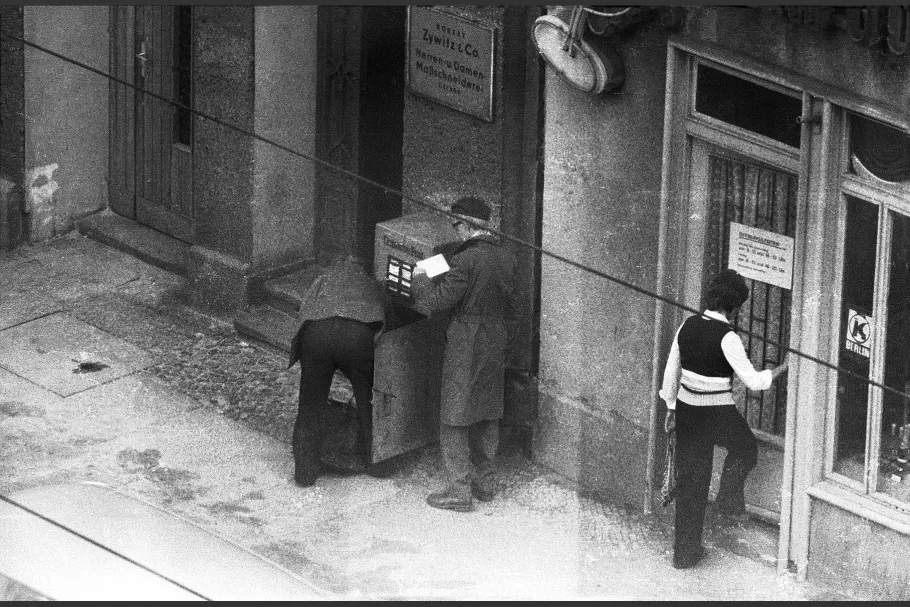
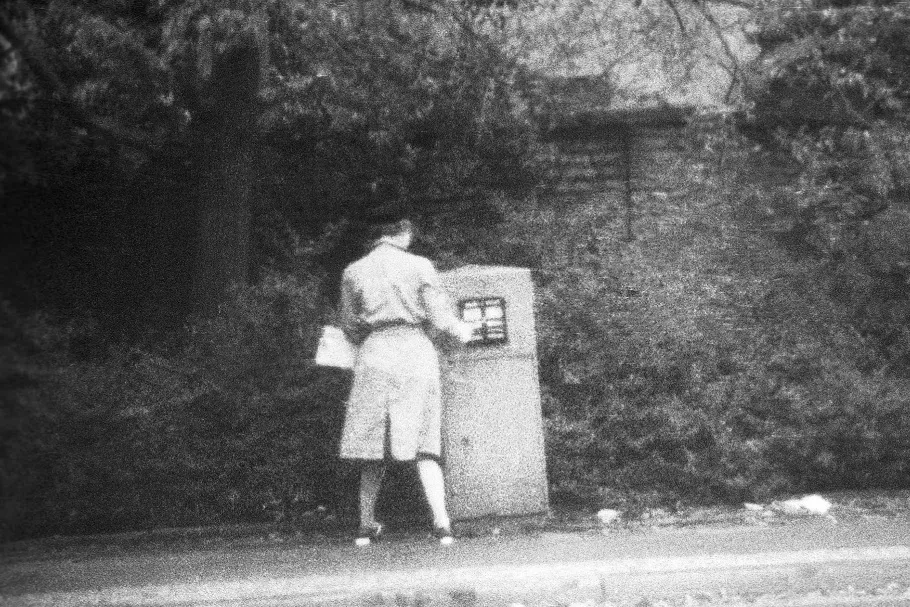
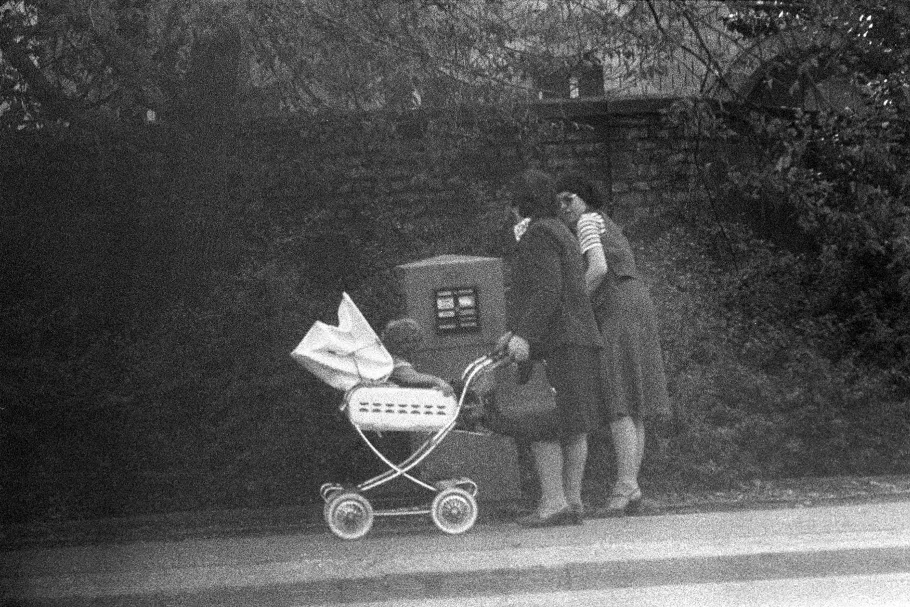
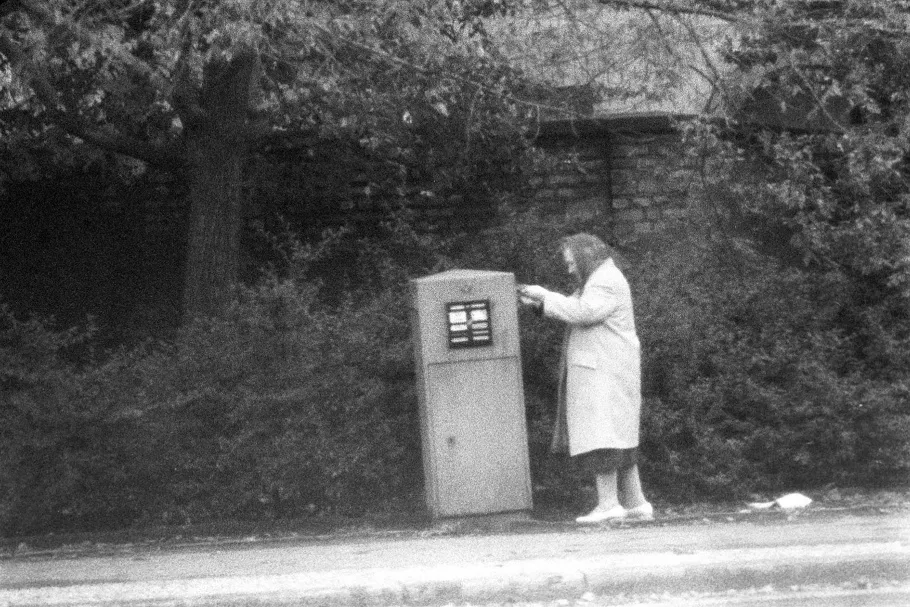
    Offizieren im besonderen Einsatz (OibE) (English: Officers in Special Operations) groups were formed specifically to monitor, and in some cases, empty mailboxes under the cover of the Deutsche Post uniforms and vehicles. They photographed persons of interest as they dropped mail off, and then opened the mail boxes and examined the contents of letters before they even reached the post office. Photographic records of their work exist, and were presented in the exhibition, “Ein offenes Geheimnis. Post- und Telefonkontrolle in der DDR” (English: “An open secret. Postal and telephone control in the GDR”) (Labrenz-Weiß, 22–24)

    Stasi / Facebook / Big Data DAAD Day 14 – Department M OibE groups


    Source: BStU

    Stasi / Facebook / Big Data DAAD Day 14 – Department M OibE groups

    Stasi / Facebook / Big Data DAAD Day 14 – Department M OibE groups

    Stasi / Facebook / Big Data DAAD Day 14 – Department M OibE groups

    Stasi / Facebook / Big Data DAAD Day 14 – Department M OibE groups

    Stasi / Facebook / Big Data DAAD Day 14 – Department M OibE groups

    Stasi / Facebook / Big Data DAAD Day 14 – Department M OibE groups

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 13 – The Stasi’s Electronic Databases

    The number of cards in the Stasi indexes grew to an incredible 39,000,000 by 1989. In order to provide constant access to this massive material data system they created various special storage units and containers as it expanded. The current mechanical powered card indexes in place at the BTsU were found after the end of the GDR and are still in use in order to meet requests of citizens who wish to view the data the Stasi kept on them.

    Stasi / Facebook / Big Data DAAD Day 13 – The Stasi’s Electronic Databases


    Mechanical index card file organization system used by the Stasi.

    Beginning in the 1960s, the MfS also used various electronic databases to track citizens.* These databases were never fully implemented as a primary source of storage because computing and software available in the GDR at the time, even machines stolen or purchased in the west, were unreliable. For six years the Stasi mirrored essential data from the F16 personal card into an electronic format. In 1975, Department XII, responsible for central data collection, information and storage, introduced the “System of automatic pre-selection” (SAVO) which allowed workers to verify that a person was “not yet recorded” in the system. This considerably reduced the time it took for verification, however it still required a substantial 12–21 days for a process to complete.

    By 1986 SAVO 2.0 was introduced providing printing functionality, increased capacity—now containing all data from the F16 card—and reducing search times to 1–6 days. It also provided teletype connections eliminating the need for couriers and allowing multiple agencies (passport control, tourism, etc.) to use the same data source simultaneously. (The Key to Power, 6) While this greatly modernized the surveillance workflow of the Stasi, it continued to act only as a duplicate of the F16 card, which was still faster for priority inquiries, and less susceptible to errors.

    Stasi / Facebook / Big Data DAAD Day 13 – The Stasi’s Electronic Databases


    A computer used by the Stasi. Source: BBC

    The logic for these implementations is echoed in modern database planning and use. While redundancy is employed for backups and increasing access speed across global networks, there is still a “master” copy of all data, or in the case of distributed system, automated processes (software) that merge and maintain distributed data into a master. Like the Stasi’s decision to completely mirror portions of the F16 system, modern systems use whichever implementation is most reliable for the master, while summarizations of that data may be “pushed” to other indexes for faster retrieval.

    The Stasi’s use of multiple systems, as well as the F16 and F22 card also preempt the concept of “joins”, which is a powerful feature in relational database management systems (RDBMS), to allow various pieces of data to be spread out across multiple indexes. Like the registration number on the F16/22 cards, records from multiple discrete RDBMS can be “joined” by matching a single identification field in order to supply additional, or limit access to other data, when performing queries.

    Multiple other computerized database systems were developed or used by the Stasi, including SOUD, a collection of information on the “enemy” shared between the GDR, Bulgaria, Cuba, Poland, the USSR, Czechoslovakia, Hungary, and Vietnam. The most expansive of all their electronic indexes, was the central database of personal data (ZPDB). Introduced in 1981, by the end it contained records on over 1,320,000 people, 417,000 situations, 558,000 objects, and numerous related information.

    The desire to track not just people, but occurrences and objects is directly visible in the largest person tracking organization today. In Facebook’s “Social Graph”, introduced in 2007, any person, place, thing, event, anything that can be named, is recorded in a massive attempt to commodify everything and our connections to it. Like the Stasi ZPDB, everything in the Facebook Social Graph is indexed by a unique identification string as single record, which Facebook considers a “node,” with links or “edges” that connect them. These definitions are based on Facebook’s desire to do data science on the their information, applying statistics and other mathematical operations from graph theory in order to understand their data and predict (and manipulate) the behavior of users.

    *Regrettably, all electronic databases and their magnetic storage was destroyed not long after the end of the GDR. Meaning, BStU staff now use the original paper F16 card system to provide services to the public.

    1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.

    Stasi / Facebook / Big Data DAAD Day 12 – The VSH card system

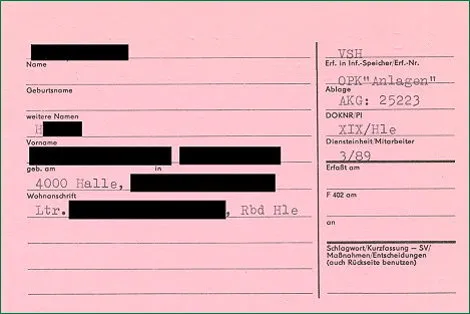
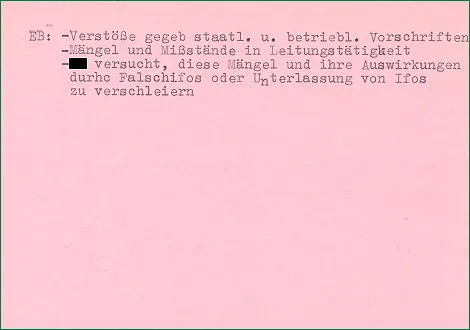
    The VSH index card system was yet another data storage method developed by the Stasi for monitoring and controlling the population. Introduced in 1974, the system used a red F401 card for all “secretly policed” persons, and a corresponding white F402 information card once that person was captured and began informing for the MfS. The system contained information not included on the Kerbloch index, for example, specifics deemed to be “operationally significant” like that person’s activity in the MfS, and ensured the flow of information on persons of interest across operational departments, districts, and facility services. The VSH files enormously expanded the number of persons surveilled, and were the most important cards used by operational service units until the end of the MfS. (The Key to Power, 6)

    Stasi / Facebook / Big Data DAAD Day 12 – The VSH card system


    Front of the pre-compaction, search and map card. Source: BStU

    Stasi / Facebook / Big Data DAAD Day 12 – The VSH card system


    Back of the pre-compression, search and map card. Source: BStU

    The VSH cards were divided into 15 categories ( PK ):

    • PK 1: Staff and agents of the enemy intelligence services
    • PK 2: Senior staff of the centers of political and ideological diversion
    • PK 3: Members of terrorist organizations and individual terrorists
    • PK 4: Members of Zionist hostile immigrant, clerical and other organizations
    • PK 5: persons who carried out orders from hostile intelligence agencies, centers of the political-ideological diversion, Zionistically hostile immigrant, clerical and other organizations against the states of the socialist community
    • PK 6: People unmasked as enemies of the opponent
    • PK 7: people who had not offered the information that was real
    • PK 8: persons who carried out provocative actions on the territories of the states of the socialist community as well as against their representatives and citizens
    • PK 9: Persons who were expelled from the states of the socialist community
    • PK 10: People who had committed particularly dangerous crimes
    • PK 11 diplomats and employees of diplomatic and consular missions of NATO , Japan and the People’s Republic of China
    • PK 12: correspondent of NATO -Mitgliedsländer, Japan and the People’s Republic of China
    • PK 13: Employees of trade and economic representatives
    • PK 14: Members of organizations that have been engaged in international smuggling on a large scale
    • PK 15: Persons whose activities were directed at a damage to the economy of the states of the socialist community
    1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.
    2. BStU: ( VSH ) of the Central Evaluation and Information Group ( ZAIG )
    3. BStU: Pre-compacting, search and identification card ( VSH ) of Division 1

    Stasi / Facebook / Big Data DAAD Day 11 – Kerblochkarten

    Stasi / Facebook / Big Data DAAD Day 11 – Kerblochkarten


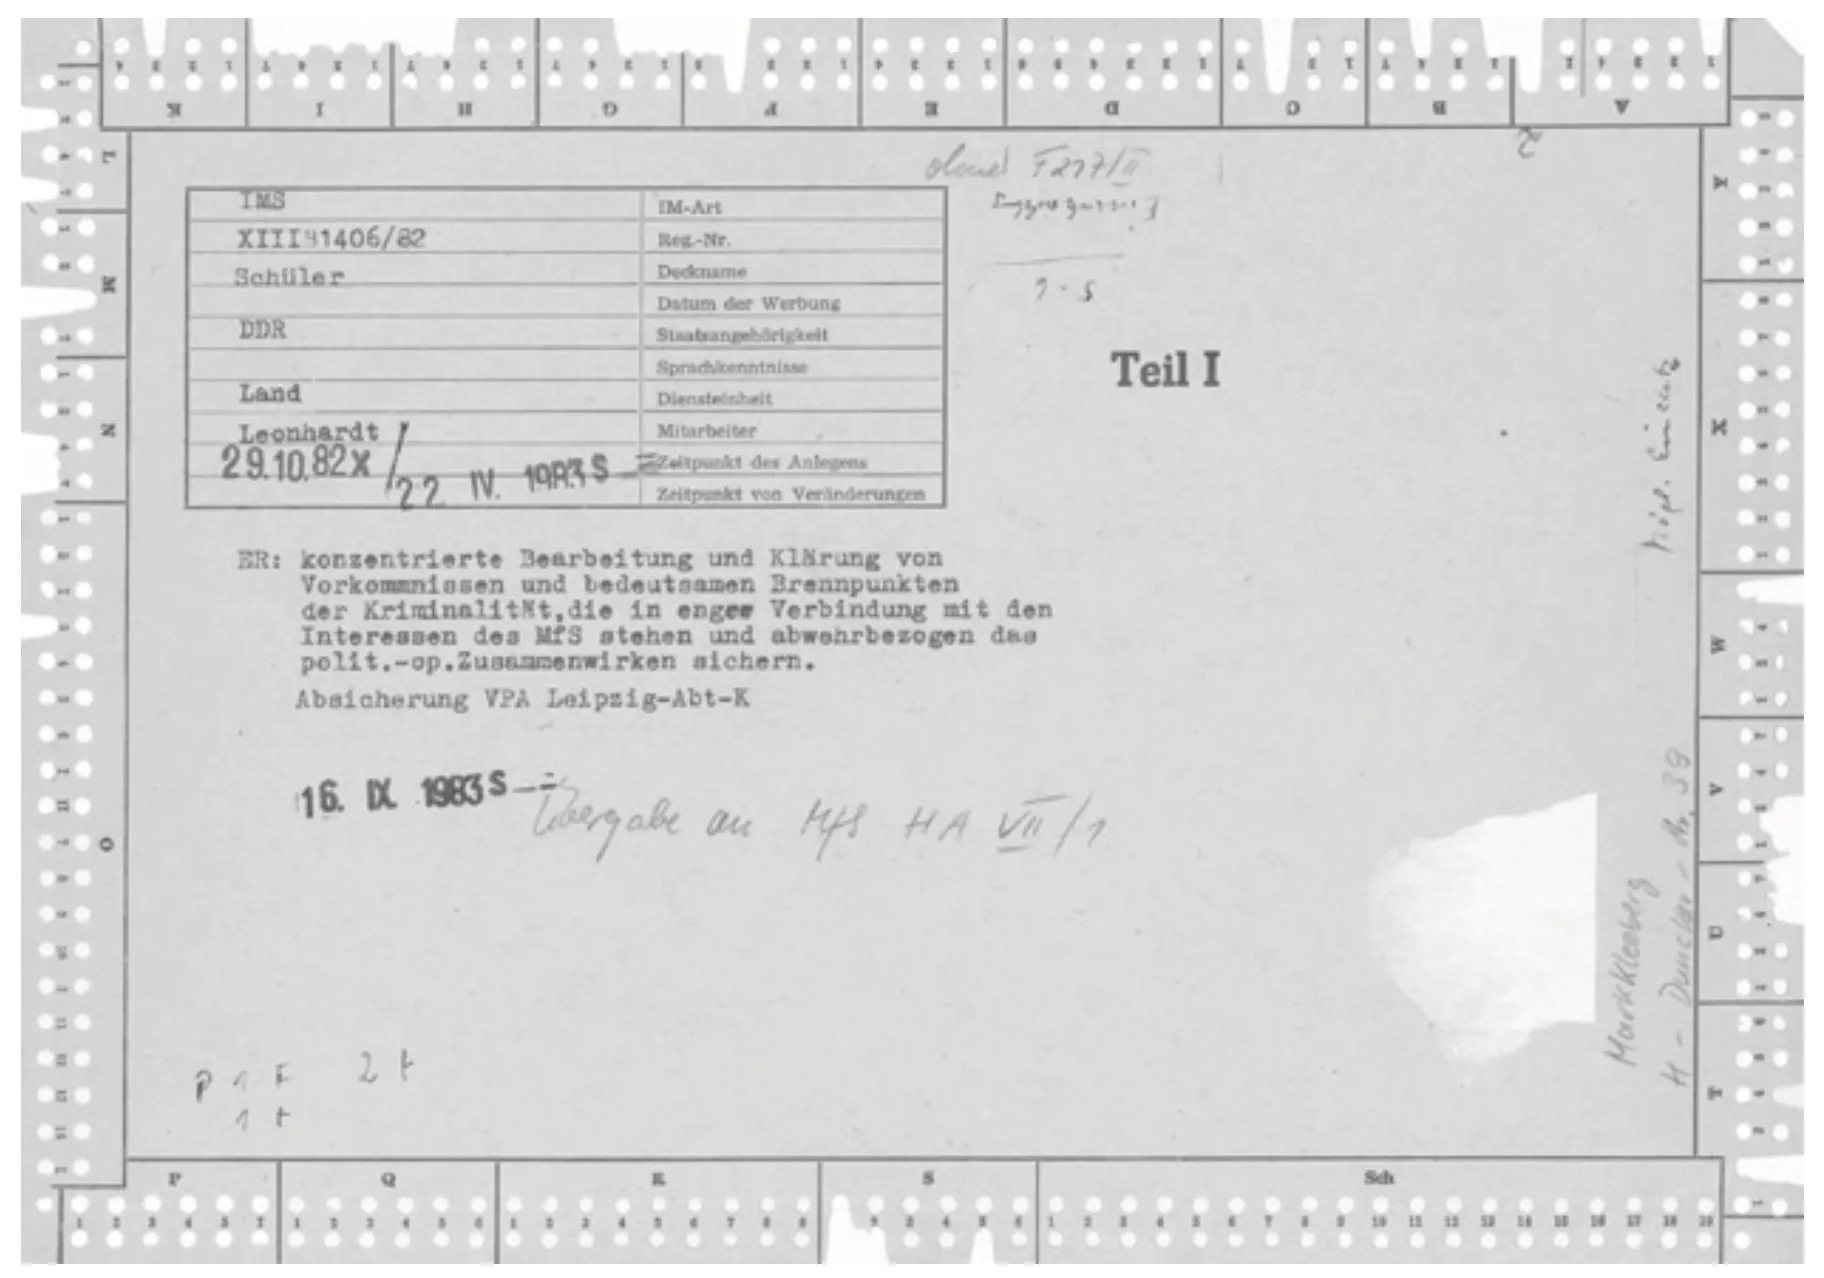
    A Stasi Kerbloch card

    The Stasi used several other card systems to assist their postal surveillance. The Kerblochkarten (English: Kerbloch cards) system allowed storage of data encoded as a series of hand-made notches. Like other punch card systems, groups of cards could then be automatically processed by a machine based on the presence of notches and a predefined key. The Kerbloch card system made it possible to perform statistical evaluations and targeted searches on up to 350 cards/persons at a time. Importantly, this card amended the functionality of the F16 cards and allowed the Stasi to quickly search for potential informants by querying characteristics relevant to a particular job. While anyone who has used a computer spreadsheet software today would take this sorting and searching functionality for granted, this was a highly useful tool for the Stasi, which by 1989 had amassed over 39 million index cards. (The Key to Power, 5)

    1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.
    2. BStU: Kerblochkarten (KK)

    Stasi / Facebook / Big Data DAAD Day 10 – Card systems of the Stasi

    The early days of the Stasi were marked by the development of new systems for monitoring the population. In the 1950s, having already incorporated a post-WWII file system used for denazification, the MfS implemented three new index card types to track citizens, all of which were stored in a central card index. These cards were distinguished by color and used to track persons considered hostile to the state (form A1 which was yellow), official staff (form B1, later replaced by the blue and grey F19), and persons who were arrested (the red, form C1).

    While official staff had titles and were on the payroll, the Stasi used hundreds of “unofficial staff.” These “Inoffizielle Mitarbeiter” (or IMs) were either foreign citizens who turned over valuable information like trade secrets, or domestic informants who spied on their colleagues, neighbors, and relatives (and sometimes even spouses). While money was a primary motivation, they were compelled for a number of other reasons, including blackmail, ideological commitments to the GDR, or gifts other than money, like lavish vacations, prostitutes, and official state awards. In fact, the Stasi implemented an impressive number of medals and rewards in order to convince both IMs and official staff to maintain loyalty and faithfully contribute their labor to the state. (Macrakis, loc 386) These awards are not unlike the loyalty cards, badges, and other gamification tactics that today’s corporations employ across their databases of customers in order to increase brand allegiance and sales.

    Similar to modern software development, the Stasi index card systems, like many of their methods over the years, were constantly being reworked and improved with each new iteration. For example, while the previous system used separate cards to track “enemies” and “friends,” as the Stasi learned to coerce those formerly consider hostile into becoming secret informants it became necessary to track persons who evolved into “frenemies of the state.”

    This situation presented a particular problem, as the Stasi needed to record and track personal data on these people, but their real identities needed to be protected should they agree to turn over valuable information. For these persons the Stasi implemented a separate “transaction card” (F22) that augmented the standard cards. The change updated the yellow card (F16, formerly A1), which contained the real name, address, birth date and place, occupational status, workplace or school, and the red card (F18, formerly C1), used for those arrested, which contained this information, as well as a mugshot, a visual description, and data related to their crime, and added a registration number if they were a Stasi informer or agent. (The Key to Power, 3–4)

    Stasi / Facebook / Big Data DAAD Day 10 – Card systems of the Stasi


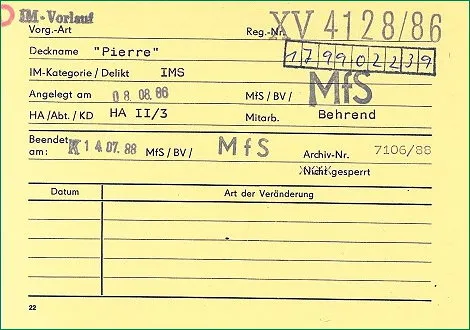
    The central operation card “F22” Credit: BStU

    The new “transaction card” (F22) recorded Stasi informants only by this registration number, as well as a secret code name and name of the case officer who managed the agent. Finding the real name of a Stasi operative meant matching not only the registration numbers on these cards, but additional comparisons, because many agents purposely shared registration numbers to add extra layers of secrecy. (Macrakis, 78) This method is similar in theory to modern relational database lookup tables, where a user’s personally identifiable information (PII) is separated and protected from data dumps containing so-called “anonymized data” , or public key encryption, where data is transmitted securely by performing mathematical operations on it using a combination of a unique private and public key.

    1. The key to power: Card indexes and other finding aids practices of State Security. Archivar 64. Jahrgang Heft 04 November 2011.
    2. Macrakis, Kristie. Seduced by Secrets: Inside the Stasi’s Spy-Tech World (Kindle Location 1615). Cambridge University Press.
    3. Jason Koebler This Visualization of NYC’s Taxis Shows the Promise and Pitfalls of Big Data Motherboard (2014)
    4. Alex Hern New York taxi details can be extracted from anonymised data, researchers say The Guardian (2014)

    Stasi / Facebook / Big Data DAAD Day 9 – MfS Department M (1960’s developments)

    The implementation of zip codes across West Germany in 1961 made it much easier to monitor postal traffic between east and west. The Berlin Wall was erected in that same year, leading to a heightening of Cold War suspicions and increased emphasis on monitoring movement of information between east and west.

    The 1960’s also saw the various reorganizations and new leaders, including Lieutenant-Colonel Walter Mehrbach, whose years of experience in the postal service led to the development of the first training manual for Department M, and certification courses in mail surveillance at the MfS Law School in Potsdam. (Labrenz-Weiß, 21)

    As Department M grew in the 1960’s, so too did the amount of mail they examined and information they recorded. This demand for intelligence required constantly expanding data storage methods, which led the department to develop a card system for efficient alphabetical sorting and identification of people, places, and objects on both sides of the East/West German border. (Labrenz-Weiß, 19) I’ll dig in a little deeper over the next few days on these cards, for now a photo from my BStU archive research last summer:

    Stasi / Facebook / Big Data DAAD Day 9 – MfS Department M (1960’s developments)


    BStU: MfS, BV, Potsdam, Abt II 764 pg 6

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 8 – MfS Department M (A captured letter from the BStU archives)

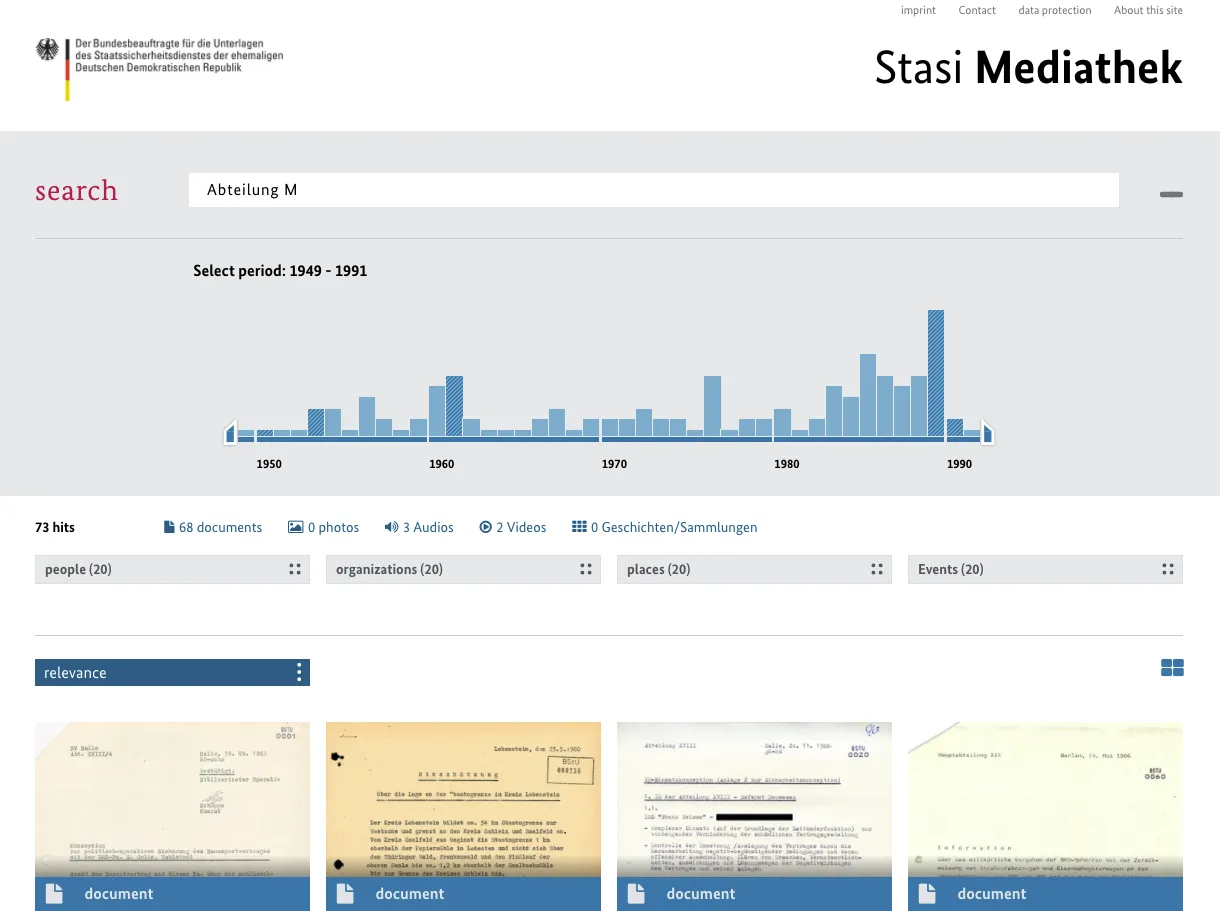
    The Stasi Mediathek website published by the BStU is an amazing resource. One can search for example “Abteilung M” (English: Department M) and find a range of digitized original documents related to the Stasi’s postal surveillance.

    Stasi / Facebook / Big Data DAAD Day 8 – MfS Department M (A captured letter from the BStU archives)

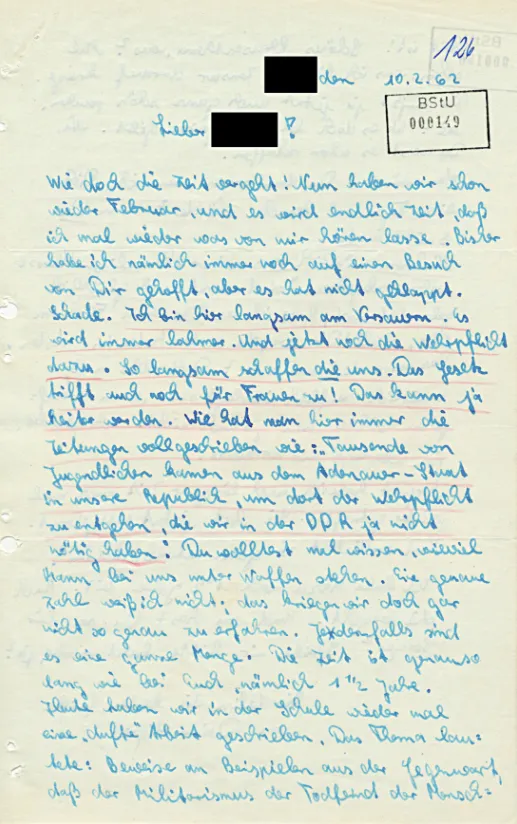
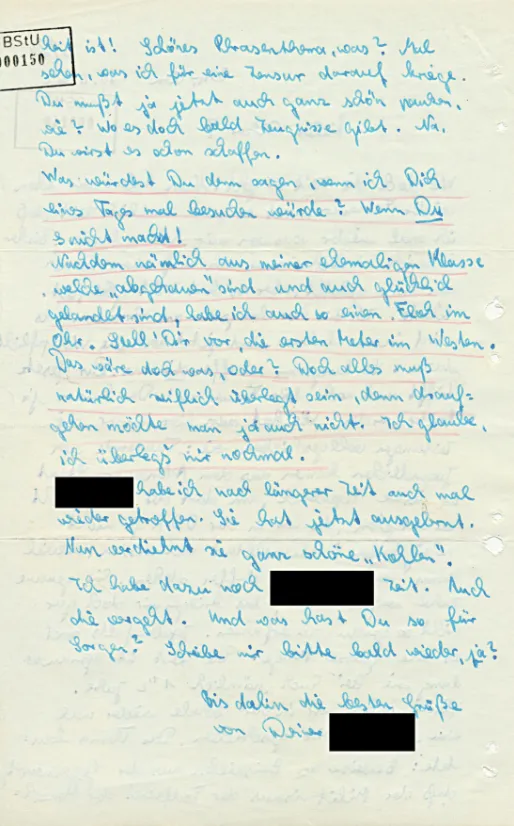
    This is an example of a letter that the Stasi Department M removed from the Deutsche Post in 1962. In the letter an East German student writes to her friend in the west about her dissatisfaction with the militarism and compulsory conscription in the east and says she is considering fleeing the GDR. Surely the Stasi placed her under a watchful eye due to the information they found through their postal surveillance. It’s also interesting the Stasi one, removed the letter altogether from the postal stream, likely in order to prevent negative sentiments from appearing in western press, and two, kept the document, perhaps as evidence against her at a later date, or potentially also as a result of the thoroughness of the bureaucratic surveillance system they had developed. An English translation can be found at the above link as well. (BStU)

    Stasi / Facebook / Big Data DAAD Day 8 – MfS Department M (A captured letter from the BStU archives)

    Stasi / Facebook / Big Data DAAD Day 8 – MfS Department M (A captured letter from the BStU archives)

    Stasi / Facebook / Big Data DAAD Day 7 – MfS Department M (Development of working methods)

    In the early years of the Department M, or Division VI as it was known at the time, there was no vocational training so the few dozen employees had to conceive of their own workflows. At that time, the standard set for workers who examined the contents of mail was to read “500 letters per person for each working hour.” Post control took place in special rooms of selected central post offices, where employees of Division VI covertly intercepted and opened mail. The onsite locations helped to ensure the Stasi could accumulate as much intelligence as possible while causing the lowest acceptable delay in the Paketstrom (English: packet stream). (Labrenz-Weiß, 13)

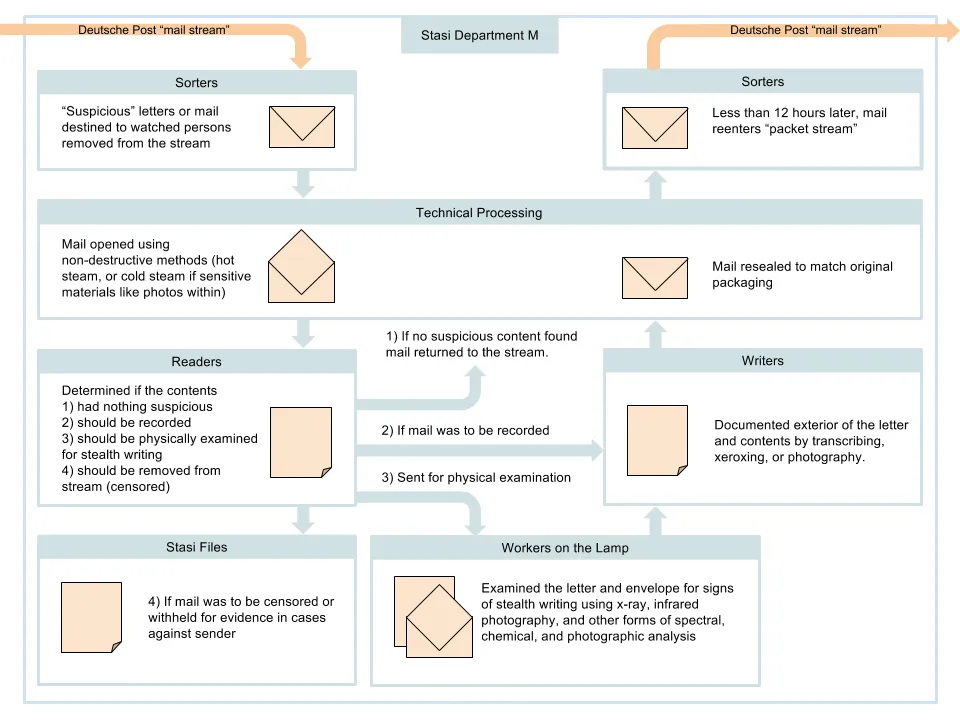
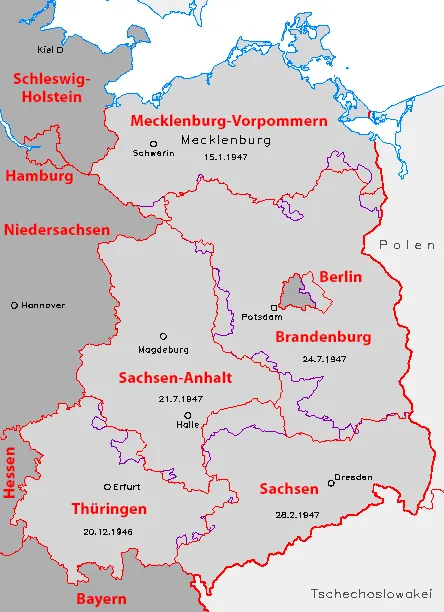
    By 1952 Department M was established and locations for inspection were formalized. The five GDR states (see previous blog post) were divided into 14 districts in order to increase efficiency by moving postal control structurally closer to sender and receiver. Various statutes were established by the MfS allowing for inspection of the post in order to prevent sedition inspired by western influence, as well as to carry out censorship through interception of materials. The process for post control was also more precisely defined and subdivided into specific working groups for: 1) Sorting mail by size; 2) Technical processing; 3) Readers; 4) Writers; and 5) Employees at the lamp.

    Units responsible for “Sorting” the mail passed any letters or parcels that appeared suspicious, as well as all mail destined for persons or organizations under postal control, to “Technical processing” where it was opened using steam or other nondestructive methods. It was then sent to “Readers” who sent letters to the “Writers” once it was determined the contents were worthy of being transcribed. The Writers had the job of recording the documents, preparing reports for each day, and passing information with clues for espionage, sabotage, or, after the addition of the Berlin wall, plans for escape, to relevant departments.

    “The work on the lamp” investigated suspicious consignments in a dark room under a quartz lamp in order to identify clandestine forms of communication like secret writing on the surface of paper, or other methods including invisible ink. If found these documents were then passed to the OTS, or Operational-Technical Sector of the MfS, for special investigation.
    These early divisions of labor served to increase efficiency much in the same way Henry Ford had done at the beginning of the century when he introduced the assembly line. Equally, the divisions helped Stasi employees to become more knowledgeable and specialized in their work, eventually developing machines to augment, improve, and speed up their tasks. (Labrenz-Weiß, 16–17)

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 6 – MfS Department M (postal control selection)

    Stasi Department M workers removed enormous amounts of mail from Deutsche Post each day for inspection. Mail was identified visually based on handwriting, types of letters, or specific addresses. Surveillance of mail was technically illegal in the GDR. Still, mail was withheld on an official basis “in order to prevent attacks” by western intelligence agencies, presumably using “threats and explosives.” This led to the inspection of all incoming and outgoing mail to press agencies, embassies and consulates of NATO countries, and other western correspondence.

    Unofficially, in the interest of multiple surveillance, control and censorship possibilities for the Stasi, everything possible was scrutinized, both foreign and domestic. The postal inspections contributed intelligence on GDR and foreign citizens who were suspected of spying for the west. They allowed the Stasi to filter information the citizens of the GDR were allowed to access, share, or communicate to the outside world. The Stasi intercepted undesirable books, seditious content, and other materials with the ultimate goal of preventing public protests, or other conspiratorial activities. While the goal of Department M was to return the mail collected for inspection back to Deutsche Post within a 12-hour window, many deliveries were seized and never returned. This massive operation naturally resulted in frequent delays in delivery or damage to letters or parcels, which including those that never arrived, led the public to become increasingly aware of the ongoing postal inspection.

    Finally, the postal surveillance provided the Stasi with information about the mood of the population in the GDR, by examining personal communications, as well as messages sent between in companies and institutions. Reports prepared by administrators in Department M on population mood included information on economic and political sentiment and specifically targeted demographic groups (Labrenz-Weiß, 13) across specific geographic locations and social strata in the GDR in order to give the best possible assessment. For example, the following population groups are described in BStU documents

    • Brandenburg: 1,000 workers each at the East coaster and the Brandenburg Steel Works, and 1,000 old and new builders
    • Mecklenburg: 1,000 workers of the shipyards, 500 students and 50 teachers of the University of Rostock, and 1,000 old and new builders
    • Saxony-Anhalt: 1,000 workers of the chemical industry and of Magdeburg heavy machinery construction, 800 students and 100 faculty members of the Martin Luther University Hall, and 1,000 old and new farmers in Altmark
    • Saxony: 1,000 workers of the Stahlwerk Riesa as well as tradesmen / merchants, and 800 students and 100 lecturers from the University of Leipzig
    • Thuringia: 1,000 workers of the Unterwellenborn steelworks, Zeiss works in Jena and tradesmen, and 800 students and 100 professors of the Jena University

    Stasi / Facebook / Big Data DAAD Day 6 – MfS Department M (postal control selection)


    East Germany’s State borders established after WWII 1945-1947 in violet. In red the borders of the new states established during reunification. Source: Wikipedia

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 5 – MfS Department M (Organizational structure overview)

    Stasi / Facebook / Big Data DAAD Day 5 – MfS Department M (Organizational structure overview)

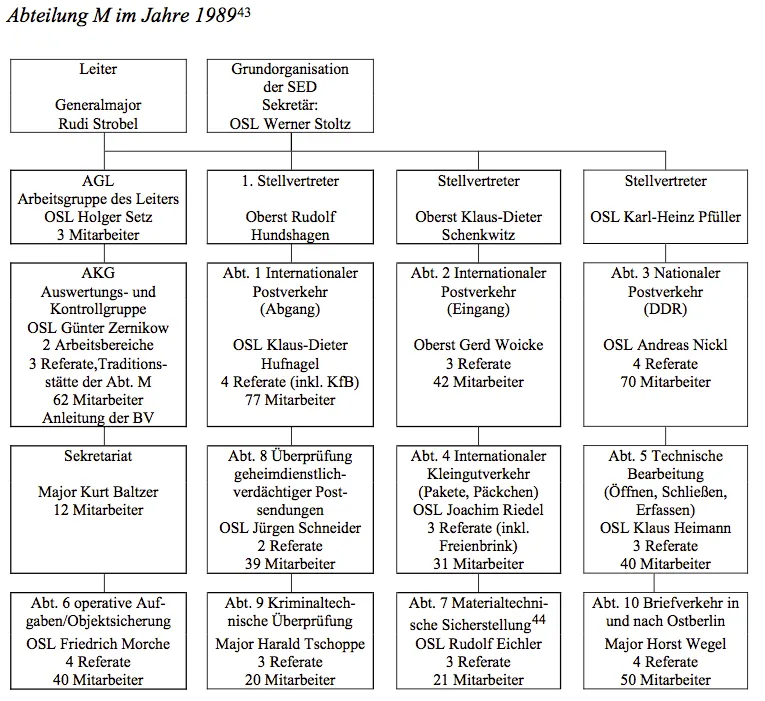
    In 1989 Department M had 10 divisions, which were subdivided into 36 units. The head office, which consisted of 8 divisions and their corresponding units, was located in East Berlin. The divisions were organized based on mail destinations (western, non-communist countries for example), types of mail (like parcels or telegrams), or function within the scope of the work of the Department. Specific units were tasked with selecting mail for examination, while in technical processing units the selected mail was opened, examined, documented, and closed again by their respective units. Other units in Department M were assigned to inspecting customs declarations, maintaining secrecy, or operational engineering, where design, manufacturing, and maintenance of the technology took place. (Labrenz-Weiß, 8–10)

    1. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 4 – MfS Department M (the workers)

    The Stasi surveilled the post of the GDR for nearly 40 years, starting with the founding in 1950, until the fall of 1989 when the Berlin wall fell. The number of workers in Department M rose from a few dozen in the beginning, to nearly 2,200 by the end. The largest office occupied two buildings in the massive Stasi headquarters complex in Berlin-Lichtenburg and included almost 500 employees, with the remaining 1,700 spread across 15 district administration offices. (Polzin, 105)

    While the ratio of women to men in Department M shrank over the years possibly due to the increasing focus on technology and automation, it was consistently at least twice that of the entire MfS. In the beginning 80% of Department M employees were women, compared with 25% in the MfS, while in the 1960s 40% were women compared to 14%. In 1989 only 20% of Department M employees were women. (Labrenz-Weiß, 5)

    Employees were subject to numerous specialized training to prepare them for their work. This included courses on typography, x-ray certification, and photography for those performing inspections. Employees who were integrated with Deutsche Post received information like electronic training for working with telegraph devices, operating postal vehicles, and other knowledge related to the movement of mail and parcels. Those employees charged with the development of specialized equipment for Department M studied engineering, paper technology, air and refrigeration systems, and the mechanics around the movement of postal and newspaper materials. (Labrenz-Weiß, 6)

    While Department M employees were physically embedded in Deutsche Post locations, their activities there were considerably constrained in order to ensure the secrecy of their work. For example, they were required to sit in closed groups in the cafeterias in order to avoid direct contact with actual postal workers. Official contacts were only allowed with Stasi officers already embedded in the post control system special operations.

    1. Arno Polzin, Postal Inspection, Telephone Surveillance and Signal Intelligence in Daniela Münkel (eds.), State Security: A Reader on the GDR Secret Police, Berlin 2016.
    2. Hanna Labrenz-Weiß, Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 3 – MfS Department M

    The Ministry for State Security’s Department M was tasked with “postal control”, or the inspection of domestic and international letters and packages. They conducted their work thanks to cooperation with Deutsche Post which, as another state institution concerned with “security of the state,” was subject to the same politics and power infrastructure of the single party system of the DDR (1). Consequently, the Department M had access to every letter and parcel which traveled throughout East Germany by inserting itself in the logistical operations of the postal system. The Stasi reserved special rooms or entire floors within the Deutsche Post buildings, which were off limits to regular post workers.

    In Berlin, Department M had offices in the post office at Nordbahnhof, in the central telegraph office on Oranienburger Strasse and in the railway post office at Ostbahnhof. These rooms used by the MfS were designated “Department 12” of the German Postal Service, both internally and officially.(2)

    1. Arno Polzin, Postal Inspection, Telephone Surveillance and Signal Intelligence in Daniela Münkel (eds.), State Security: A Reader on the GDR Secret Police, Berlin 2016.
    2. Hanna Labrenz-Weiß: Abteilung M (MfS Handbuch). Hg. BStU. Berlin 2005.

    Stasi / Facebook / Big Data DAAD Day 2 – The Stasi’s automatic letter opener invention

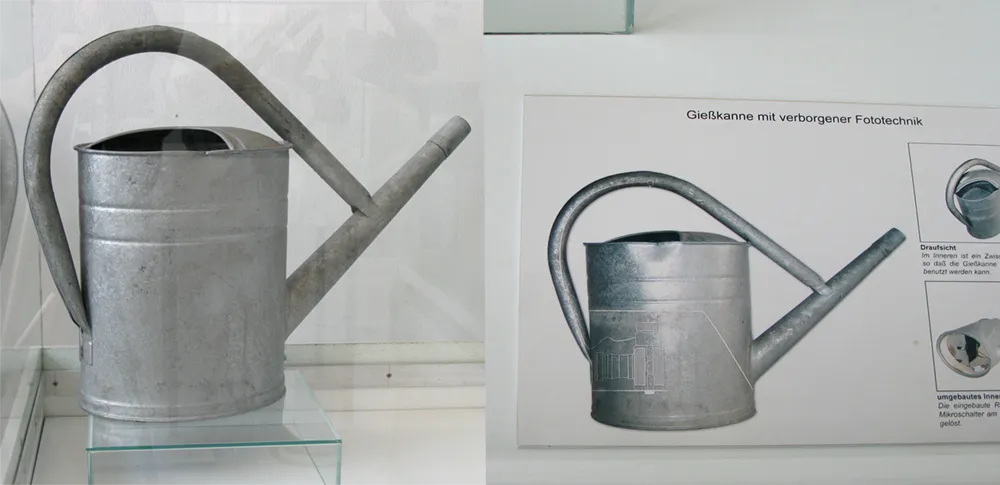
    The former East Germany’s Ministry for State Security (more popularly referred to as the MfS or “Stasi”) is widely known for the inventive and clandestine gadgets that appear in films like Das Leben der Anderen (English: The Lives of Others) or on exhibit at the Stasi Museum in Berlin. Some of my favorites from the museum are the cameras disguised as everyday, boring objects. Take this watering can with a hidden camera.

    Stasi / Facebook / Big Data DAAD Day 2 – The Stasi’s automatic letter opener invention

    Imagine a sweet old Oma in her garden, tipping the can just so, with the intention of spying on the grandma next door. This technologically-enabled interpersonal collection of data of our “friends” was very much like how Facebook operates today. The Stasi used blackmail to infiltrate networks and get people to give up their neighbors, while Facebook coerces us in different ways; for example, through algorithms that implore us to post details from our private lives in order to build up one’s cultural capital and sense of self worth. I’ll explore this connection more in later weeks, particularly in reference to a special type of behind the scenes inventions of the Stasi: a series of machines that automatically opened personal letters and closed and resealed them after their contents were examined.

    Stasi / Facebook / Big Data DAAD Day 2 – The Stasi’s automatic letter opener invention

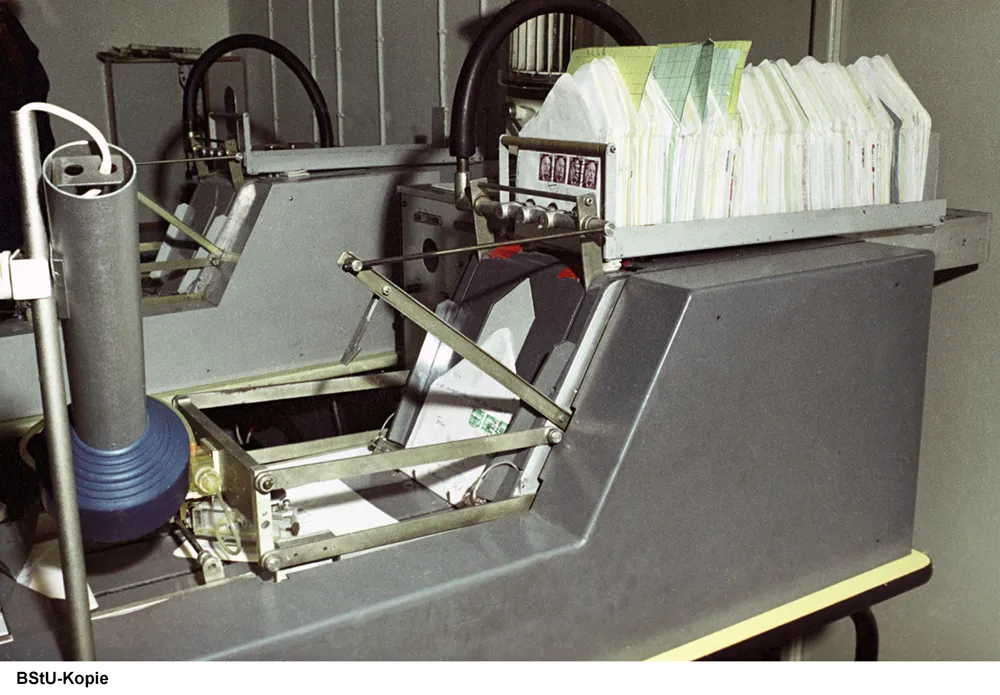
    In this project, a central question is what do the motivations and methods of this machine, which was used to intercept and automate the secret unpacking and examination of personal information of letters between private citizens, tell us about how the software used by the NSA for monitoring citizens around the globe? Or about the even more secretive methods of Google or Facebook as they examine our personal information in order to influence our behavior? Until tomorrow.

    Stasi / Facebook / Big Data DAAD Day 1 – Willkommen in Deutschland

    This is the first post in a long time. Over the next two months I will add one every day while I’m working on a new stage of an ongoing project I began in Berlin in 2010. I haven’t posted like this in a while. I find it extremely helpful to share and collect research, create an arc for the work, and of course to stay focused. While the project will evolve as I add content to this space, I’ll share the essential bits from my plans here:

    This proposal for a DAAD grant will support research and a series of writings and visualizations that examine how the technological inventions of the East German Ministry for State Security preempt Facebook, the NSA, and the world of Big Data. I will work at Humboldt University and the Stasi Records Agency (BStU) in Berlin and the Museum at the Round Corner in Leipzig, researching and documenting the schematics and actual machines developed by the Stasi for surveillance. With this knowledge I will frame an investigation that uses the analog devices of the Stasi to lend insight into the methods implemented today as software by social media, advertising groups, and intelligence agencies in the service of domestic surveillance and censorship.

    I feel super fortunate to be able to continue this project I started almost seven years ago thanks to support from the German Academic Exchange Service or DAAD (German: Deutscher Akademischer Austauschdienst) and Prof. Dr. Wolfgang Ernst at the Institute of Musicology and Media Studies at Humboldt University Berlin.

    Stasi / Facebook / Big Data DAAD Day 1 – Willkommen in Deutschland

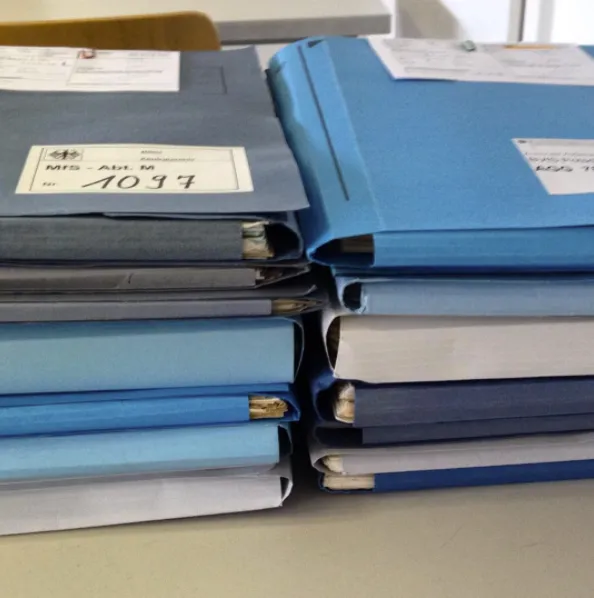
    Stasi files at the BStU. These are not the personal files the Stasi collected, but notes, diagrams, and parts lists detailing the inventions and processes developed during the Stasi’s almost 40 year reign.

    I Know Where Your Cat Lives launched

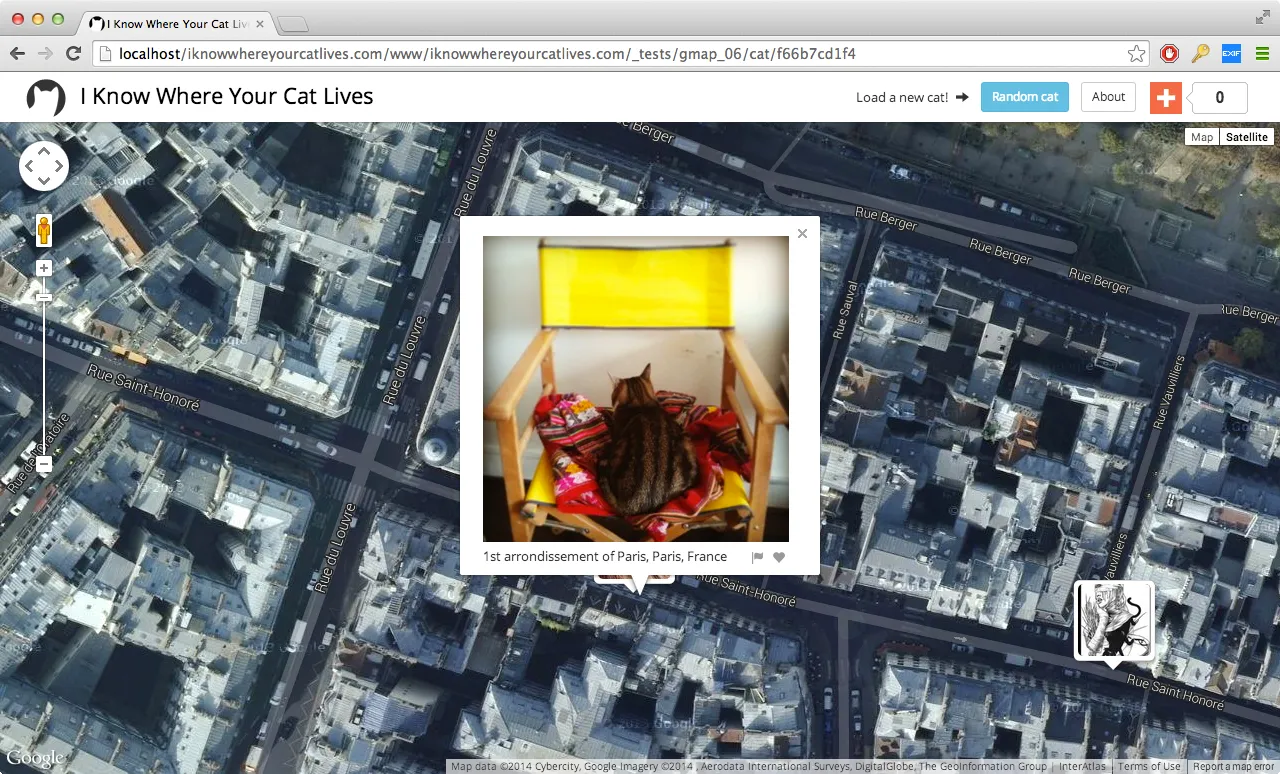
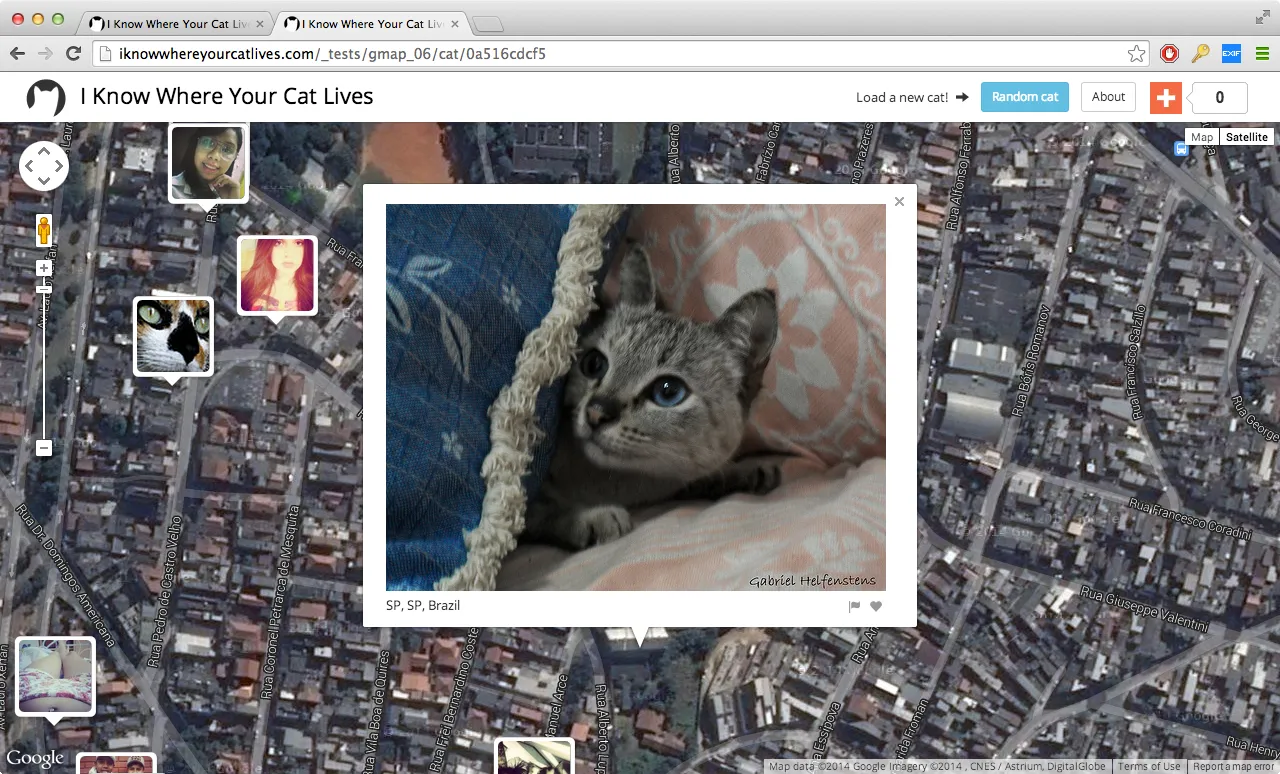
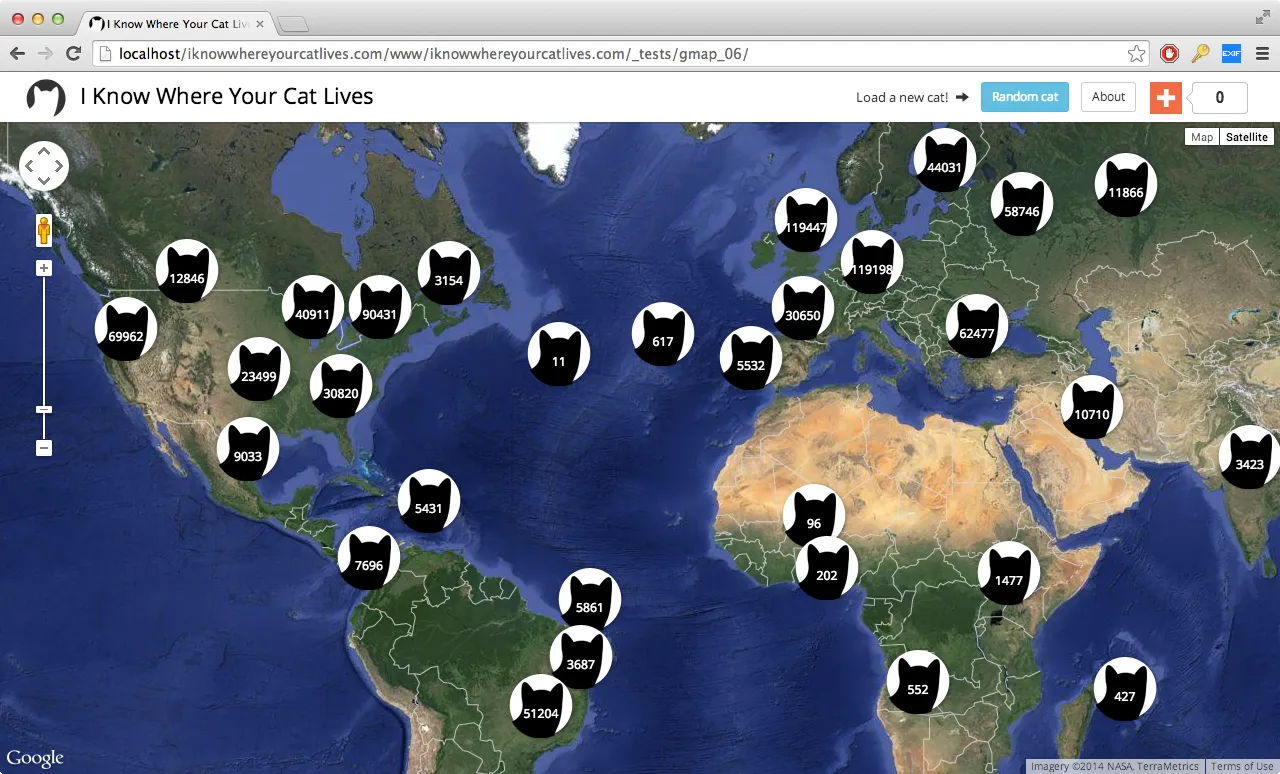
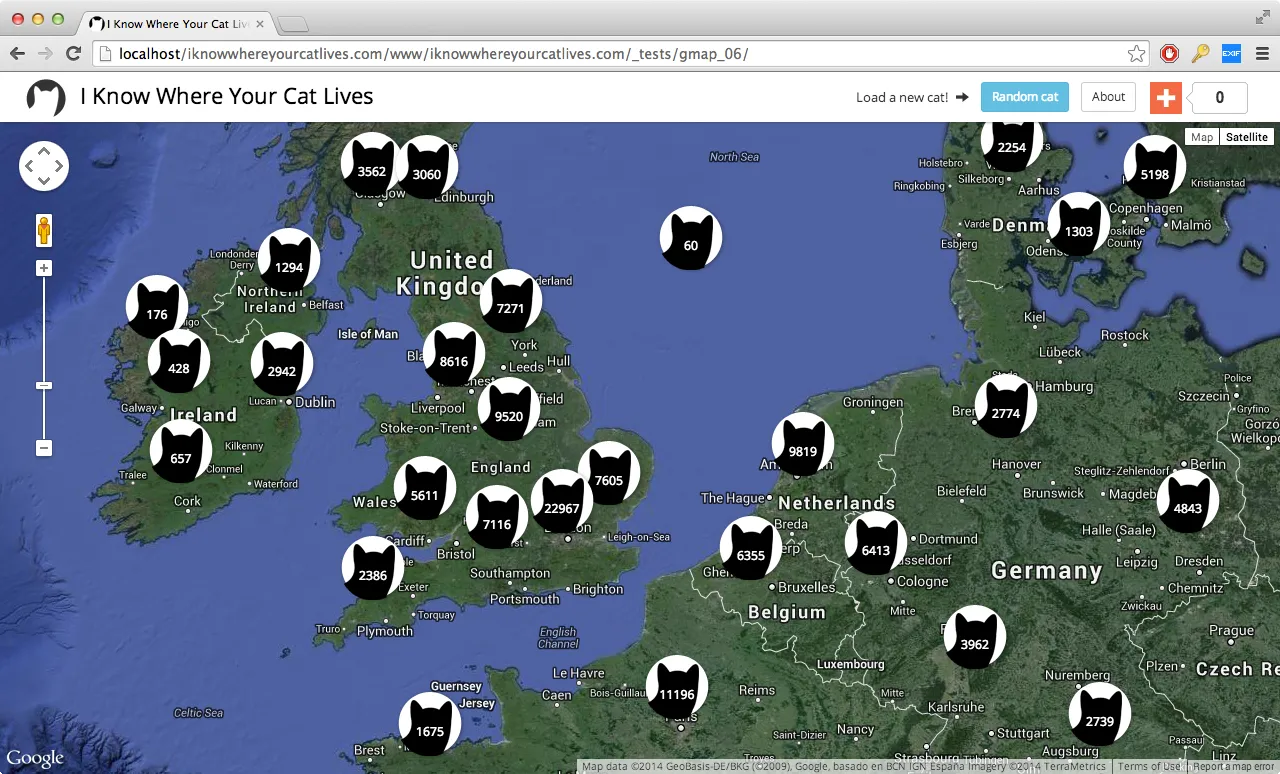
    I just launched a new ongoing project this week. Here’s the text, a video and some screenshots. I’ll post more about how I made it soon.

    Welcome to the today’s internet—you can buy anything, every website is tracking your every move, and anywhere you look you find videos and images of cats. Currently, there are 15 million images tagged with the word “cat” on public image hosting sites, and daily thousands more are uploaded from unlimited positions on the globe.

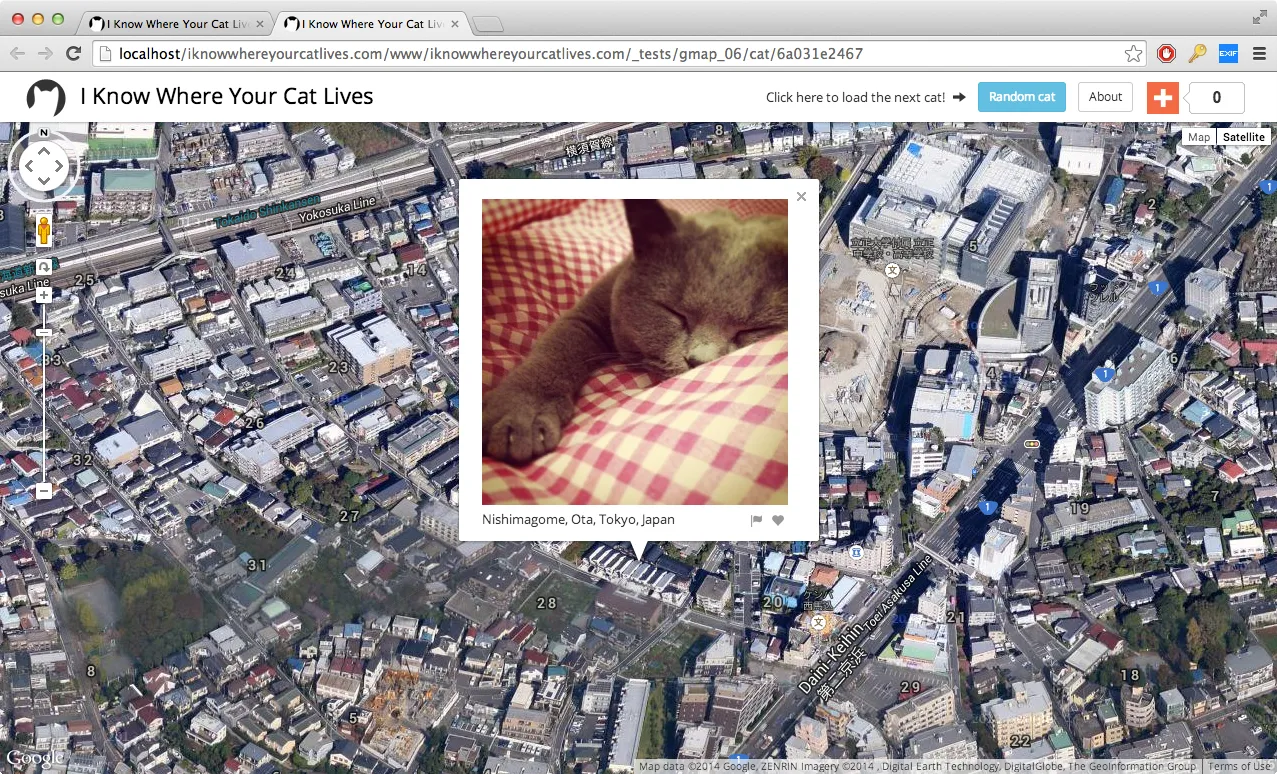
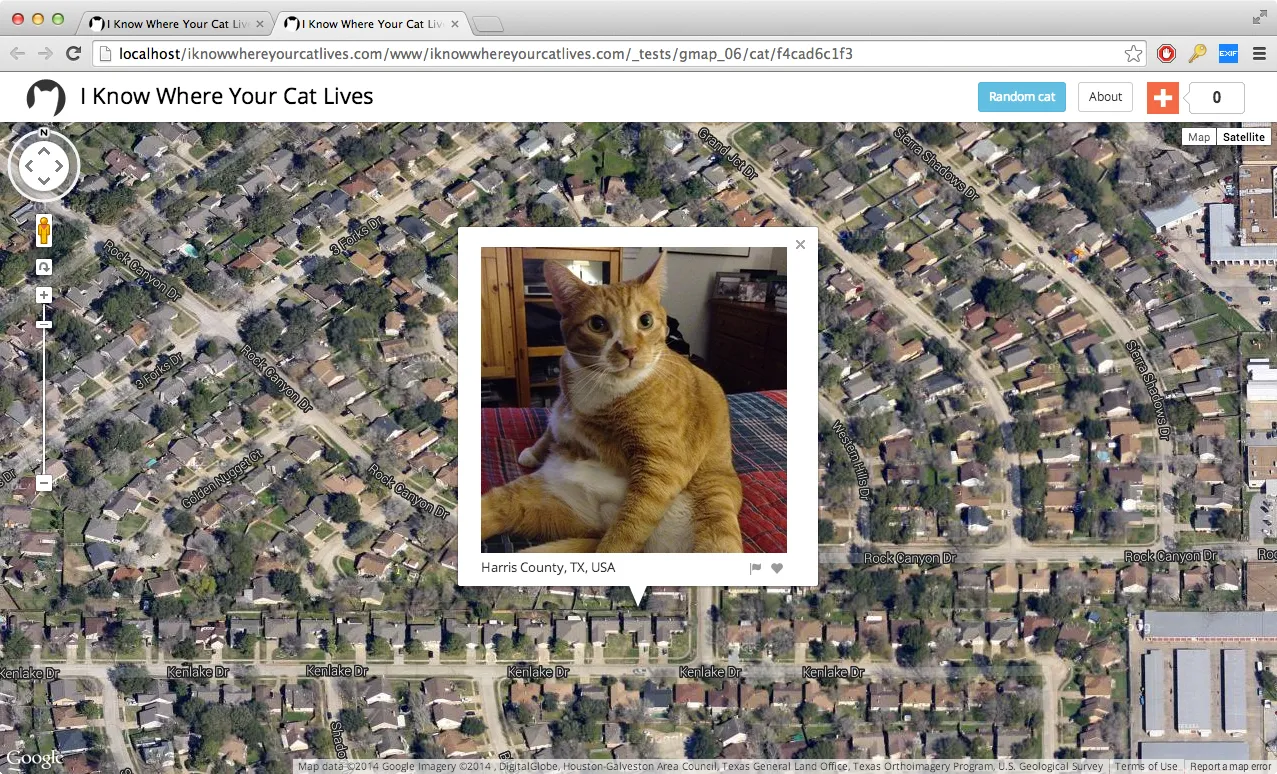
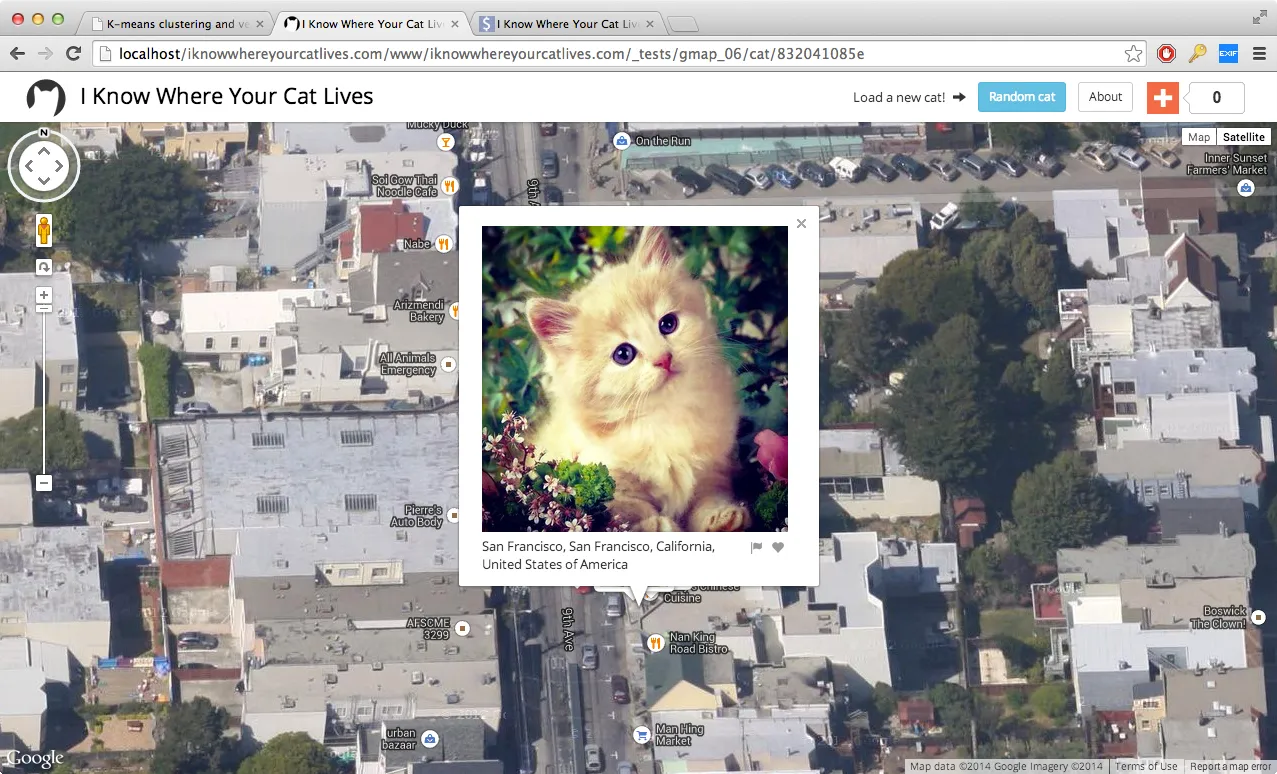
    “I Know Where Your Cat Lives” iknowwhereyourcatlives.com is a data experiment that visualizes a sample of 1 million public pics of cats on a world map, locating them by the latitude and longitude coordinates embedded in their metadata. The cats were accessed via publicly available APIs provided by popular photo sharing websites. The photos were then run through various clustering algorithms using a supercomputer at Florida State University in order to represent the enormity of the data source.

    This project explores two uses of the internet: the sociable and humorous appreciation of domesticated felines, and the status quo of personal data usage by startups and international megacorps who are riding the wave of decreased privacy for all. This website doesn’t visualize all of the cats on the net, only the ones that allow you to track where their owners have been.

    Folks can also contribute to a kickstarter to help with hosting costs.

    I Know Where Your Cat Lives

    I Know Where Your Cat Lives

    I Know Where Your Cat Lives

    I Know Where Your Cat Lives

    I Know Where Your Cat Lives

    I Know Where Your Cat Lives

    I Know Where Your Cat Lives

    “The Earth Observation Guide” – Post Media Lab notes

    I’m back from Lüneberg, Germany and already missing the simplicity of traveling by train as well as the pleasure of fine wurst. However I had an engaging few days at the Post Media Lab’s Taking Care of Things!. The event began with a keynote by Kelly Dobson from RISD, followed by a tour of Stadtarchive the next morning. Then we broke off into groups to address various topics around archives, art, media, and politics.

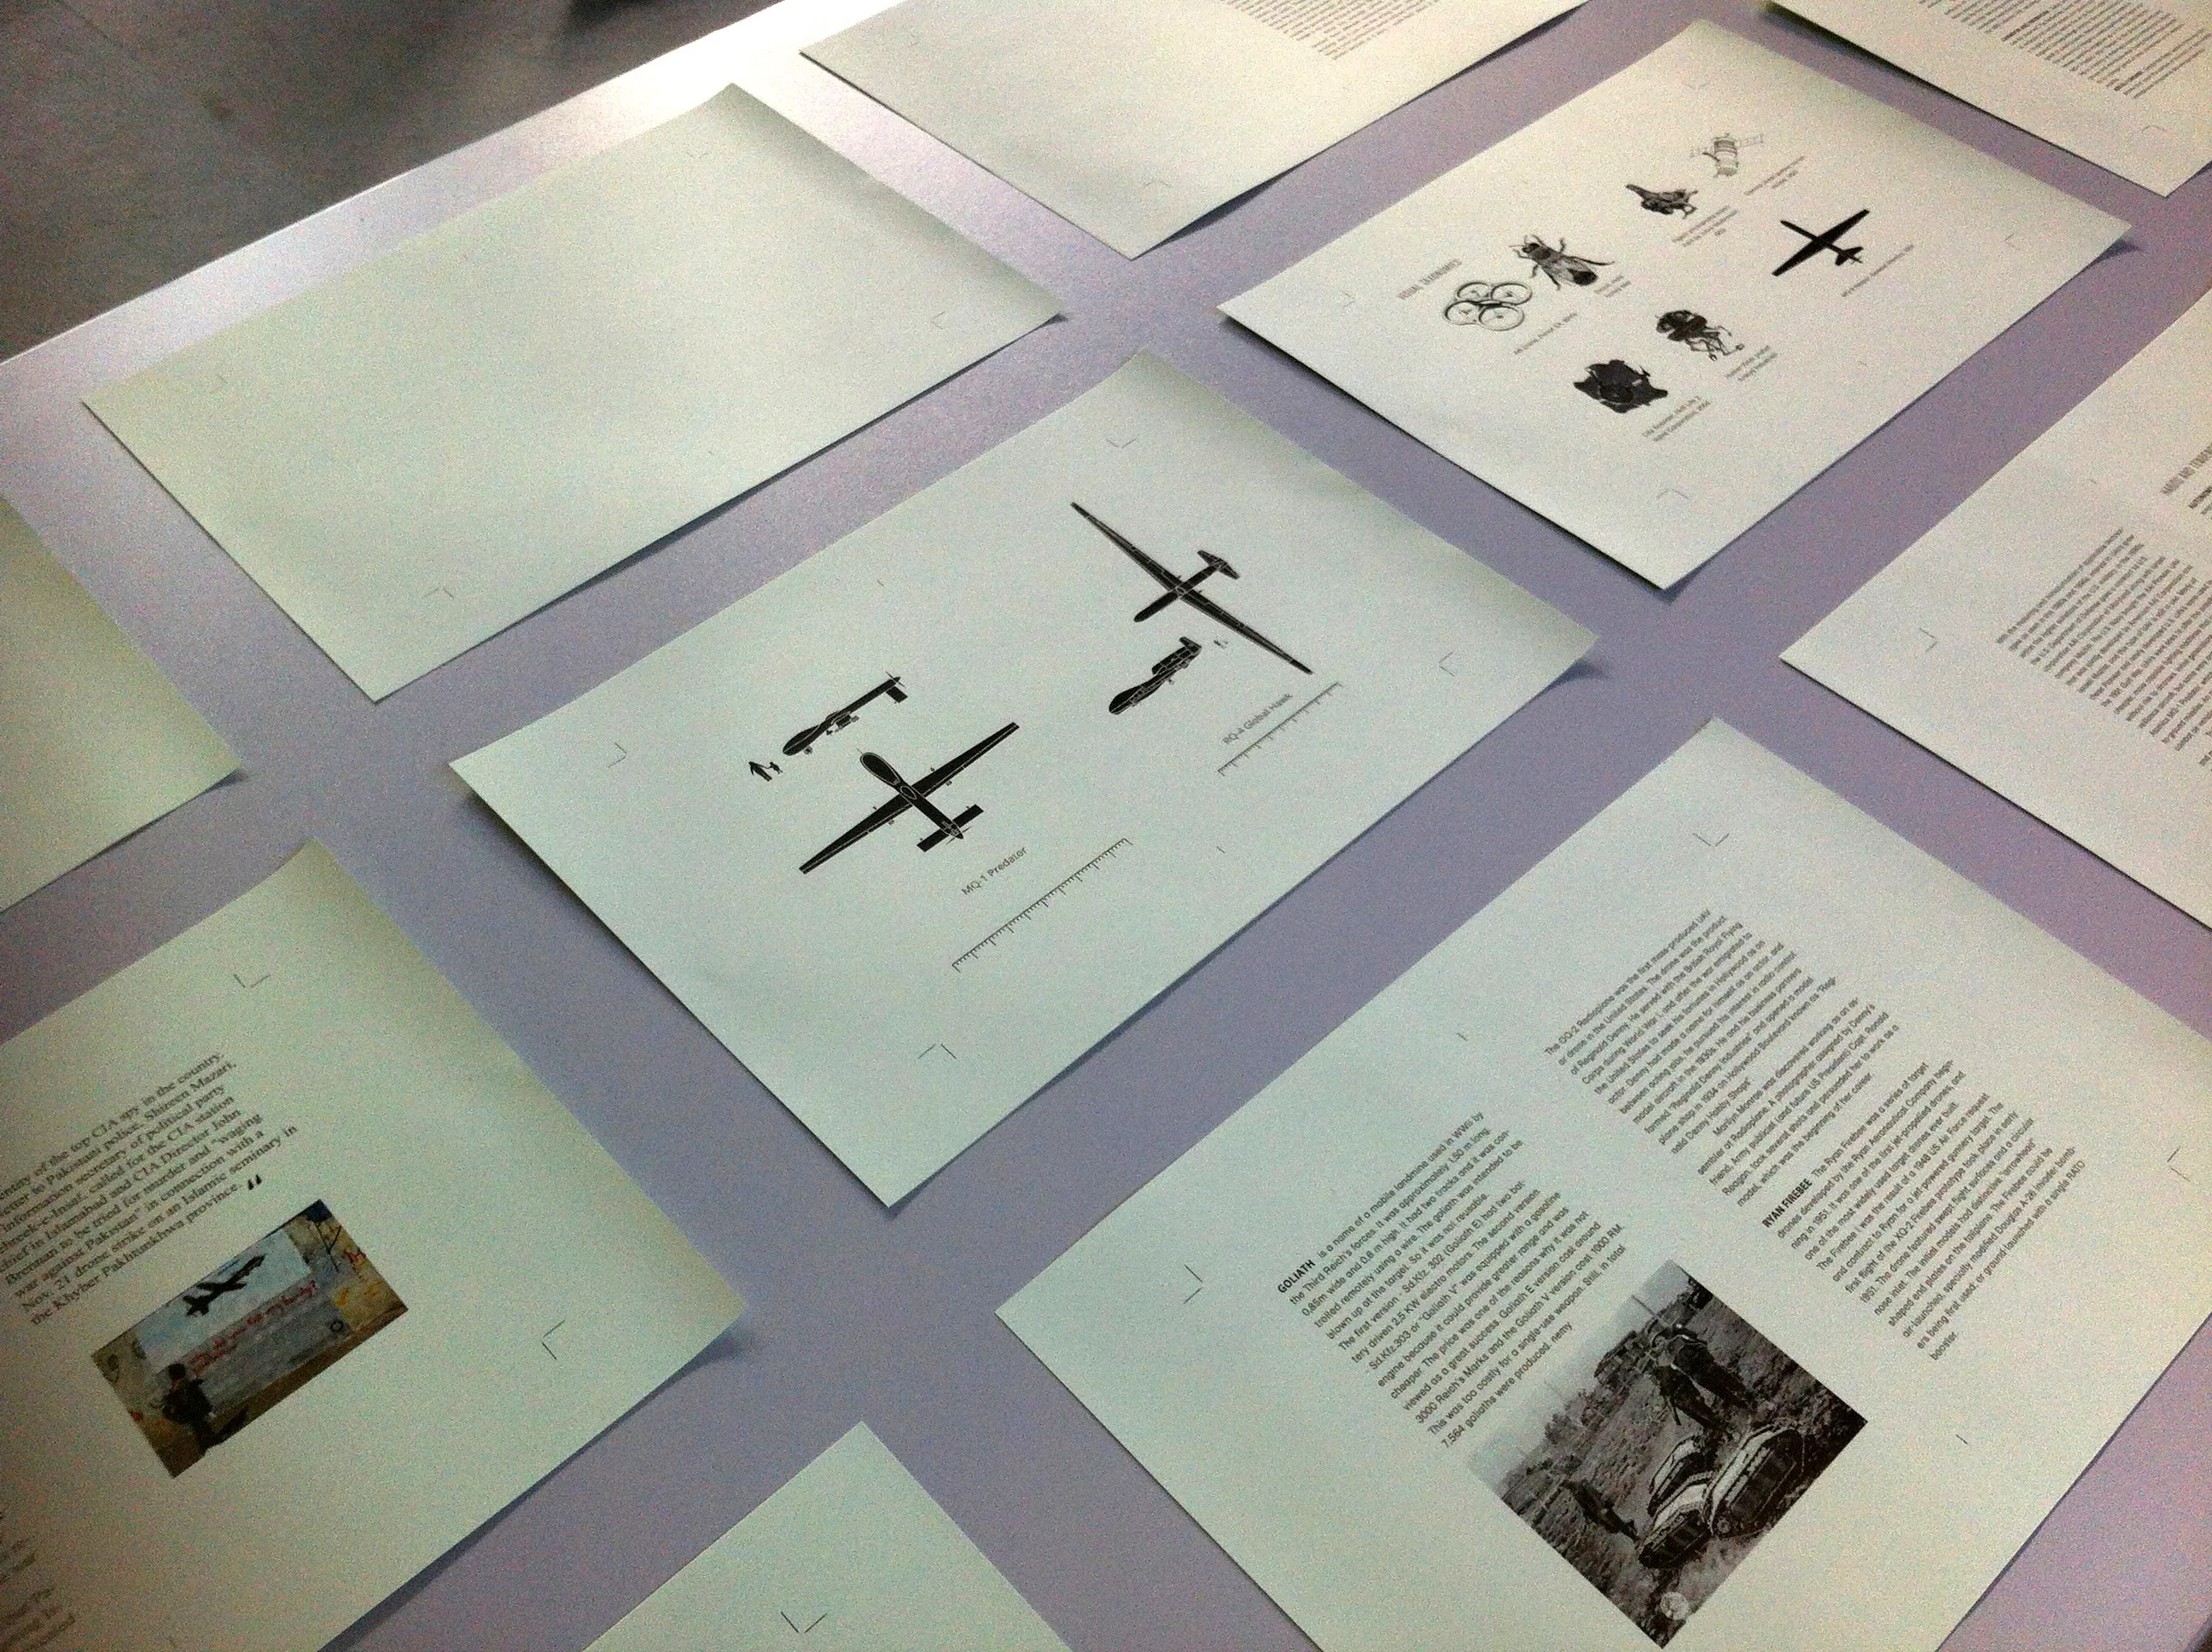
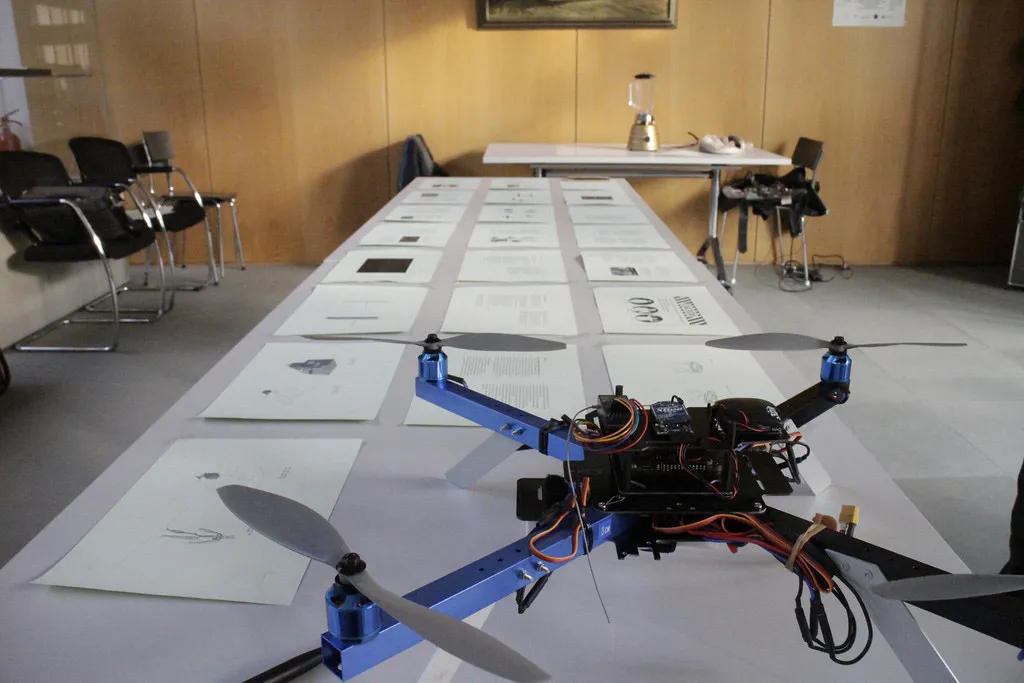
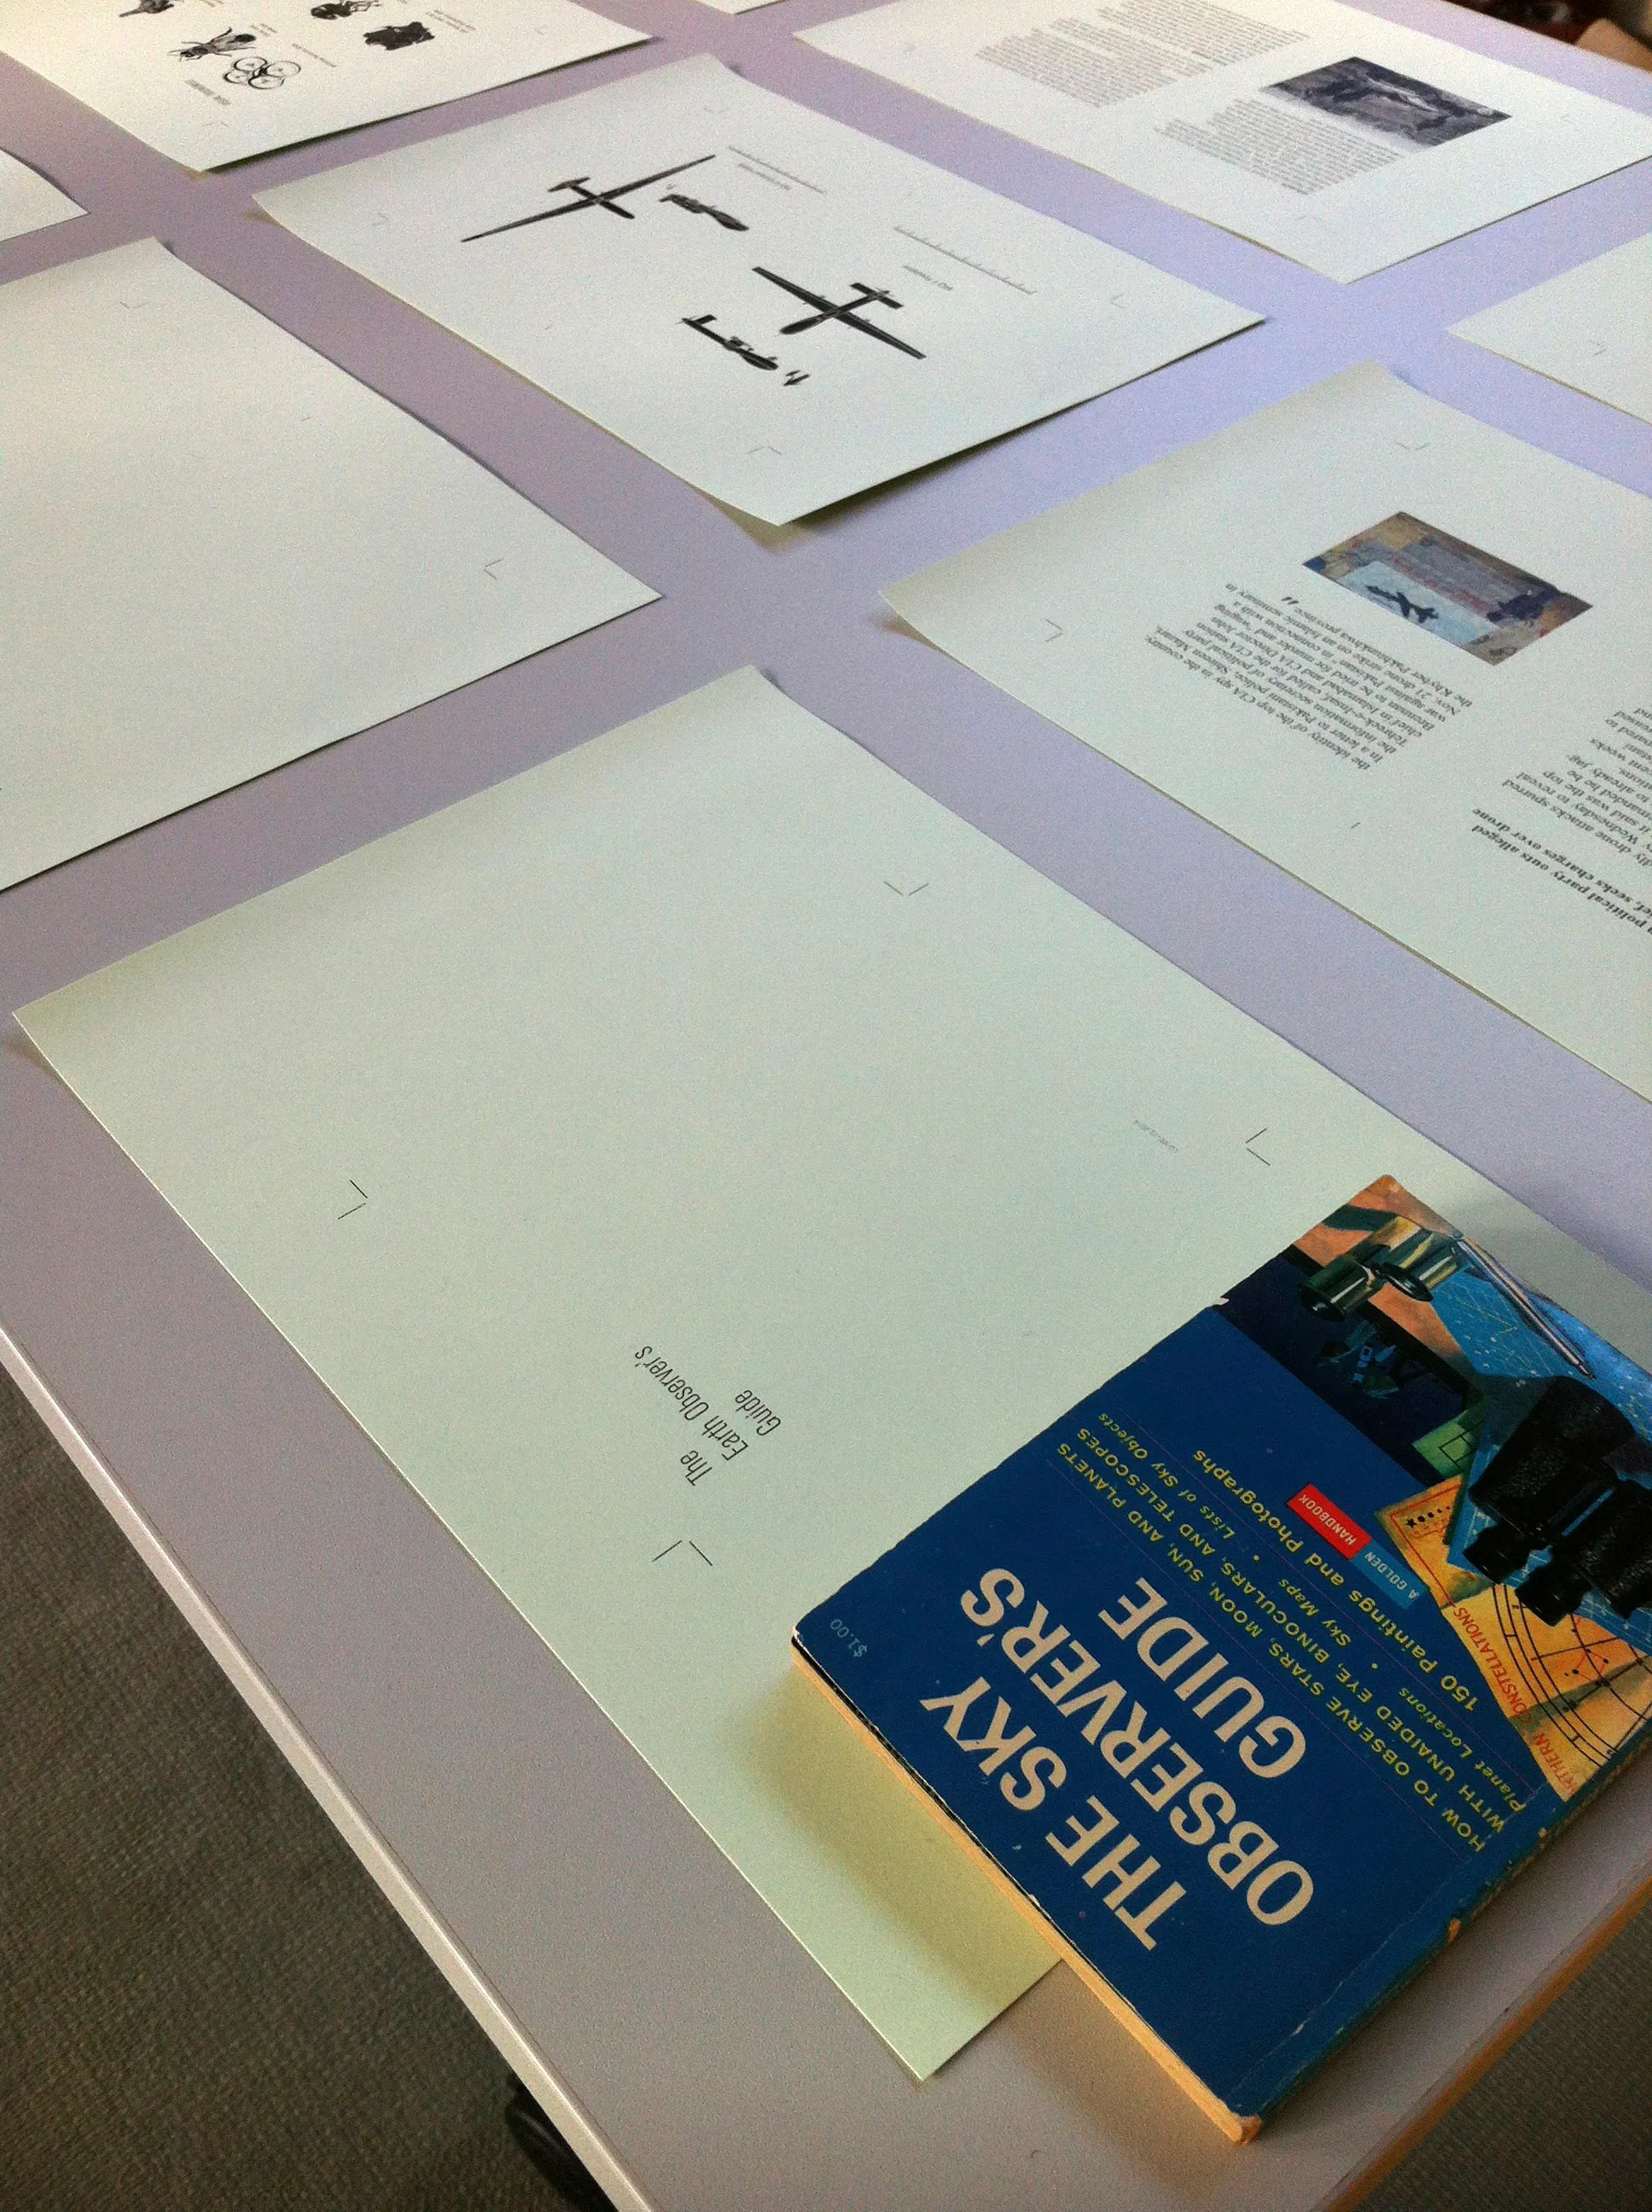
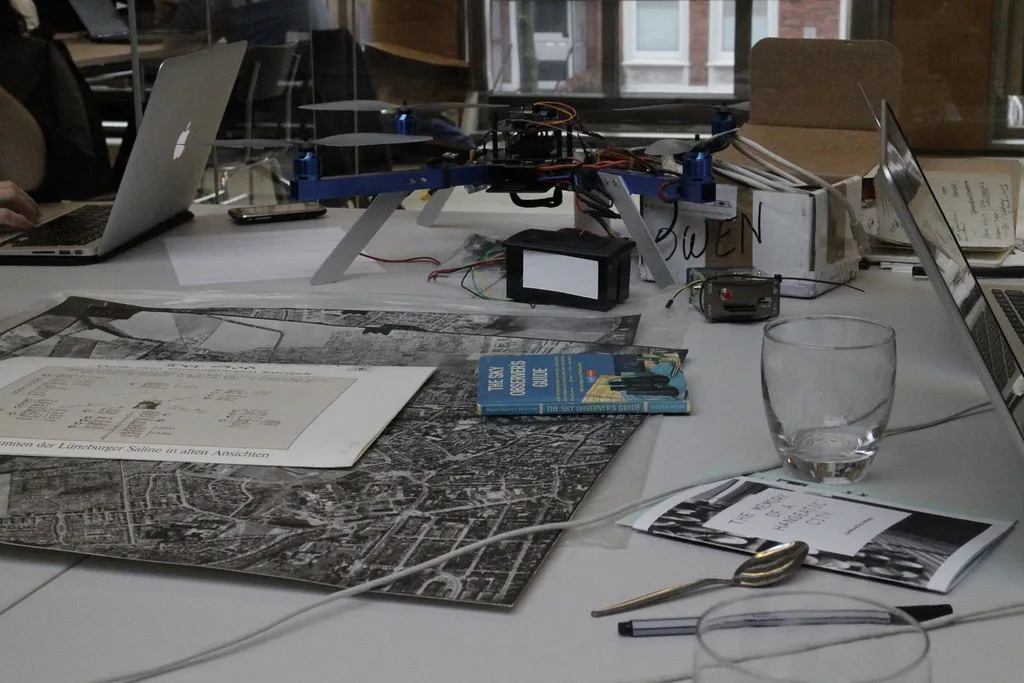
    I worked in the Measure Drones group with colleagues, Kristian Lukic, Moritz Queisner, Boaz Levin, Daniel Herleth, Adam Kaplan, Frédéric Eyl, and Oliver Lerone Schultz (one of the coordinators of Taking Care of Things along with Christina Kral). Together, over the course of two days, we worked together to conceive, research, write, illustrate, and design a booklet called “The Earth Observation Guide.” This is not a history of art about drones, nor does it try to tackle the whole subject. Rather it is more akin to a time capsule that preserves a moment in time before drones are widespread. It acts as a guidebook, recording what is known about their past and present, illustrating shifts and concerns, and addressing how humans might understand their future. Here are some images of the presented work on the third day:

    The Earth Observation Guide, Post Media Lab

    Taking Care of Things at the Stadtarchiv Lüneburg

    The Earth Observation Guide, Post Media Lab

    Taking Care of Things at the Stadtarchiv Lüneburg

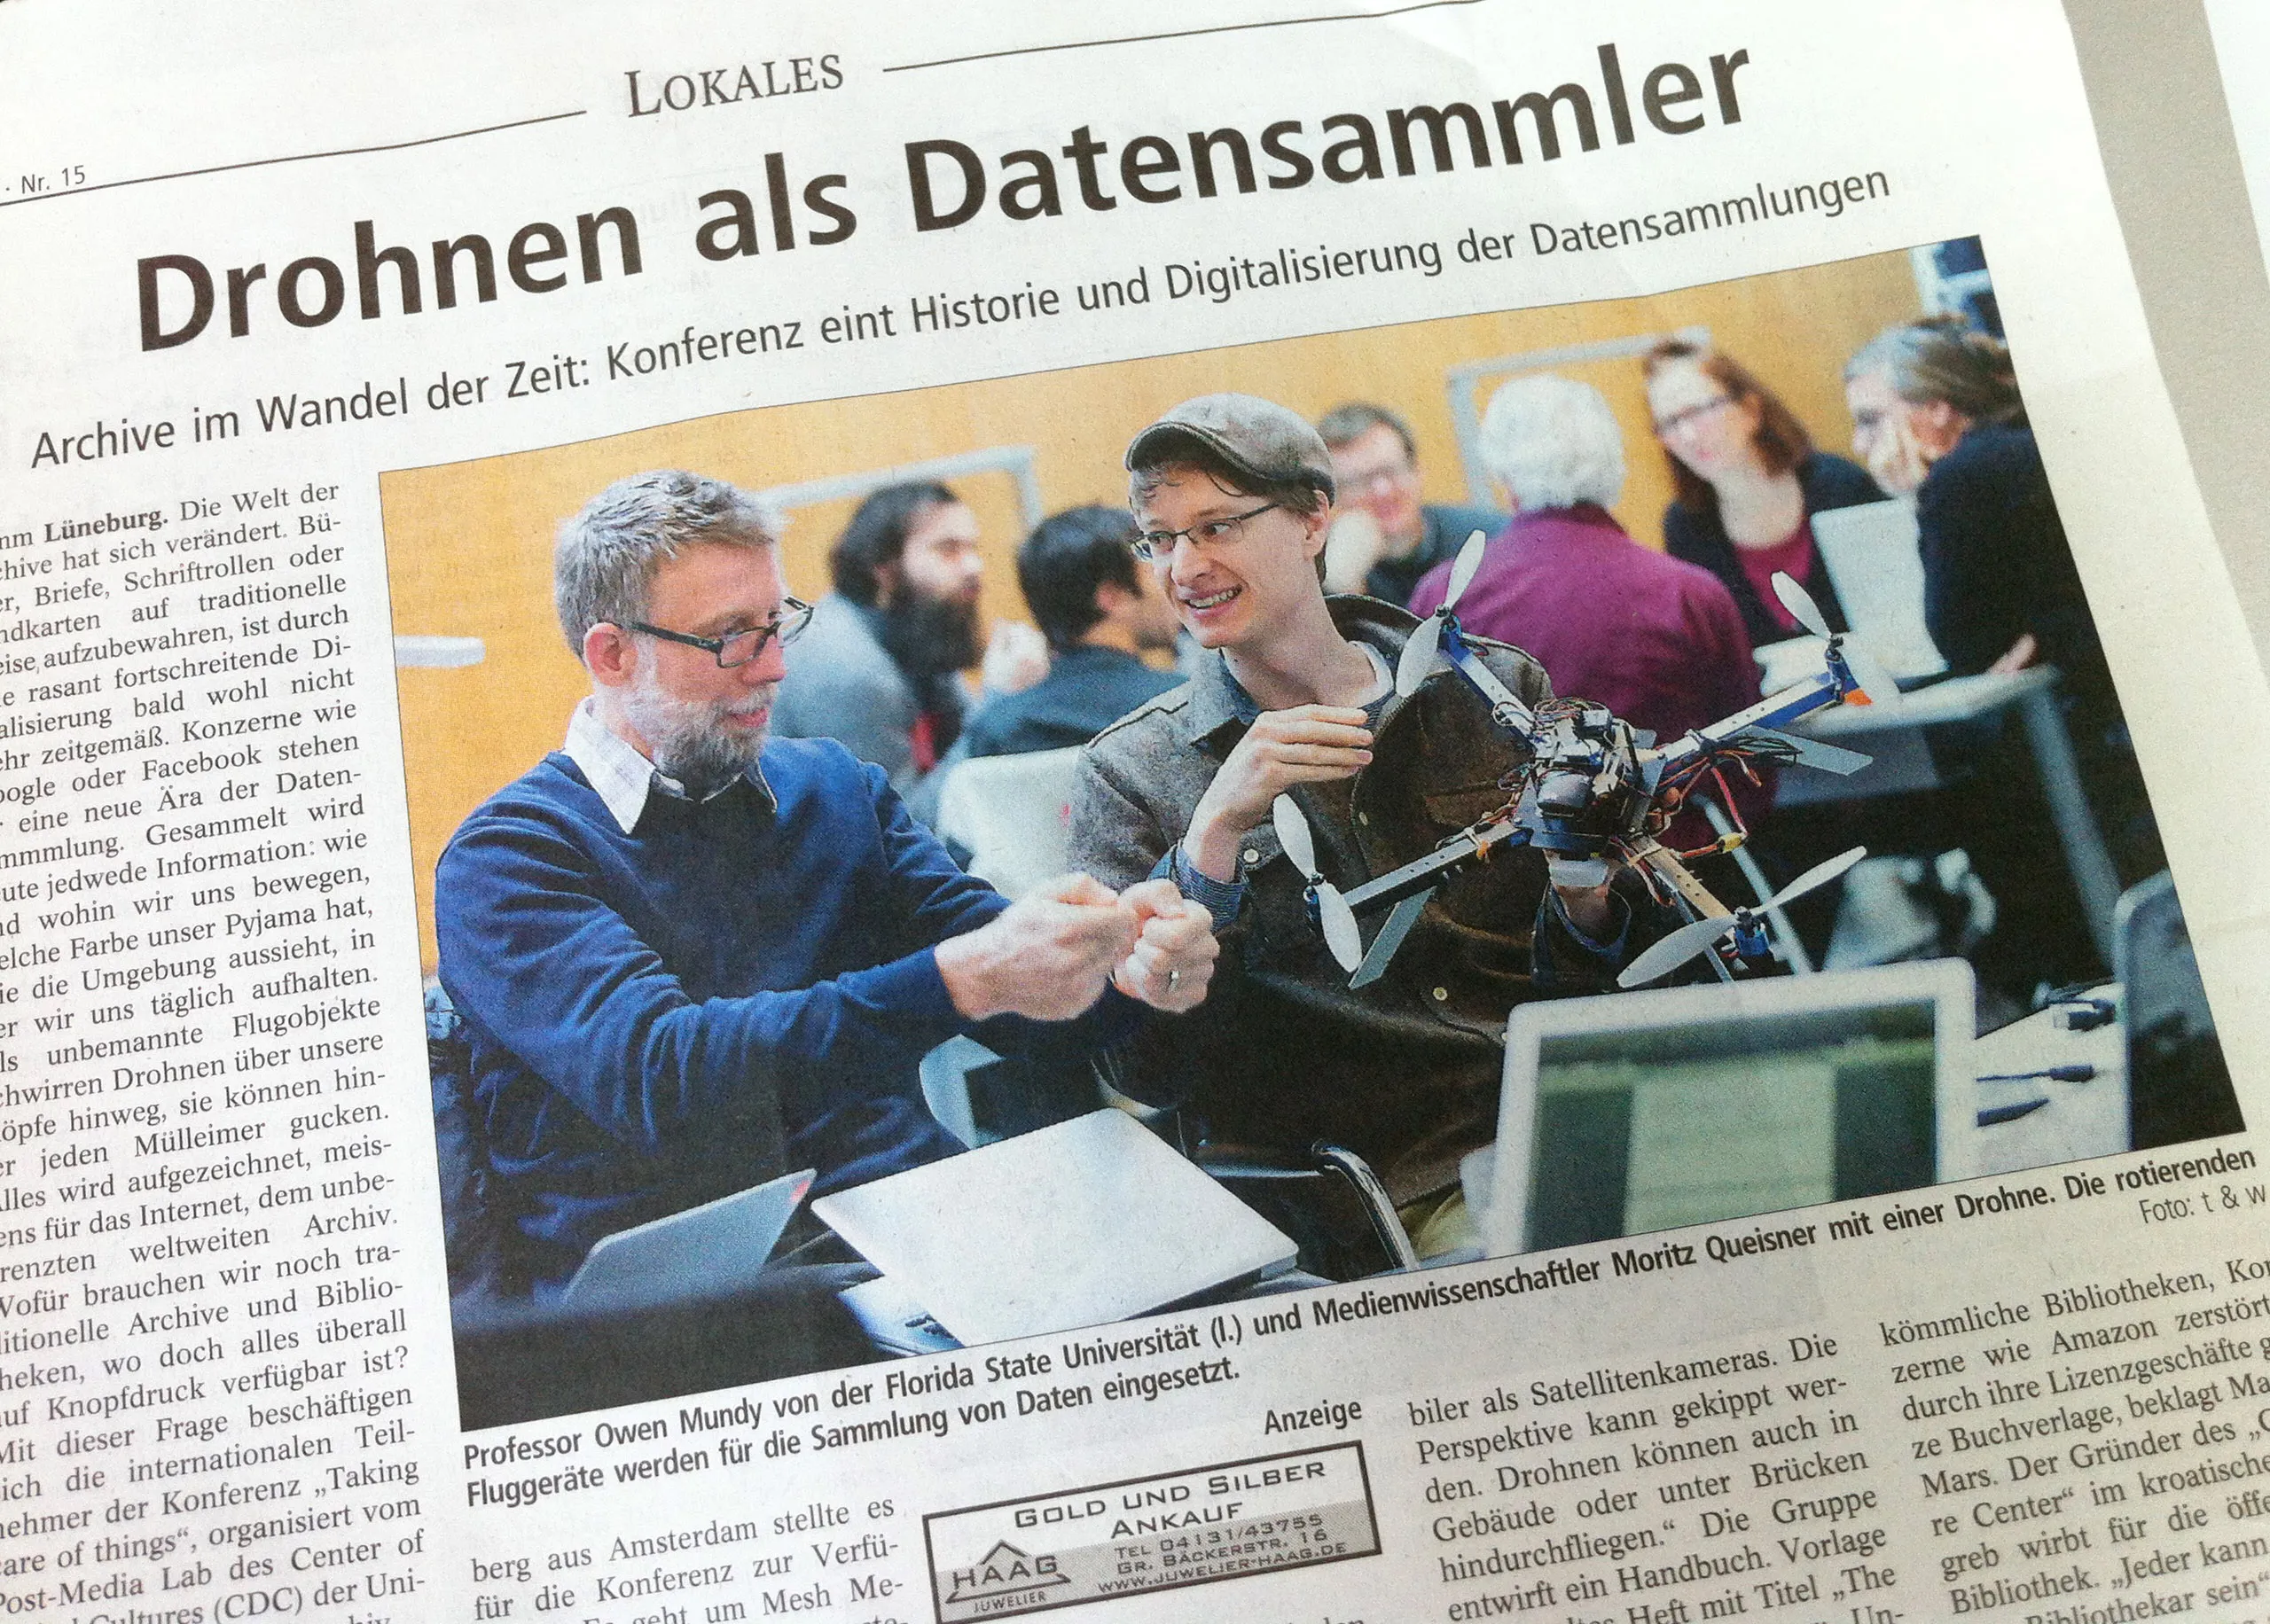
    I also somehow managed to get my mug in the newspaper in Lüneberg. I think it says “American professor launching spy drones in Germany” or some such thing.

    The Earth Observation Guide, Post Media Lab

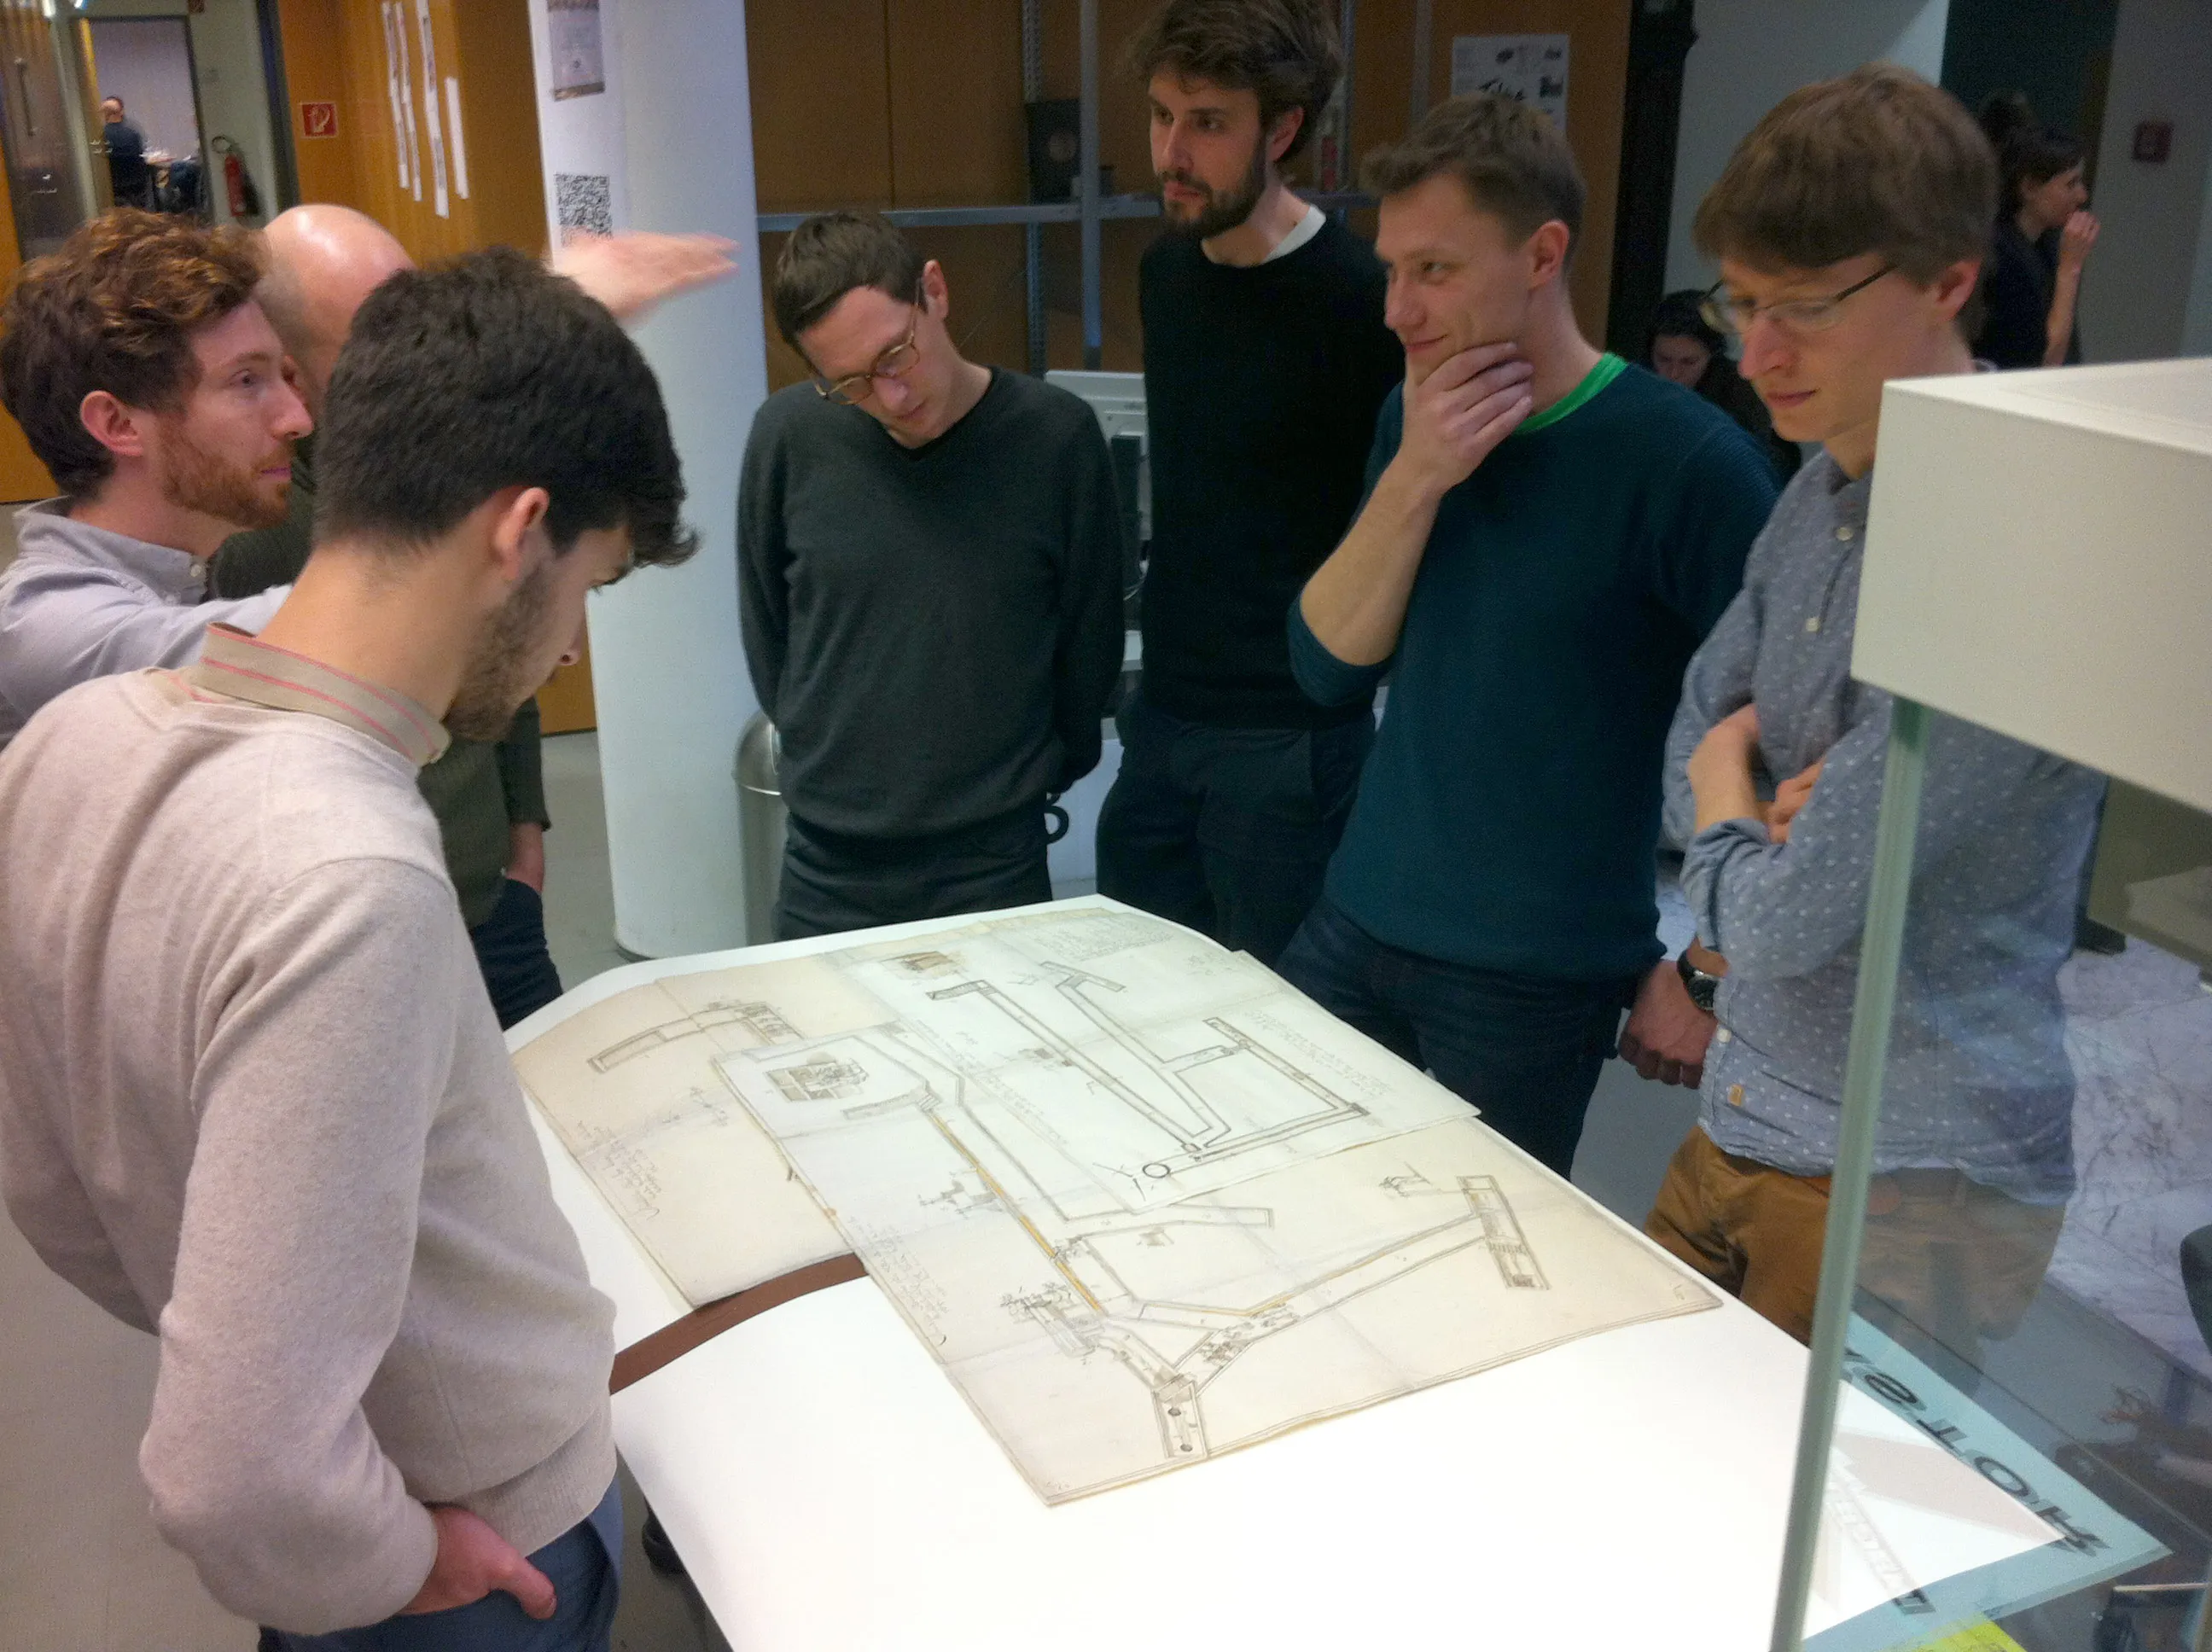
    The group examining 16th century drawings of salt mines from the archive.

    The Earth Observation Guide, Post Media Lab

    Taking Care of Things! Archives, Life-Cycles, Care, Lüneburg, Germany

    Excited to be heading to Lüneburg, Germany, tomorrow for this conference organized jointly by Habits of Living (Brown University, CIS Bangalore) and the Post-Media Lab in conjunction with Stadtarchiv Lüneburg.

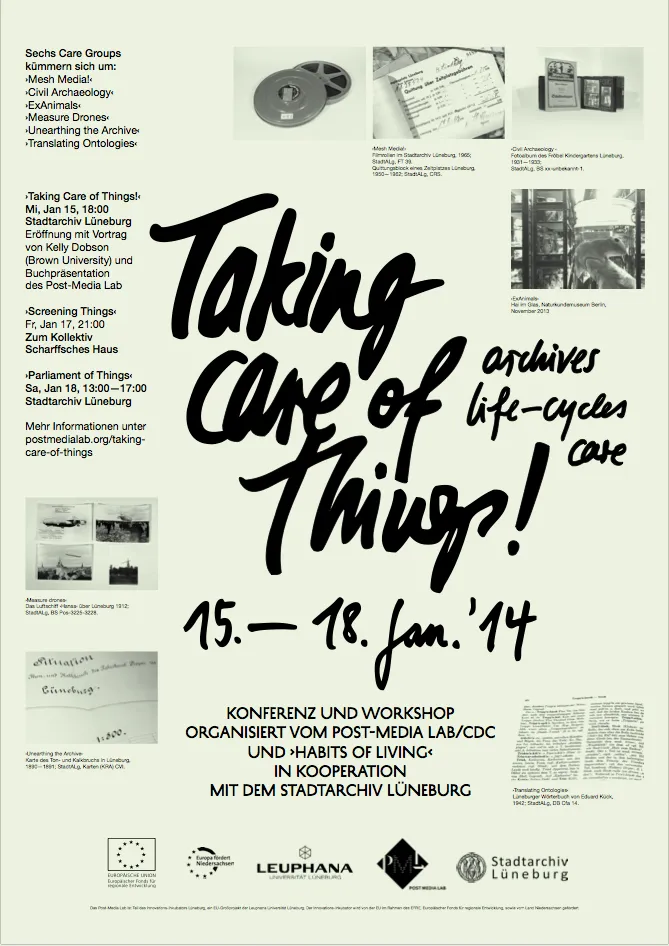
    Poster for Taking Care of Things!

    January 15-18
    Taking Care of Things!
    Archives – Life-Cycles – Care
    organized by Post-Media Lab/CDC and Habits of Living in cooperation with the Stadtarchiv Lüneburg

    Venue: Stadtarchiv Lüneburg, Germany

    From the perspective of current theoretical approaches the figure of the archive seems to have lost its central status and its fever. Meanwhile, in our medial and cultural set-up new (kinds of) archives seem to crop up everywhere, accelerated by new means of production and distribution. Cultural repertoires are being remixed alongside technological repositories – often giving new life to almost forgotten relics. Ever more things, valuables, processes, projects, constituencies, even movements, need to be taken care of. It is not only cultural and critical theory that is being challenged, but also law, the natural sciences and design, alongside other applied sciences. But what are the complex dynamics and contexts of these new (non-)archives? Do they really make sense? And if so, by and for whom?

    To address these questions, ‘Taking Care of Things!’ focuses on the transformation of things – analog and digital – into life-cycles and specific practices of care. This will be done in different thematic groups dealing with topics, like Mesh Media!, Civil Archaeology, Measure Drones, Unearthing the Archive, Translating Ontologies and Extinction in Context.

    This workshop will address such fundamental changes in archiving and objects by generating practices and chances to take care of things. That is, we will seek to extend (or sometimes end) the life-cycle of objects not by simply preserving them (this usually guarantees they will be forgotten), but rather through acts that respond, react, and/or reuse.

    ‘Taking Care of Things!’ will be based at and operating from the Stadtarchiv Lüneburg, the city’s rich and still to-be-further-explored archive, headed by Danny Kolbe.

    ‘Taking Care of Things!’ will start Wednesday evening (Jan 15) with a public talk by Kelly Dobson (Brown University) and followed by short introductions by Oliver Lerone Schultz, Nishant Shah and Wendy Chun to set the scene for the following days. Clemens Apprich together with Marcell Mars will then turn the evening into a Public Library, offering the first charge of Post-Media Lab publications as free downloads.

    Thursday and Friday (Jan 16-17) will be reserved for intensive exchanges and workshops among the invited participants, all of whom deal very differently and critically with post-medial (non-)archives. There will be the opportunity to interface with the Lüneburg public, assembling archival objects of different kinds. On Saturday (Jan 18) all these activities will culminate in a public presentation and fair under the umbrella of ‘Parliament of Things’ held at the Stadtarchiv.

    ‘Taking Care of Things!’ will create multiple interweavings not only with the rich repository of the Stadtarchiv, but also with the multiple potentials of existing and new collaborations around the Center for Digital Cultures – possibly starting some repositories that will carry on into a future, where the Post-Media Lab will have been supplanted by other, new life-cycles.​

    ‘Taking Care of Things!’ is a collaborative event between Habits of Living (Brown University, CIS Bangalore) and the Post-Media Lab in conjunction with Stadtarchiv Lüneburg.
    This event will mark the conclusion of the first life-cycle of the Post-Media Lab by bringing together former fellows and new participants.

    Among the participants are: Adnan Hadzi and James Steven (DeckspaceTV), Femke Snelting and Michael Murtaugh (Constant/Active Archives), Eric Kuitenberg and David Garcia (Tactical Media Files), Boaz Levin and Daniel Herleth and Adam Kaplan (The Rise of Data), Fabian Giraud and Inigo Wilkins (Glass Bead), Jonathan Kemp and Martin Howse („Stack, Frame, Heap –SFH)”, as well as Memory of the World (Marcell Mars), Mathias Fuchs (Gamification Lab), Cornelia Sollfrank (Giving What You Don´t Have), Hauke Winkler (Freifunk Lüneburg), Robert Ochshorn (InterLace), Tapio Makela (M.A.R.I.N.) [had to cancel bec of illness], Fabrizio Augusto Poltronieri (MaisZero), Rodrigo Novaes (Flusser Archiv/UdK), Owen Mundy, Kristian Lukic (NAPON), Vahida Ramujkic (irational), Volker Grasmuck (CDC/Grundversorgung 2.0), Kilian Froitzhuber (netzpolitik.org), Vincent Normand, Jeremy Lecomte, Ida Soulard, Erich Berger, Connie Mendoza, and more.

    Coordination & Care
    Christina Kral: christina.kral@inkubator.leuphana.de
    Oliver Lerone Schultz: oschultz@leuphana.de

    Team
    Wendy Chun, Nishant Shah, Clemens Apprich, Josie Berry Slater, Anthony Iles; and Nora Hannemann, Sina Hurnik, Nina Kersten, Ann-Kathrin Wagner, Nicolas Schrape

    CYBER IN SECURITIES, Pepco Edison Place Gallery, Washington, DC

    CYBER IN SECURITIES at Pepco Edison Place Gallery

    clockwise l to r: Ricarda McDonald and Donna Szoke, and all watched over by machines of loving grace; Birgit Bachler, Walter Langelaar, Owen Mundy, and Tim Schwartz, Commodify.us; Lexie Mountain, Ball Hard; Whitefeather, Parent Folder

    CYBER IN SECURITIES
    Dates: August 30 – September 27, 2013
    Location: Pepco Edison Place Gallery, 702 8th Street, NW, Washington, DC

    Curated by: Lisa Moren, Professor, Department of Visual Art, University of Maryland, Baltimore County

    Participating Artists: Birgit Bachler, Walter Langelaar, Owen Mundy, and Tim Schwartz; Channel TWo (CH2): Adam Trowbridge and Jessica Westbrook, with Jesus Duran; Heather Dewey-Hagborg; Hasan Elahi; The Force of Freedom with Dave Young; Taylor Hokanson; Ricarda McDonald and Donna Szoke; Lexie Mountain; Preemptive Media; David Rokeby; Julia Kim Smith; and WhiteFeather

    Opening Reception: Friday, August 30, 2013, 6-8pm
    Exhibition Hours: Tuesday – Friday, 12pm-4pm

    Experimental Media Video Screening Series
    Juried by Jason Eppink, Associate Curator of Digital Media, Museum of the Moving Image, New York

    Experimental Media Video Series Night One: Thursday, September 12, 2013, 6:30pm
    Location: The Phillips Collection, 1600 21st Street, NW, Washington, DC

    Experimental Media Video Series Night Two: Monday, September 24, 2013, 6:30pm
    Location: The Corcoran Gallery of Art and College of Art + Design, 500 17th Street, NW, Washington, DC

    Experimental Media Symposium: Saturday, September 21, 2013
    Location: Pepco Edison Place Gallery, 702 8th Street, NW, Washington, DC

    Experimental Media 2013 will explore security, privacy, and surveillance in the digital age, through a gallery exhibition, video screenings series, and panel discussion.

    “Google” one-week performance at Transmediale

    Google logo

    I am tele-participating in a one-week online performance of Google queries at Transmediale 2012 in Berlin. The project, plainly titled, “Google,” is organized by Johannes P. Osterhoff and will run from Jan 30 to Feb 5, 2012. Each participant edits the search method for their browser search bar so that everything they type in this box, from the personal to the mundane, becomes instantly visible at google-performance.org.

    The project (“manifesto” below) makes public what Facebook, Google, and any online search engine, crowdsourcing website, or social network already does by harvesting searches from users, and re-representing that data in a new context. While Google uses these queries to build and sell condensed user demographic data to advertisers, Osterhoff’s project asks, who actually owns your search data?

    We shall do an one-week performance piece.

    The piece is called “Google” and documents all searches we perform withthe search engine of the same name.

    The performance shall take place during transmediale 2012 and shall start on Monday, January 30 and shall end on Sunday, February 5, 2012.

    We shall not use undocumented ways to use the search engine Google during this time.

    Each of our search queries shall create a web page that is indexed by this search engine and thus makes our searches publicly available as search results for everybody.

    A Single Composite [vert]

    Finally finding time to edit documentation from A Single Composite exhibition this summer in Berlin.

    A Single Composite is a series of kinetic installations and projection apparatuses that stretch, twist, and loop film strips containing declassified and other found reconnaissance footage. Using reconstituted digital printer chassis, this cinematic enterprise is projected on walls, ceilings, and floors, to form a series of individual moments of surveillance and implied violence.

    Give Me My Data: A Facebook Application Inspired by the Stasi Files Controversy, talk at DAAD Meeting in Dresden, Germany

    Give Me My Data home page: Freiheit für meine Akte!

    Giving a talk today in Dresden, Germany titled, “Give Me My Data: A Facebook Application Inspired by the Stasi Files Controversy.” Here is the abstract.

    During the final days of the German Democratic Republic (or GDR) it became evident that the Ministry for State Security (more popularly known as the “Stasi”) was destroying incriminating evidence from its 40-year history of domestic and international surveillance. These documents, which the Stasi was attempting to destroy using shredding machines, as well as by hand when the machines failed, included information gathered through various clandestine methods about lives of citizens of the GDR without their knowledge or consent.

    On January 15, 1990, protestors stormed the Stasi headquarters in Berlin in attempt to prevent the destruction of personal records which they felt they should be able to access. The phrase, “Freiheit für meine Akte!” (in English: Freedom for my file!) spray painted on the Stasi guardhouse during this protest embodies a desire by citizens to open this closed world of state surveillance in order to understand the methods of control employed the Stasi

    This moment in history inspires my ongoing project, Give Me My Data, a Facebook application that helps users export their data out of Facebook. While clearly utilitarian, this project intervenes into online user experiences, provoking users to take a critical look at their interactions within social networking websites. It suggests data is tangible and challenges users to think about ways in which their information is used for purposes outside of their control by government or corporate entities.

    At the height of its operations, the Stasi is believed to have hired, between spies and full- and part-time informants, one in every 6.5 East German citizens to report suspicious activities, almost 2.5 million people.1 At this moment, the ratio of people entering data on Facebook to non-members is one in fourteen for the entire world,2 introducing possibly the most effective surveillance machine in history.

    Automata: Counter-Surveillance in Public Space paper on the Public Interventions panel at ISEA2010

    ISEA2010 logo

    ISEA2010 RUHR Conference in Dortmund, Germany

    P26 Public Interventions
    Tue 24 August 2010
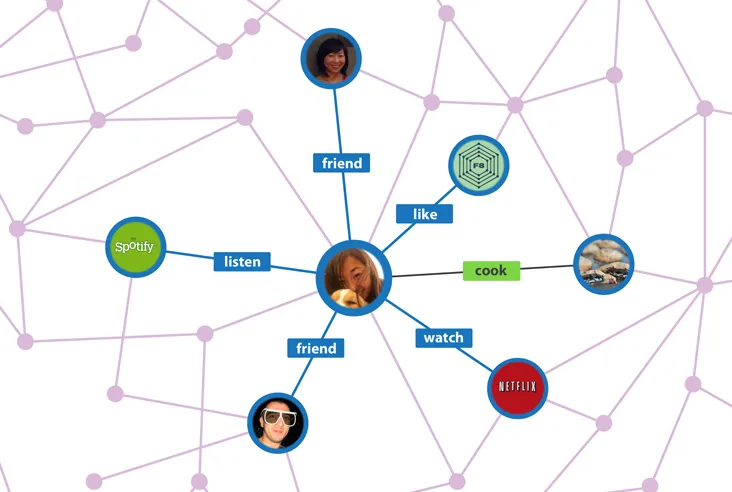
    15:00–16:30h
    Volkshochschule Dortmund, S 137a
    Moderated by Georg Dietzler (de)

    • 15:00h | Owen Mundy (us): Automata: Counter-Surveillance in Public Space
    • 15:20h | Christoph Brunner (ch/ca), Jonas Fritsch (dk): Balloons, Sweat and Technologies. Urban Interventions through Ephemeral Architectures
    • 15:40h | Georg Klein (de): Don’t Call It Art! On Artistic Strategies and Political Implications of Media Art in Public Space
    • 16:00h | Georg Dietzler (de): Radical Ecological Art and No Greenwash Exhibitions

    About my talk:

    Automata is the working title for a counter-surveillance internet bot that will record and display the mutually-beneficial interrelationships between institutions for higher learning, the global defense industry, and world militaries. Give Me My Data is a Facebook application that helps users reclaim and reuse their Facebook data. The two projects, both ongoing, address important issues surrounding contemporary forms of communication, surveillance, and control.